Formbook-Payload-Extraction-XOR-Decryption-Net-Assembly-Analysis

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…

An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.

Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…

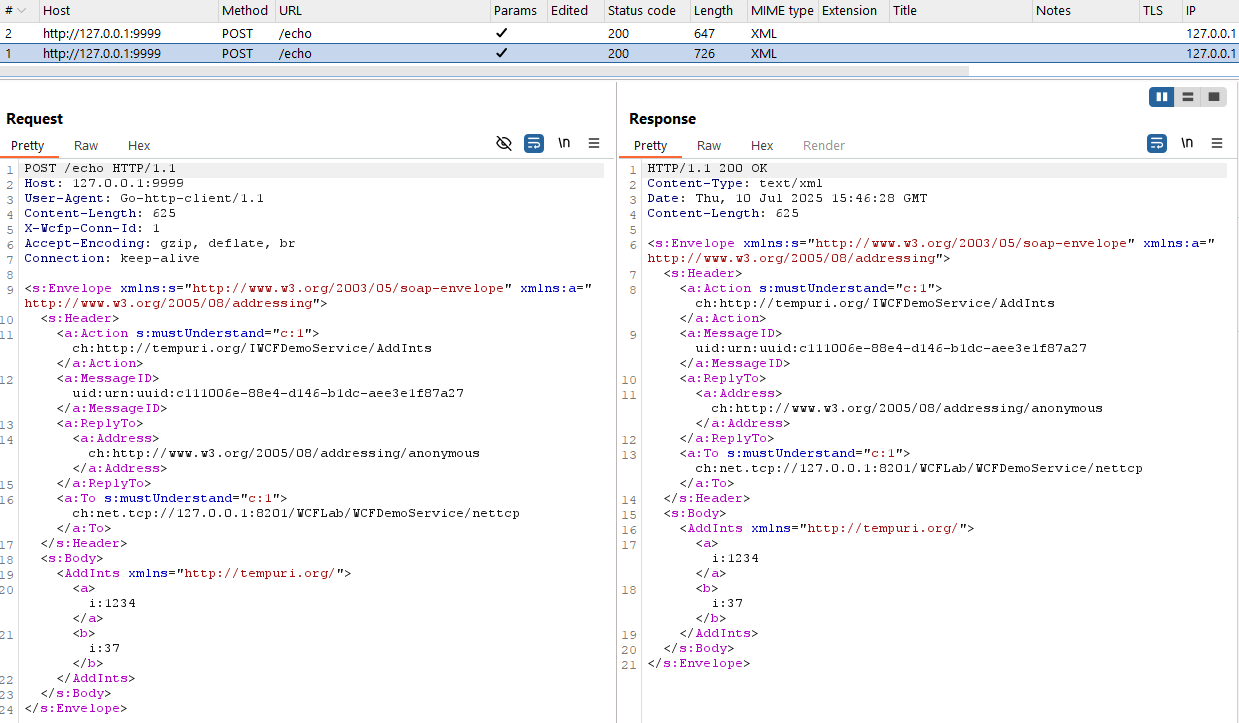
A proxy for net.tcp-based WCF traffic.

CVE 2025 27237 Zabbix LPE proof of concept.

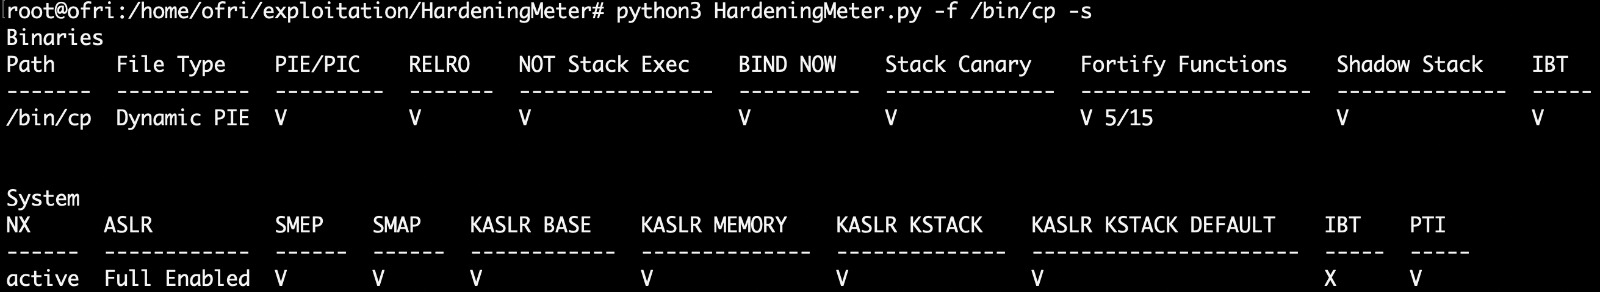
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck