

uefi-firmware-parser
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
binary-analysisembedded-systems-securityfirmware-analysis+2
928
theopolis/uefi-firmware-parserParse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
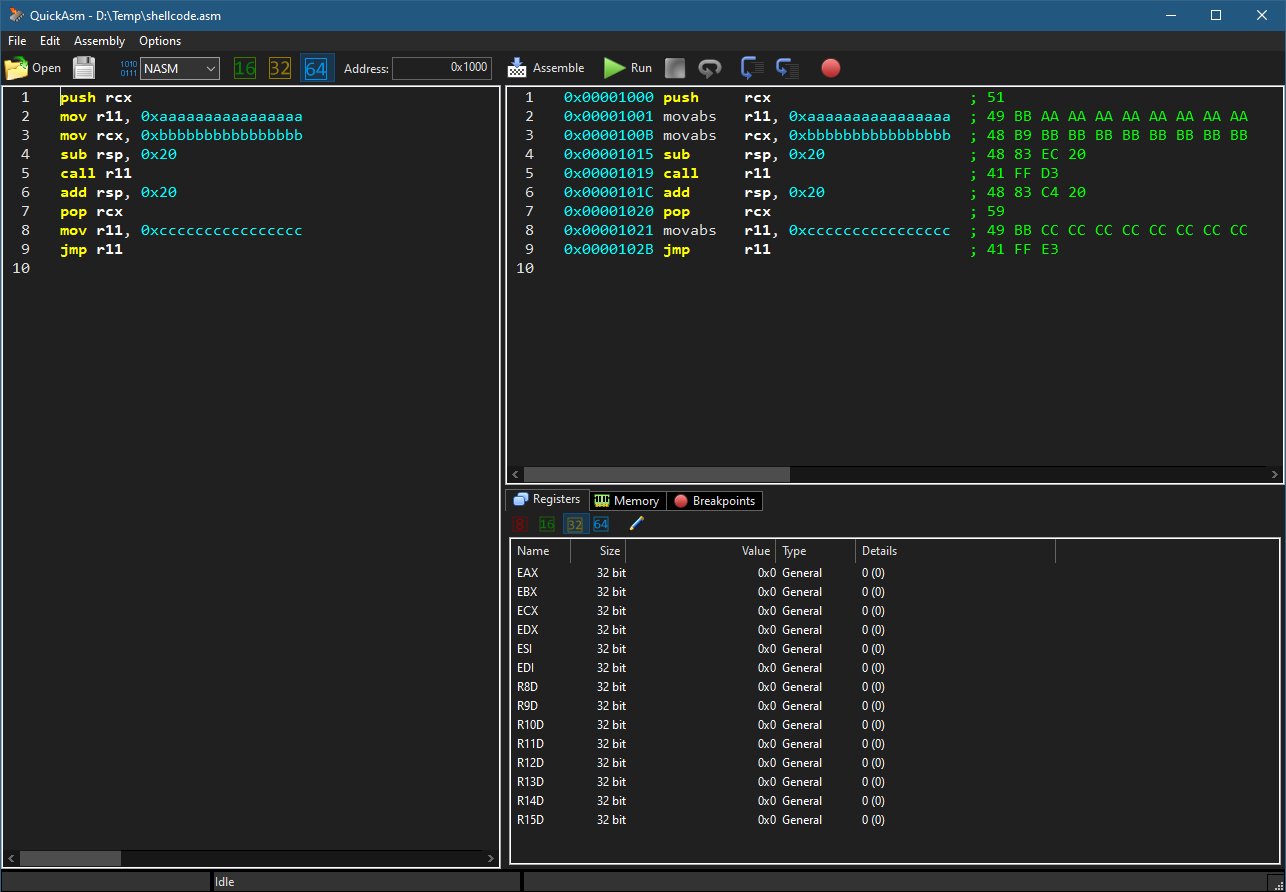 zodiacon/quickasm
Simple x86/x64 Assembler/Disassembler/Emulator
 sentinel-one/efi_fuzz
Coverage-guided fuzzer for UEFI NVRAM variables using Qiling emulation and AFL++ to discover firmware vulnerabilities through automated input…
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 thinkycx/activemq-rce-cve-2023-46604
activemq-rce-cve-2023-46604
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 clearbluejar/cve-2024-20696
Test harness for CVE-2024-20696 Windows libarchive RCE vulnerability, enabling binary analysis and exploitation testing of archiveint.dll with custom…
 osirislab/awesome-rust-security
Curated list of awesome projects and resources related to Rust and computer security
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 tin-z/cve-2021-20294-poc
Simple CVE-2021-20294 poc
 gmh5225/deobf-arxan-deob-c
Simple C program to quickly deobfuscate windows executables protected with Arxan.
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 mildsunrise/protobuf-inspector
🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition