

dissect.cobaltstrike
 fox-it/dissect.cobaltstrike
Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
binary-analysiscommand-and-controldigital-forensics+4
212
fox-it/dissect.cobaltstrikePython library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
 mandiant/goresym
Parses Go binaries to recover symbols, function metadata, types, file paths, and embedded strings, including stripped or UPX-packed samples, with IDA…
 eddinos2/cve-2026-64705
Root-cause analysis and proof-of-concept for CVE-2026-64705, a macOS HFS xattr kernel heap overflow. Includes weaponized HFS+ image, patcher, parser,…
 577industries/aegisgraph
AegisGraph: graph-based application-layer assessment evidence platform for Secure Messaging Applications (SMAs). DARPA ASEMA HR0011SB20254-12 Tier 3…
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
 jschicht/logfileparser
Parser for $LogFile on NTFS
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
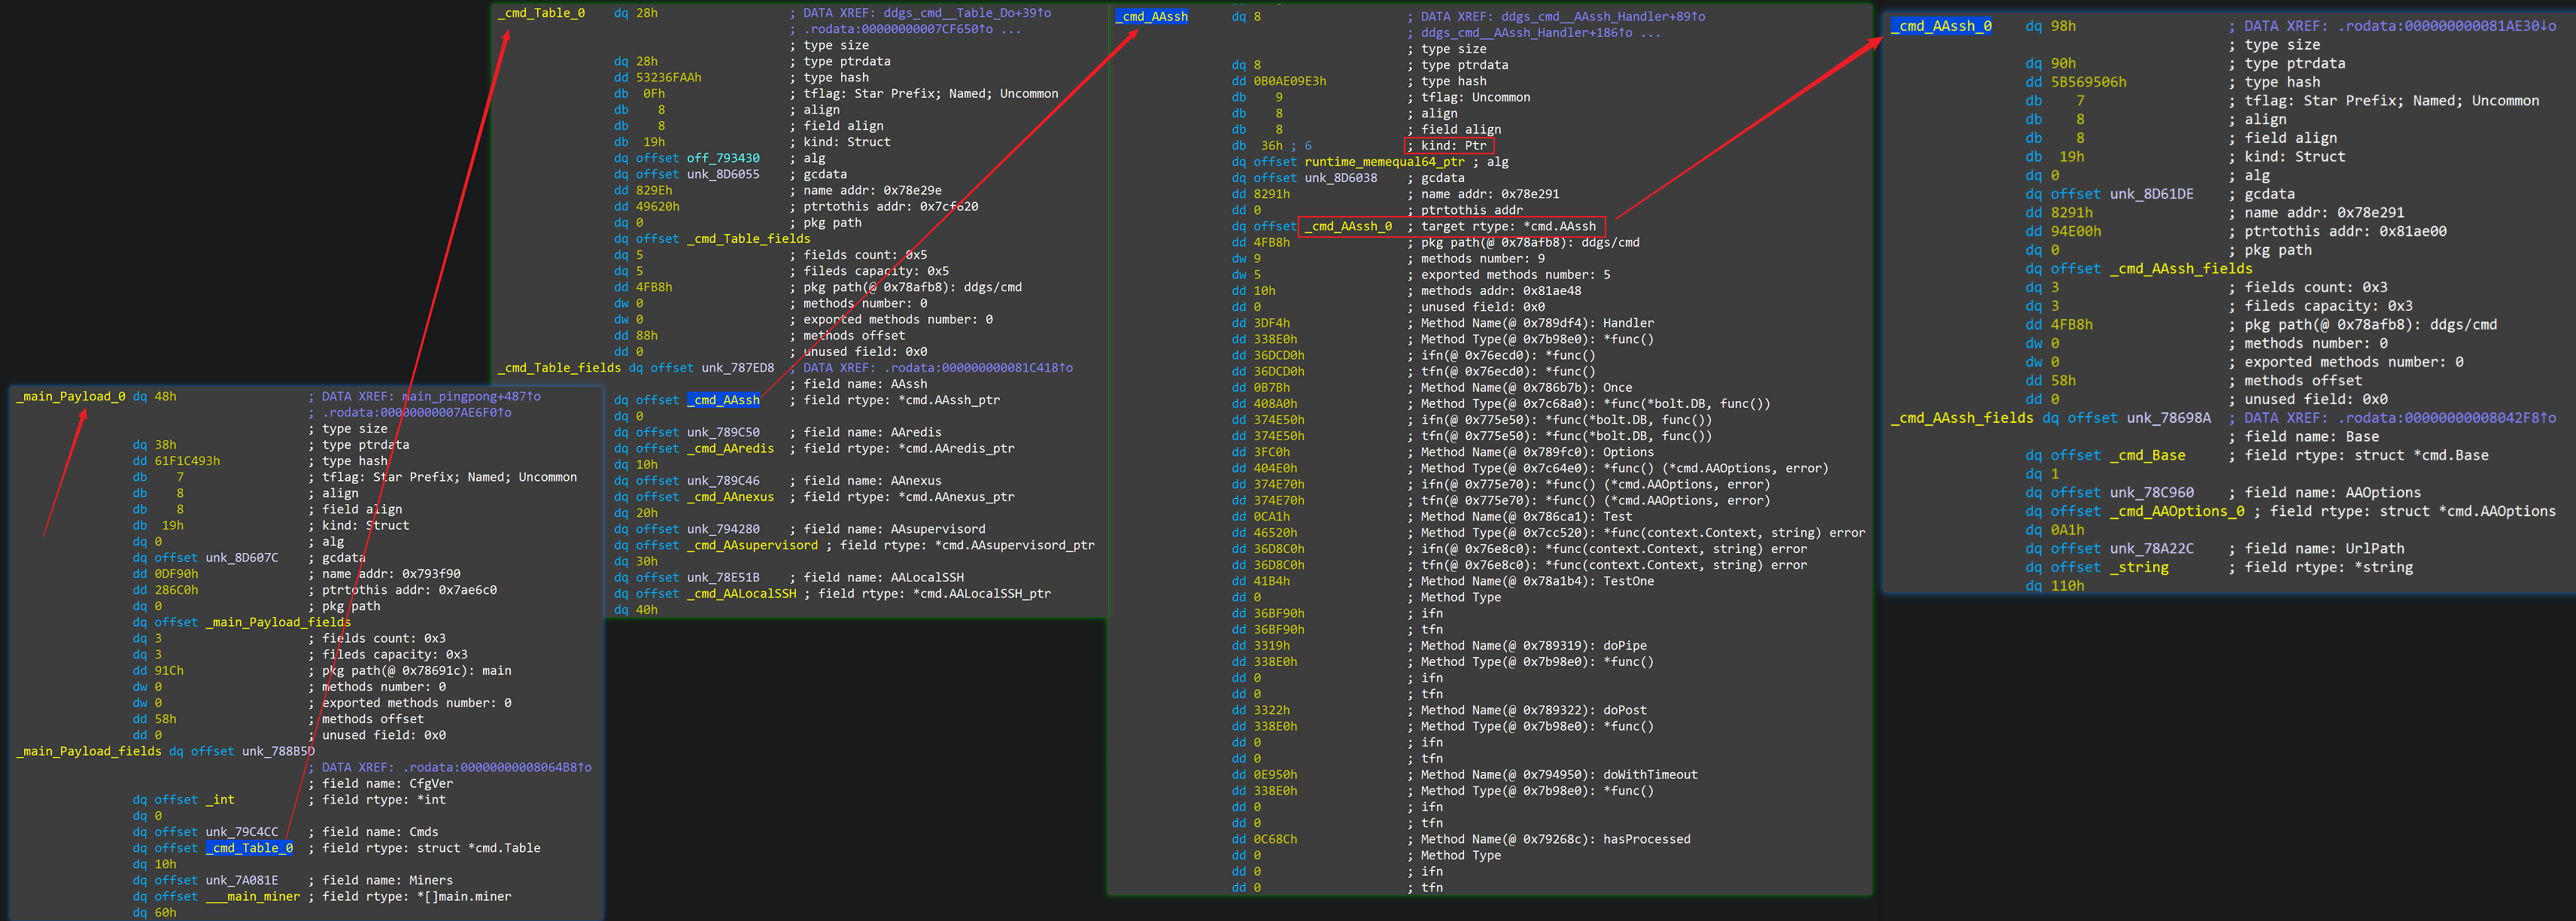 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
 gleaming0/cve-2019-13288
CVE-2019-13288 analysis repository: bundles the Xpdf PDF parser source and documentation to reproduce, analyze, and patch the vulnerable parsing…
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…