Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…

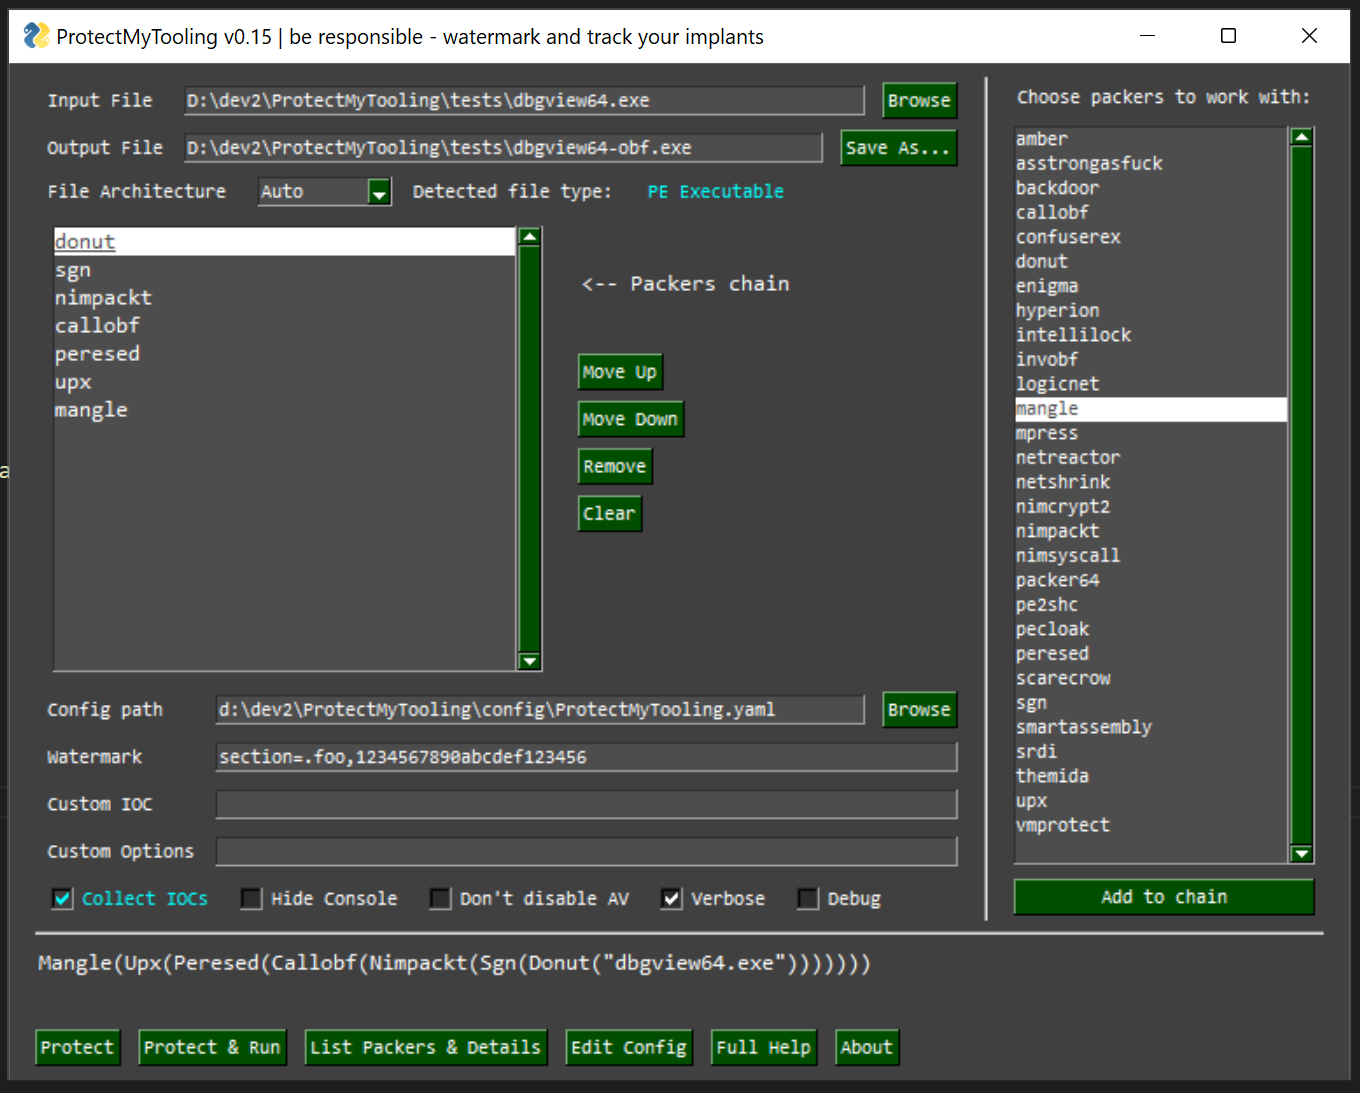
Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

Library for unwinding processor call stacks, supporting multiple architectures and operating systems, with build and regression testing instructions.

C library for stack unwinding and backtrace generation across multiple architectures, providing APIs for programmatic inspection of call stacks and…

C library for stack unwinding and backtrace generation, supporting multiple architectures and operating systems, with build and regression testing…

Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…


A reverse engineering framework written in Python.