
sqlite-rtree-rowid0
 abraxas/sqlite-rtree-rowid0
SQLite 3.53.4 - High - Local - UAF - rtree last_insert_rowid 0 node hash
binary-analysisdatabase-securitydynamic-analysis-sandboxing+5
abraxas/sqlite-rtree-rowid0SQLite 3.53.4 - High - Local - UAF - rtree last_insert_rowid 0 node hash
 oalabs/hashdb-ida
HashDB API hash lookup plugin for IDA Pro
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
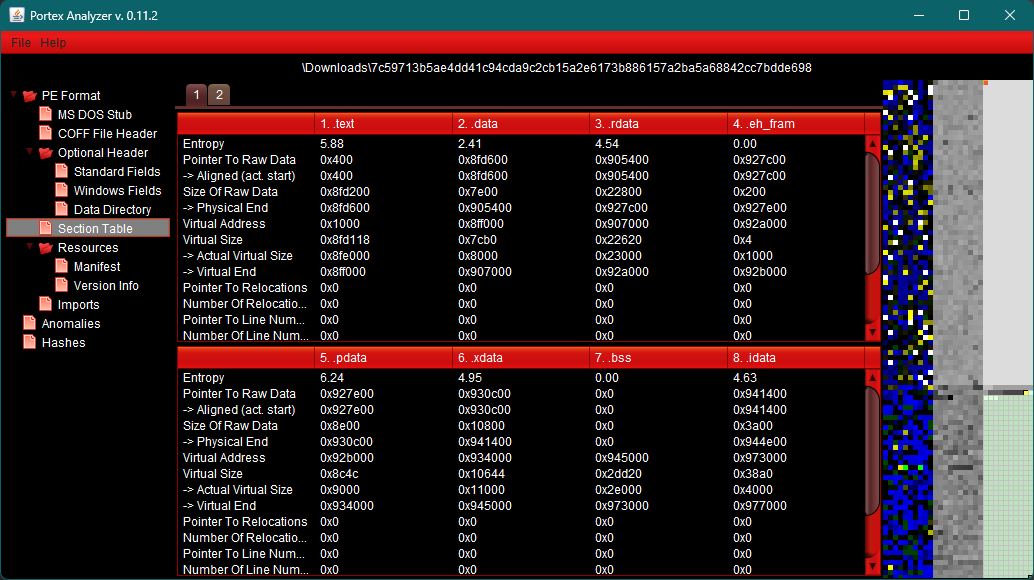 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
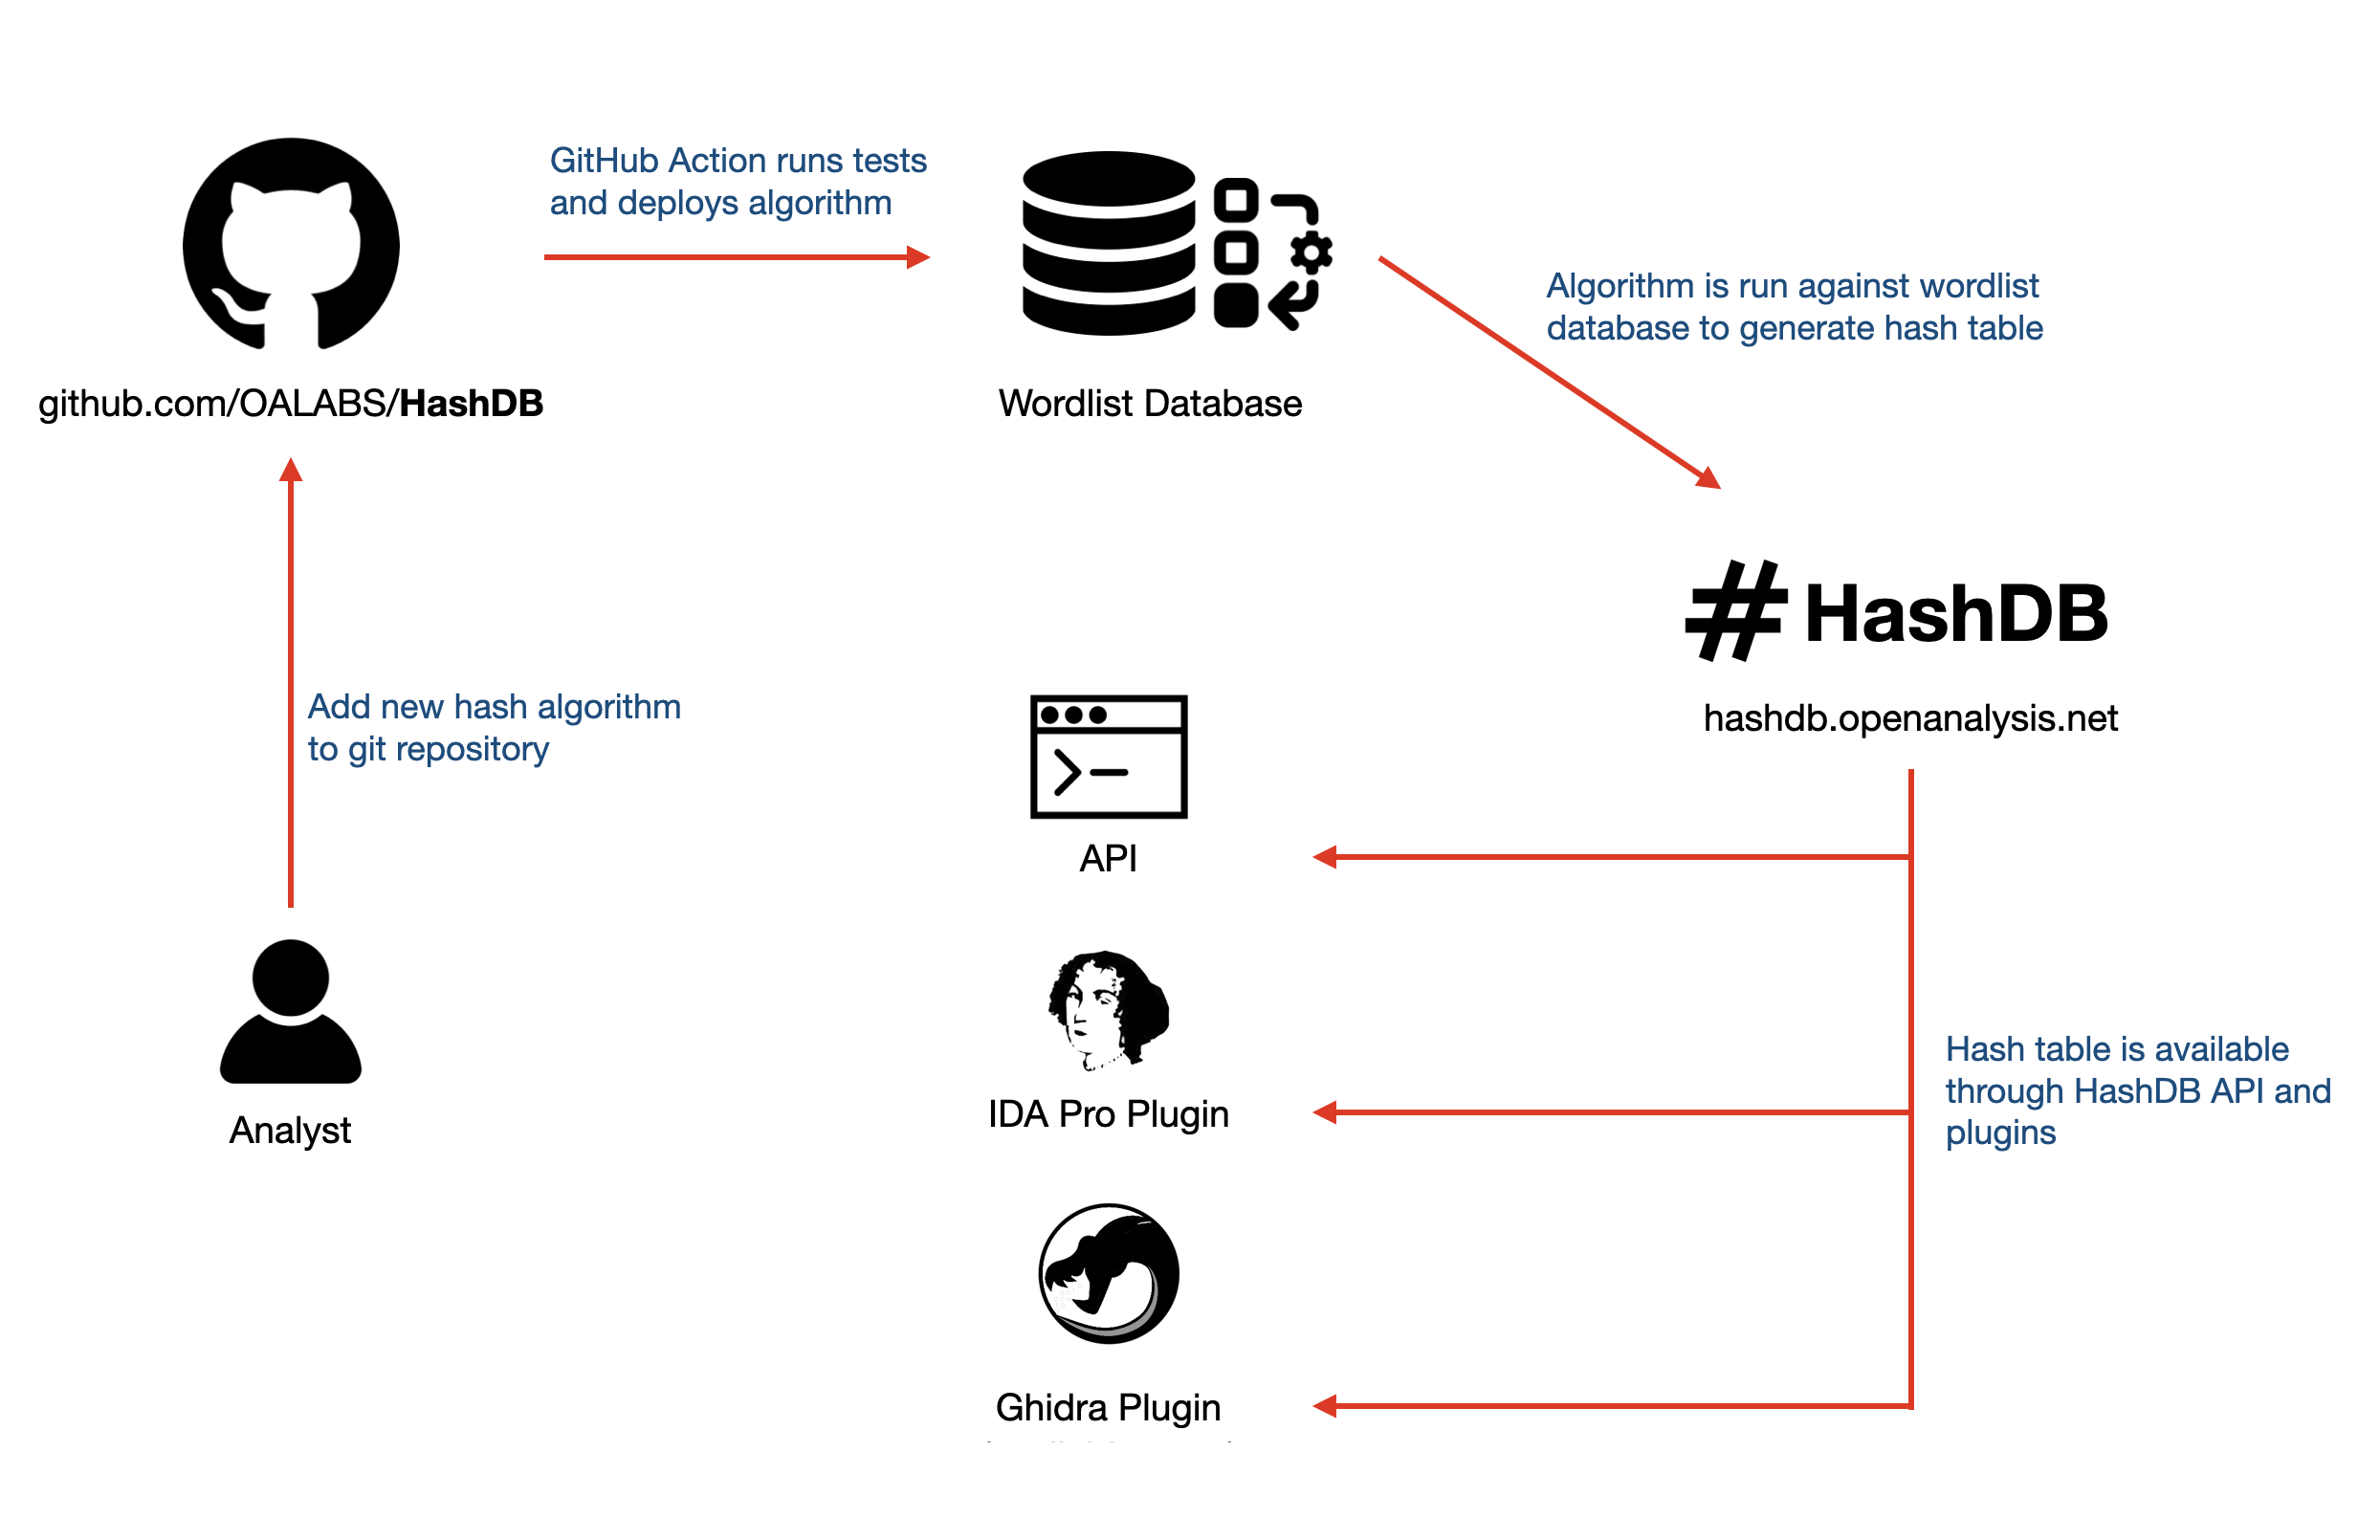 oalabs/hashdb
Assortment of hashing algorithms used in malware
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
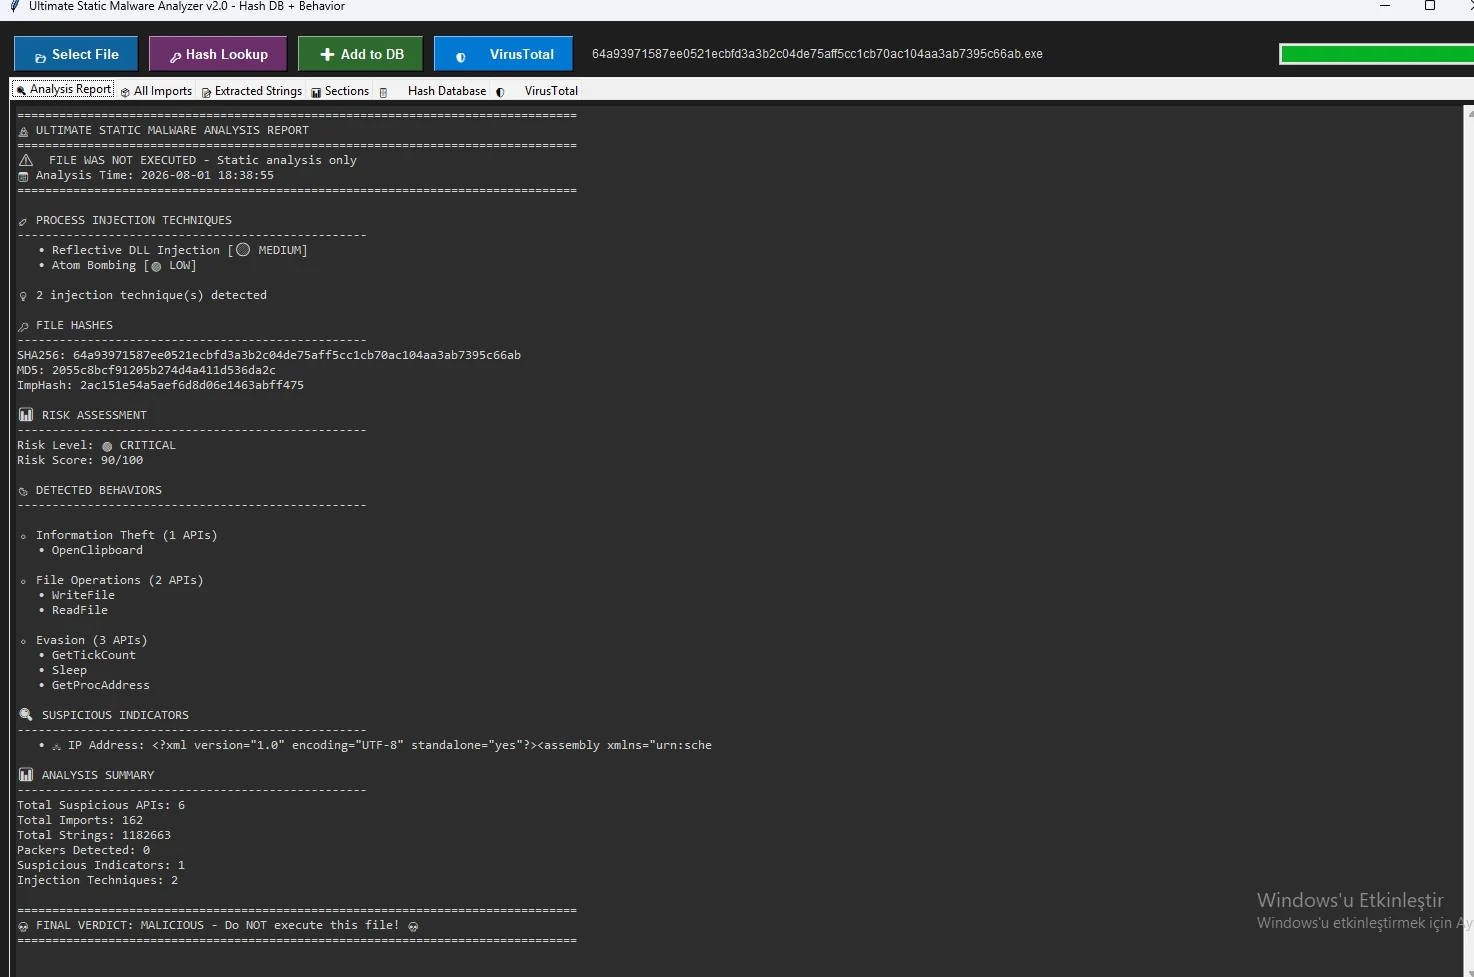 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
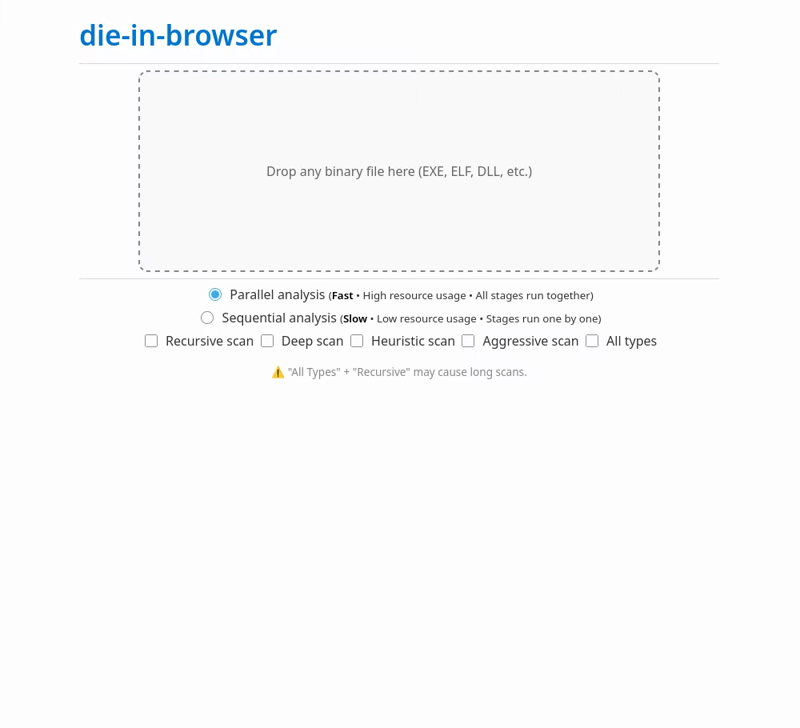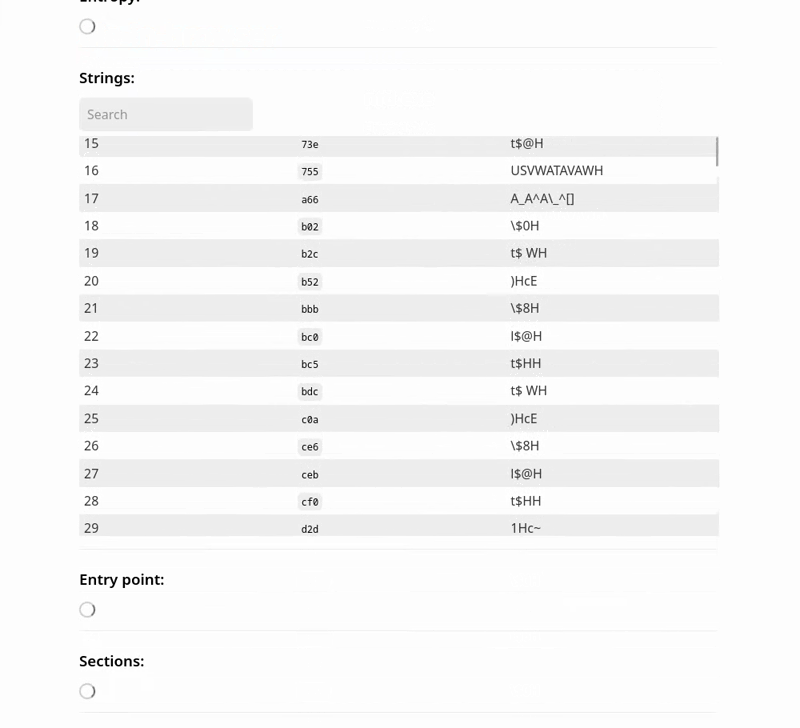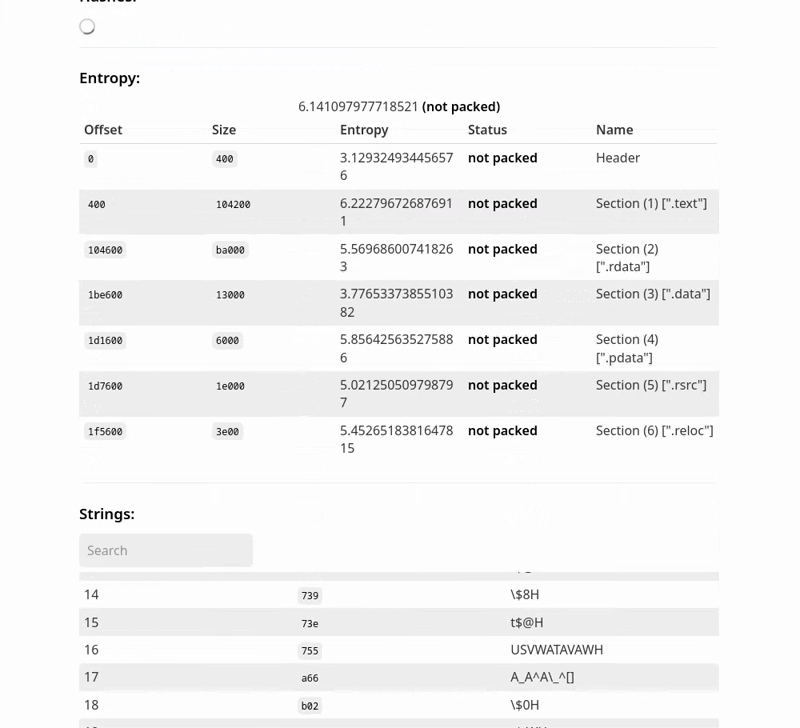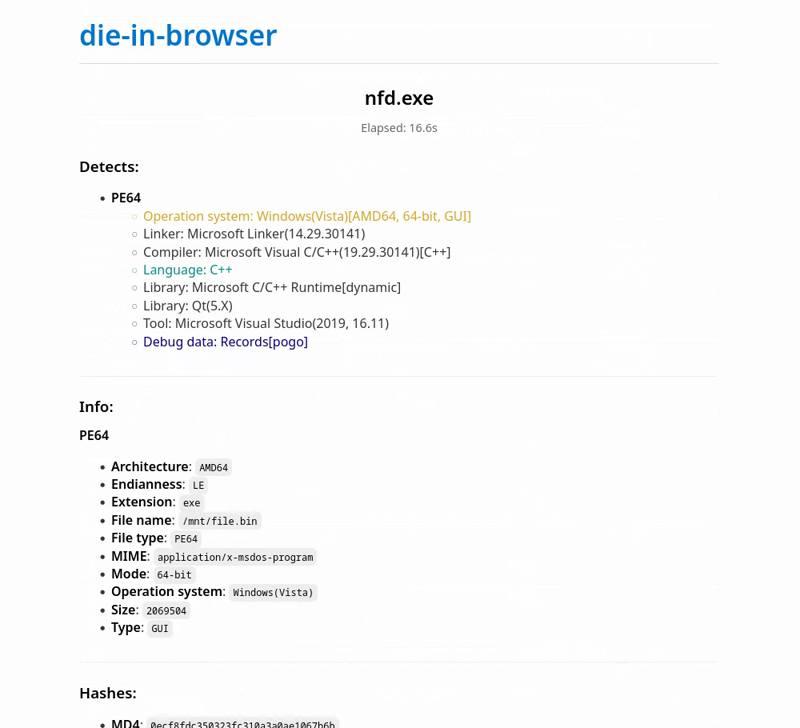 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
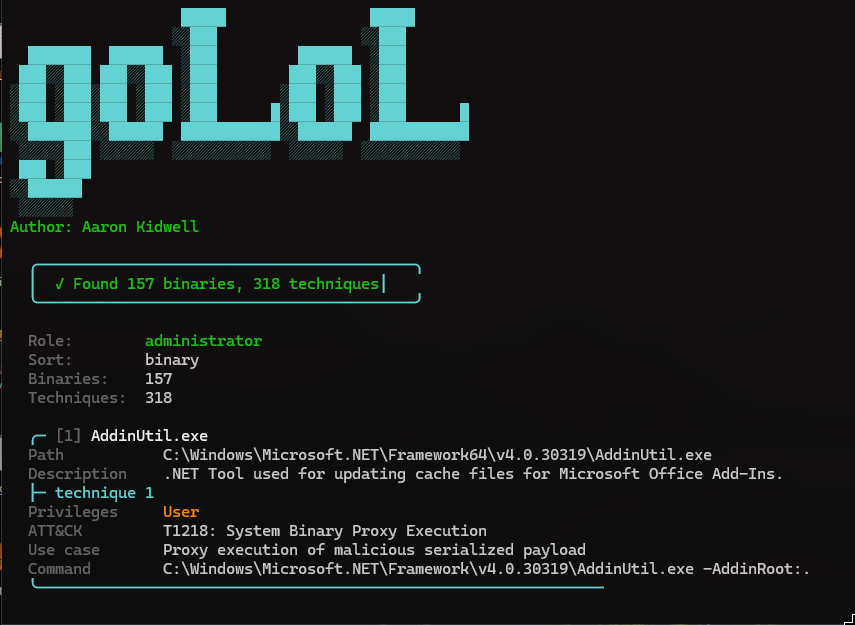 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 onhexgroup/tabpe
A monthly Windows PE baseline dataset for Cyber security researchers
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
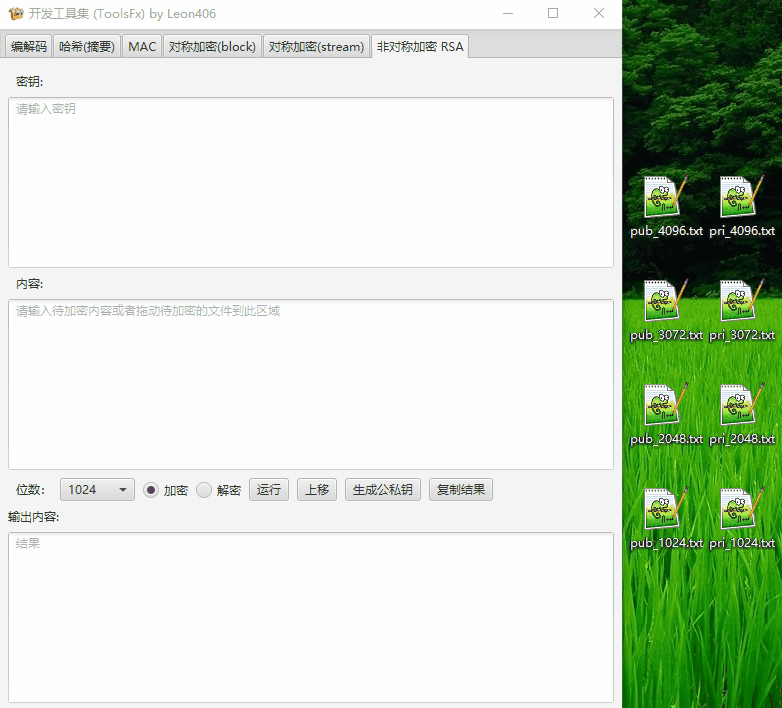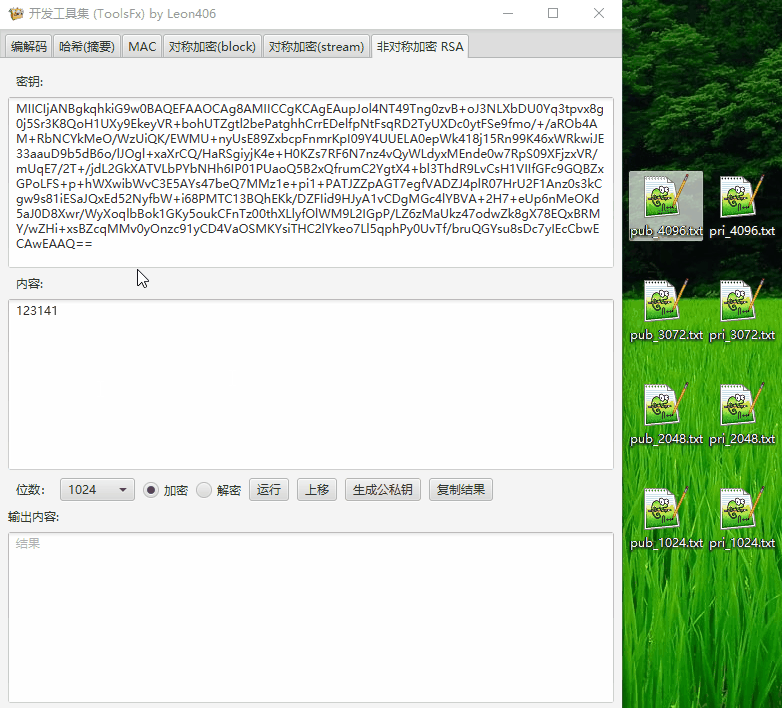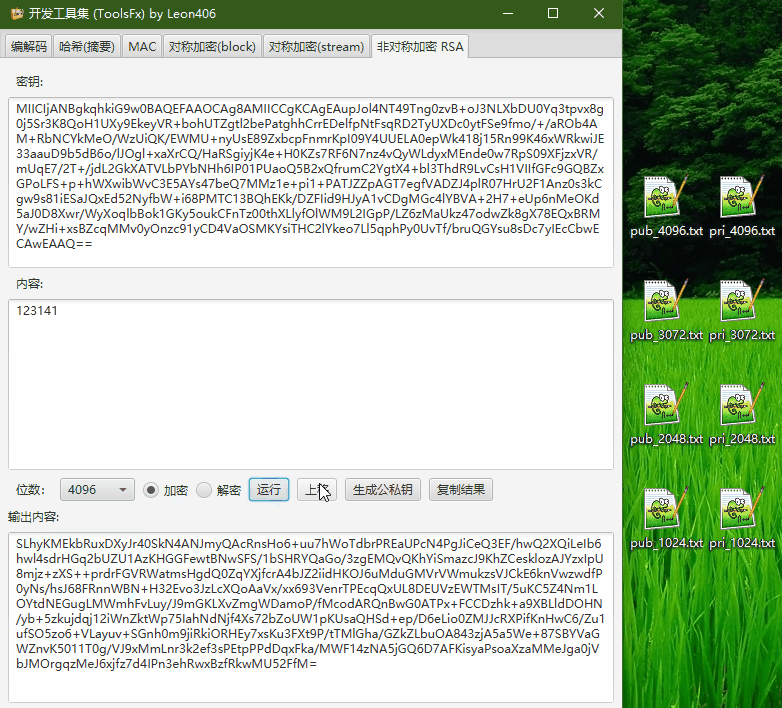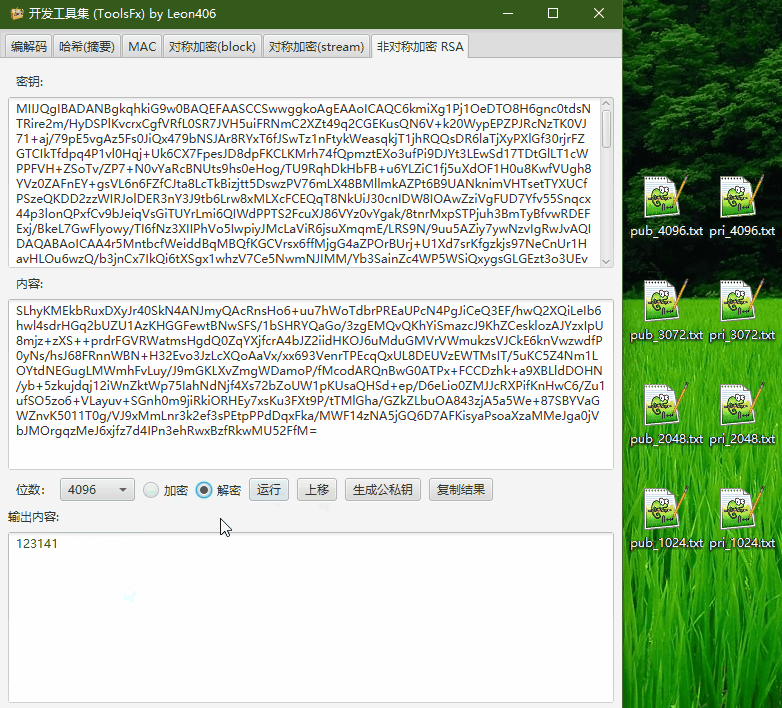 leon406/toolsfx
跨平台密码学工具箱。包含编解码,编码转换,加解密, 哈希,MAC,签名,大数运算,压缩,二维码功能,CTF等功能。
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
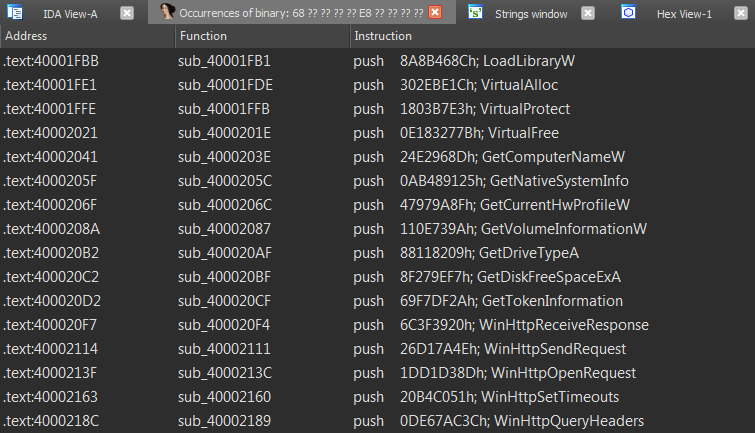 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
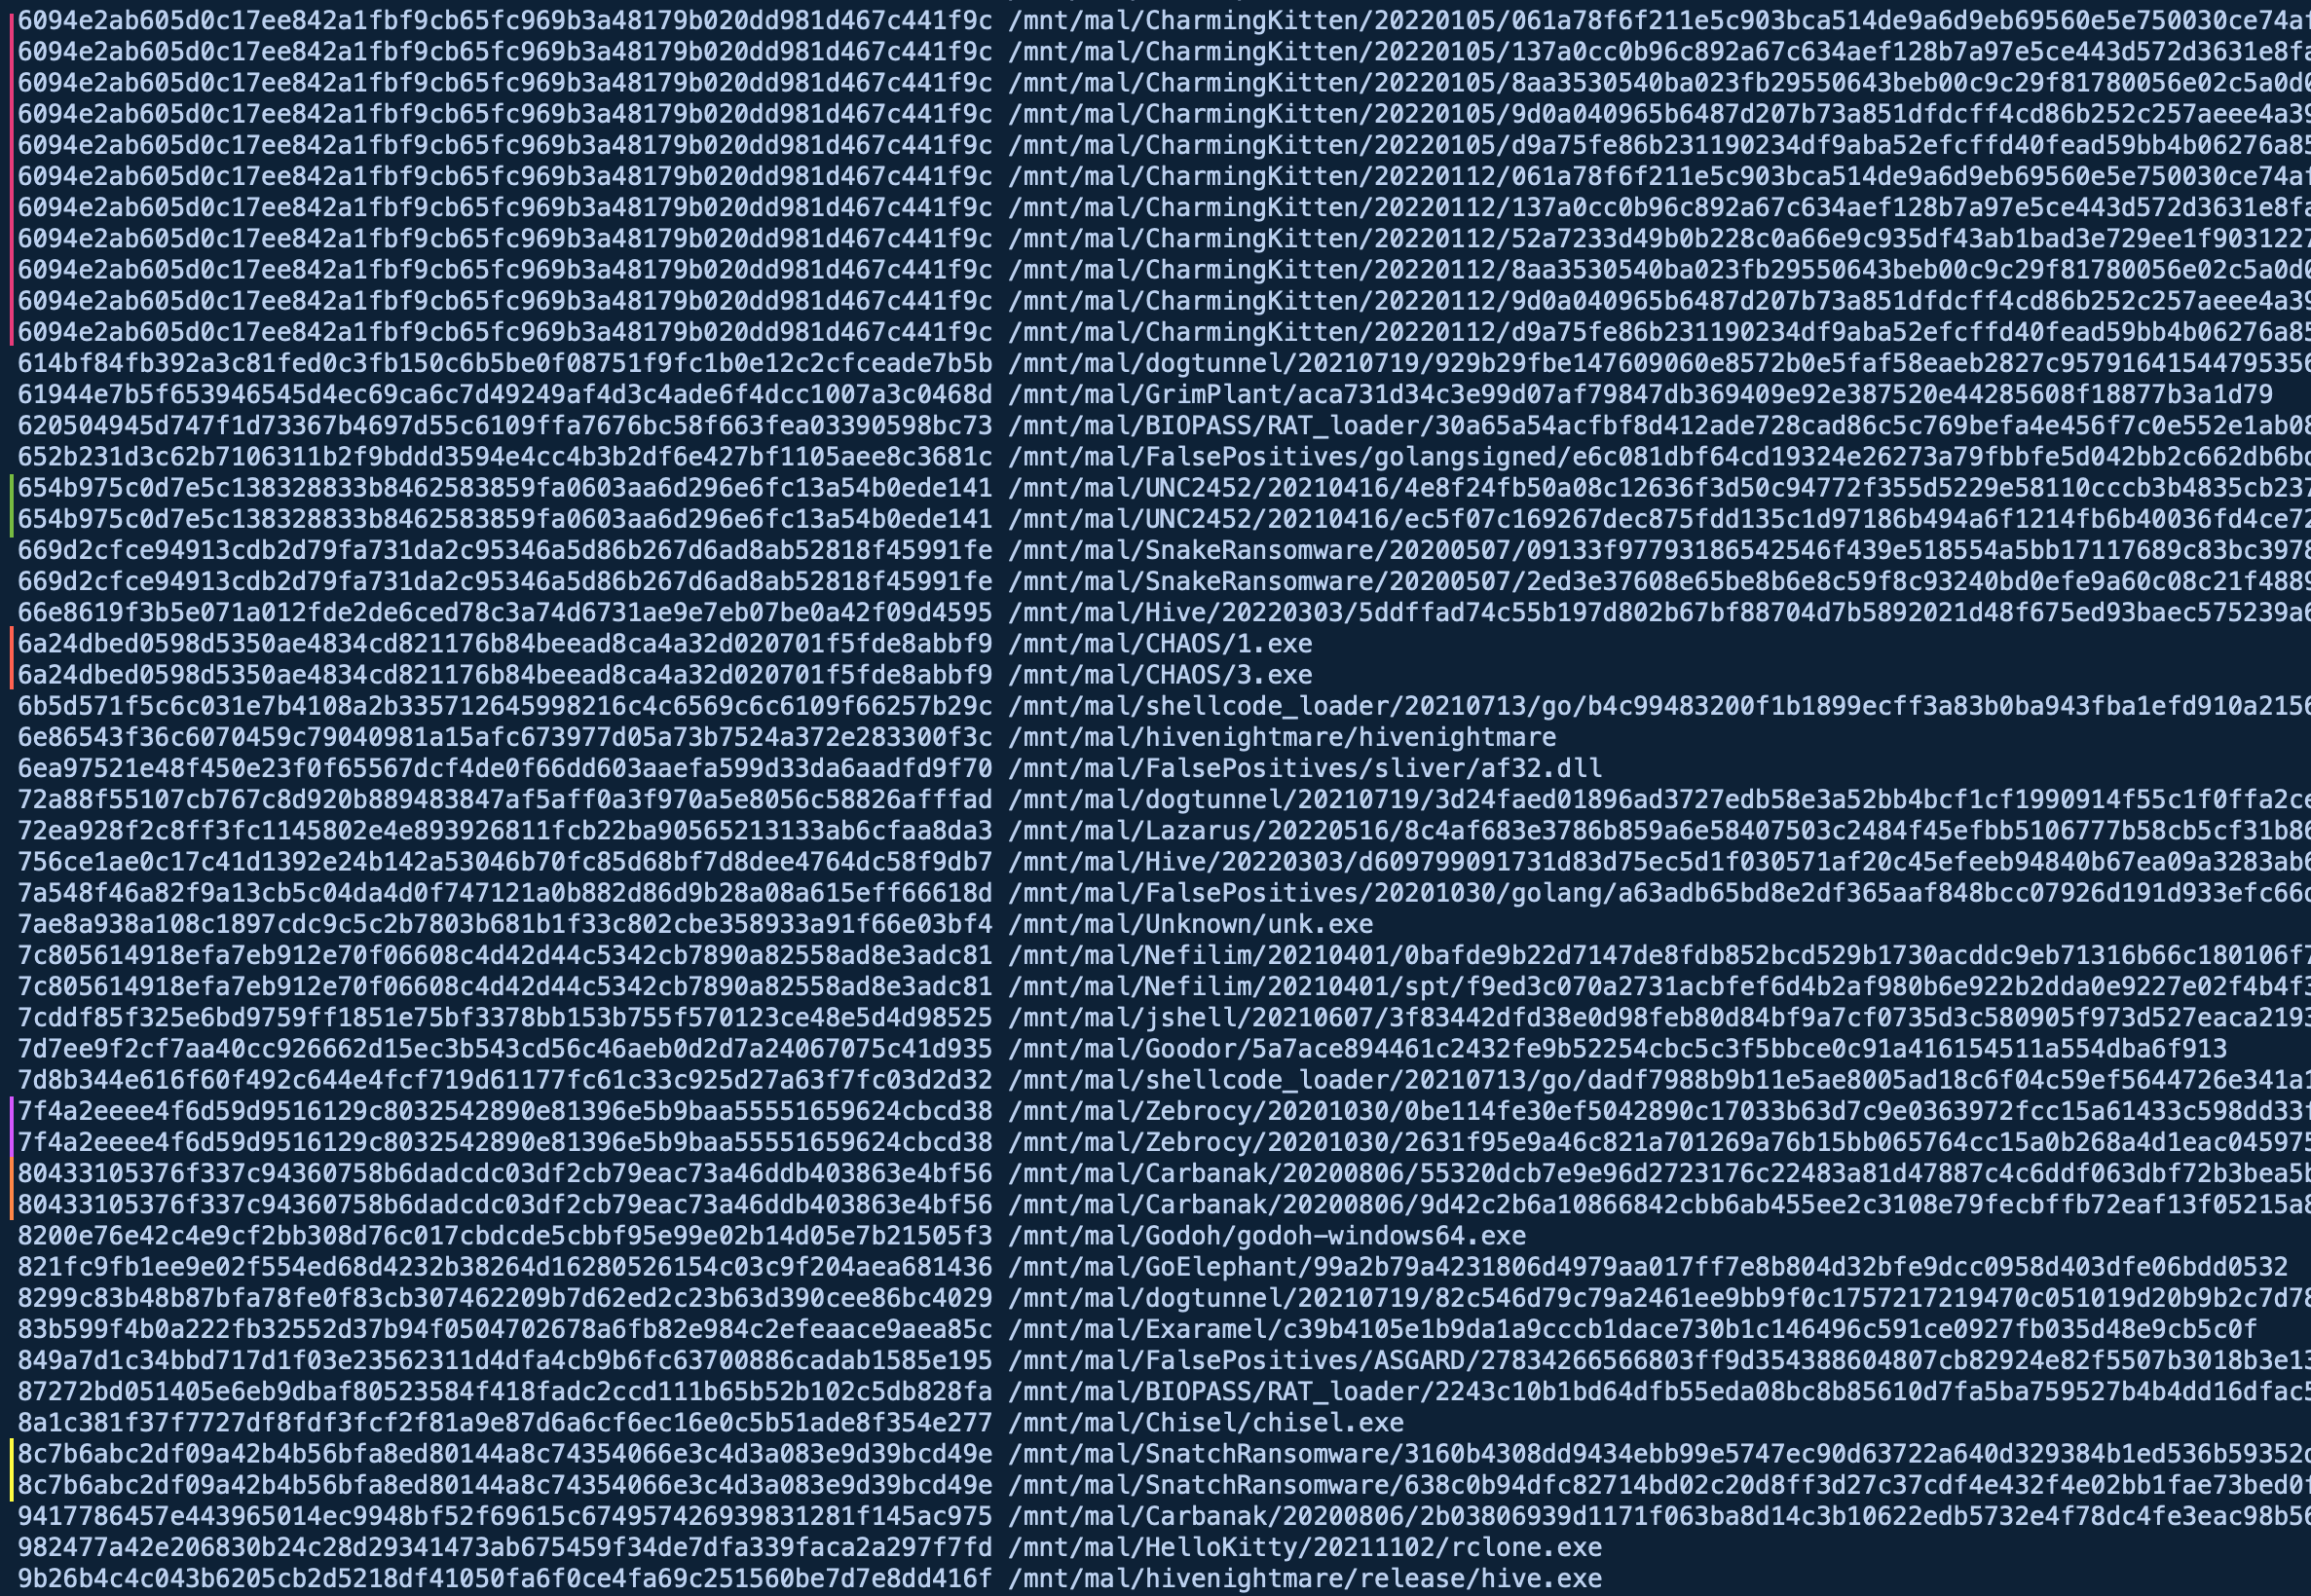 nextronsystems/gimphash
Imphash-like calculation on Golang binaries
 decalage2/collisions
Hash collisions and their exploitations