
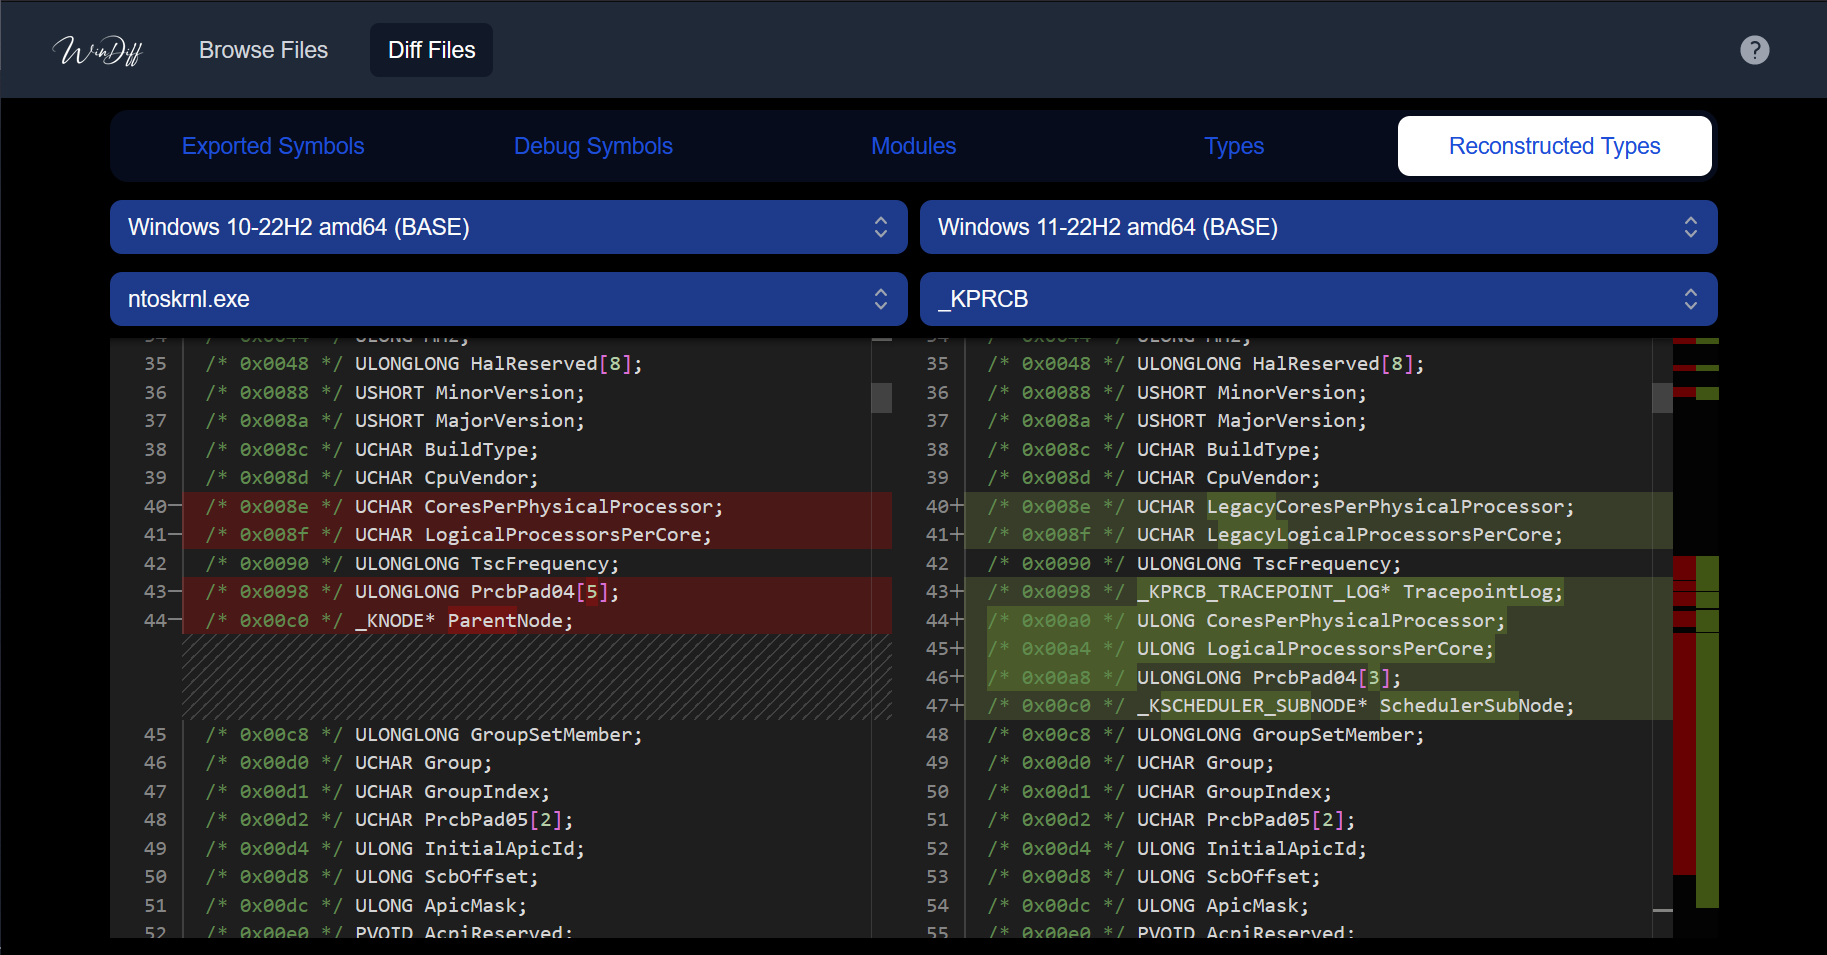
windiff
 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
binary-analysisinformation-gatheringreverse-engineering+1
392
ergrelet/windiffTool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
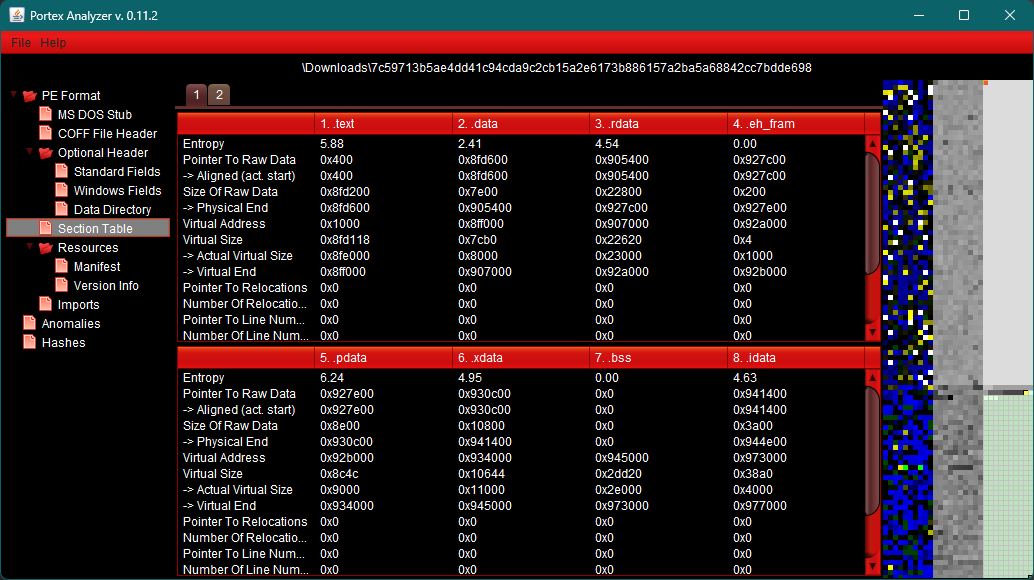 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
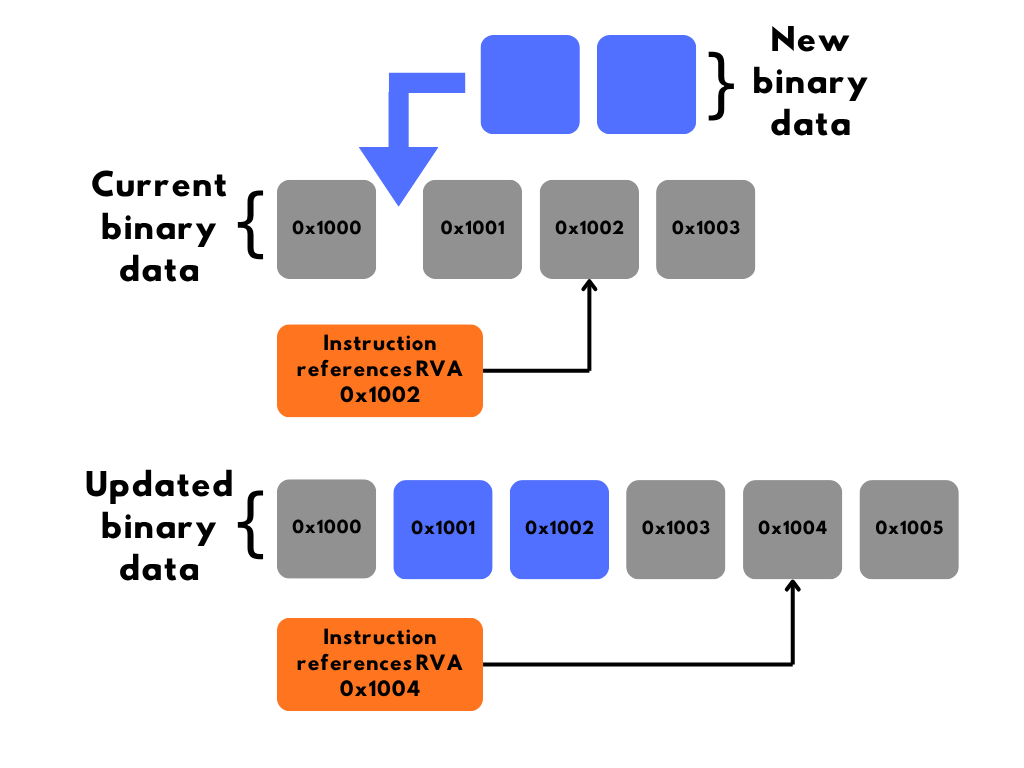 noahware/binprotect
x64 PE bin2bin obfuscator which doesn't add a section to the binary
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
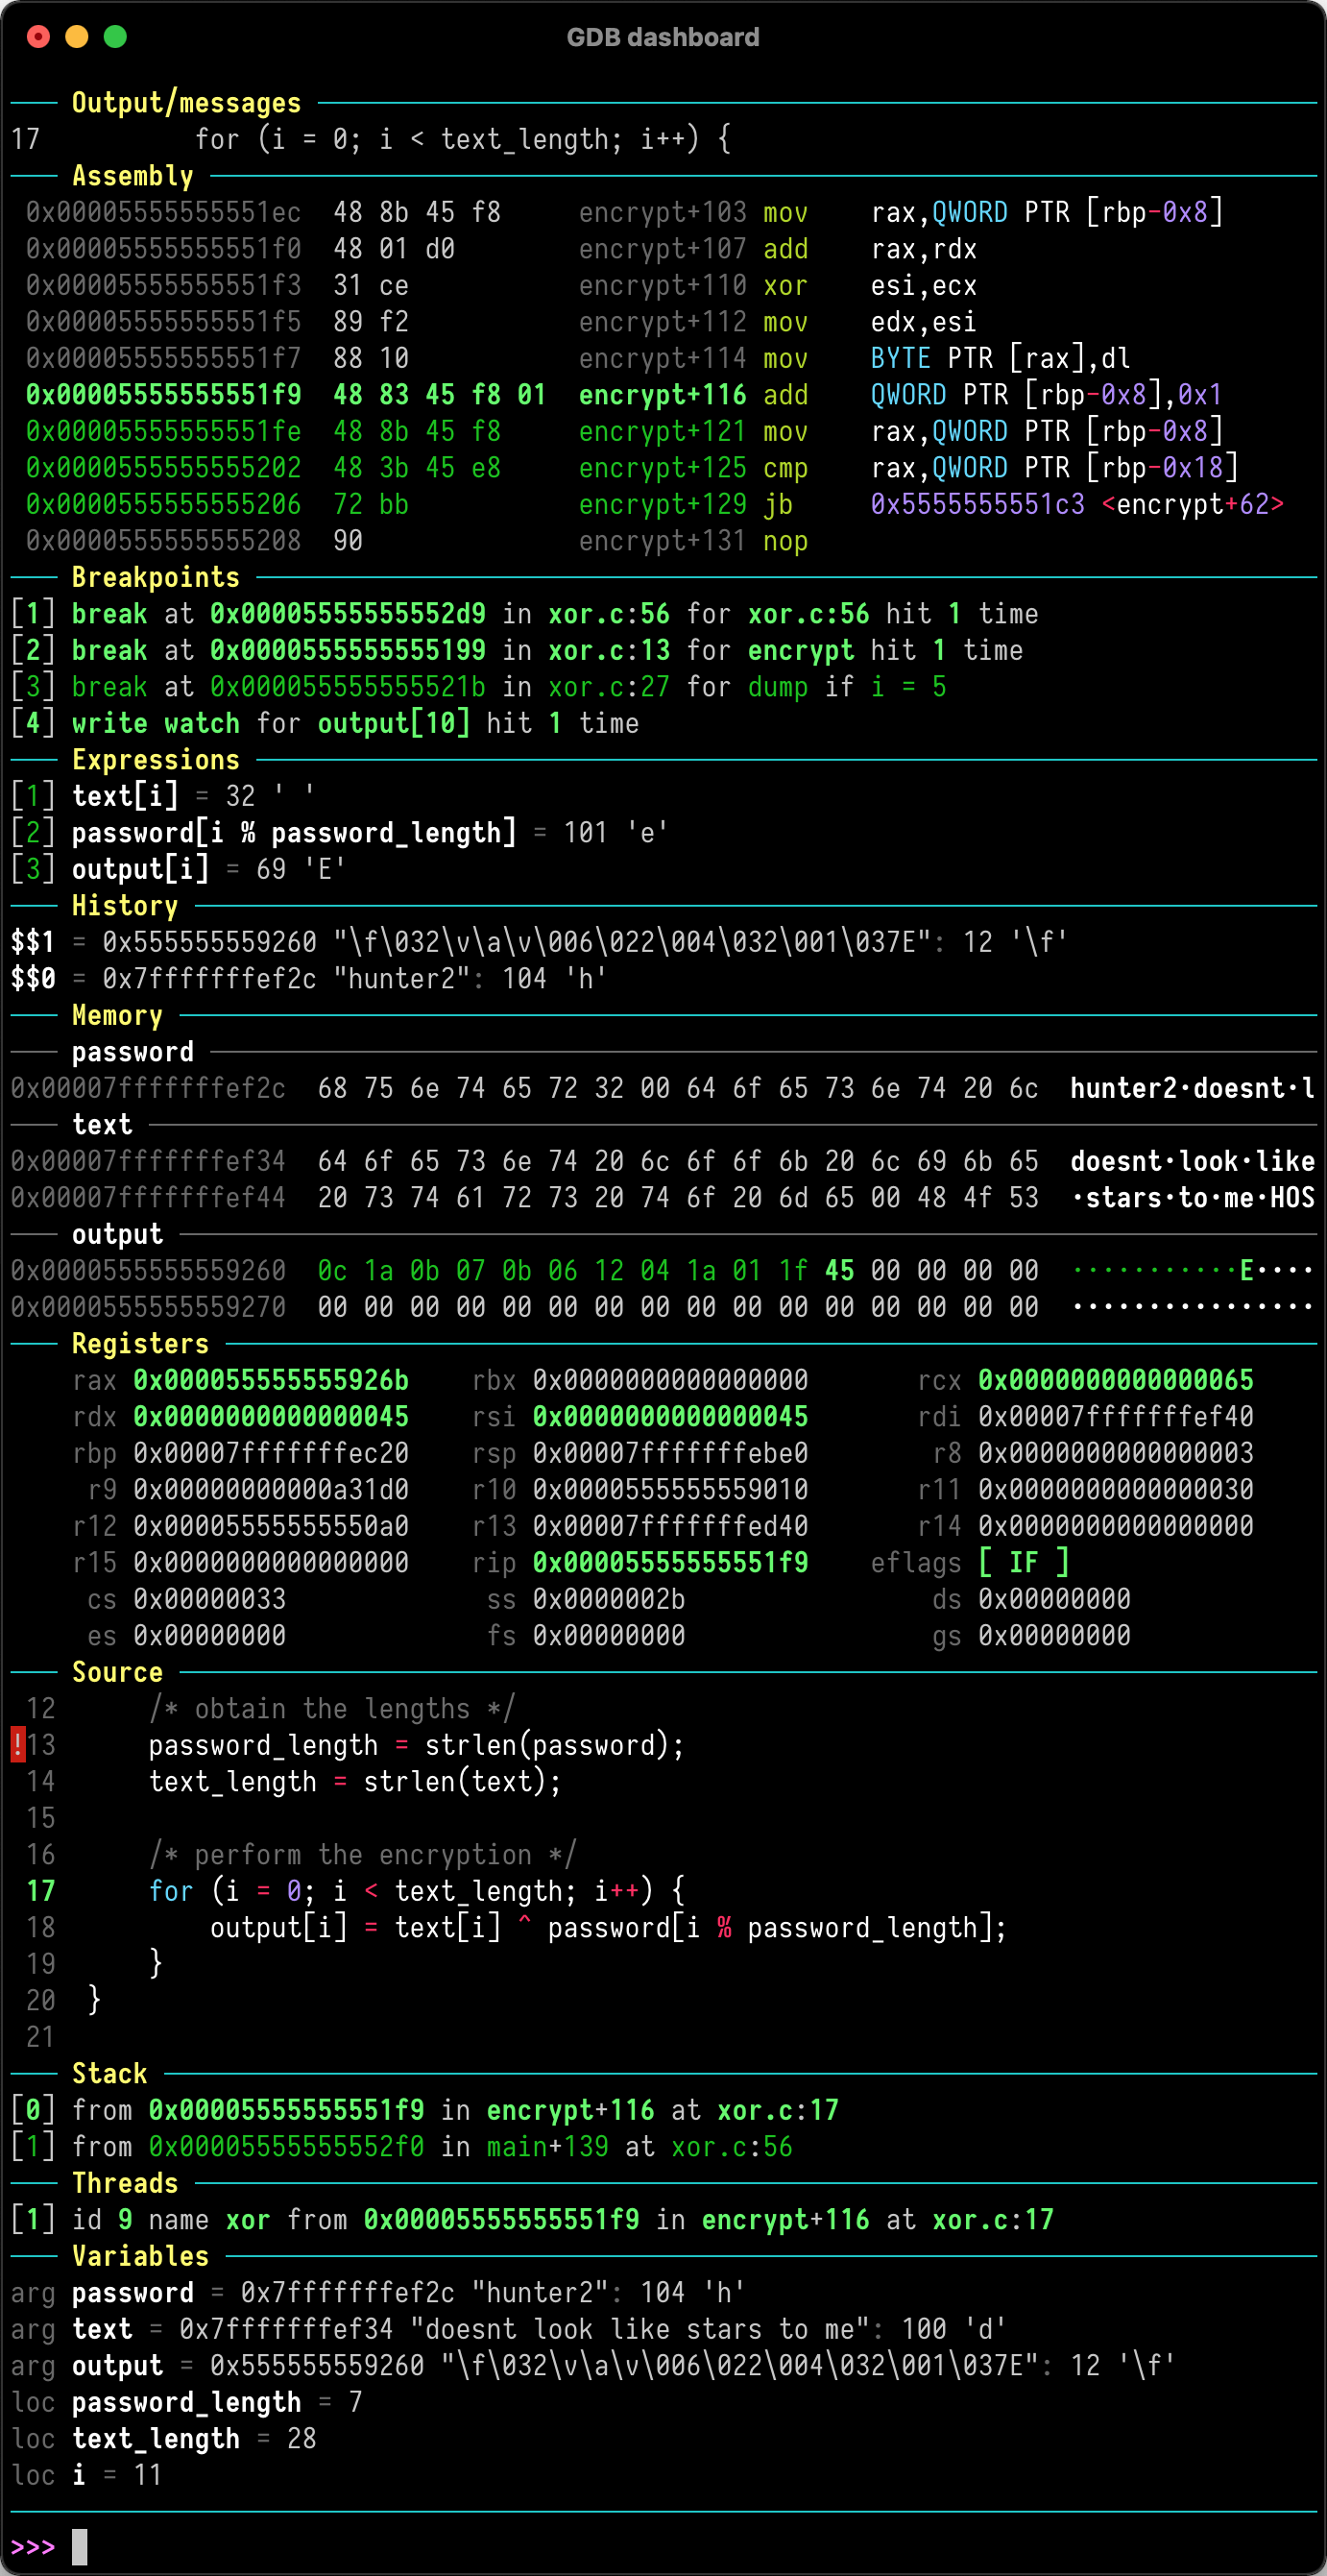 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 kaandemir993/vidar-stealer-reverse-engineering
"In-depth reverse engineering analysis of Vidar Stealer 2.0 covering Task Scheduler tampering (1999 timestamps), Explorer.exe process hollowing, and…
 zodiacon/alltools
All reasonably stable tools
 onhexgroup/tabpe
A monthly Windows PE baseline dataset for Cyber security researchers
 sita-technologies/cve-2025-39247
HikCentral Professional - Pre-Auth License ActiveCode Leak
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
 whokilleddb/psi_bof
A BOF designed to inspect processes memory and addresses
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.