
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
dd preview

dd

GitHubricccrd/dd

JIT-based userspace Linux kernel that runs containers natively on Apple Silicon macOS without a VM. Drop-in Docker Engine API replacement with…
binary-analysiscontainer-securitydevsecops+3
259
2 days ago
linux-insides preview

linux-insides

GitHub0xax/linux-insides

A book-in-progress about the Linux kernel and its insides.
binary-analysiscurated-resourceseducation+2
33.5k2 days ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
18512 days ago
KernelPatch preview

KernelPatch

GitHubbmax121/kernelpatch

Patching and hooking the Linux kernel with only a stripped Linux kernel image.
android-securitybinary-analysisbinary-exploitation+7
1.5k17 days ago
KernelPatch preview

KernelPatch

GitHublyravoid/kernelpatch

Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
android-securitybinary-analysisbinary-exploitation+6
1018 days ago
wtf preview

wtf

GitHub0vercl0k/wtf

Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k22 days ago
memory-forensic preview

memory-forensic

GitHubsecurityronin/memory-forensic

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
binary-analysiscontainer-escapedata-recovery+7
101 month ago
linux-kernel-algif-aead-checker preview

linux-kernel-algif-aead-checker

GitHubridhinva/linux-kernel-algif-aead-checker

Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
binary-analysisexploitationvulnerability-analysis+1
1 month ago
cve-2023-20768 preview

cve-2023-20768

GitHubmurf-xd/cve-2023-20768

Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
android-securitybinary-analysisbinary-exploitation+4
1 month ago
HyperDbg preview

HyperDbg

GitHubhyperdbg/hyperdbg

State-of-the-art native debugging tools

binary-analysisdebuggerseducation+4
4.1k1 month ago
kernel-c-to-rust-spike preview

kernel-c-to-rust-spike

GitHubruntimeverification/kernel-c-to-rust-spike

Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).
binary-analysiseducationfuzzing+4
11 month ago
Linux-Kernel-Copy-Fail-CVE-2026-31431- preview

Linux-Kernel-Copy-Fail-CVE-2026-31431-

GitHubjihwan77/linux-kernel-copy-fail-cve-2026-31431-

Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…
binary-analysiseducationexploitation+2
2 months ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
LID preview

LID

GitHubazqzazq1/lid

LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
binary-analysiseducationexploitation+6
203 months ago
CVE-2026-31431-Analysis-and-Fix preview

CVE-2026-31431-Analysis-and-Fix

GitHubabdelkabirouadoukou/cve-2026-31431-analysis-and-fix

In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
binary-analysiscurated-resourceseducation+3
24 months ago
gobee preview

gobee

GitHubboratanrikulu/gobee

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
binary-analysiscode-analysisdevsecops+3
3484 months ago
CopyFail-for-dummies preview

CopyFail-for-dummies

GitHubchernstepanov/copyfail-for-dummies

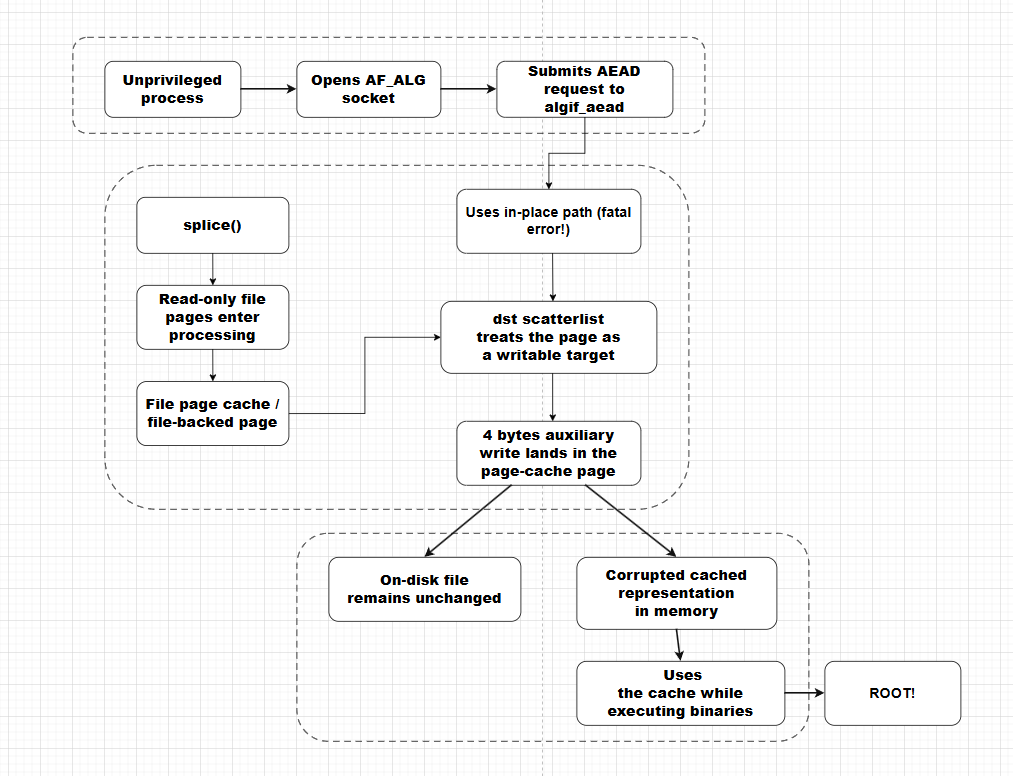
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
binary-analysiseducationexploitation+2
14 months ago
ane preview

ane

GitHubeiln/ane

Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…

ai-securitybinary-analysisembedded-systems-security+3
5072 years ago
Previous123Next