
pefile
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
erocarrera/pefilepefile is a Python module to read and work with PE (Portable Executable) files
 ariyanpegu/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
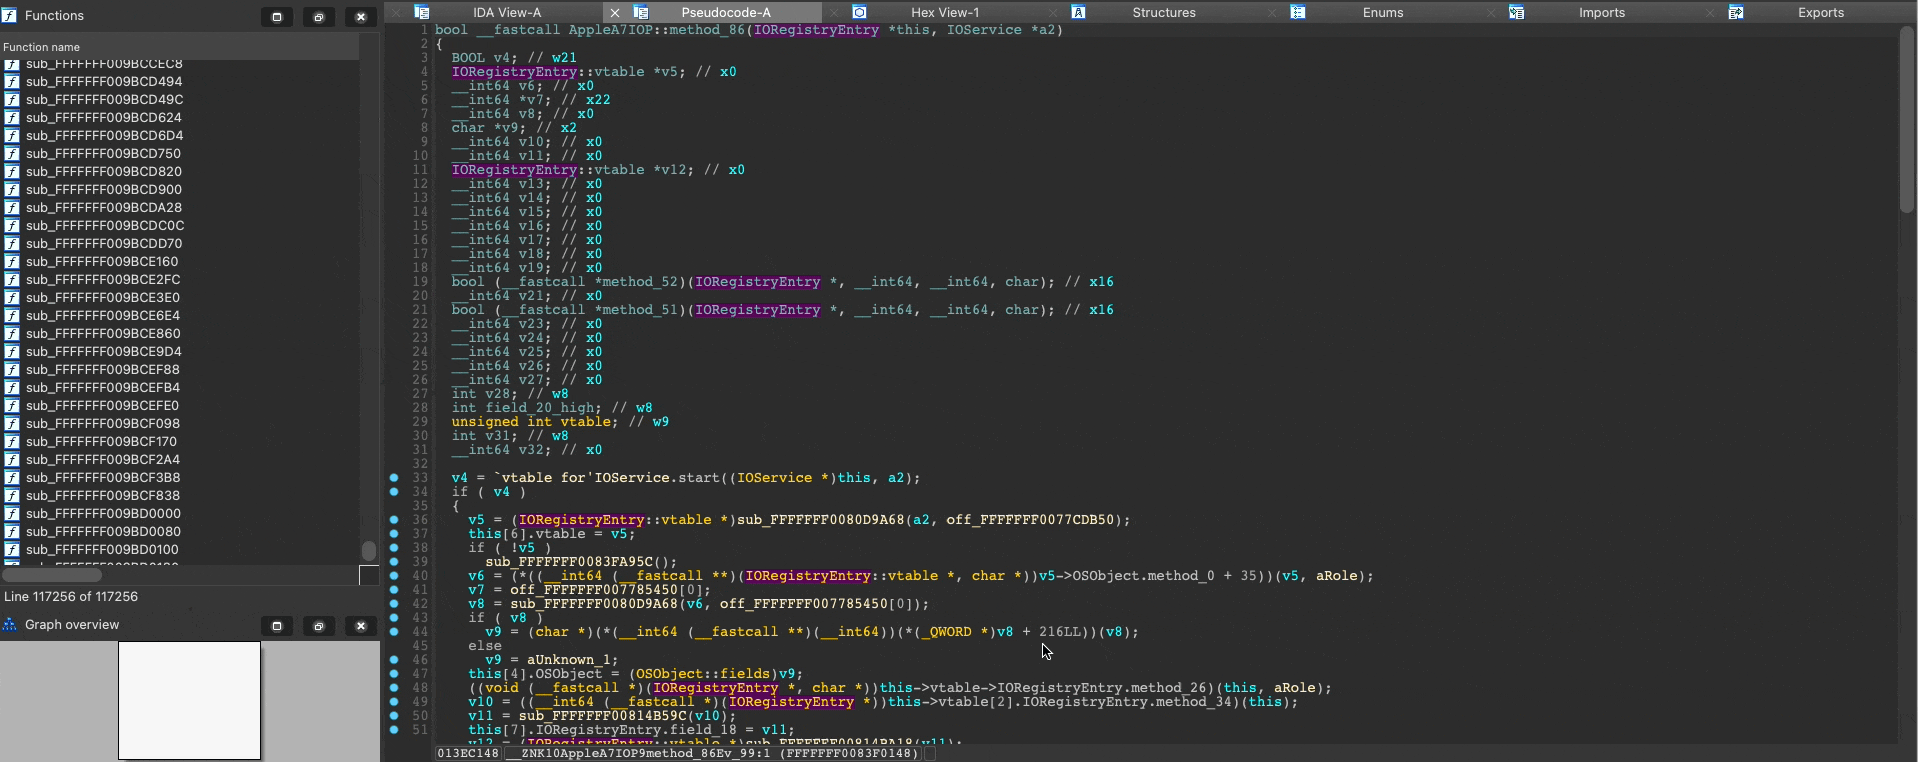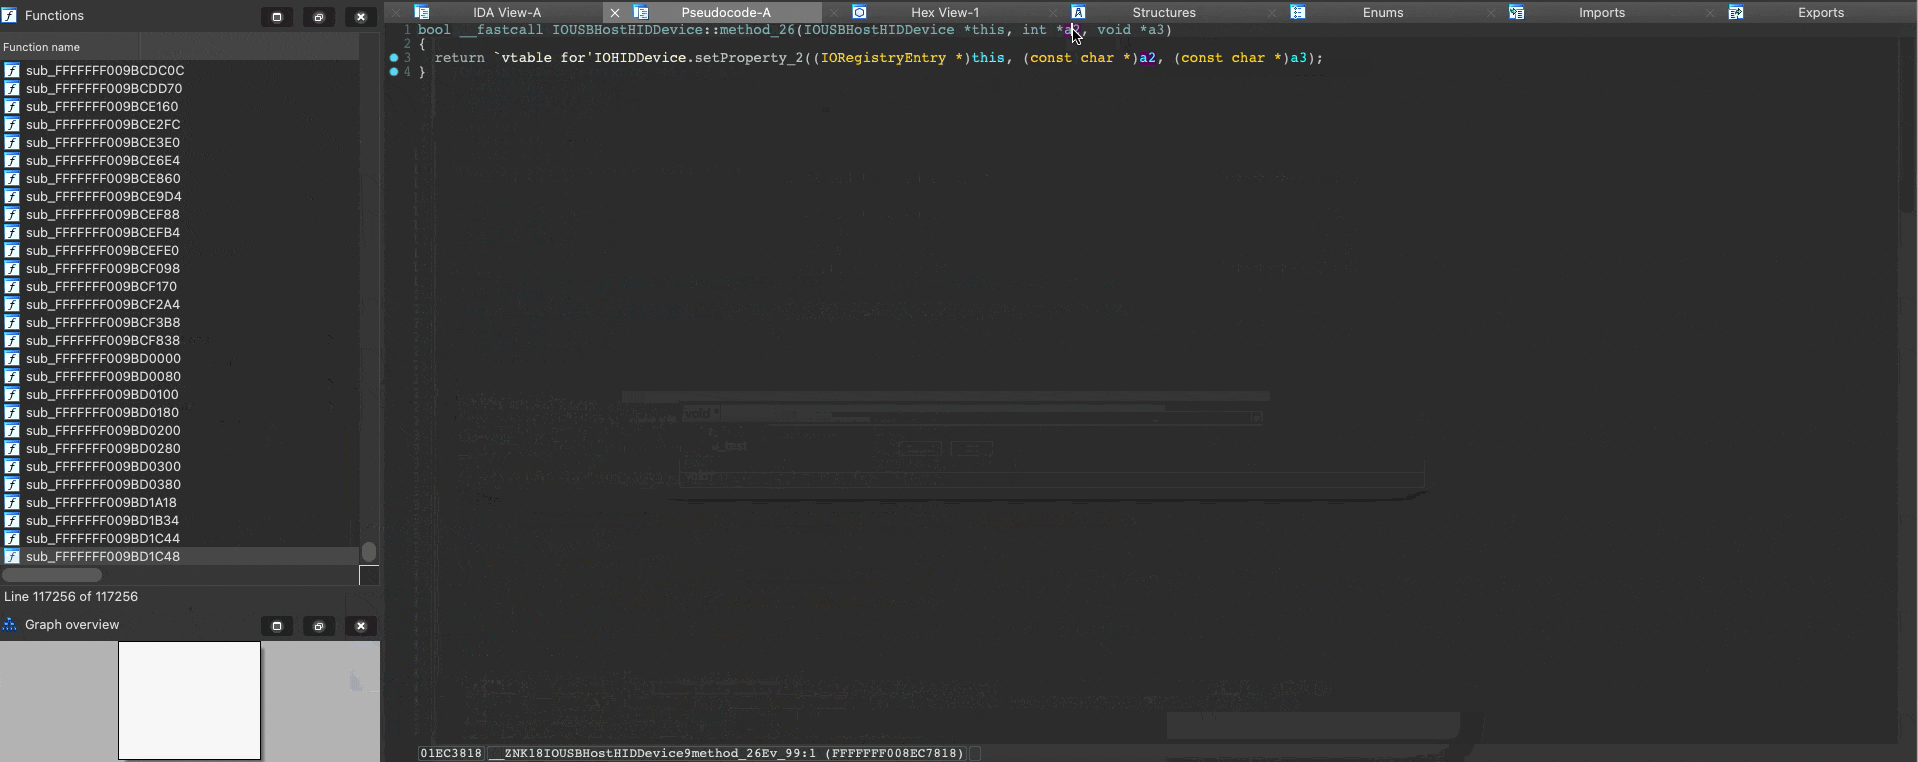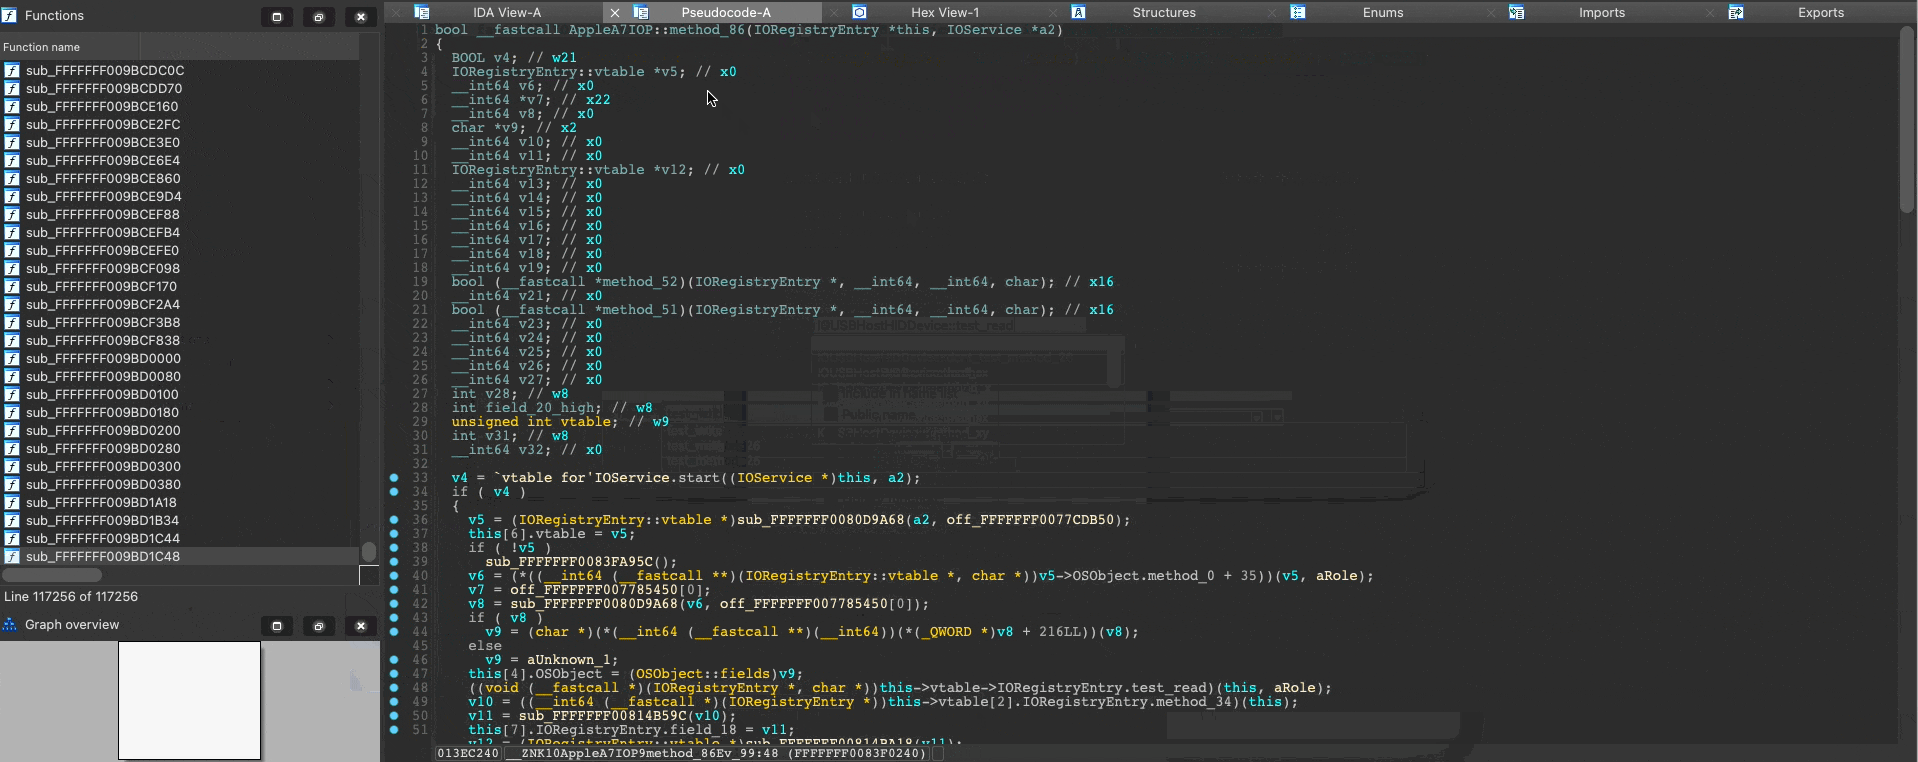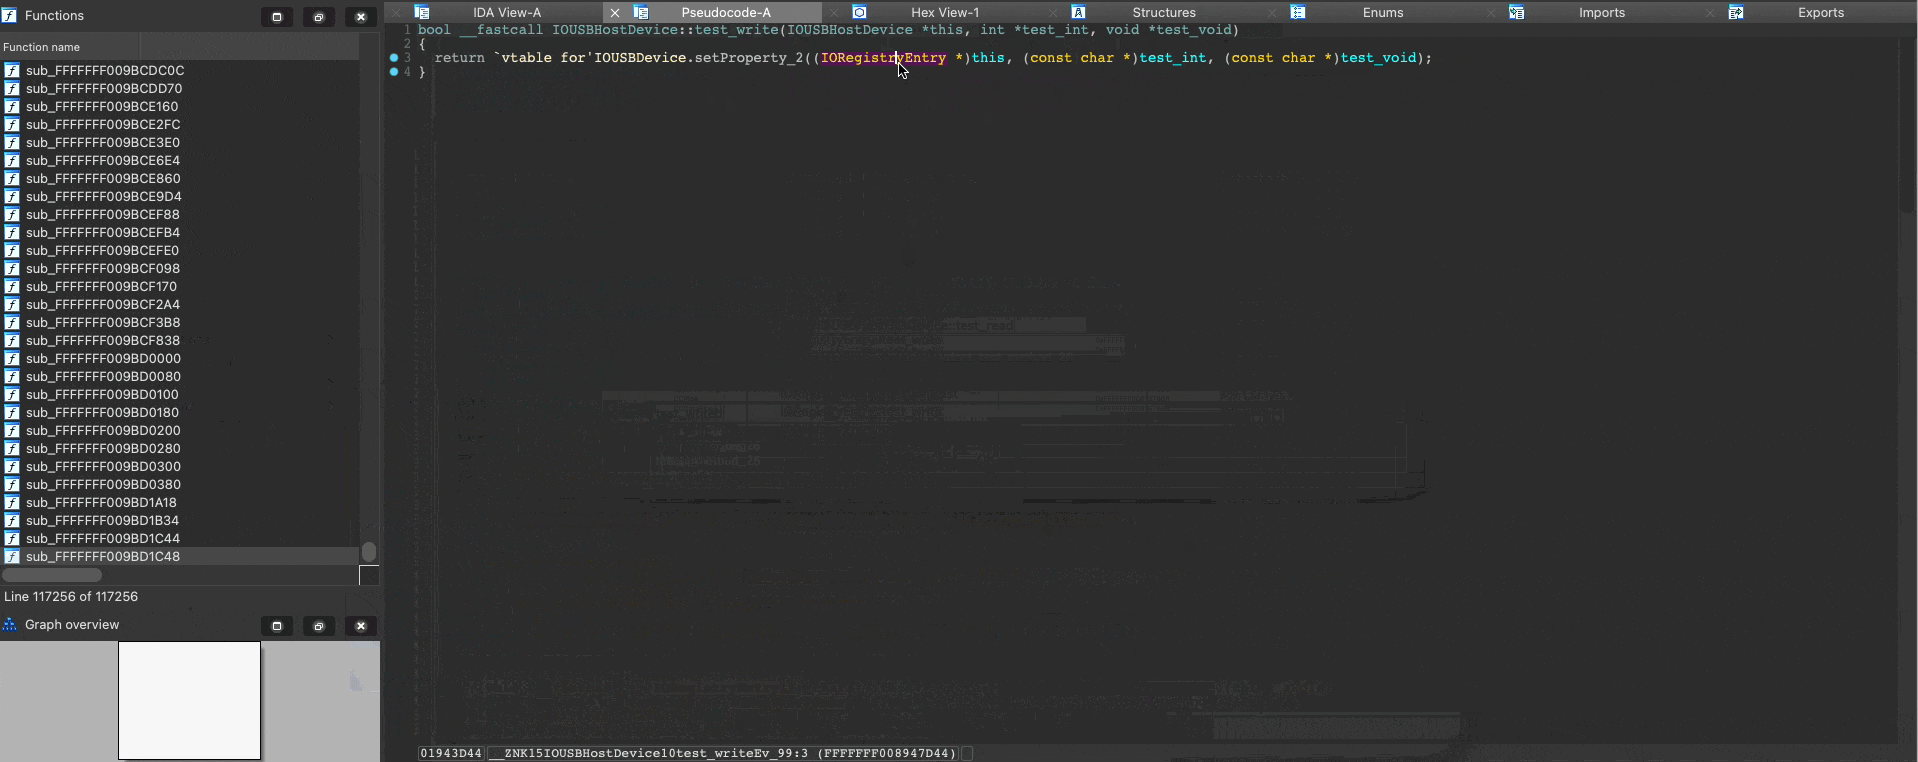 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 vichhka-git/magisk-renef
Magisk module that auto-packages renef_server (dynamic instrumentation for Android)
 20enderdude20/ghidra_v810_v830
Ghidra processor description module for NEC/Renesas v810 and v830 families
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 eversinc33/drvtrace
WinDbg plugin to trace module transitions from a debugged driver.
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 theatha/yara_for_config_extraction
Tutorial and source code for building a custom YARA module in C to extract malware configurations, with a practical Danabot example and reusable…
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 lodi-g/cve-2023-33668
Technical analysis and proof-of-concept bypass for CVE-2023-33668 in DigiExam proctoring software, demonstrating weak VM detection and native module…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…