

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.8k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 dwexi/entropystrip
Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine
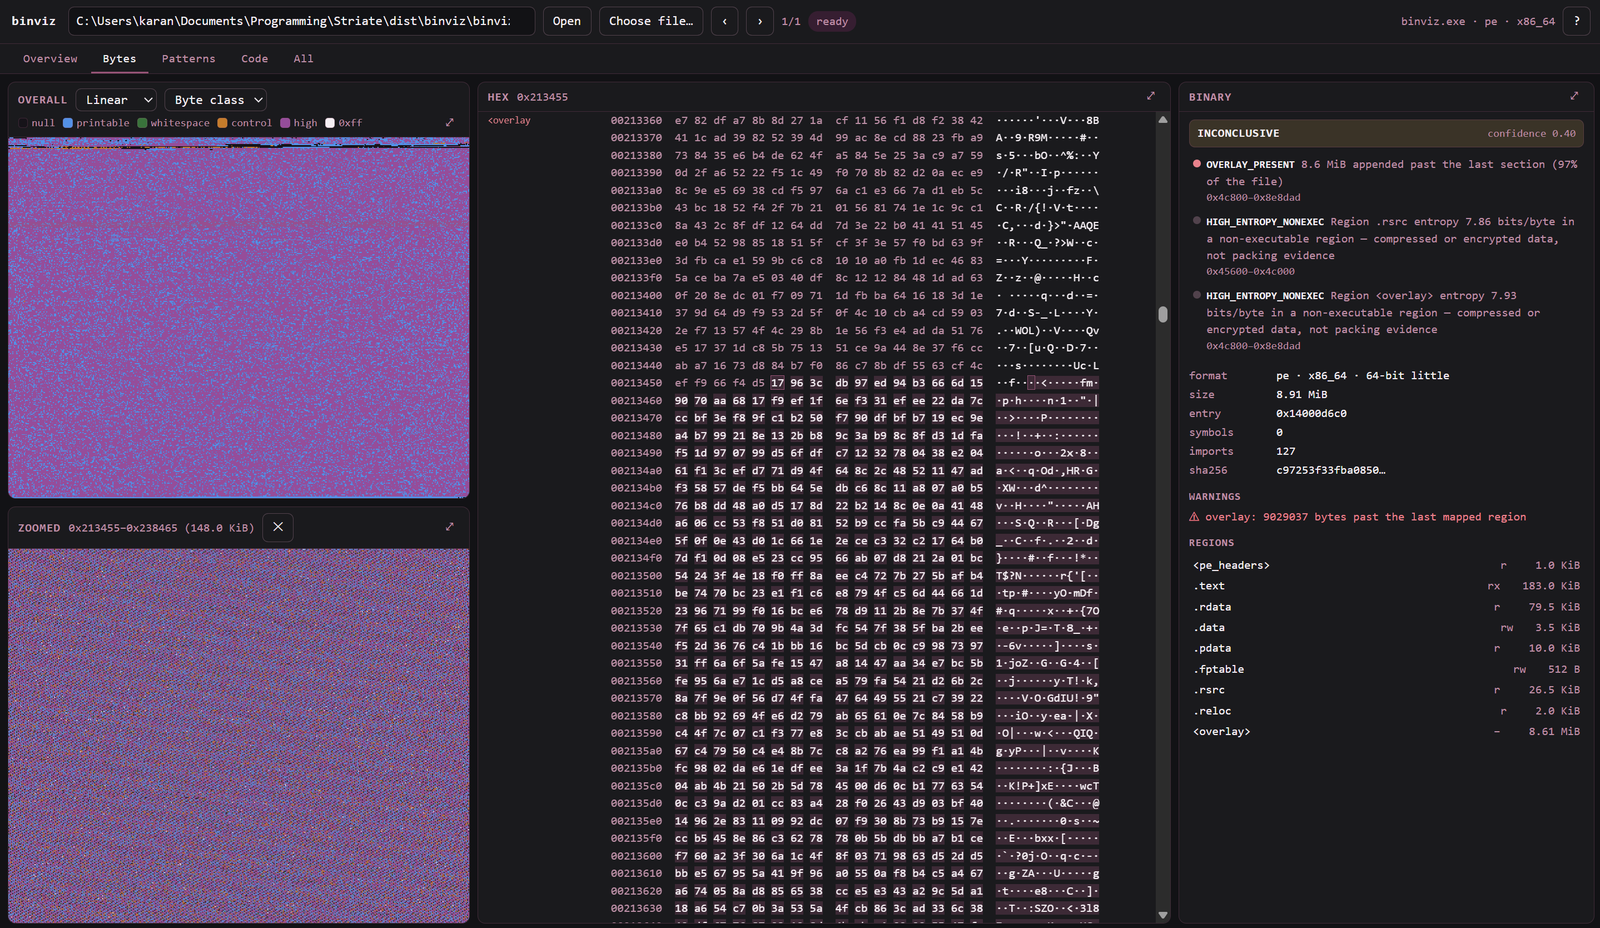 karankantaria/binviz
Binary visualiser and triage tool — entropy, byte-class and Hilbert surfaces, dot plots and control-flow graphs over one shared address-space model.
 warpedatom/offsetinspect
PowerShell toolkit for AMSI/Defender detection-boundary analysis and static malware triage maps byte offsets to detection triggers, plus YARA,…
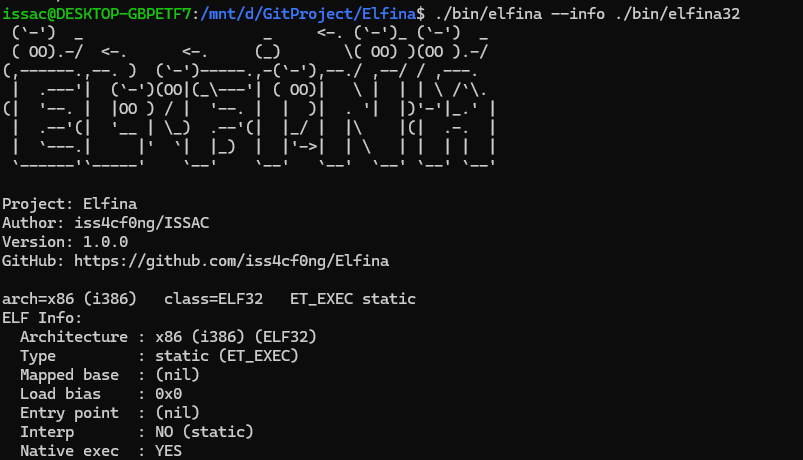 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
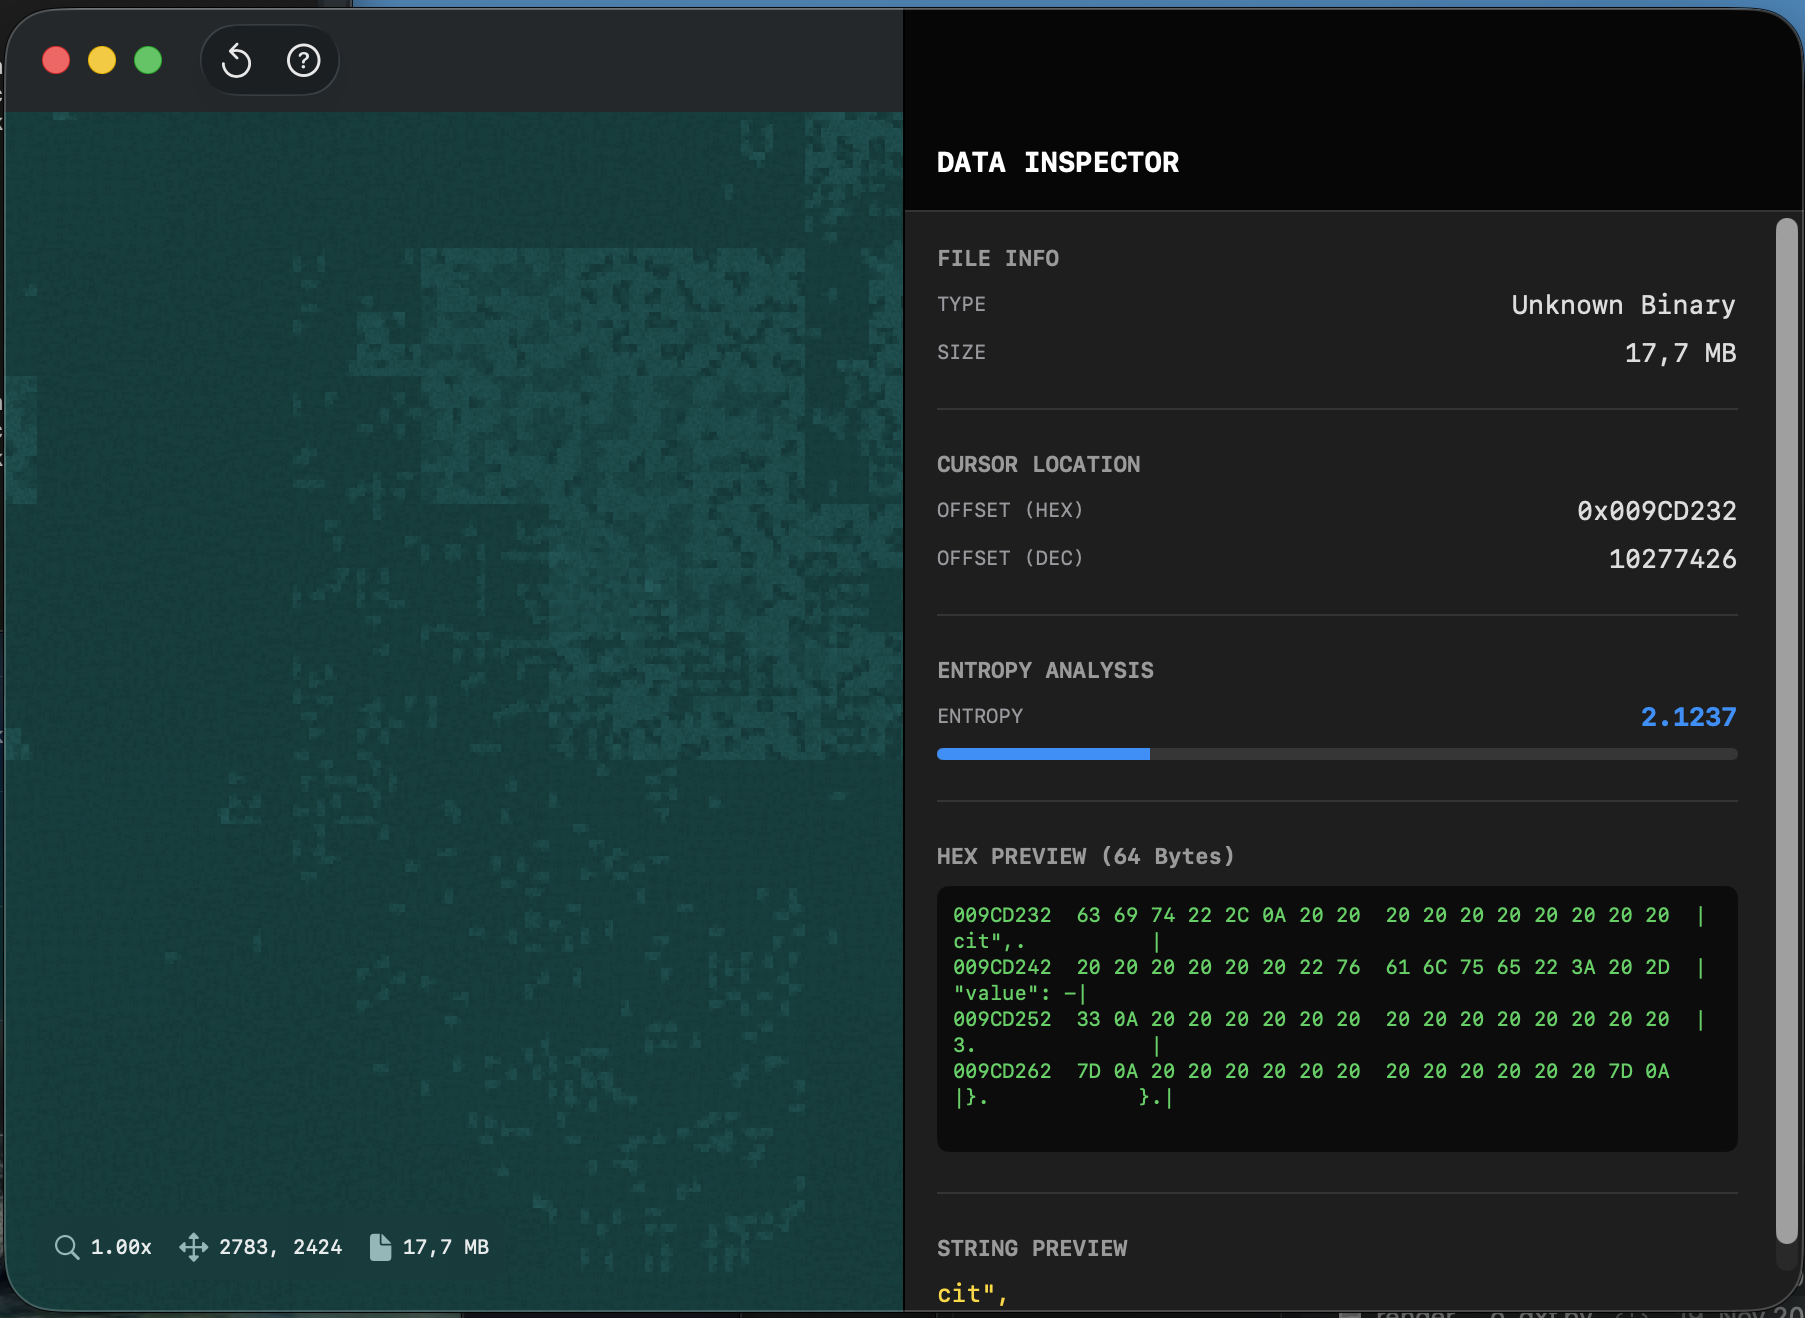 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 33hps/wibu-codemeter-analysis
Cryptographic analysis of WIBU CodeMeter DRM - entropy analysis reveals XOR patterns instead of claimed AES-256
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…