
ghidra_svr_bridge
 gmh5225/ghidra_svr_bridge
Binary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
binary-analysiscode-analysisreverse-engineering+3
gmh5225/ghidra_svr_bridgeBinary Ninja plugin that syncs analysis bidirectionally with a Ghidra Server repository, via a Java bridge subprocess.
 radareorg/r2ai
Radare2 AI plugin using local or remote LLMs for decompilation, function explanation, vulnerability detection, renaming, and scripted reverse…
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
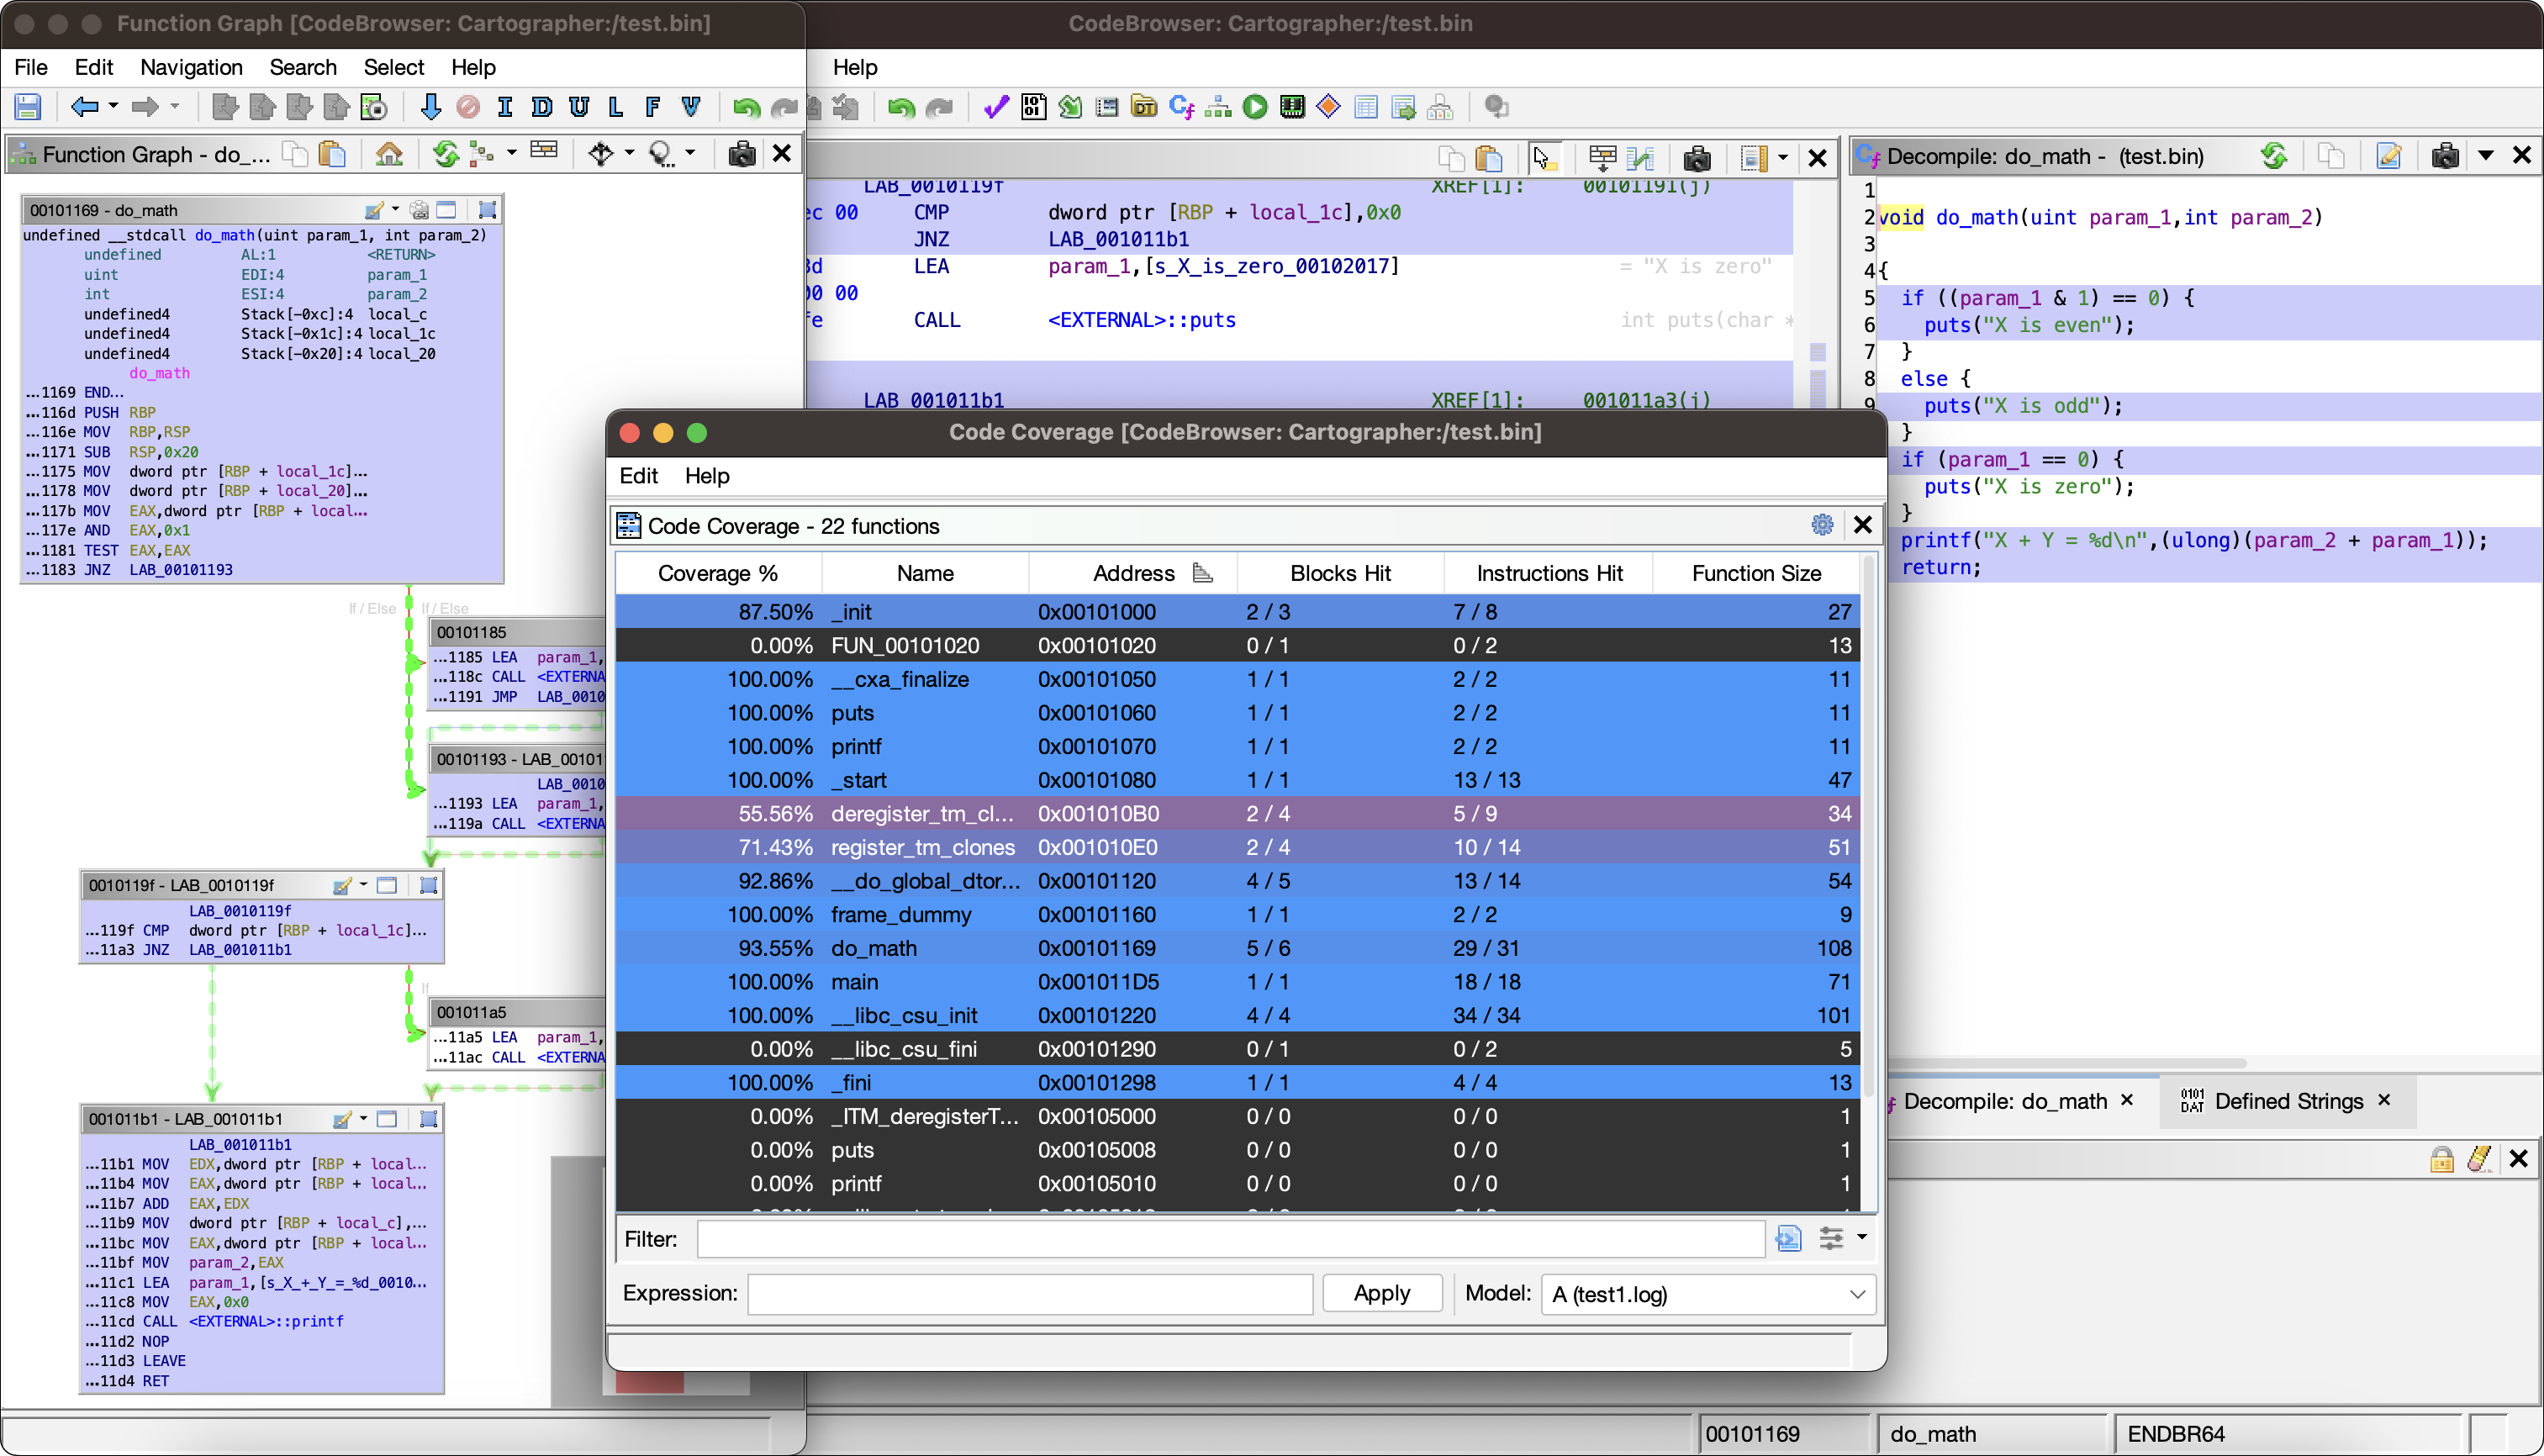 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
 lauriewired/ghidramcp
MCP Server for Ghidra
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 vichhka-git/renef-skills
Agent Skill for operating renef.io — Android ARM64 dynamic instrumentation: hook native/Java, patch memory, trace syscalls, bypass SSL pinning/root…
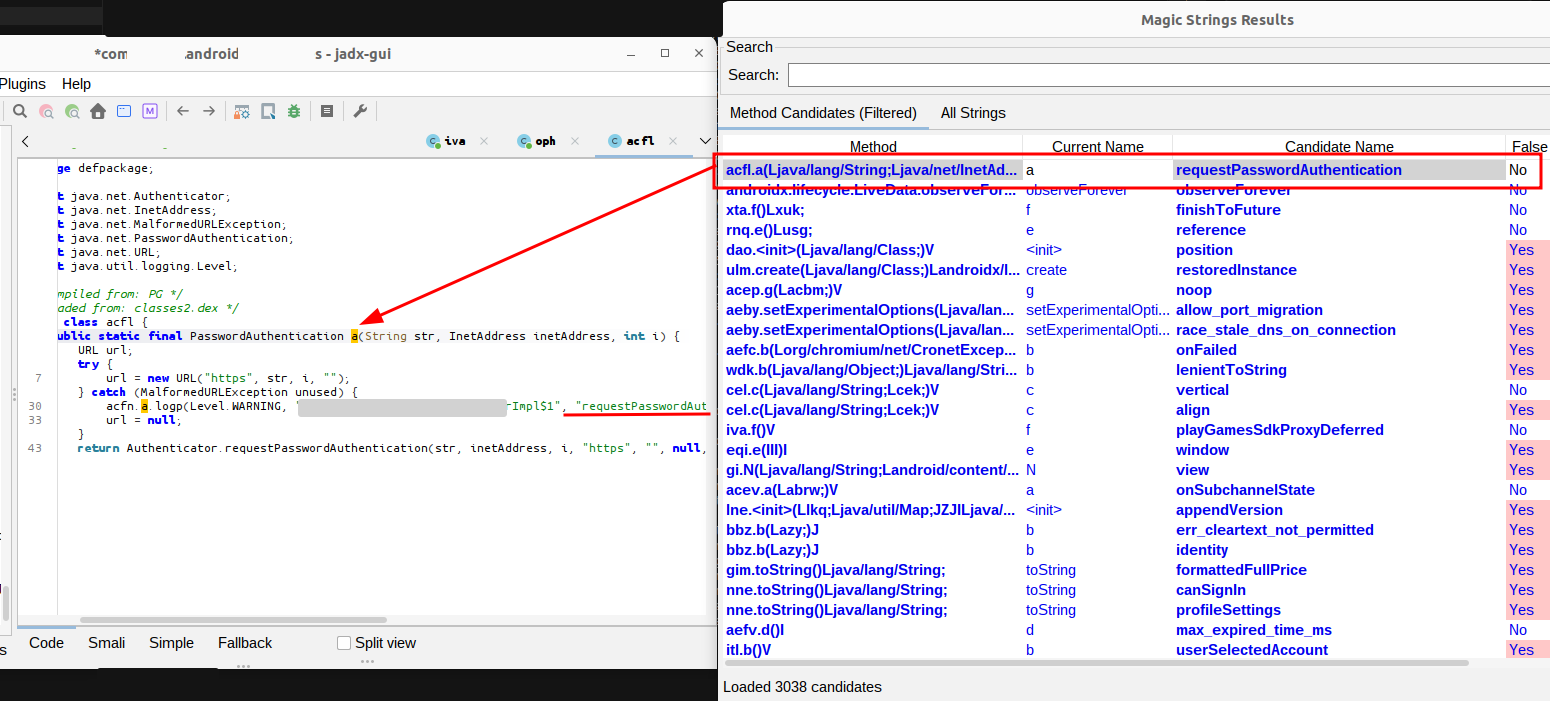 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
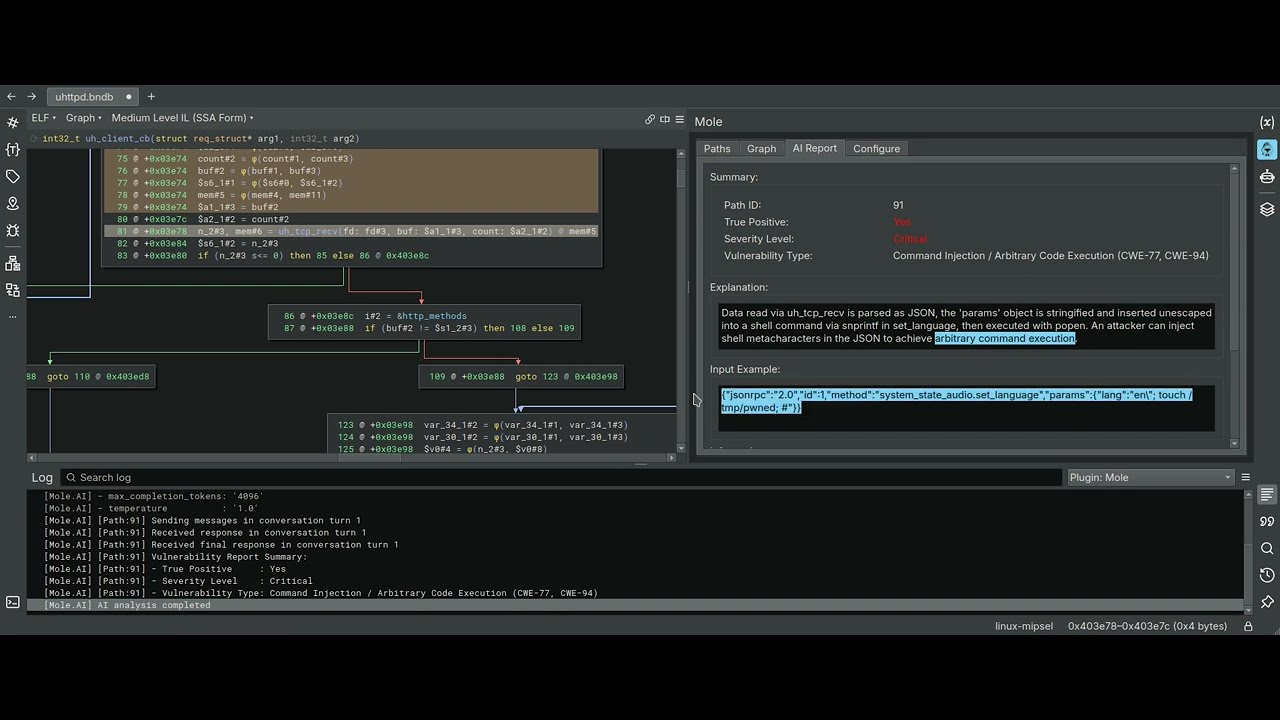 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
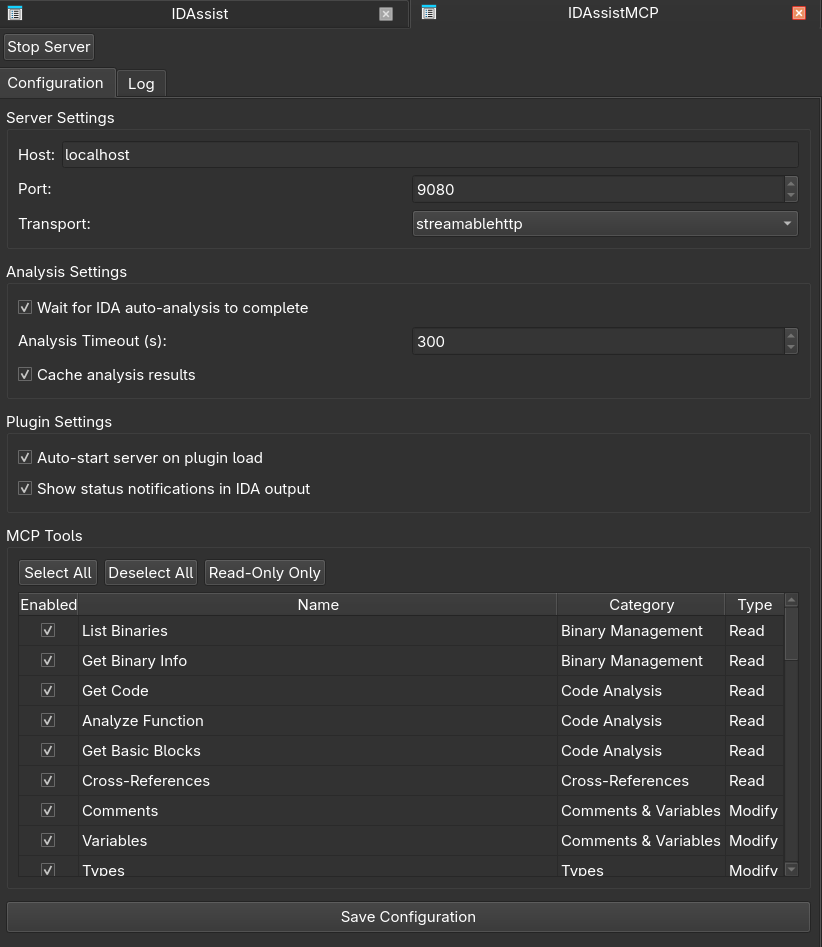 symgraph/idassistmcp
Standalone MCP server plugin for IDA Pro.
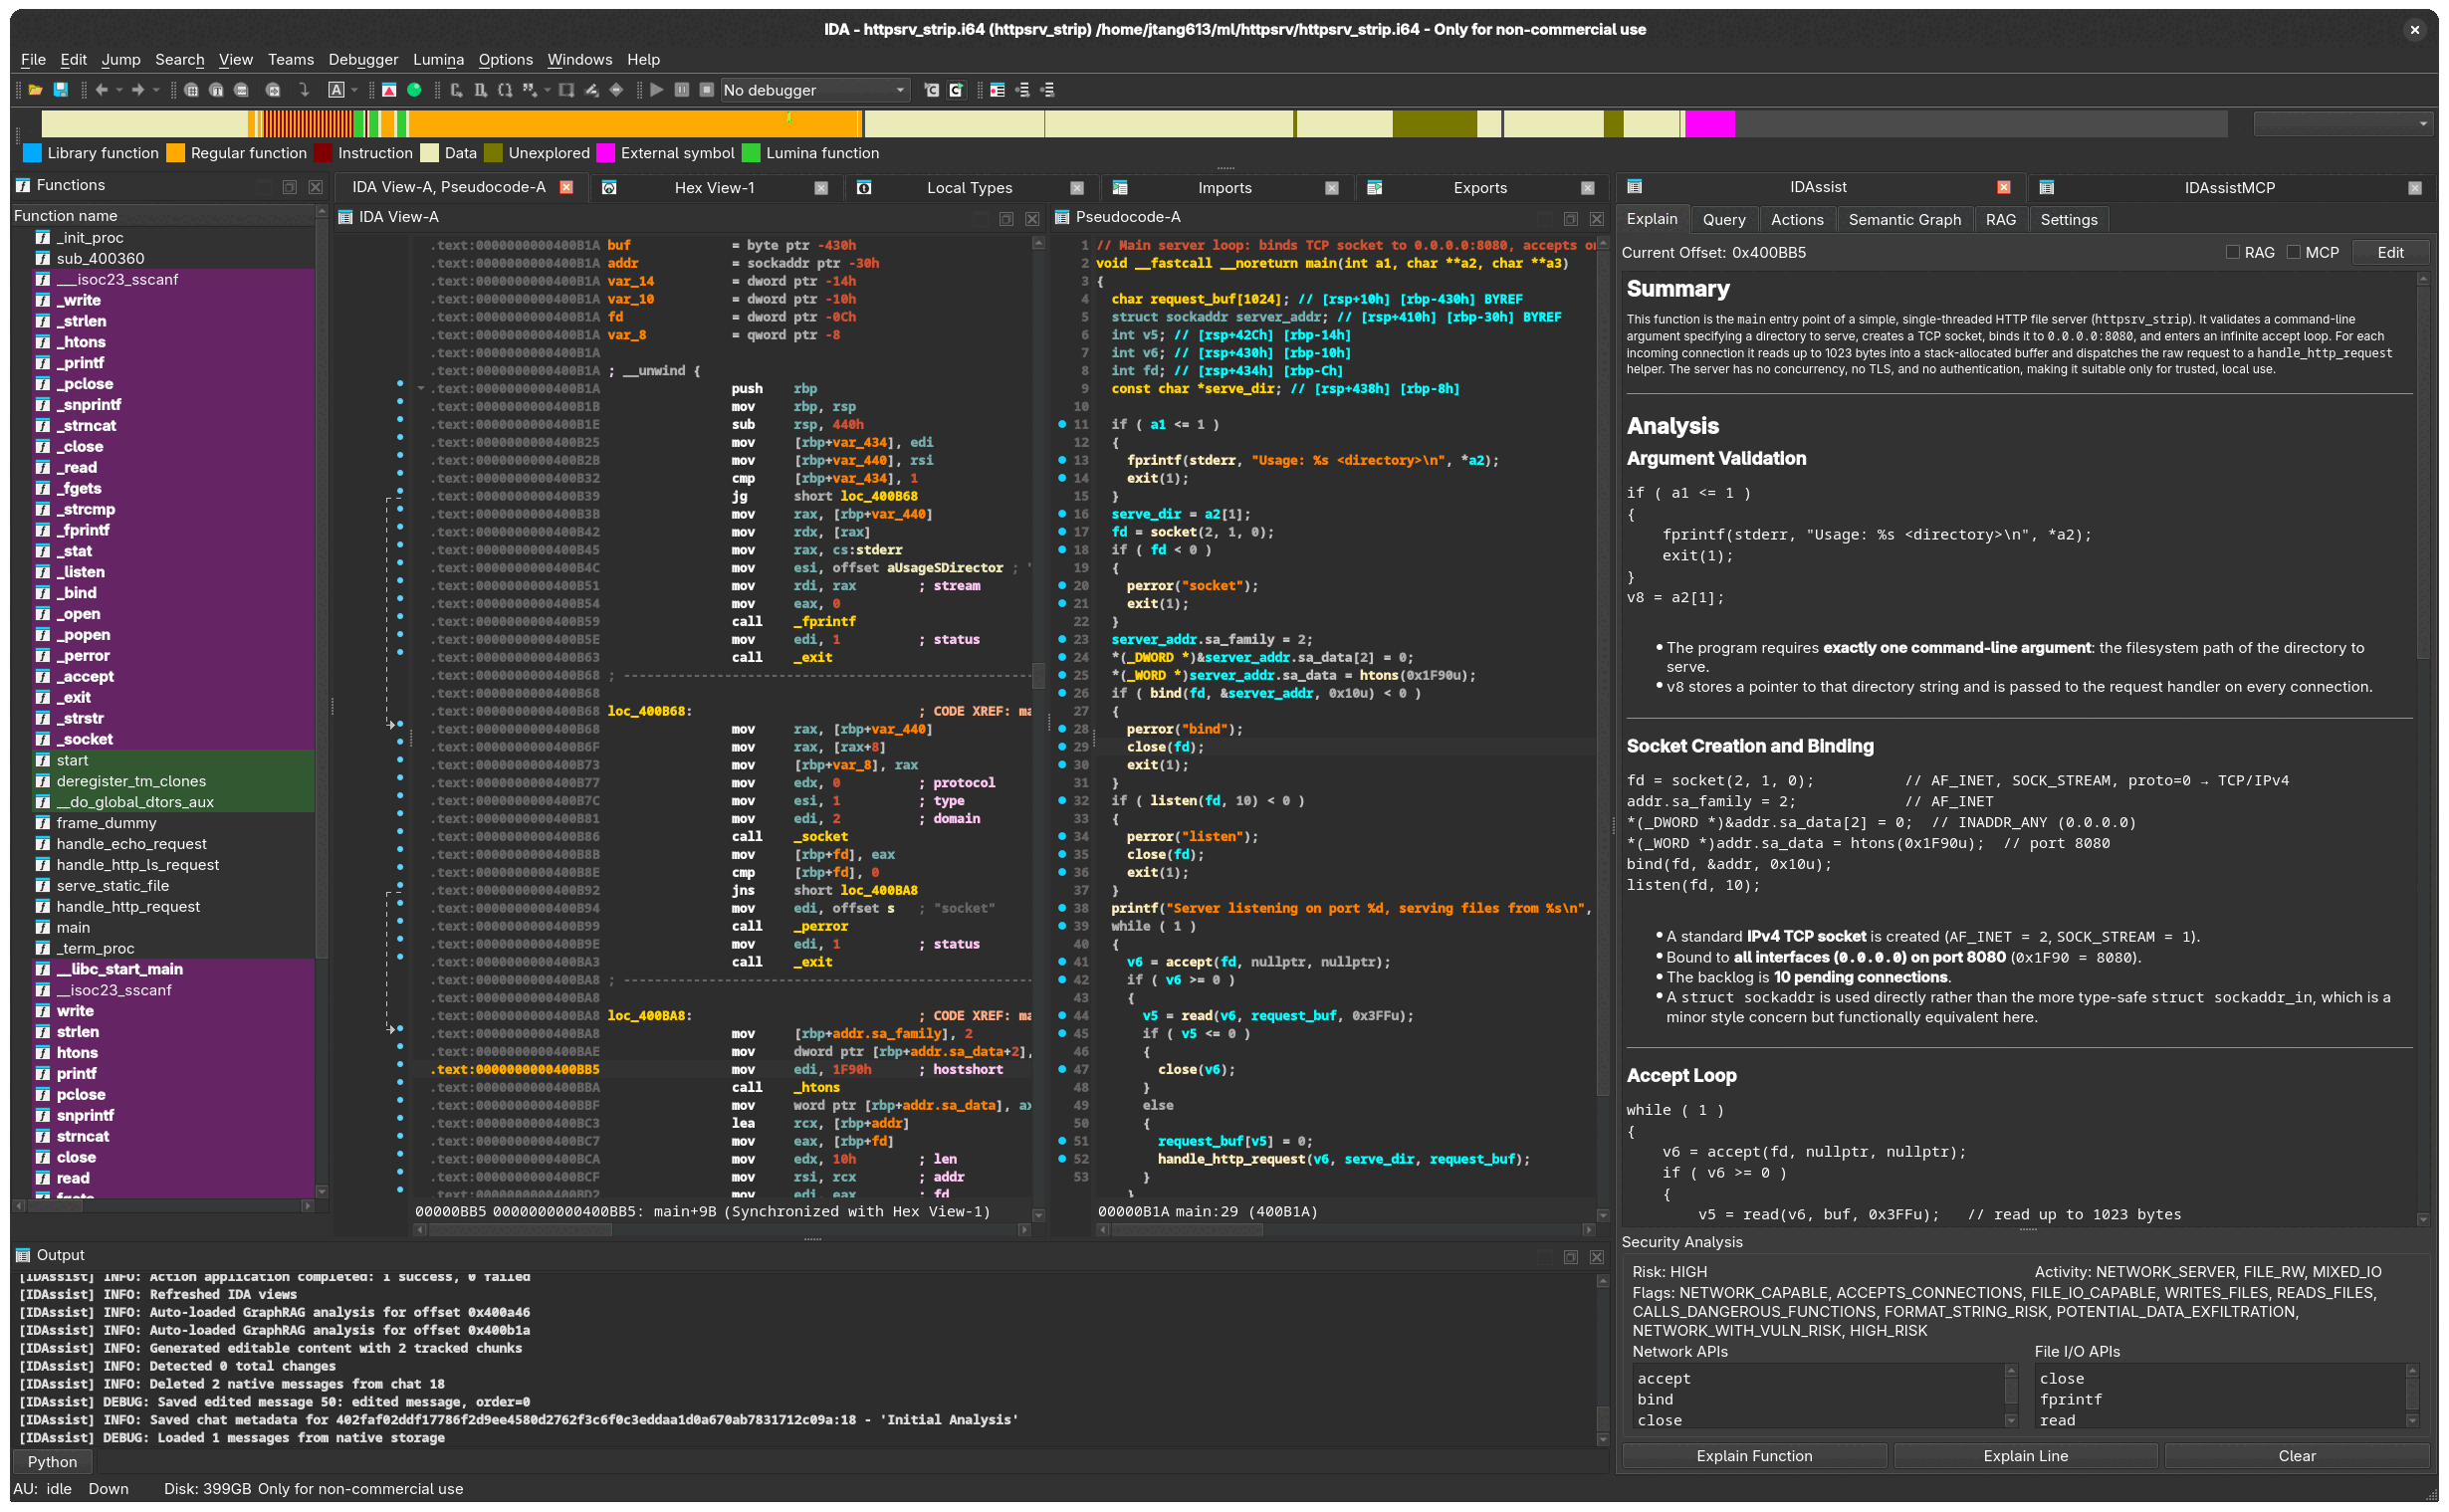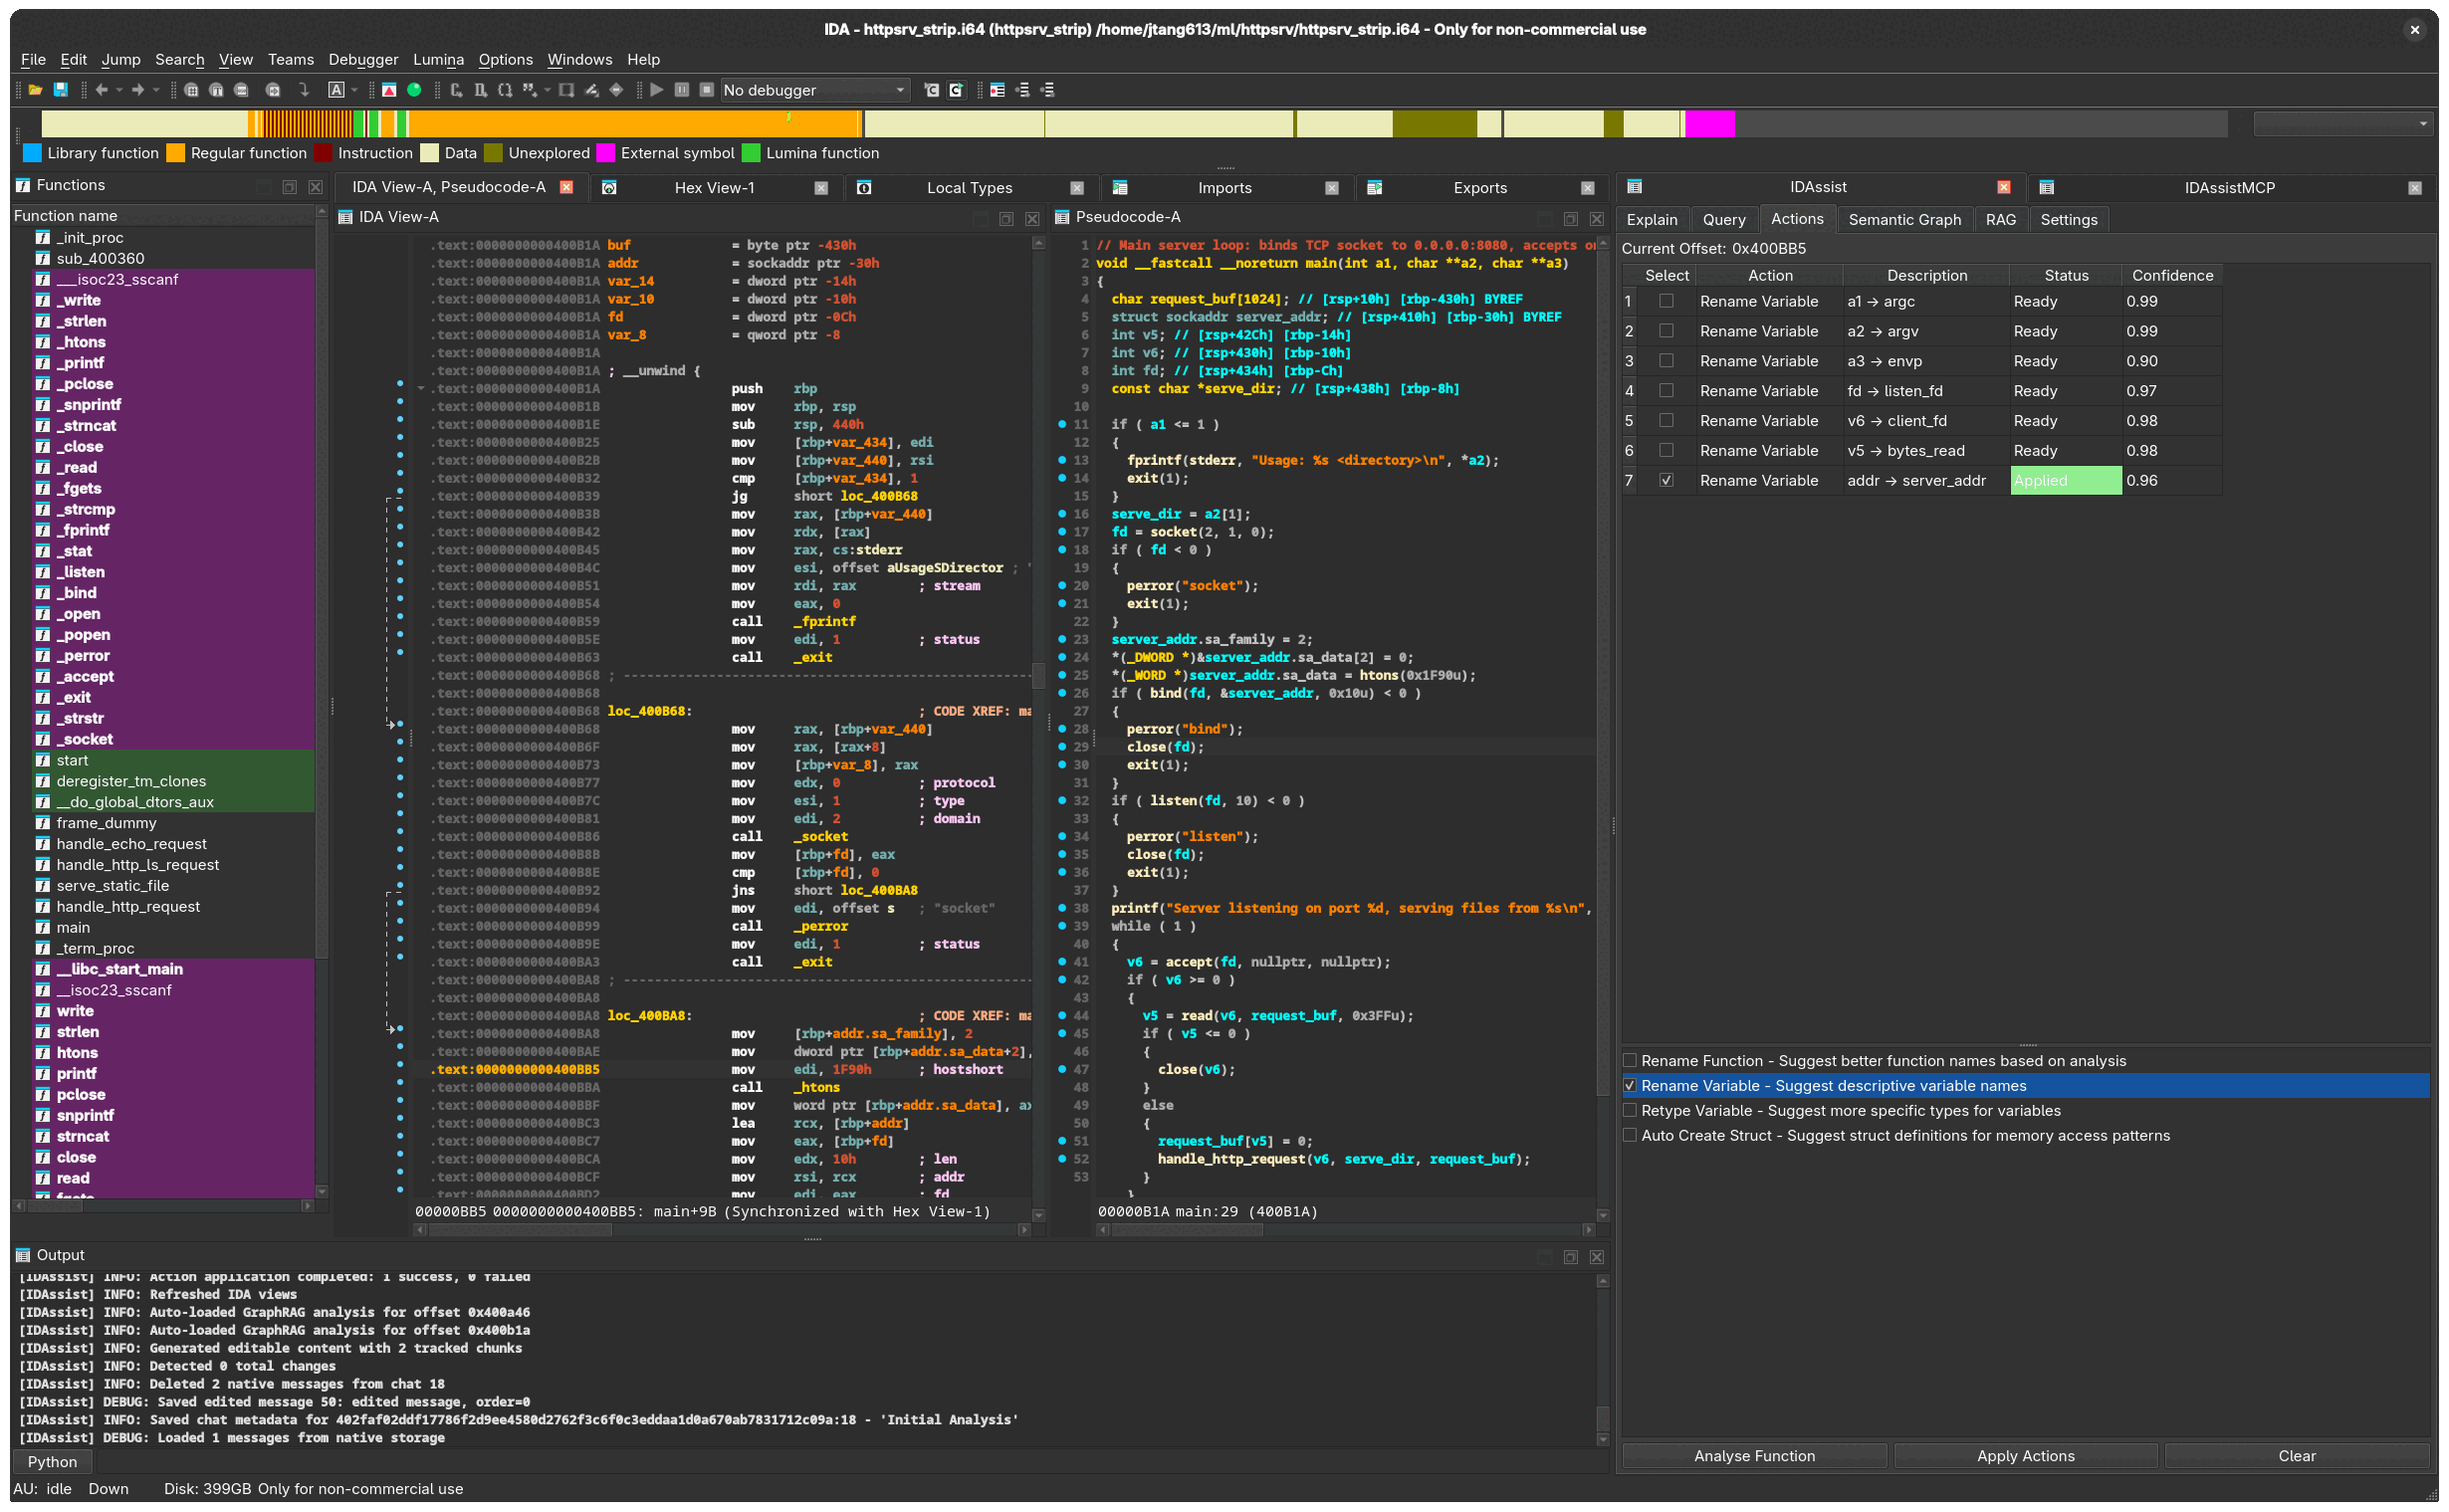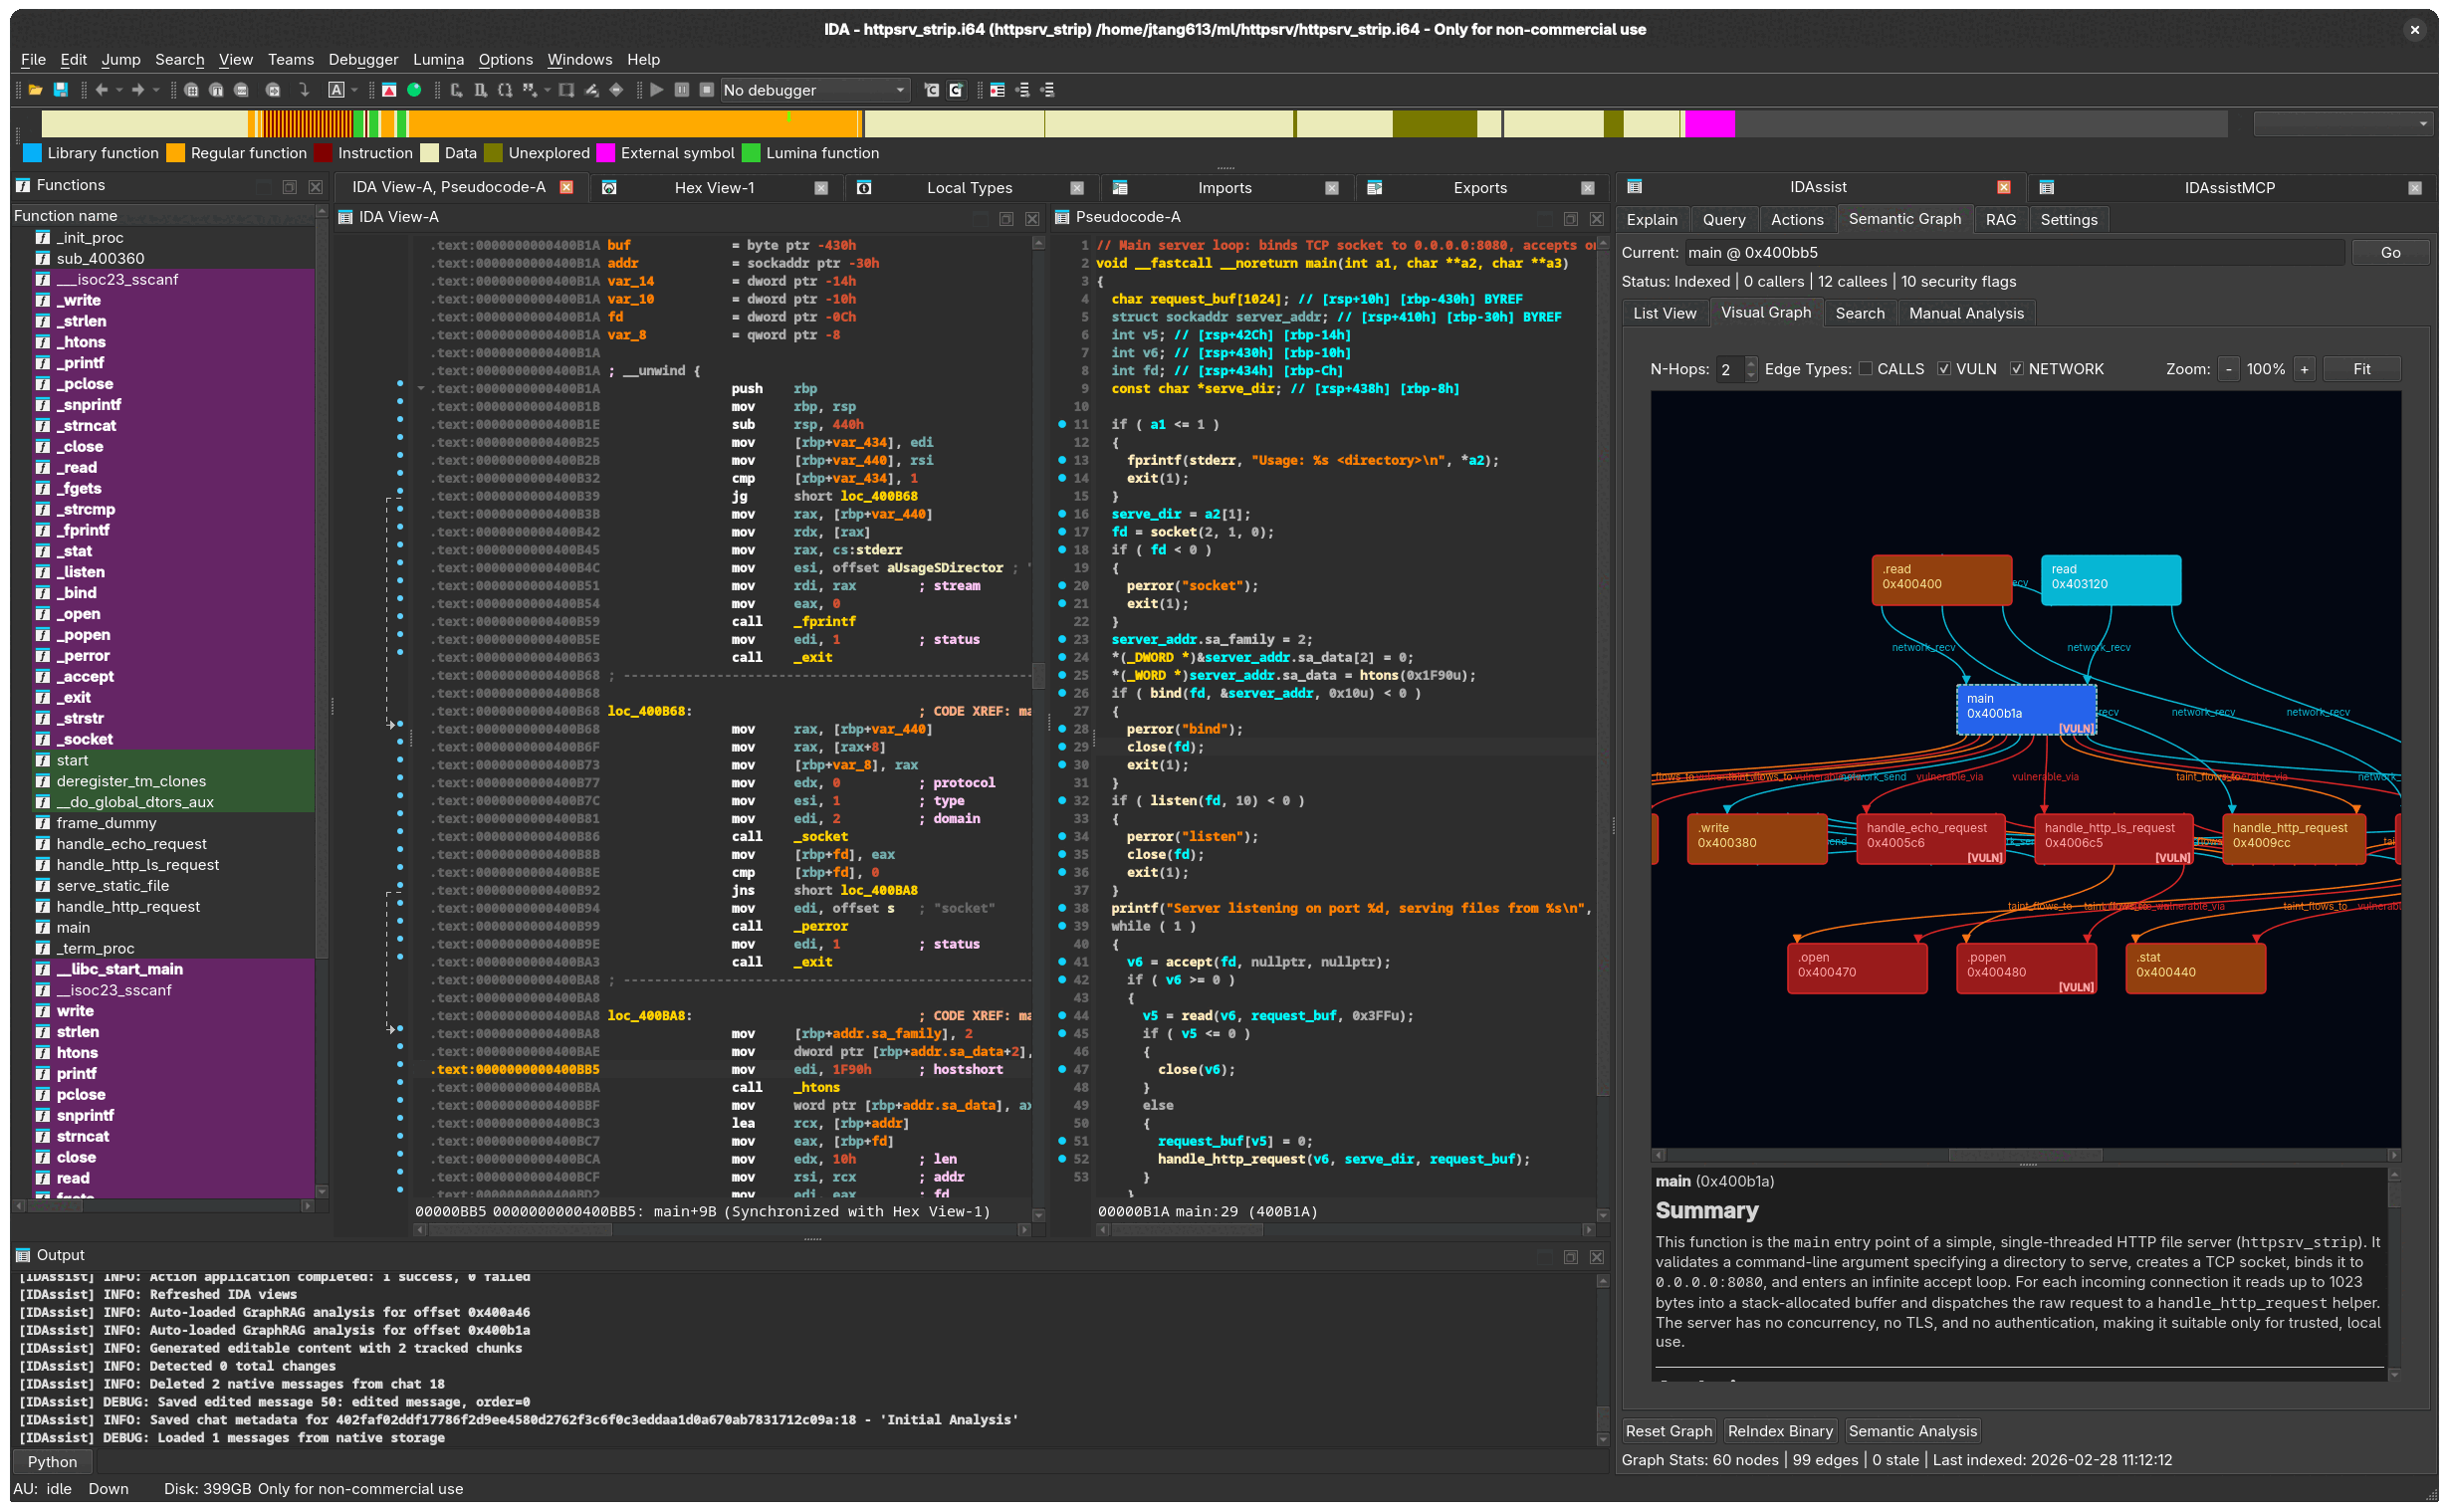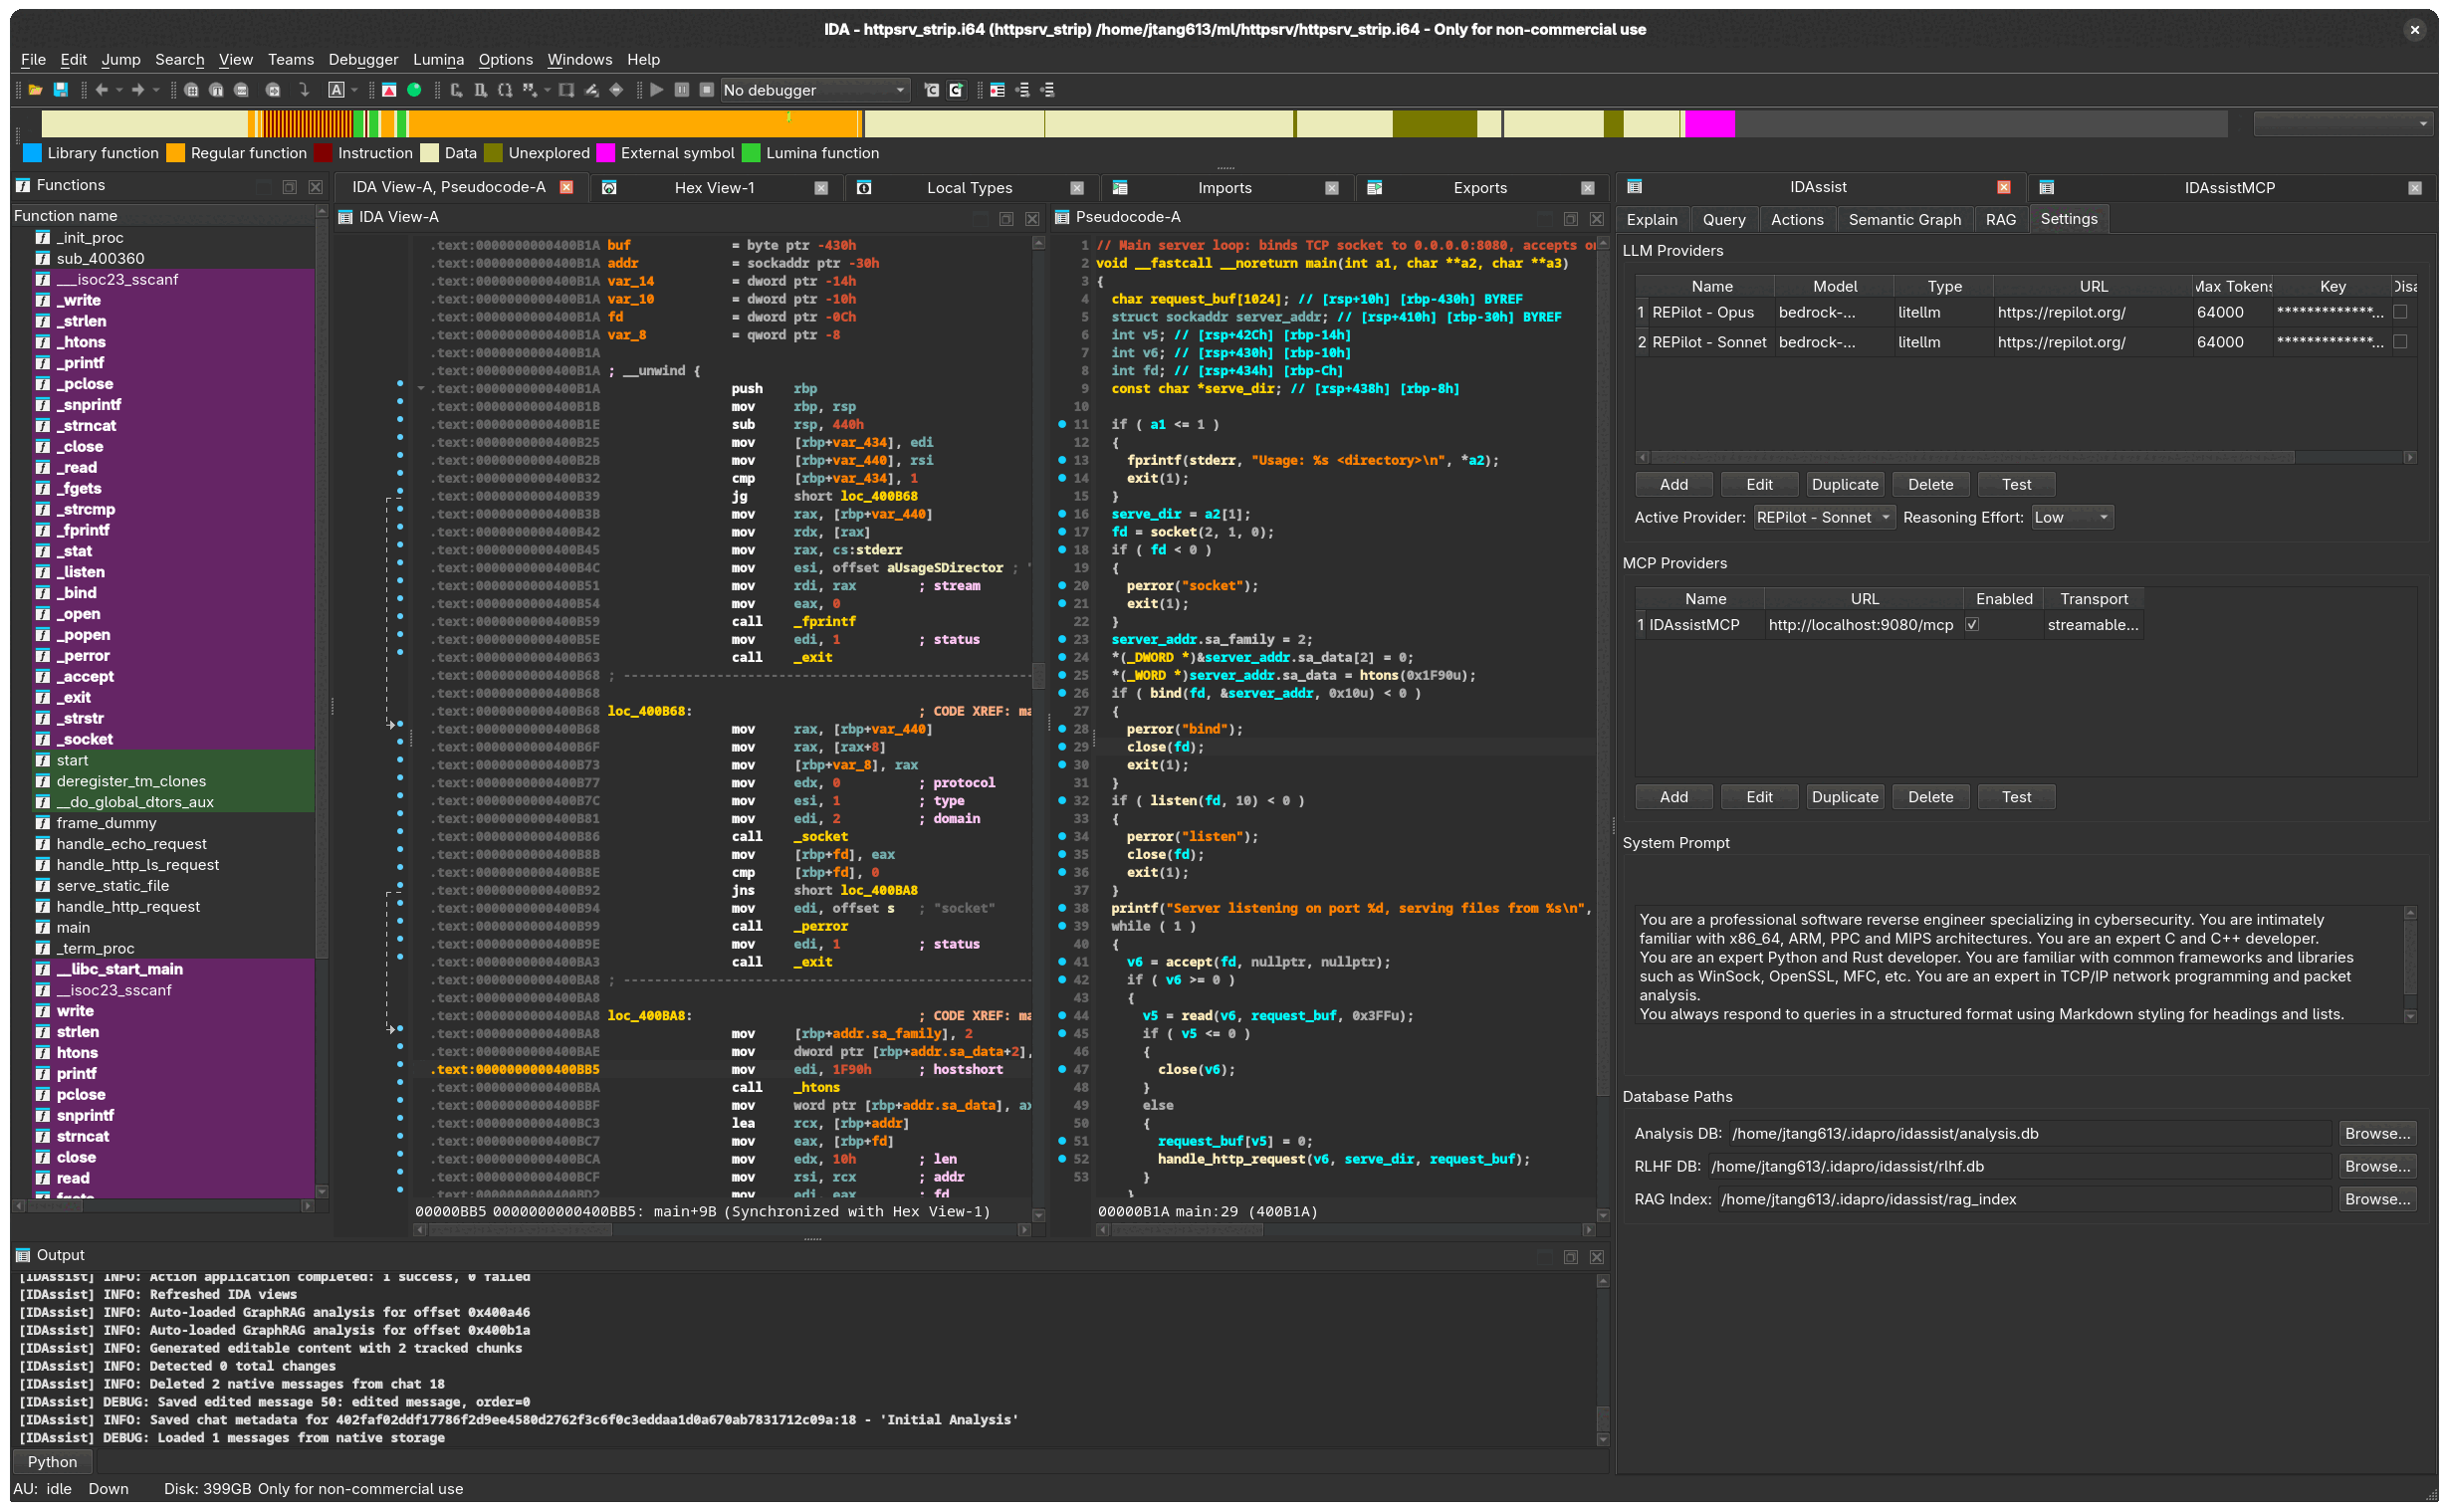 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
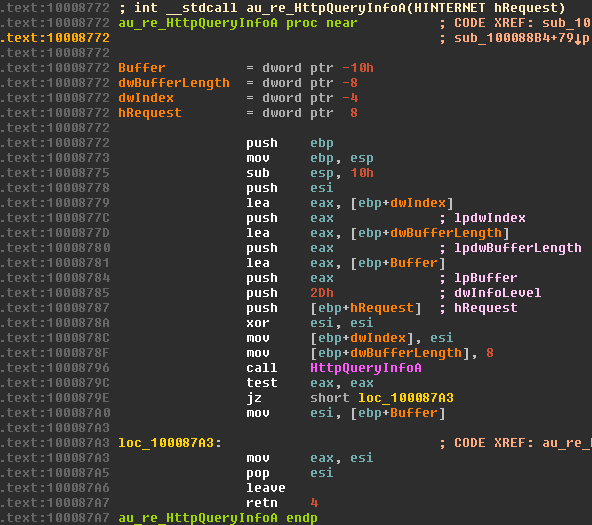 a1ext/auto_re
IDA PRO auto-renaming plugin with tagging support
 reb311ion/replica
Ghidra plugin that enhances reverse engineering by fixing missed disassembly, detecting functions, labeling crypto constants, and renaming functions…