
CVE-2026-96515
 whoami-012/cve-2026-96515
Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
binary-analysisembedded-systems-securityexploitation+7
1
whoami-012/cve-2026-96515Technical report and authenticated reverse-shell PoC for CVE-2026-96515, a root command execution flaw in the Netlink HG323RW router's BOA diagnostic…
 notrequiem/antidbg
A stealthy, fully syscalled C/C++ userland anti-debugging library for Windows, designed to protect software from reverse engineering
 kemrec/cve-2025-0324-axis-vapix-privesc
Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 george0papasotiriou/cve-2026-20404-mediatek-modem-remote-dos-rogue-base-station-scenario-
A MediaTek modem input validation issue can cause a system crash (remote DoS) when a UE connects to a rogue base station controlled by an attacker…
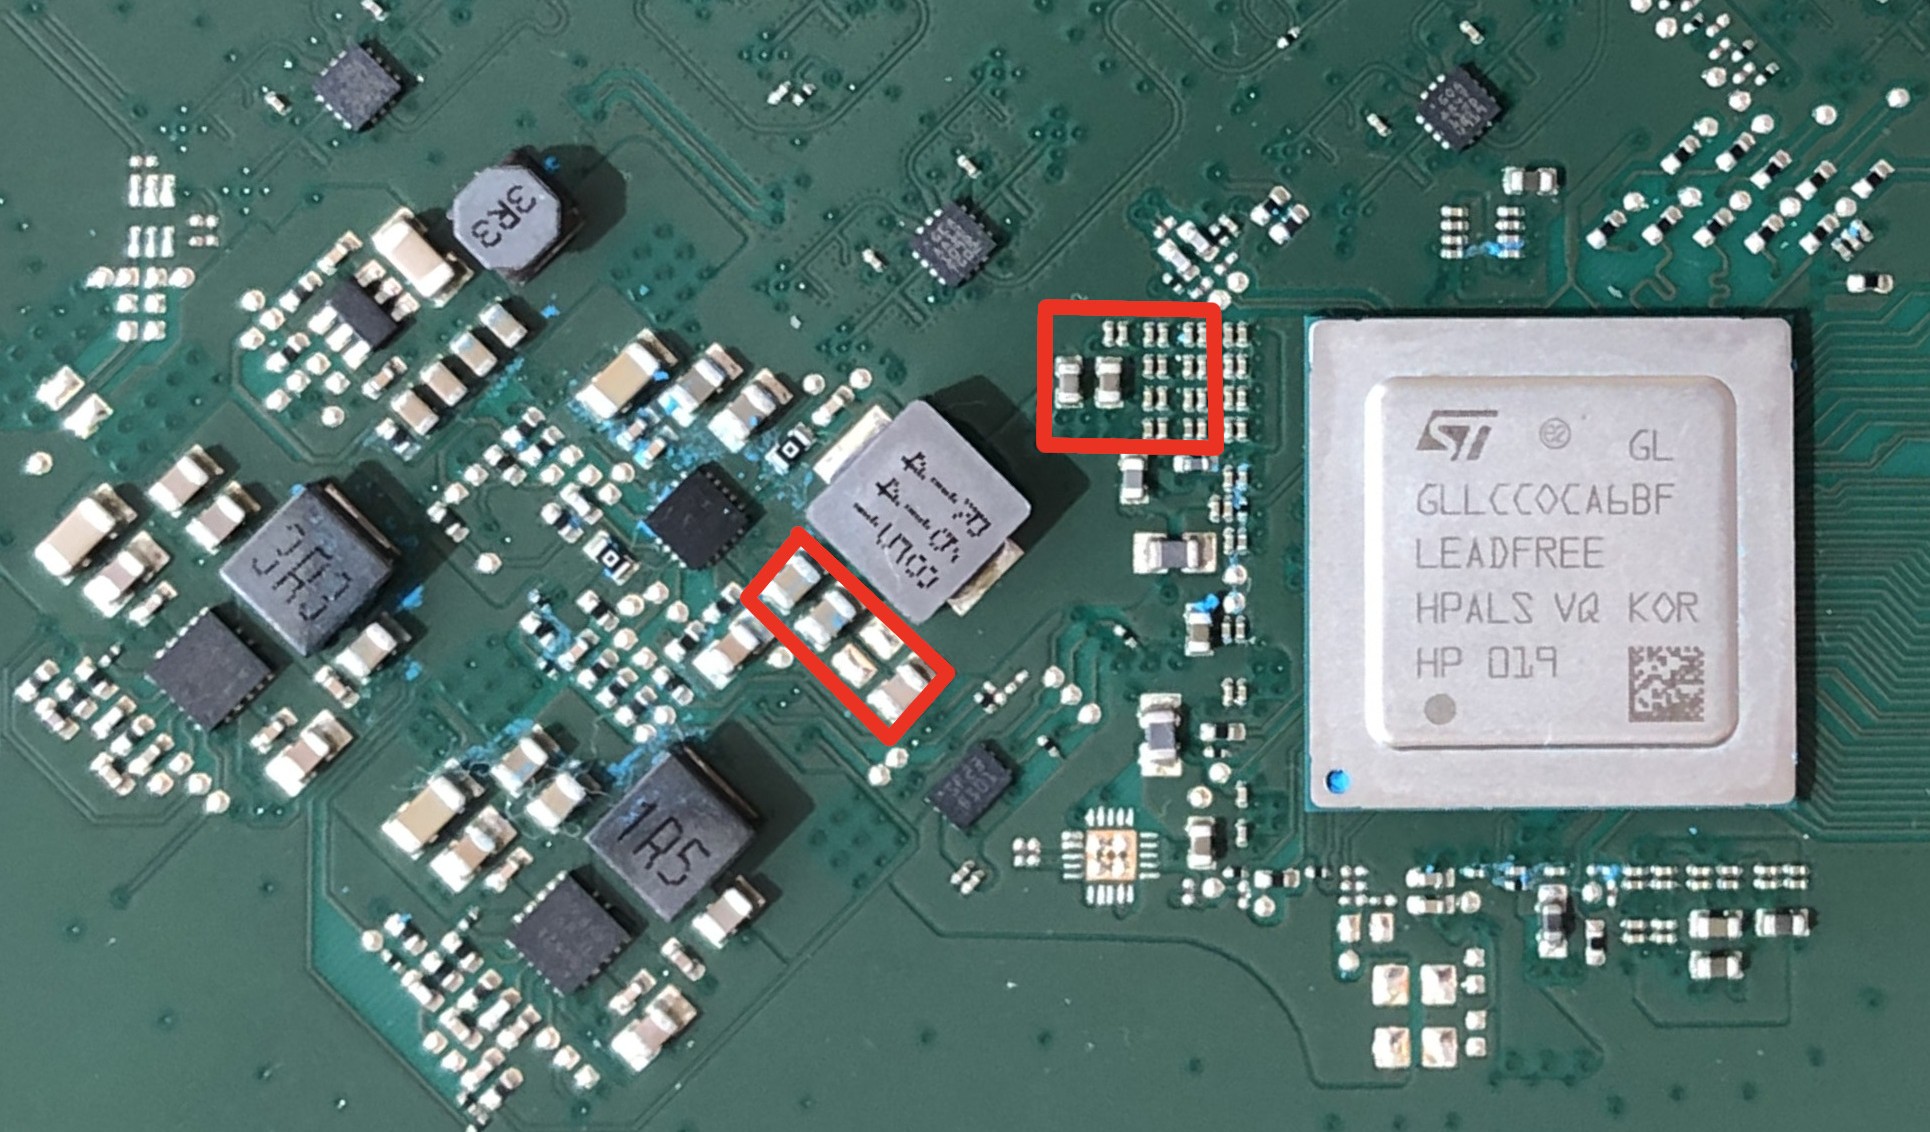 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 darkcodersc/psylodbg
User-friendly Microsoft Windows Debugger for Malware Analysts.
 hasherezade/ida_ifl
IFL - Interactive Functions List (plugin for IDA Pro)
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 synacktiv/captainhook
Traces user inputs to detect injection vulnerabilities in Java methods via JDWP and Frida, identifying potential command and SQL injection points.
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 ugvxb/cve-2026-9490
The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…
 ugvxb/cve-2026-9789
A critical local privilege escalation vulnerability has been discovered in Acer NitroSense software (PSAdminAgent.exe). The vulnerability allows any…
 l41kaa/cve-2024-48705
Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.