
OmniSec-Hex
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
ai-securitybinary-analysisfuzzing+9
vighnesh91/omnisec-hexBrowser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 deathshotxd/0xcr0sscrush
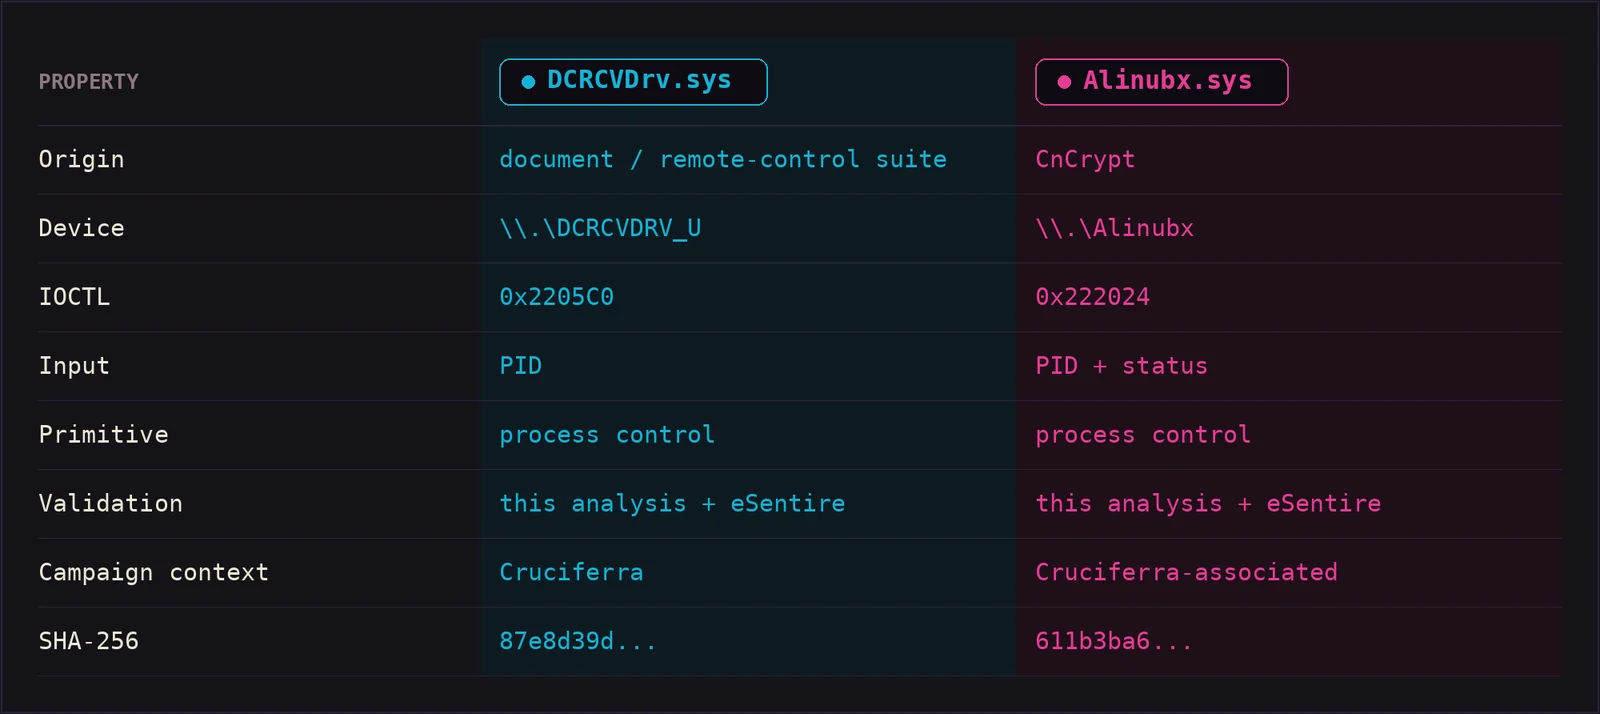
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 vighnesh91/ipaforge
Dependency-free Python CLI to unpack, inspect, edit, and rebuild iOS .ipa archives, converting plists and strings to XML while preserving Mach-O…
 gmh5225/eac-kernel-packet-fucker
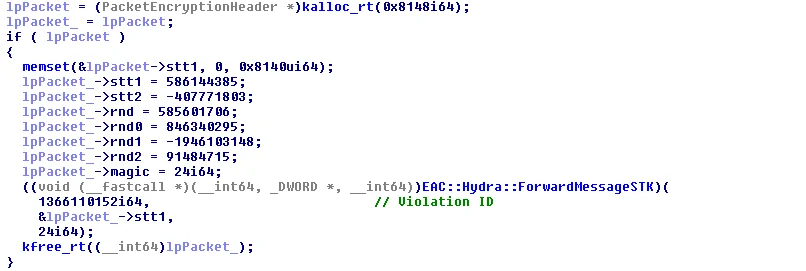
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
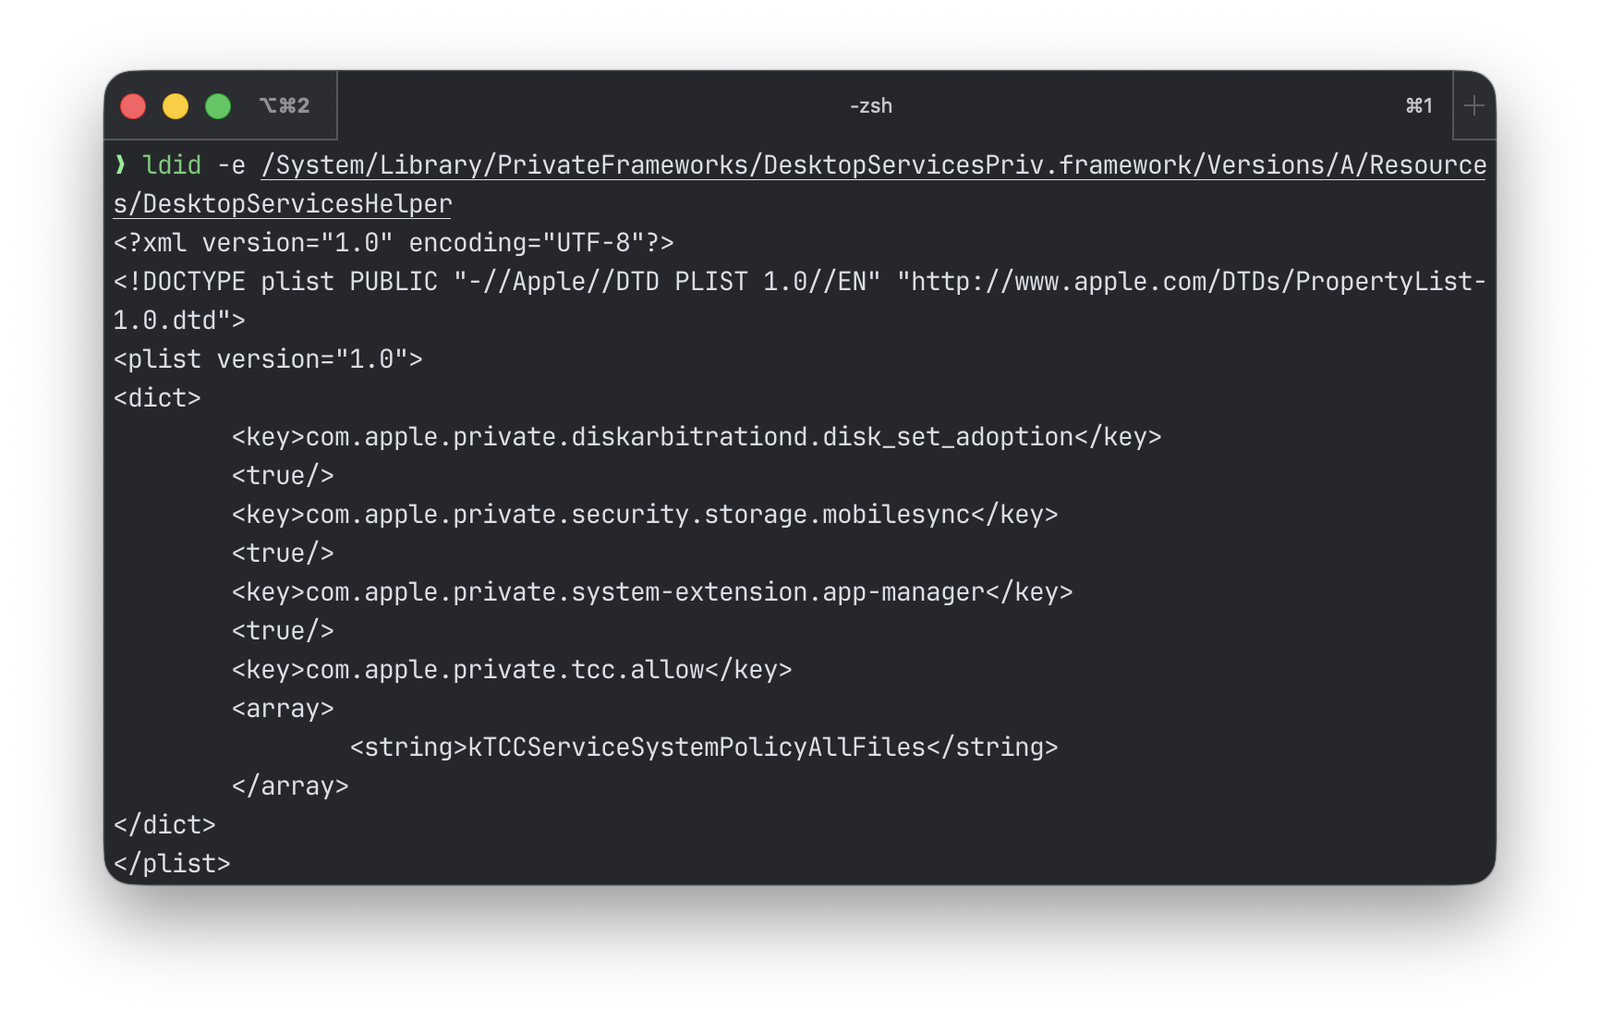 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 crissyfield/super-trouper
MCP server exposing Frida instrumentation as tools for coding agents to connect to devices, inspect processes, manage sessions, and load JavaScript…
 harshrajsinghania/cve-2026-90782-s2opc-status-clobber
Standalone PoC for CVE-2026-90782: status-clobbering NULL dereference in S2OPC alloc_notification_message_items() (DataChange fails, Event succeeds)
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 gmh5225/dot-cfg-challenge
C++ challenge repository exploring Control Flow Guard (CFG) bypass techniques for Windows binary exploitation research.
 gmh5225/driver-hidekernelthread-iocancelirp
Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…
 gmh5225/driver-keattachprocess-kedetachprocess-rebuild
Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.
 gmh5225/driver-pidqserializationwrite-example
How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
 gmh5225/driver-soulextraction
SoulExtraction is a windows driver library for extracting cert information in windows drivers
 nathan-luevano/silica
Exhaustive differential validation of all 4.3B AArch64 instruction encodings.