

disrobe
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
android-securitybinary-analysisfirmware-analysis+4
167
1-3-7/disrobeRust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 p0dalirius/pdbdownload
An utility to download PDB files associated with a Portable Executable (PE).
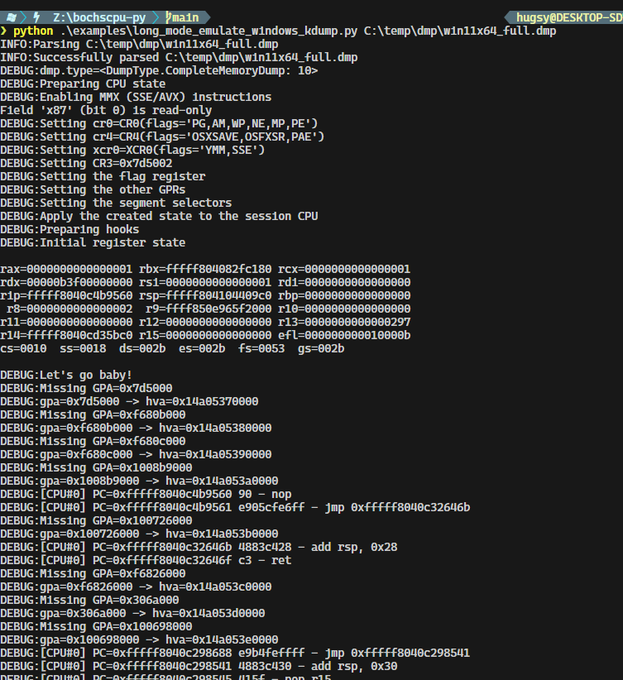 hugsy/bochscpu-python
Python bindings for BochsCPU
 xyl2k/black-eye-rsa-attacking-toolkit-v0.1f-compiled
The great RSA Attacking Toolkit compiled for Windows

 intrigus-lgtm/cve-2020-14955
Proof-of-concept exploit for CVE-2020-14955 targeting a kernel driver IOCTL vulnerability in Jiangmin Antivirus 16.0.13.129 on Windows 7 x32.
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
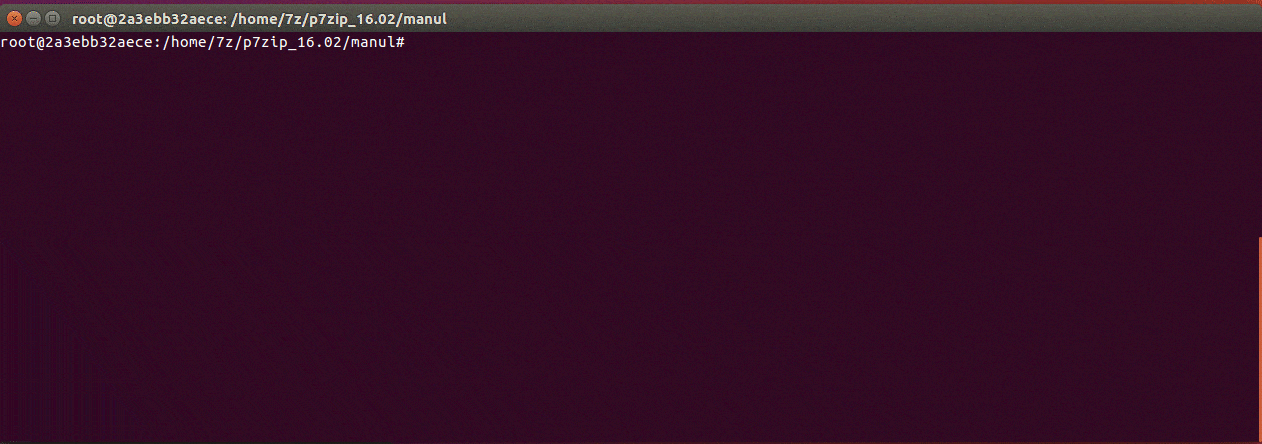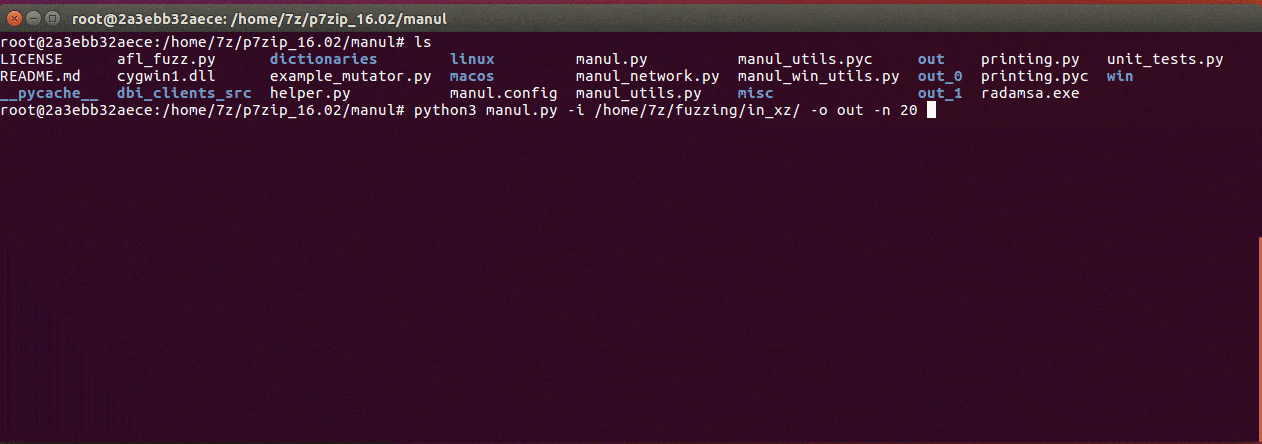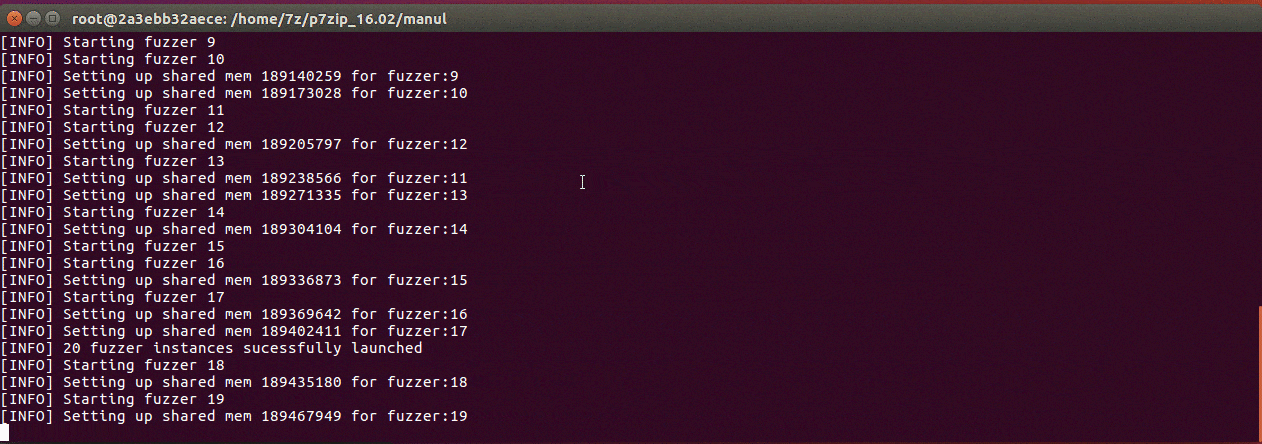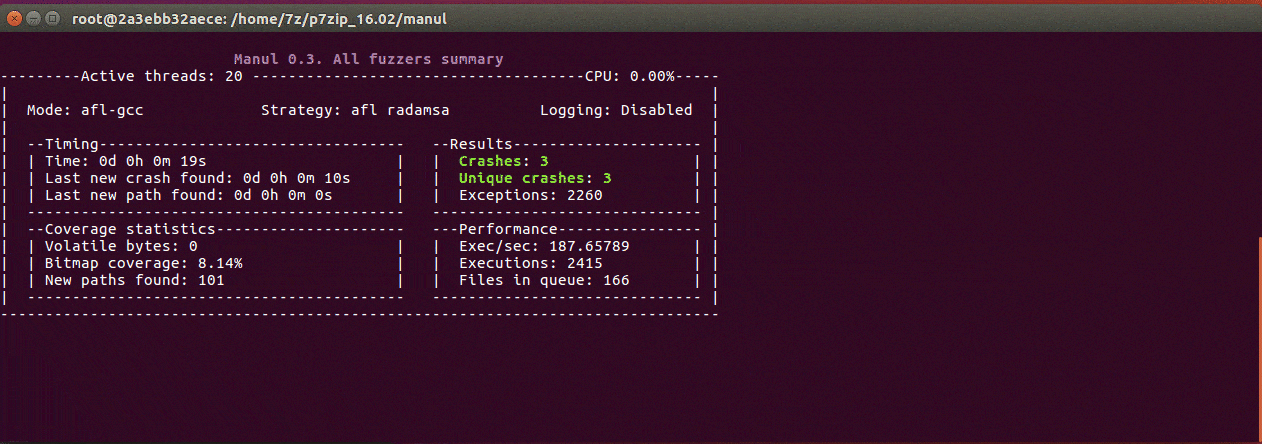 mxmssh/manul
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.