

BogusMips
 jankammerath/bogusmips
Forensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
ai-assisted-reversingandroid-securitybinary-analysis+8
4
jankammerath/bogusmipsForensic analytics for disassembly, reassembly, reverse engineering and auditing of Android apps
 ph4ntom-rev/ph4ntom-ida-bridge
Secure local REST, CLI, MCP, and agent bridge for IDA Pro 9.x
 fareedfauzi/mantis
Multi-Sources Analysis & Threat Intelligence Search
 xen0bit/netprobe-cve-2026-98432
Black-box remote probe that detects CVE-2026-98432, a Linux IPv4 TCP ireq_opt use-after-free, via differential SYN-ACK option echo, plus static…
 fare9/dragon-tales
Binary analysis library built on LLVM for disassembling, lifting, and symbolically executing machine code across x86, ARM, and RISC-V, with CFG…
 jfrog/jfrog-openssl-tools
Python utilities to check whether a TLS server requires client certificates and to scan local ELF binaries for vulnerable OpenSSL 3.x code linked to…
 scyrix-llc/cve-2026-88773
Technical analysis of a NetScaler nsppe HTTP/1.1 chunk-size integer-wrap request smuggling flaw, with disassembly, wire-level PoC flows, and firmware…
 qybaihe/bla
Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and…
 s12cybersecurity/whatpatchguardprotects
Reference of all kernel structures, routines, and MSRs monitored by PatchGuard (KPP) on Windows.
 1llu50ry/mcp-reverse
MCP server exposing 180+ reverse-engineering tools that aggregate Ghidra, IDA, x64dbg, Frida and 56 other backends with native binary parsers and a…
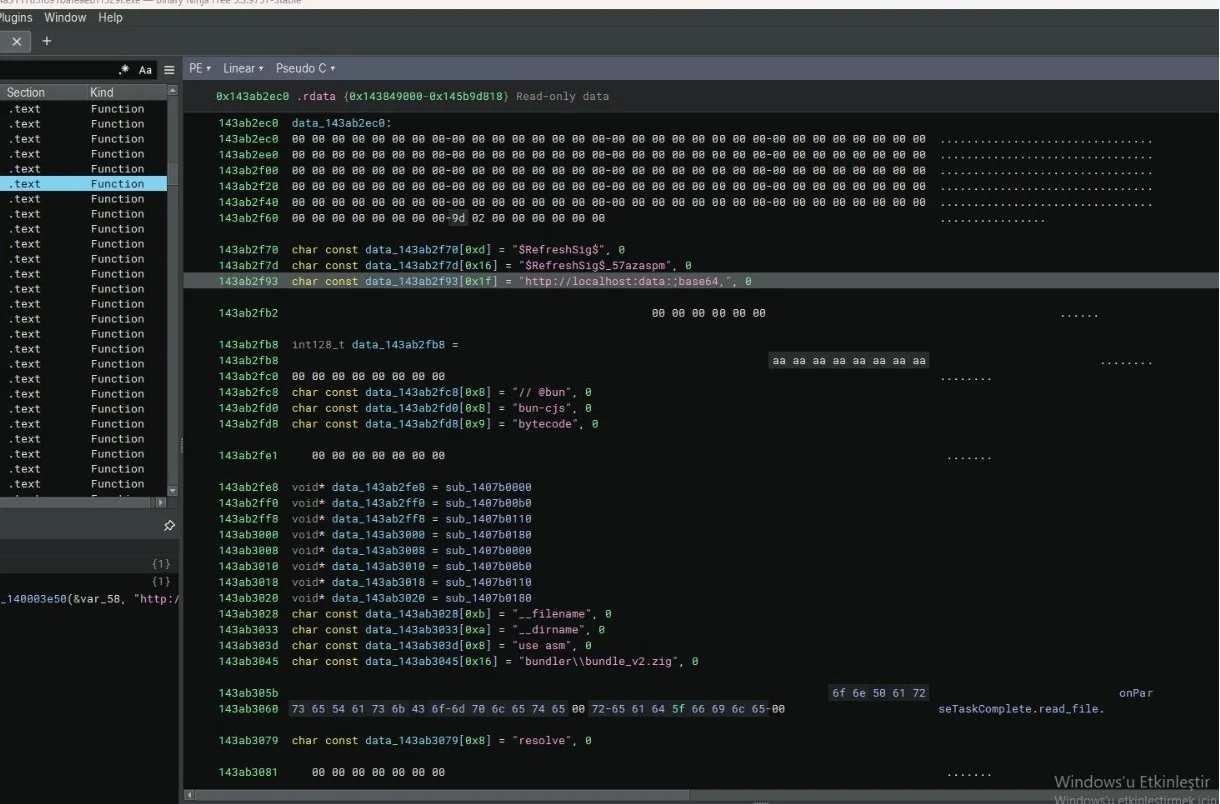 kaandemir993/nwh-stealer-analysis-fileless-bun-runtime-execution-clipboard-image-theft-cloud-c2-aws-r2-
Static analysis and payload extraction of NWH Stealer. Features deep dive into fileless execution via Bun JavaScript Runtime, in-memory clipboard…
 1llu50ry/aegis
Single-header C++20 software protection SDK with polymorphic VM code virtualization, compile-time MBA and string obfuscation, 25+ crypto primitives,…
 faicalom/zte-mf904q-reverse-engineering
Open research documentation and source review for ZTE MF904Q bootloader, firmware extraction, and reverse engineering.
 nighthawkk/jnisleuth-mcp
Automated Android JNI RegisterNatives recovery, stripped ARM64 .so type reconstruction, OLLVM BR X8 deobfuscator, and universal LLM/MCP bridge for…
 exporx/idachef
CyberChef-style recipe toolkit for IDA Pro: chain 289 encoding, cipher, compression, and hashing operations on database bytes, then patch results…
 tylermcm/wonderlanternz7
Experimental Nikon Z7 camera firmware research lab: source patcher, QEMU emulation harness, and validation tooling for building and testing modified…
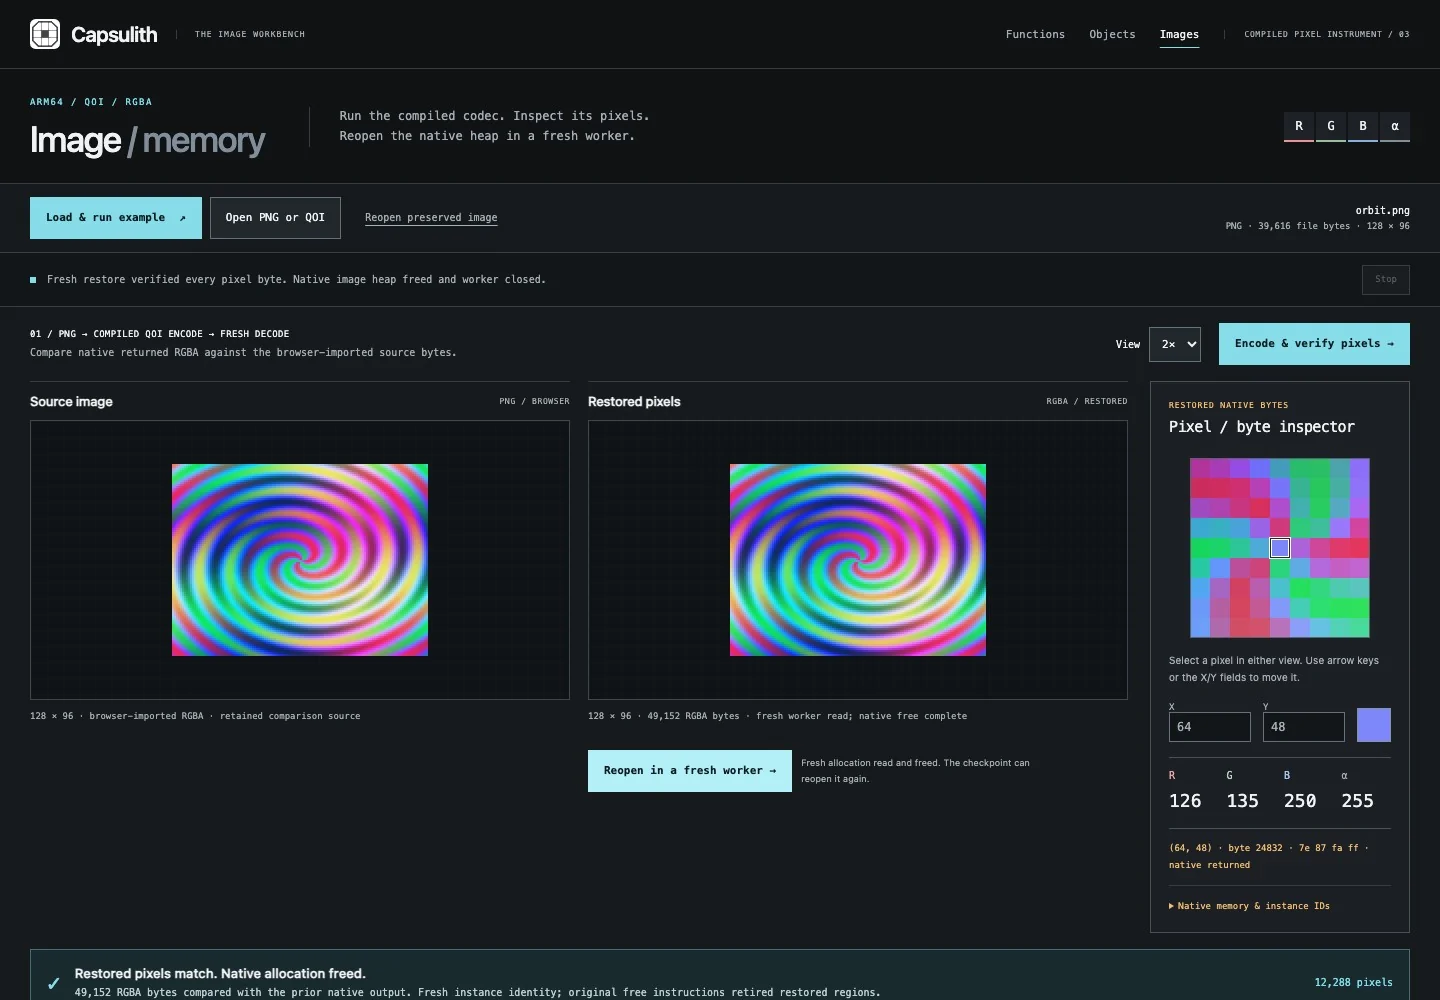 nazeeh111/capsulith
Run preserved ARM64 code in Node or a browser; inspect decoded image pixels and initialized memory.
 0xade1a1de/mastik
C toolkit implementing micro-architectural side-channel attacks on Intel x86-64, including Prime+Probe, Flush+Reload, Flush+Flush, CacheBleed and…