
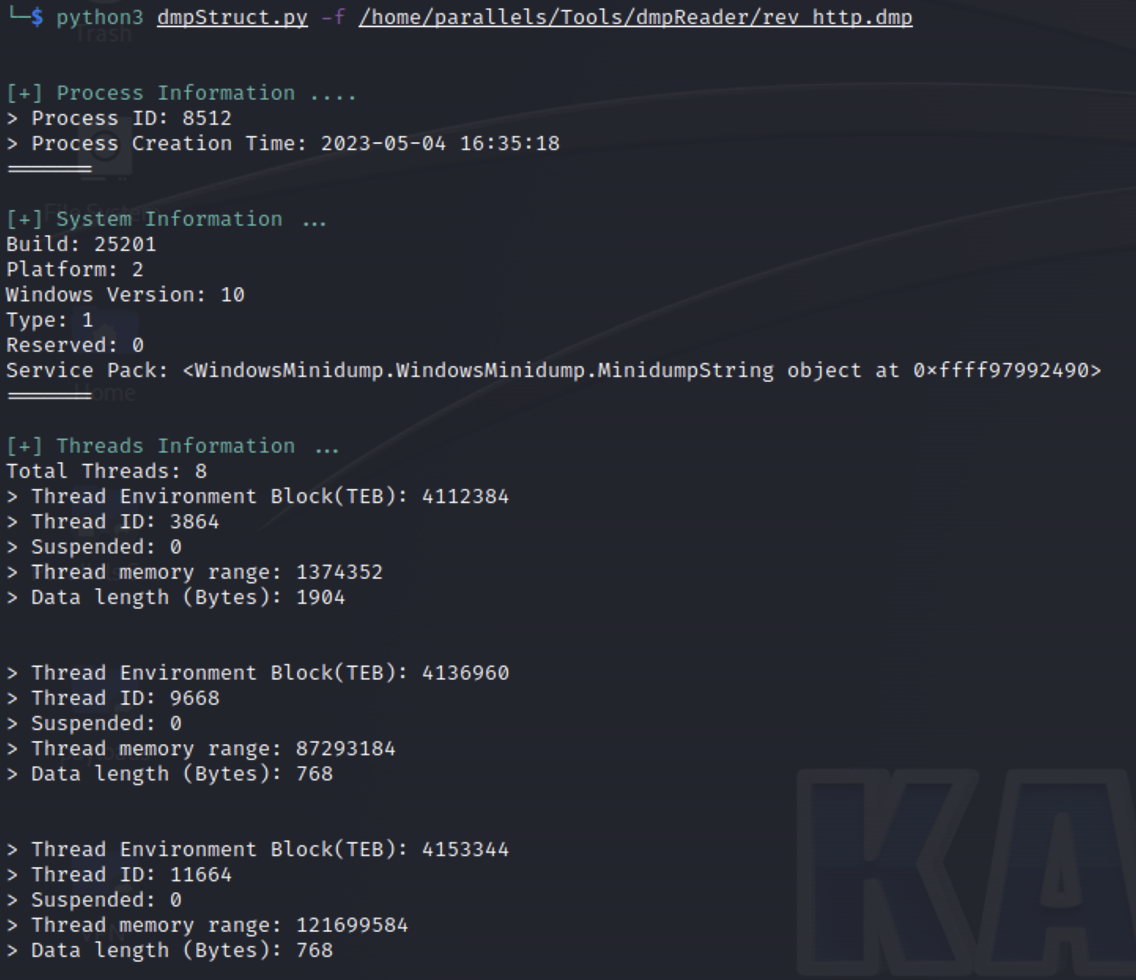
miniDumpReader
 gmh5225/minidumpreader
Parses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
binary-analysisdigital-forensicsforensics+3
gmh5225/minidumpreaderParses Windows MiniDump (MDMP) files with Kaitai Struct, extracting memory strings and scanning them against YARA rules for forensic and malware…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 nccgroup/windowspatchdetector
Experimental Windows .text section Patch Detector
 libyal/libfwsi
Library to access the Windows Shell Item format
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
 hiddenillusion/nomorexor
Tool to help guess a files 256 byte XOR key by using frequency analysis
 juul/xz-backdoor-scan
Scan for files containing the signature from the `xz` backdoor (CVE-2024-3094)
 cyberclues/rtf_exploit_extractor
Script to extract malicious payload and decoy document from CVE-2015-1641 exploit documents
 pazhanivelmani/libexif_android10_r33_cve-2016-6328
C-based library for parsing, editing, and saving EXIF metadata from JPEG images, with a focus on exploiting CVE-2016-6328 for Android 10.
 m10ust/machscope
macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
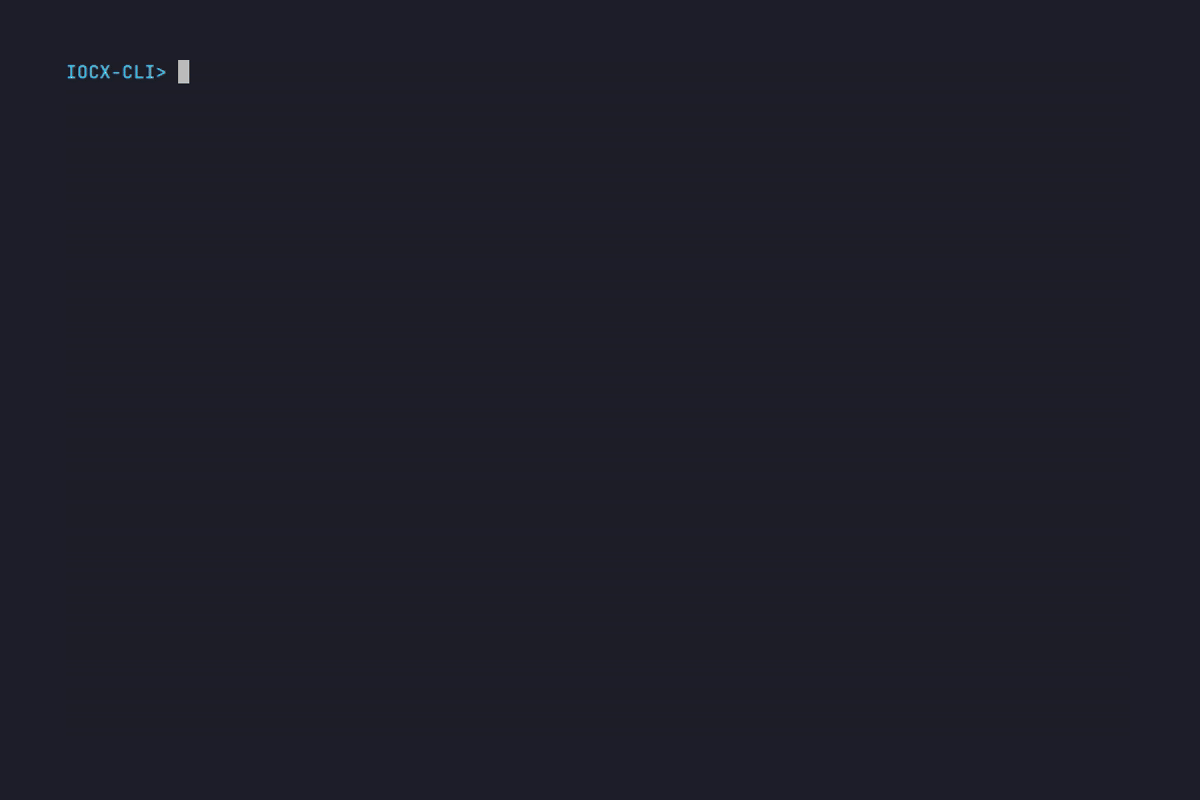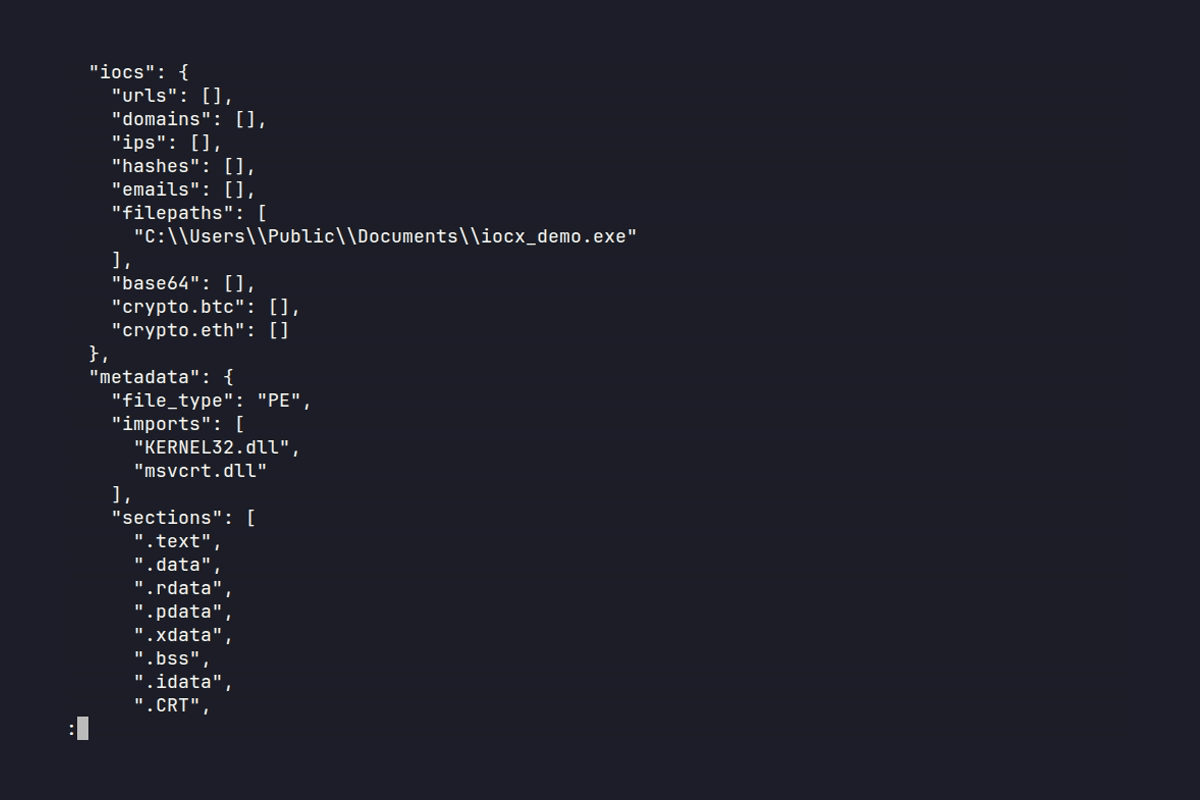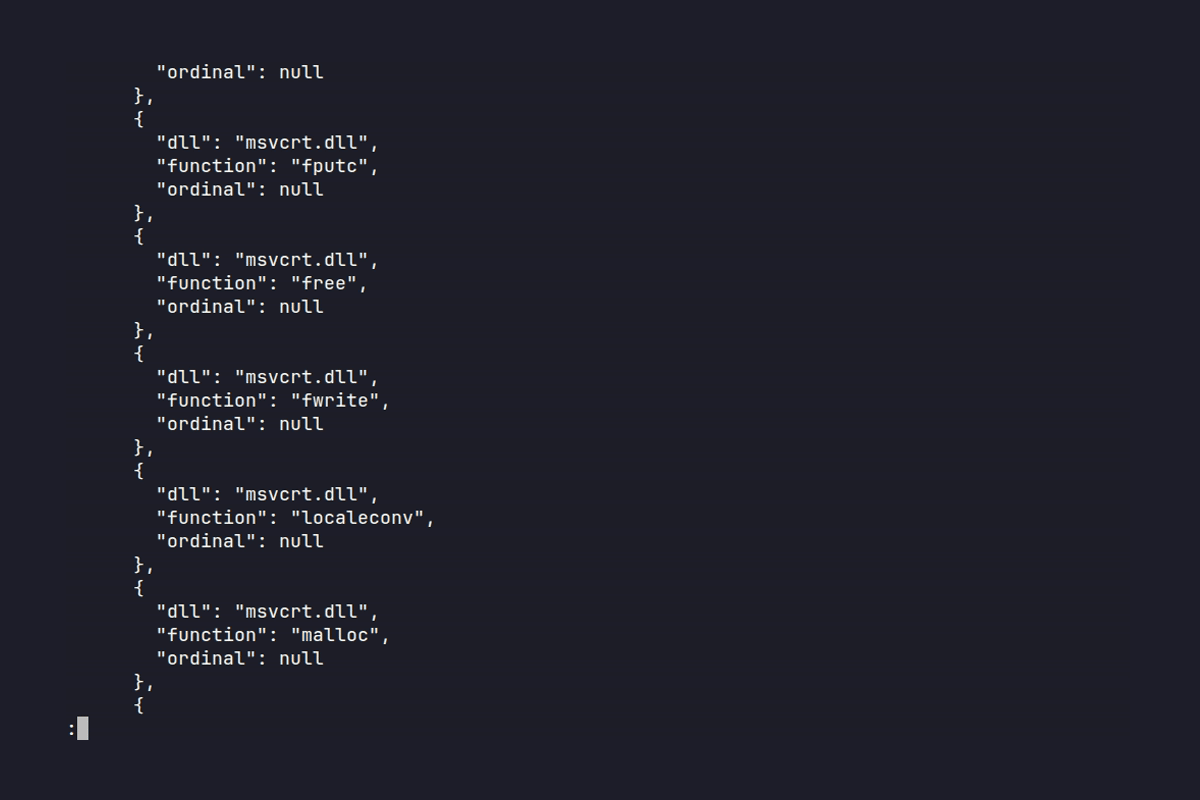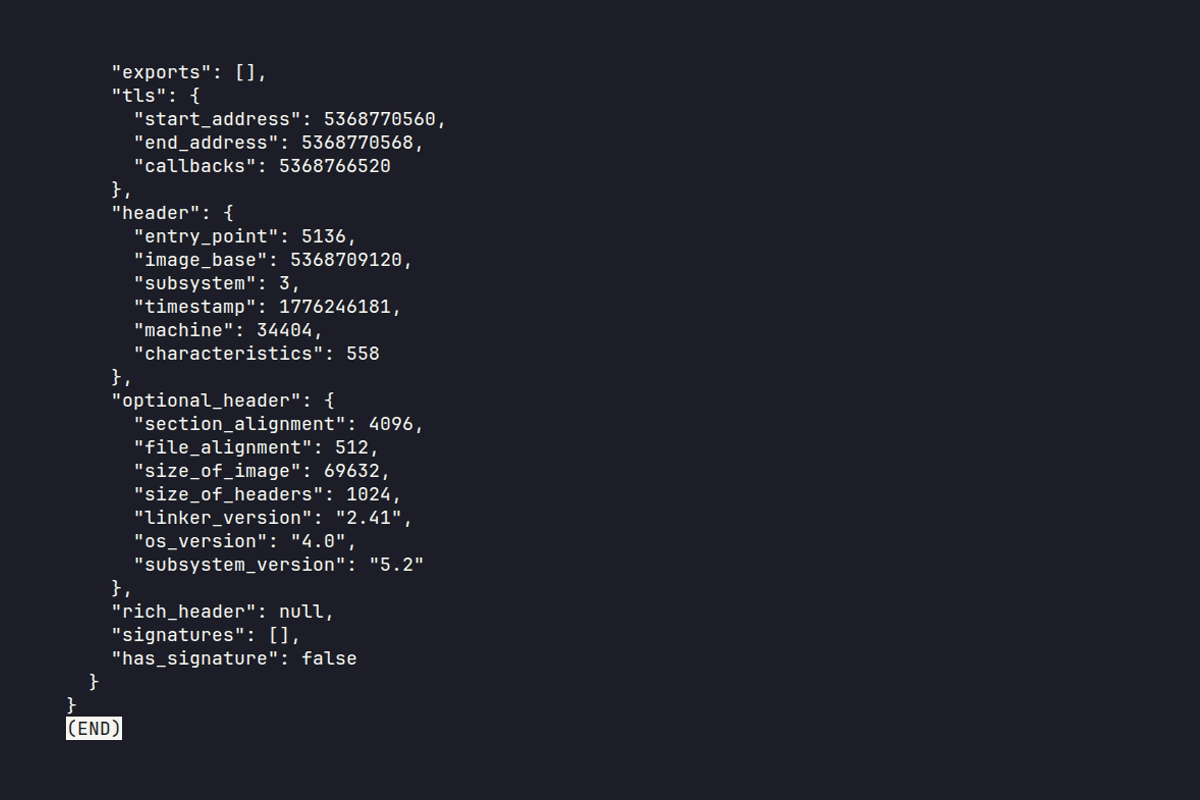 iocx-dev/iocx
An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 dimareverse/nuitka-static-unpacker
Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.
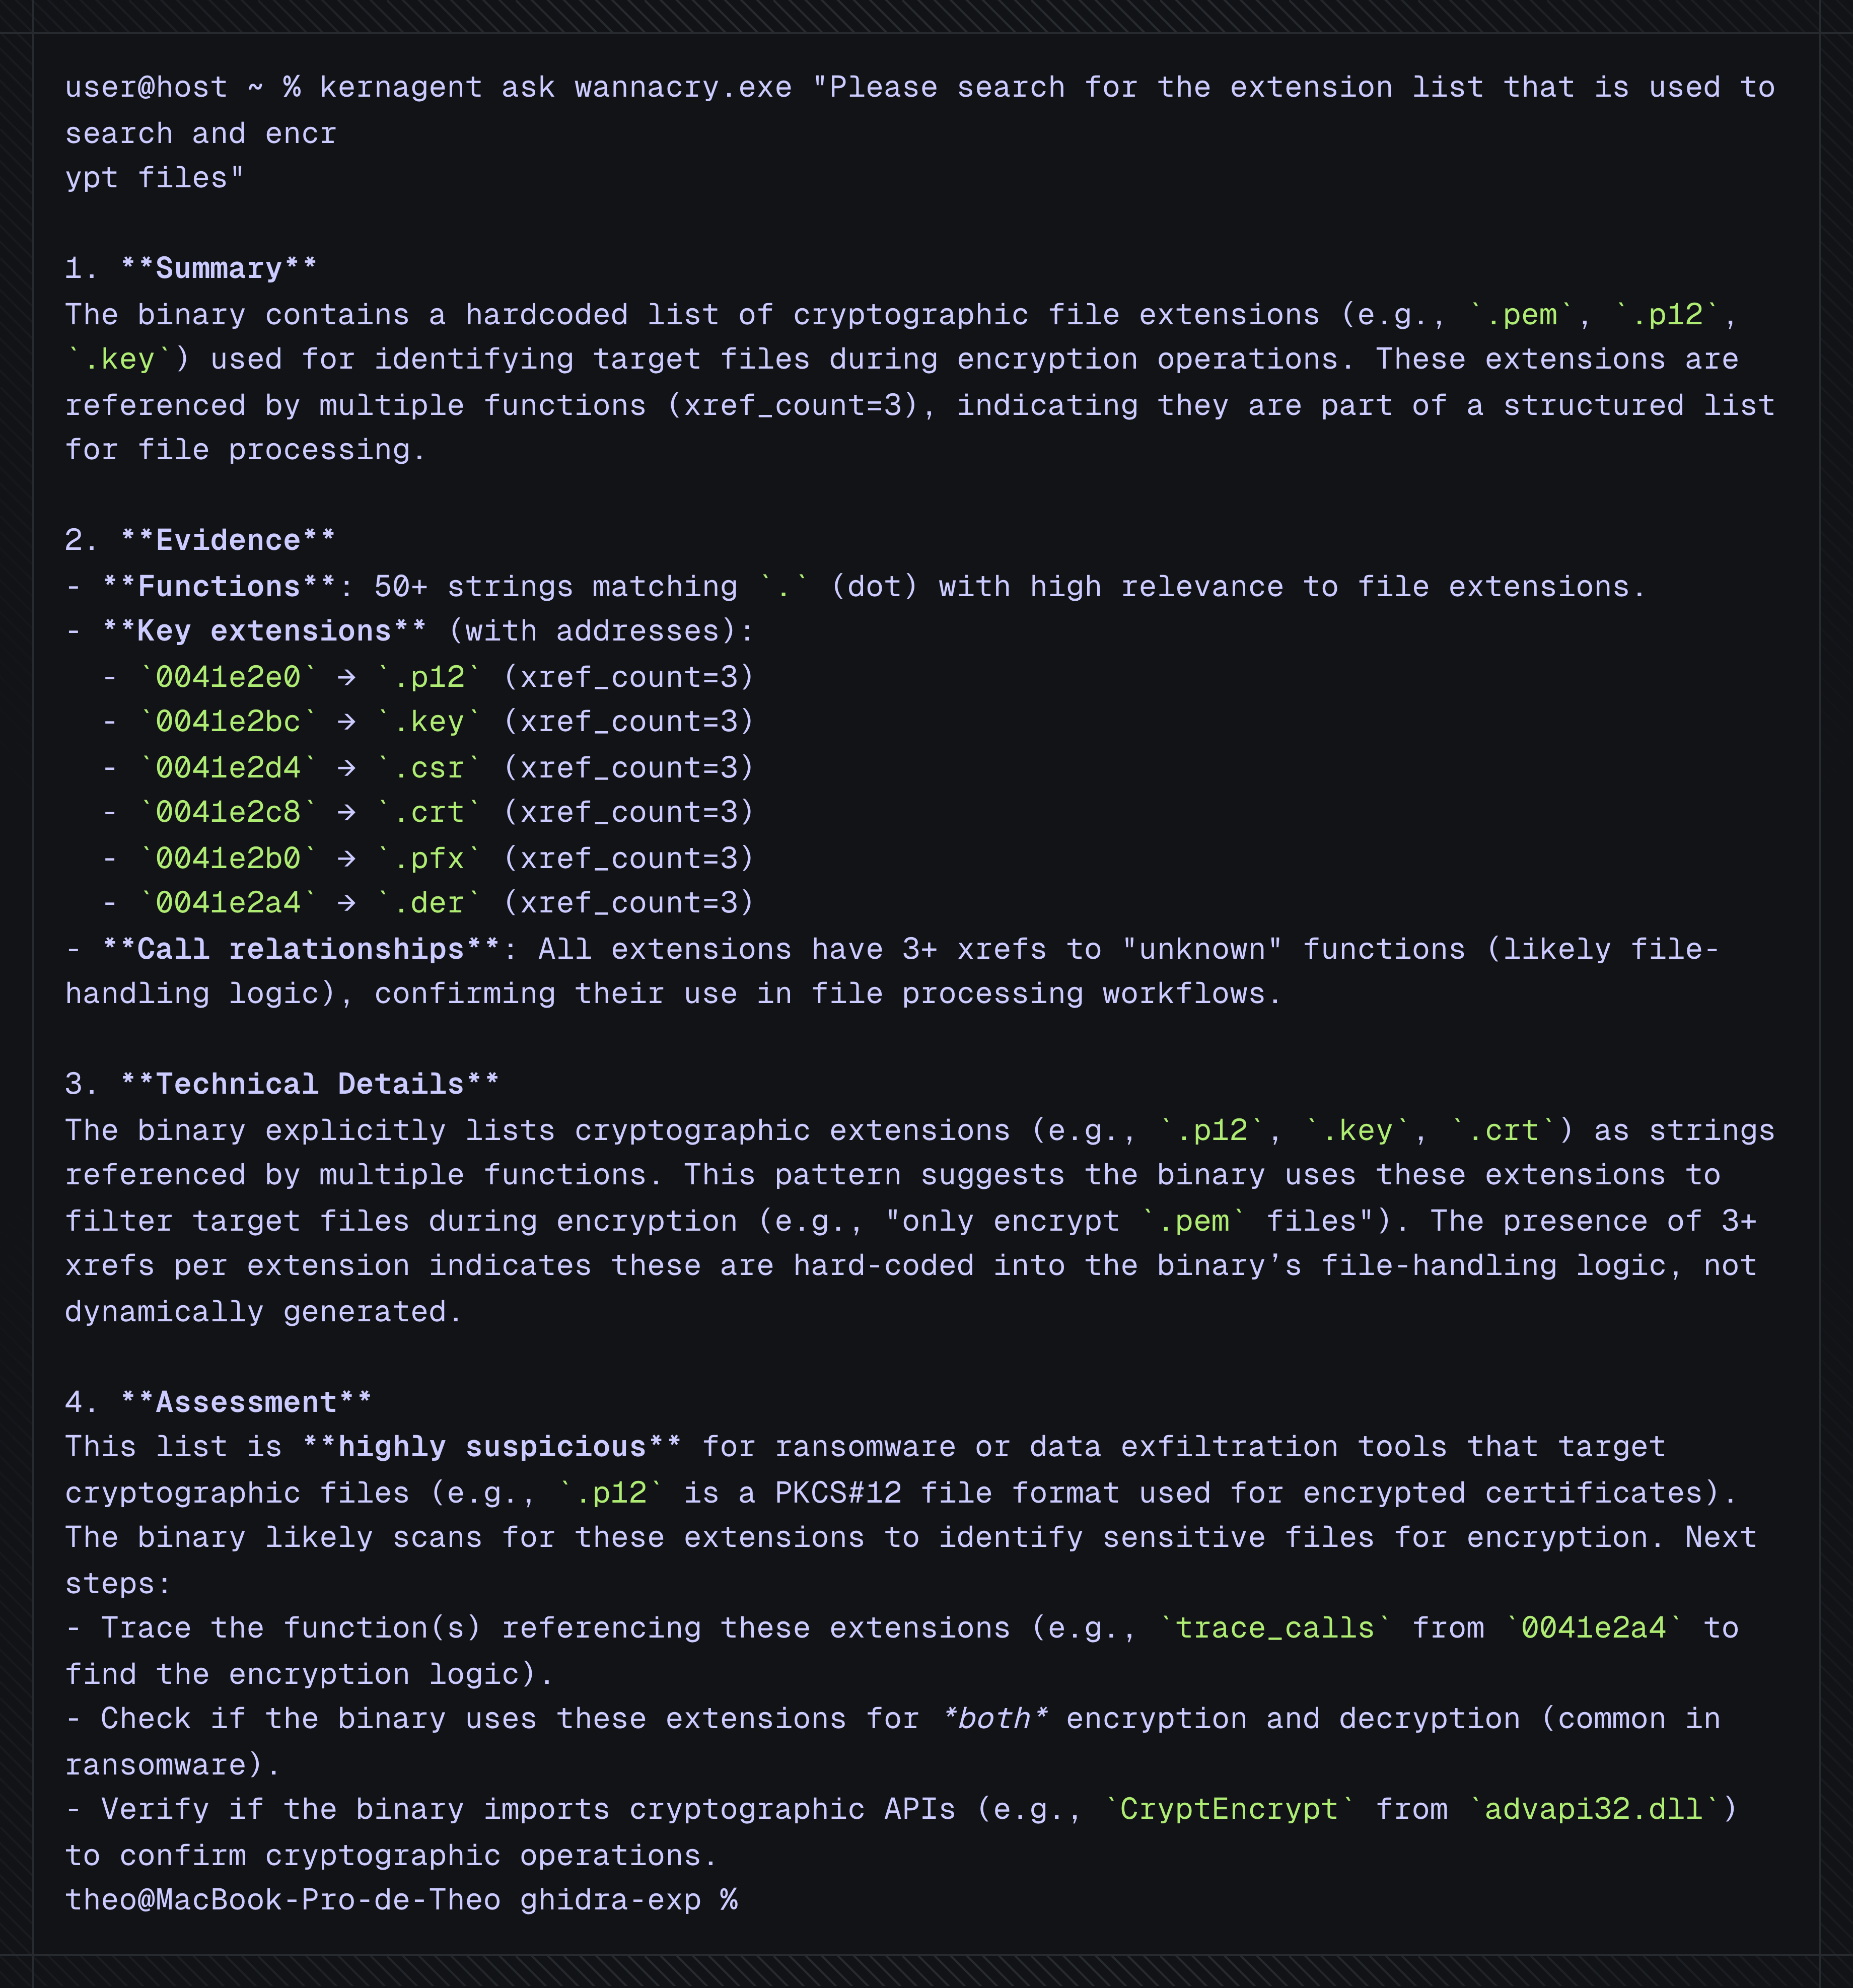 karib0u/kernagent
Headless AI agent for deterministic reverse engineering.