
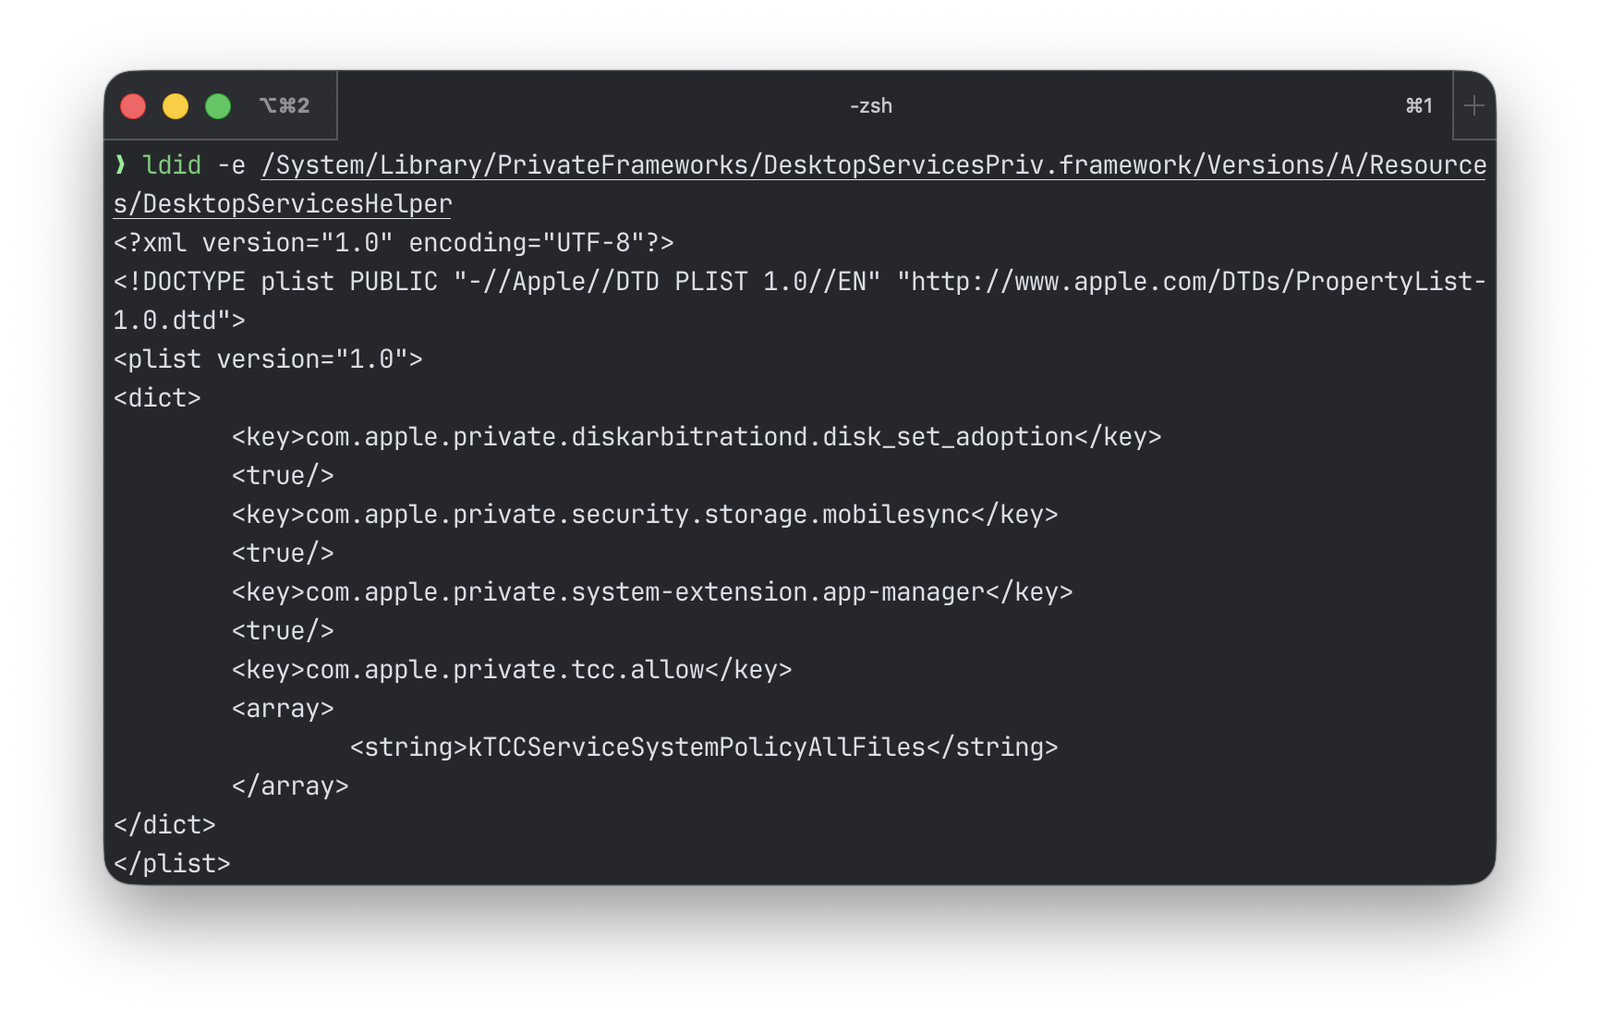
CVE-2026-43783
 andrd3v/cve-2026-43783
Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
binary-analysisexploitationpapers-research+4
2
andrd3v/cve-2026-43783Proof-of-concept and technical writeup for CVE-2026-43783, a macOS local privilege escalation via DesktopServicesHelper XPC arbitrary chown to gain…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 suleram/view8
Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
 virus-or-not/cve-2026-32202
Generates LNK files with crafted _IDCONTROLW structures to research Windows Shell spoofing vulnerabilities CVE-2026-21510 and CVE-2026-32202,…
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 george0papasotiriou/cve-2026-22187-bio-formats-unsafe-java-deserialization-via-.bfmemo
Bio-Formats ≤ 8.3.0 performs unsafe Java deserialization of attacker-controlled .bfmemo cache files during image processing; crafted .bfmemo can…
 pealeap/cve-2026-21045_and_cve-2026-21048
Generates crafted TIFF/DNG files to trigger out-of-bounds writes in Samsung's libimagecodec.quram.so, including binary analysis and reproduction…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
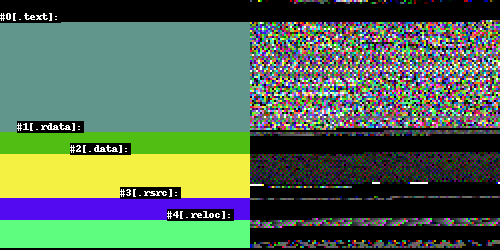 hasherezade/pe2pic
Small visualizator for PE files
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 hasherezade/pe-bear-old
PE-bear (builds only)