
OmniSec-Hex
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
ai-securitybinary-analysisfuzzing+9
vighnesh91/omnisec-hexBrowser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases

 fuzzysecurity/powershell-suite
My musings with PowerShell
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
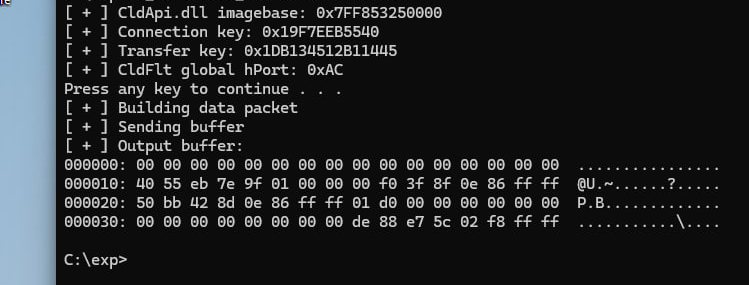 crackercat/cve-2024-26160
cldflt.sys information disclosure vulnerability (KB5034765 - KB5035853, Win 11).
 gtgalaxi/electronvulnerableversion
Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129
 sandi-go/ps-2017-13---cve-2018-9950
Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…
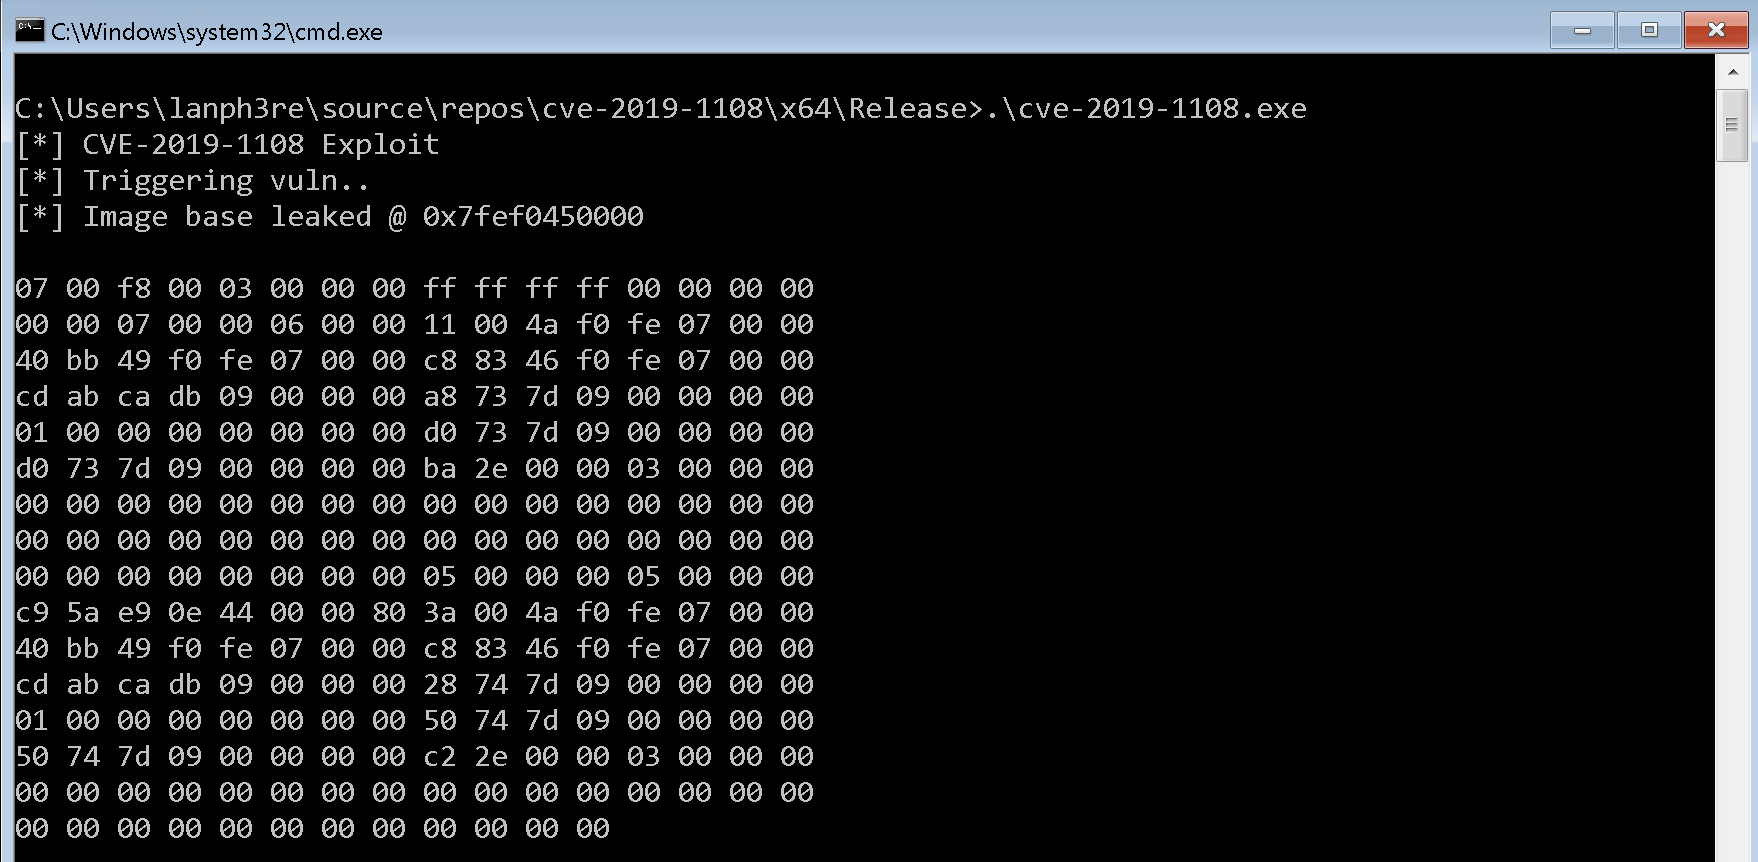 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 karollooool/cve-2026-50416-writeup-and-poc
CVE-2026-50416: Windows 11 KASLR bypass
 m10ust/machscope
macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool
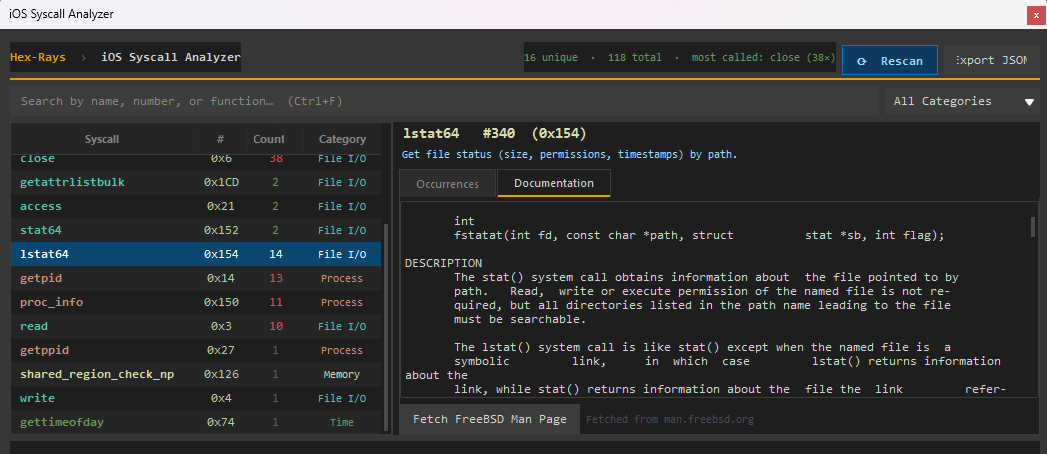 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X