Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
33 results
Driver-KeAttachProcess-KeDetachProcess-rebuild preview

Driver-KeAttachProcess-KeDetachProcess-rebuild

GitHubgmh5225/driver-keattachprocess-kedetachprocess-rebuild

Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.

binary-analysismalware-analysisreverse-engineering
2
4 years ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

binary-analysisembedded-systems-securityfirmware-analysis+3
4072 years ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
1016 days ago
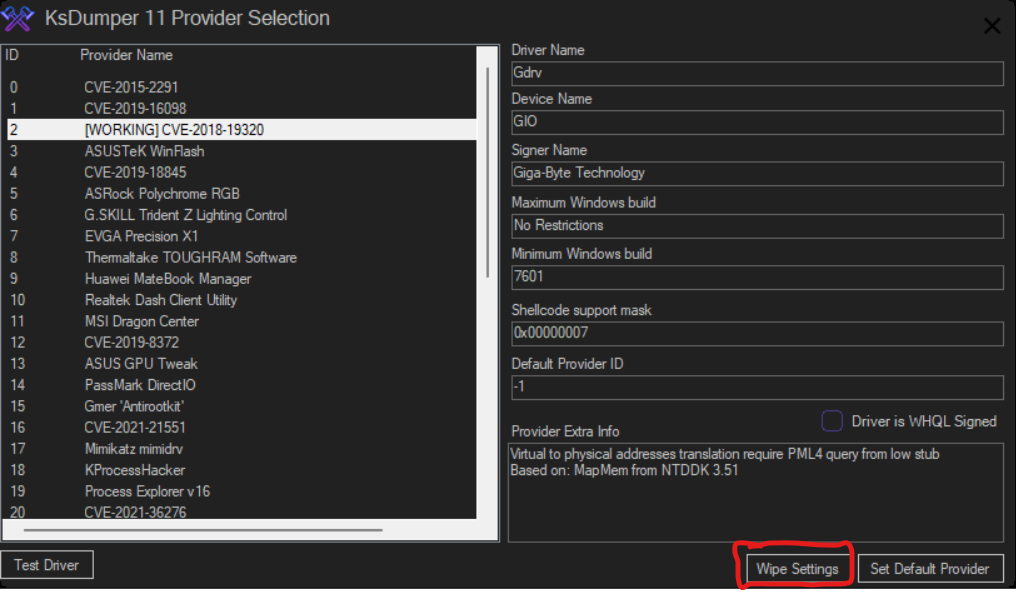
KsDumper-11 preview

KsDumper-11

GitHubmastercodeon314/ksdumper-11

A revival of the classic and legendary KsDumper

binary-analysisexploitationmemory-forensics+1
5871 year ago
CVE-2026-20805-PoC preview

CVE-2026-20805-PoC

GitHubuzair-baig0900/cve-2026-20805-poc

The PoC of information disclosure in Microsoft Desktop Windows Management.

binary-analysisexploitationinformation-gathering+2
28 months ago
upx-recovery-tool preview

upx-recovery-tool

GitHubnozominetworks/upx-recovery-tool

Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…

binary-analysismalware-analysisreverse-engineering
1183 years ago
ReverseKit preview

ReverseKit

GitHubzer0condition/reversekit

x64 Dynamic Reverse Engineering Toolkit

binary-analysisdynamic-code-analysismalware-analysis+1
7843 years ago
windows-api-function-cheatsheets preview

windows-api-function-cheatsheets

GitHub7etsuo/windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

binary-analysiscurated-resourcesmalware-analysis+3
1.5k1 year ago
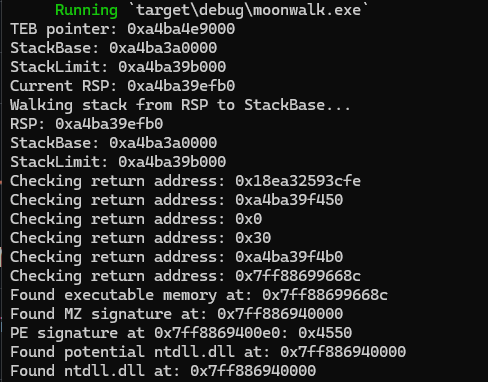
moonwalk preview

moonwalk

GitHubteach2breach/moonwalk

find dll base addresses without PEB WALK

binary-analysiseducationpayload-development+2
1701 year ago
TinyInst preview

TinyInst

GitHubgoogleprojectzero/tinyinst

A lightweight dynamic instrumentation library

binary-analysiscode-analysisdebuggers+3
1.4k17 days ago
RedTeamCCode preview

RedTeamCCode

GitHubmr-un1k0d3r/redteamccode

Red Team C code repo

binary-analysisdefensive-toolsmalware-analysis+1
5741 year ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
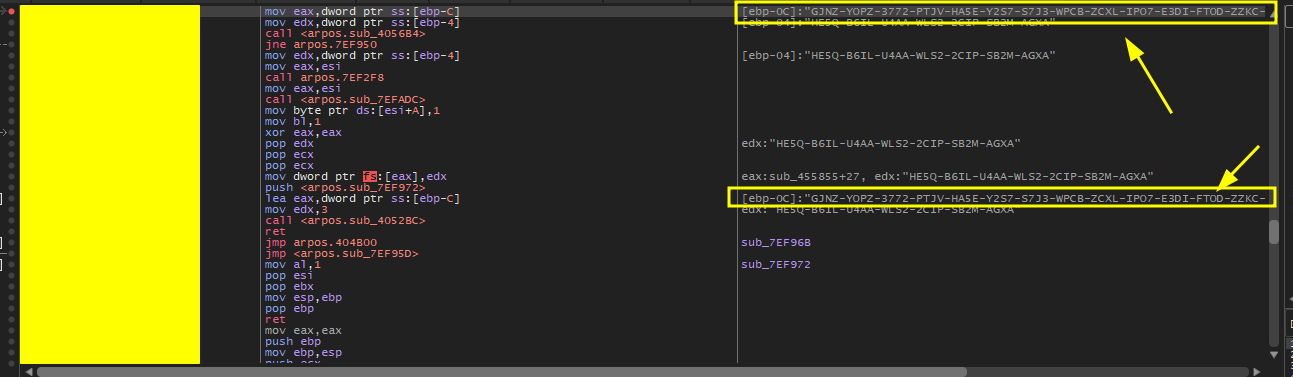
CVE-2025-65320 preview

CVE-2025-65320

GitHubyonathanpy/cve-2025-65320

CVE-2025-65320 proof-of-concept demonstrating cleartext license key extraction from process memory via debugger attachment, enabling software…

binary-analysisdebuggersexploitation+3
26 months ago
CVE-2025-54574-Squid-Heap-Buffer-Overflow preview

CVE-2025-54574-Squid-Heap-Buffer-Overflow

GitHubstarrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow

Vulnerability Found on Squid Proxy.

binary-analysisexploitationfuzzing+3
7 months ago
CVE-2025-14174-analysis preview

CVE-2025-14174-analysis

GitHubtypeconfused/cve-2025-14174-analysis

Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)

binary-analysisexploitationhardware-security+4
38 months ago
CVE-2025-61155 preview

CVE-2025-61155

GitHubsf0rzin/cve-2025-61155

CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…

binary-analysiseducationexploitation+7
32 months ago
apiscope preview

apiscope

GitHubkaisonox/apiscope

An API hooking framework for intercepting and monitoring Windows applications

api-security-testingbinary-analysisdebuggers+4
203 months ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .

binary-analysisdebuggerseducation+3
2155 days ago
Previous12Next