
KernelPatch
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
android-securitybinary-analysisbinary-exploitation+7
1.5k
bmax121/kernelpatchPatching and hooking the Linux kernel with only a stripped Linux kernel image.
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.
 eiln/ane
Reverse engineered Linux kernel driver and userspace library for the Apple Neural Engine (ANE), enabling hardware access and analysis on Linux…
 0xax/linux-insides
A book-in-progress about the Linux kernel and its insides.
 abdelkabirouadoukou/cve-2026-31431-analysis-and-fix
In-depth technical analysis of Linux kernel CVE-2026-31431 (Copy Fail), a local privilege escalation via AF_ALG in-place scatterlist bug, including…
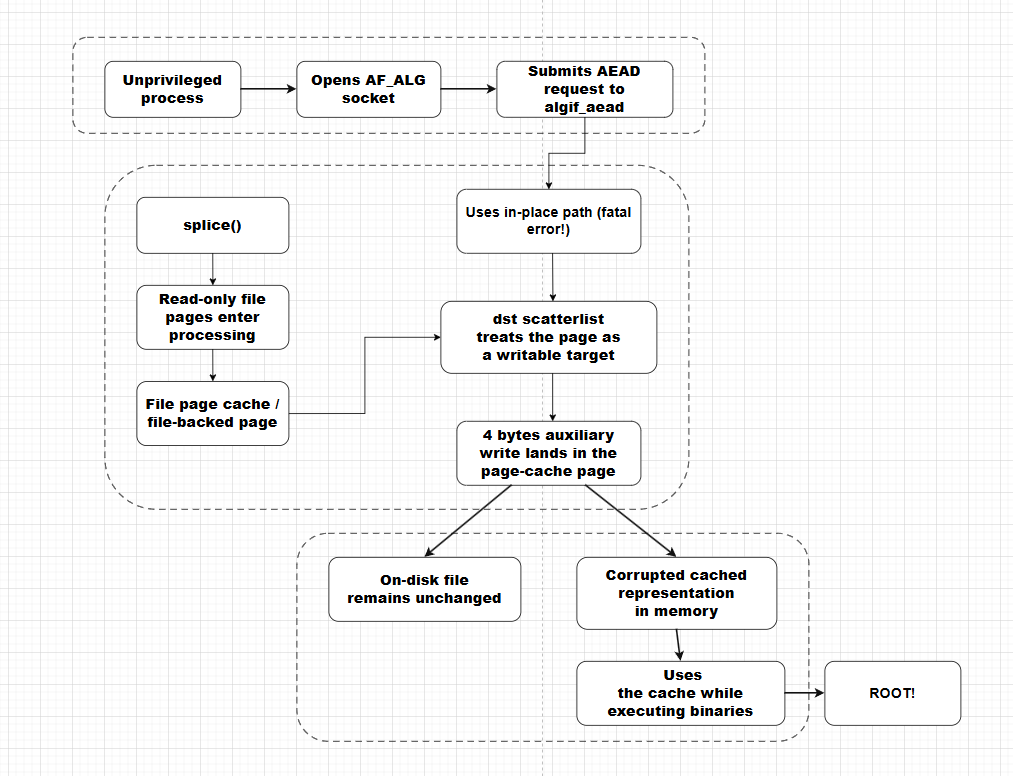 chernstepanov/copyfail-for-dummies
Research notes and proof-of-concept for Linux kernel CVE-2026-31431, documenting the AF_ALG splice() page cache corruption bug with source artifacts…
 securityronin/memory-forensic
Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
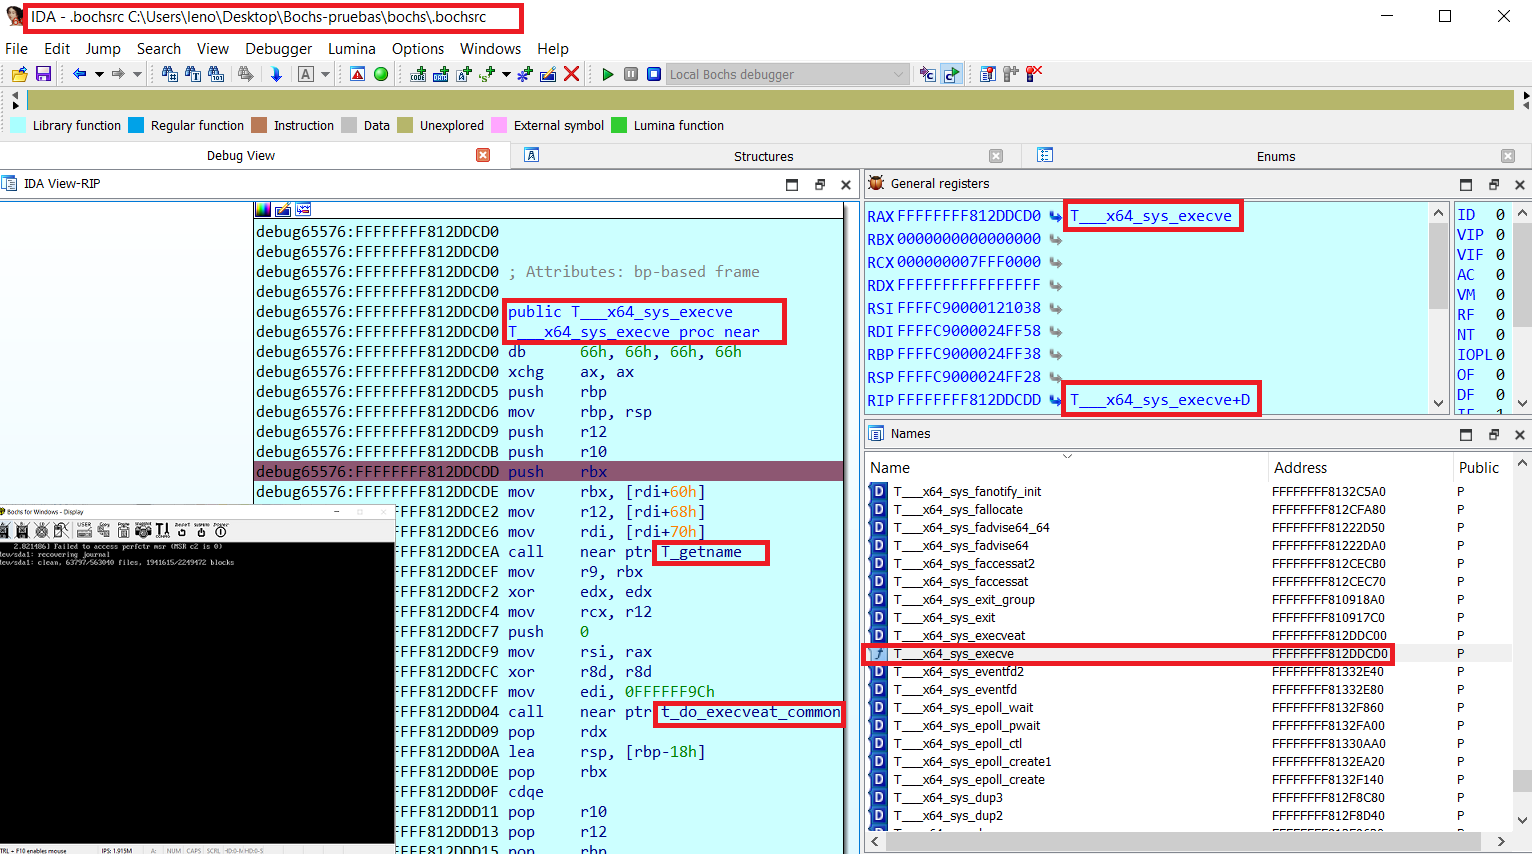 therealdreg/bochs_linux_kernel_debugging
Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
 nccgroup/triforceafl
AFL/QEMU fuzzing with full-system emulation.
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
 runtimeverification/kernel-c-to-rust-spike
Hardening kernel C parsers via Rust rewrite + differential fuzzing + formal verification. First target: UVC (CVE-2024-53104).
 tarunyadav/fix-cve-2013-2094
Generates portable SystemTap kernel modules to mitigate CVE-2013-2094 on Enterprise Linux systems, with automated build and deployment scripts for…
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 boratanrikulu/gobee
Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
 nanopathi/linux-4.19.72_cve-2020-29370
Linux kernel version 4.19.72 with a specific patch for CVE-2020-29370, intended for vulnerability analysis and exploitation research.