
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
17 results
LetMeGG preview

LetMeGG

GitHubgmh5225/letmegg

Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
anti-botbinary-analysisdebuggers+1
15
4 years ago
TitanHide preview

TitanHide

GitHubmrexodia/titanhide

Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
anti-botbinary-analysisdebuggers+4
2.9k2 months ago
rea preview

rea

GitHubmorluto/rea

Reverse engineer anything with agents, from app behavior down to native binaries.
ai-assisted-reversingai-securitybinary-analysis+5
2.0k5 days ago
EAC preview

EAC

GitHubgmh5225/eac

Compiles EAC and EOC anti-cheat SDKs, reversing research, and code resources to study how game anti-cheat systems integrate and operate.

binary-analysiscurated-resourceseducation+2
112 years ago
Driver-PiDqSerializationWrite-Example preview

Driver-PiDqSerializationWrite-Example

GitHubgmh5225/driver-pidqserializationwrite-example

How to use PiDqSerializationWrite. Introduces how to safely read and write from mapped driver
binary-analysisdebuggersdynamic-analysis-sandboxing+5
23 years ago
CrackMeZ3S-CTF-CrackMe-Tutorial preview

CrackMeZ3S-CTF-CrackMe-Tutorial

GitHubpelock/crackmez3s-ctf-crackme-tutorial

How to write a CrackMe for a CTF competition. Source code, technical explanation, anti-debugging and anti reverse-engineering tricks.
binary-analysisctfeducation+2
483 years ago
OWN-Defender preview

OWN-Defender

GitHubnirvanaon/own-defender

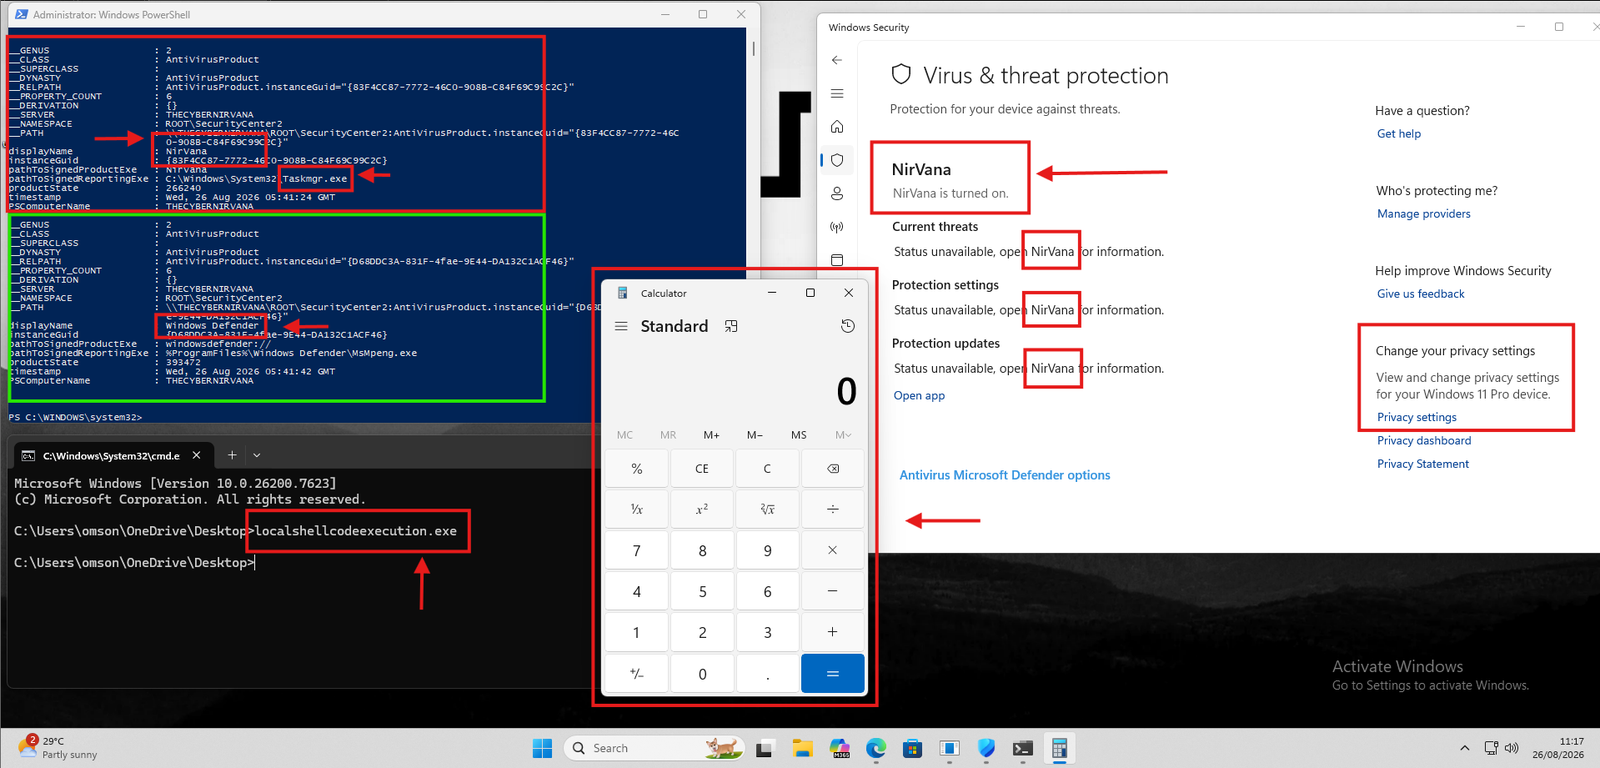
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
binary-analysisdefensive-toolseducation+2
361 month ago
CVE-2026-0073-Research preview

CVE-2026-0073-Research

GitHubnovaek/cve-2026-0073-research

CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
binary-analysisexploitationreverse-engineering+2
55 months ago
TEE-reversing preview

TEE-reversing

GitHubenovella/tee-reversing

A curated list of public TEE resources for learning how to reverse-engineer and achieve trusted code execution on ARM devices
android-securitybinary-analysiscurated-resources+9
1.0k9 months ago
packer-tutorial preview

packer-tutorial

GitHubfrank2/packer-tutorial

A tutorial on how to write a packer for Windows!
binary-analysiseducationmalware-analysis+1
3182 years ago
revsync preview

revsync

GitHublunixbochs/revsync

realtime cross-tool collaborative reverse engineering
binary-analysiscode-analysisreverse-engineering
1003 years ago
psr preview

psr

GitHubnccgroup/psr

Pointer Sequence Reverser - enable you to see how Windows C++ application is accessing a particular data member or object.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
768 years ago
pyshell2bin preview

pyshell2bin

GitHubelevenpaths/pyshell2bin

pyshell2bin

binary-analysisexploitationpayload-development+2
36 years ago
CVE-2023-42829 preview

CVE-2023-42829

GitHubjamesd4/cve-2023-42829

Analysis of a logic vulnerability in the macOS SSH client leading to client passphrase exposure to a local attacker
authenticationbinary-analysiseducation+2
21 year ago
CVE-2025-70330 preview

CVE-2025-70330

GitHubthemalwareguardian/cve-2025-70330

Easy Grade Pro 4.1 file parsing bug used as an educational example to show how beginners can start vulnerability research through reverse engineering.
binary-analysisbinary-exploitationcode-analysis+7
26 months ago
Flutter-Reverse-Engineering-Labs preview

Flutter-Reverse-Engineering-Labs

GitHubbrnpl/flutter-reverse-engineering-labs

Hands-on challenges for learning how to reverse engineer Flutter applications.
android-securitybinary-analysisctf+6
5925 days ago
game-of-kingshot-re preview

game-of-kingshot-re

GitHubkdbugk/game-of-kingshot-re

Educational reverse engineering study of a Unity/IL2CPP Android game. Documents gateway protocol decoding, native anti-tampering SDK analysis, SSL…

android-securitybinary-analysisdynamic-analysis-sandboxing+5
355 months ago