
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
28 results
Enigma preview

Enigma

GitHubbunnybuzz/enigma

Native C++ reverse-engineering engine with disassembly, decompilation, and analysis pipeline for PE/ELF binaries, featuring interactive GUI and…
ai-assisted-reversingbinary-analysisdebuggers+3
61
10 days ago
RPC-Triage preview

RPC-Triage

GitHubtalha-nazeef-ahmed/rpc-triage

A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
binary-analysisreconnaissancered-teaming+3
141 month ago
VivisectION preview

VivisectION

GitHubatlas0fd00m/vivisection

Analysis Plugin and Tools for Vivisect
binary-analysisdebuggersdynamic-analysis-sandboxing+2
221 month ago
moonwalk preview

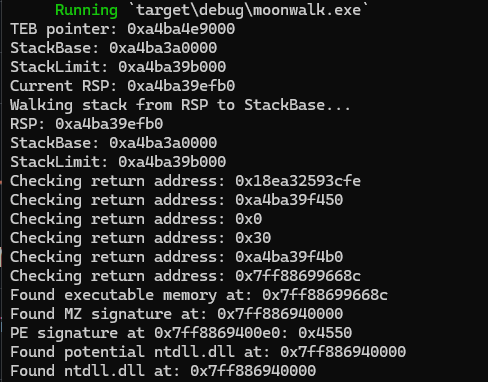
moonwalk

GitHubteach2breach/moonwalk

find dll base addresses without PEB WALK
binary-analysiseducationpayload-development+2
1691 year ago
Winstrument preview

Winstrument

GitHubnccgroup/winstrument

Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
binary-analysisdynamic-code-analysisreverse-engineering+1
686 years ago
thats_no_pipe preview

thats_no_pipe

GitHubsynacktiv/thats_no_pipe

Windows named pipe hooking toolkit

binary-analysisdebuggersdynamic-analysis-sandboxing+3
456 months ago
Maverick preview

Maverick

GitHubblacksnufkin/maverick

Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
binary-analysiscommand-and-controlencryption-decryption-tools+5
1183 months ago
windows_tcpip_fuzz preview

windows_tcpip_fuzz

GitHubpersonnumber3377/windows_tcpip_fuzz

This is my attempt at fuzzing the tcpip.sys driver in windows via using scapy. This is inspired by this vulnerability here:…

binary-analysisexploitationfuzzing+2
1 year ago
Find-VulnerableElectronVersion preview

Find-VulnerableElectronVersion

GitHuboitapps/find-vulnerableelectronversion

Scans an executable and determines if it was wrapped in an Electron version vulnerable to the Chromium vulnerability CVE-2023-4863/ CVE-2023-5129

binary-analysisstatic-analysisvulnerability-analysis
52 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

binary-analysiscommand-and-controldigital-forensics+7
672 months ago
SHGenOb preview

SHGenOb

GitHuboldboy21/shgenob

Python based tool for generating Shellcode from PIC C
binary-analysiseducationencryption-decryption-tools+5
4310 months ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex
binary-analysisforensicsmalware-analysis+3
209 months ago
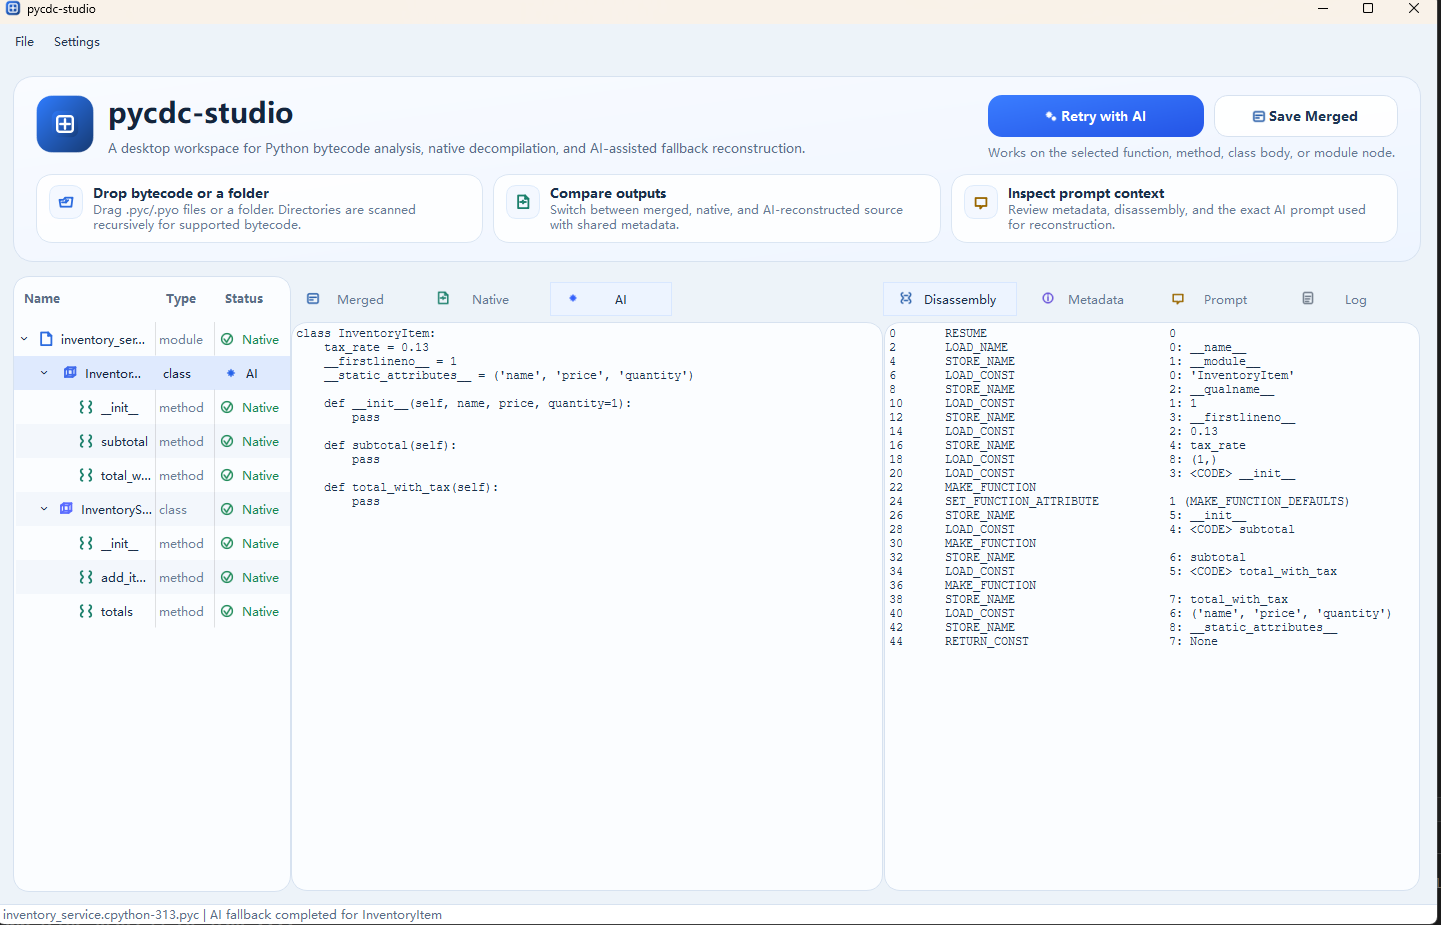
pycdc-studio preview

pycdc-studio

GitHubddouworld/pycdc-studio

A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
ai-assisted-reversingbinary-analysisdebuggers+4
425 months ago
android-reverse-engineering-skill preview

android-reverse-engineering-skill

GitHubsimoneavogadro/android-reverse-engineering-skill

Decompiles Android APK/XAPK/JAR/AAR files and extracts HTTP APIs, authentication patterns, and call flows using jadx, with R8-resistant Kotlin name…
android-securityapi-security-testingbinary-analysis+8
7.9k18 days ago
CVE-2025-9491_POC preview

CVE-2025-9491_POC

GitHubamperclock/cve-2025-9491_poc

Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)

binary-analysiseducationexploitation+3
1810 months ago
DeepZero preview

DeepZero

GitHub416rehman/deepzero

Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
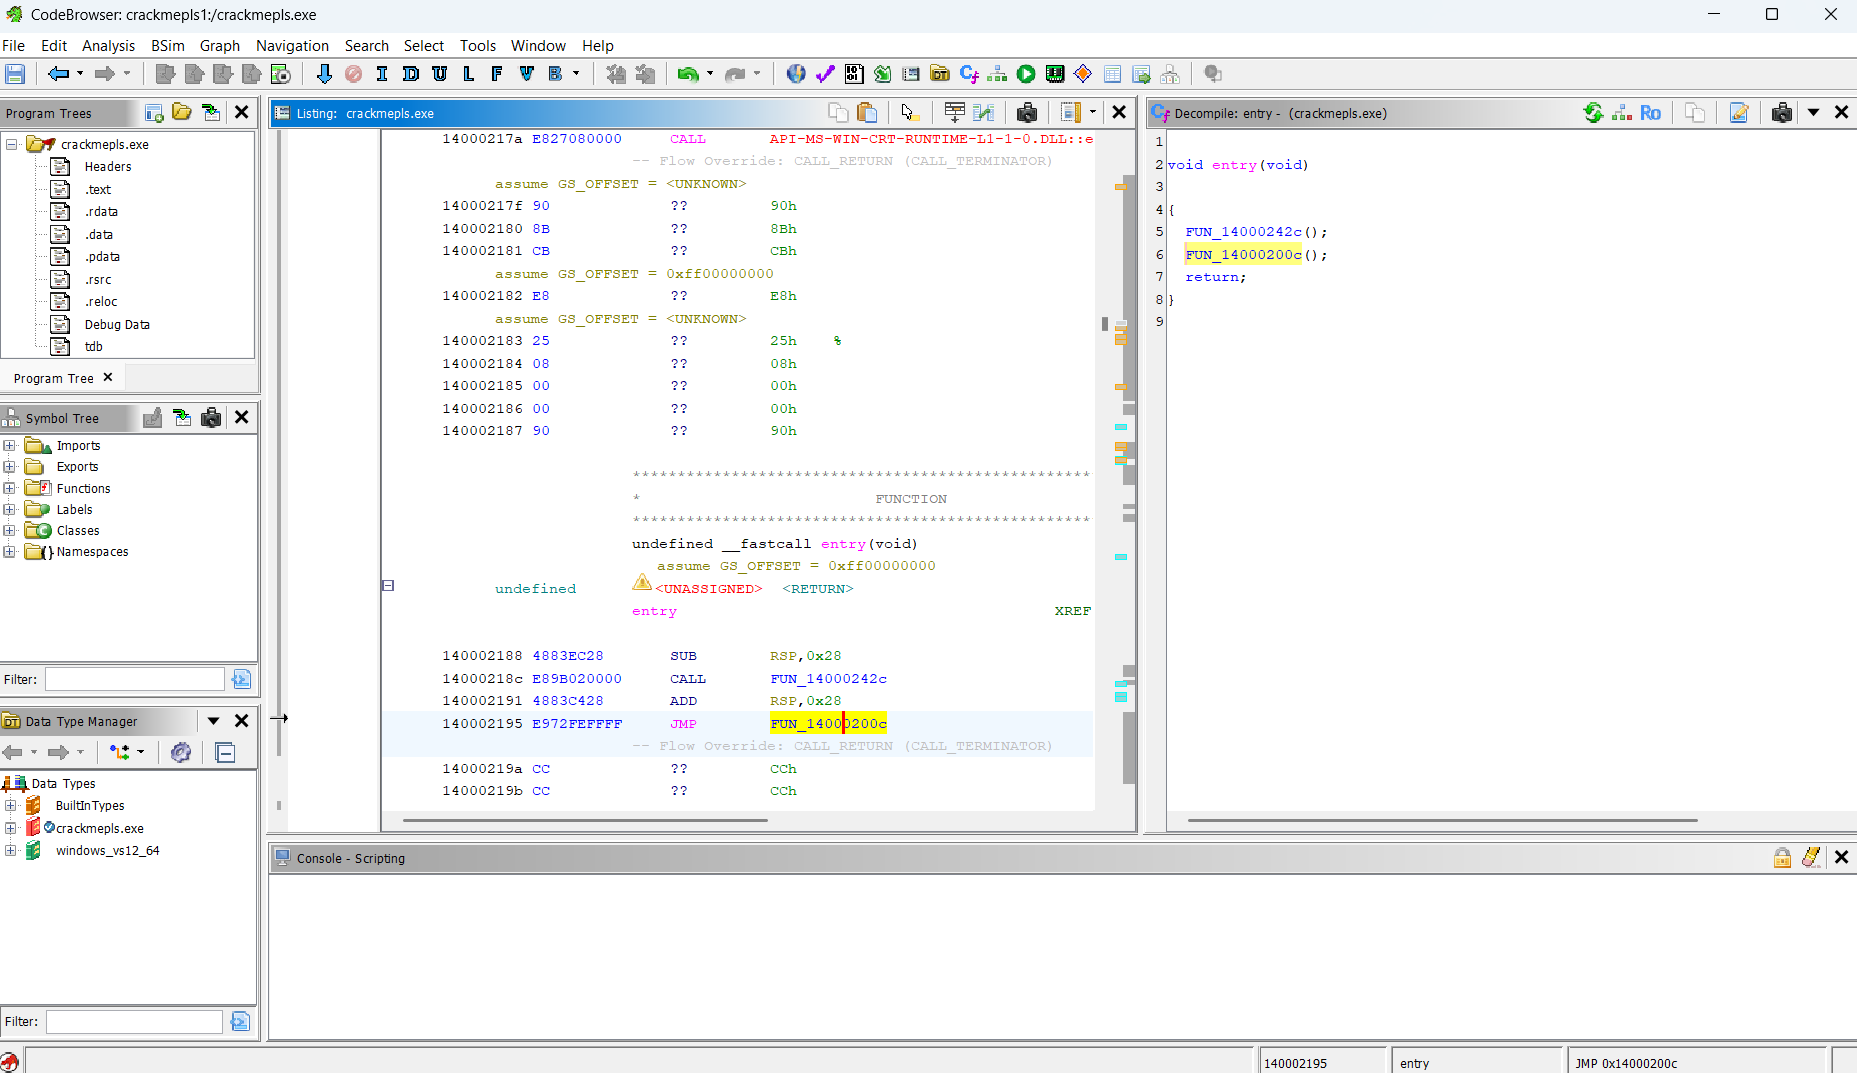
ai-assisted-reversingbinary-analysisfuzzing+3
72816 days ago
gemma_crackme_tutorial preview

gemma_crackme_tutorial

GitHubmarkoglasgow/gemma_crackme_tutorial

Step-by-step tutorial on using Google's Gemma 4 E4B local AI model to reverse engineer a Windows crackme with Ghidra, including setup for local…
ai-assisted-reversingbinary-analysisdebuggers+3
355 months ago
bincat preview

bincat

GitHubairbus-seclab/bincat

Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection

binary-analysisdebuggersreverse-engineering+2
1.9k1 year ago
Previous12Next