CVE-2026-3008
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
binary-analysisexploitationmalware-analysis+2
1
llgsjsm/cve-2026-3008Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
 jaf0rk/cve-2026-3909
Proof-of-concept exploit for CVE-2026-3909, a Chromium Skia out-of-bounds vulnerability, with patches and crash analysis for reliable triggering in…
 dwisiswant0/cve-2025-46819
Proof-of-concept exploit for CVE-2025-46819, a Redis Lua long-string delimiter out-of-bounds read, demonstrating a crash via malformed input.
 bilalclicksafe/cve-2025-60595
SPH Engineering UgCS 5.13.0 is vulnerable to Arbitary code execution. This is the public refrence to be used on CVE site
 nygard/class-dump
Generate Objective-C headers from Mach-O files.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 synacktiv/mojarragadget
Proof-of-concept exploit for a Java gadget chain in the Mojarra library, demonstrating deserialization vulnerability exploitation for versions 2.3…
 0xjohnnydev/webkit-navigationapi-sop-bypass
WebKit NavigateEvent.canIntercept SOP bypass via cross-port interception — iOS 26.3.1 BSI (CVE-2026-20643)
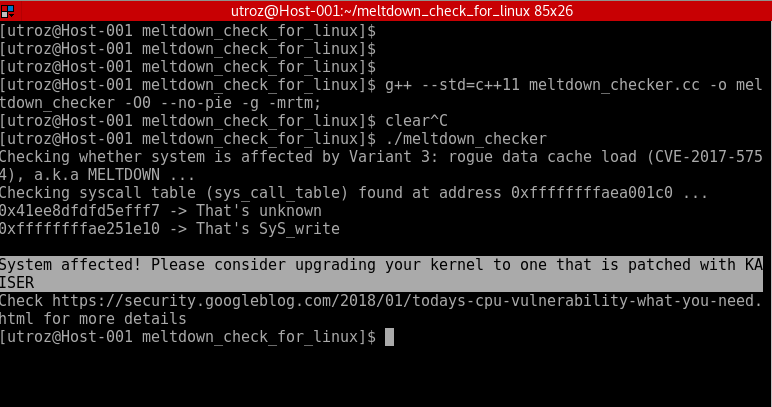 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
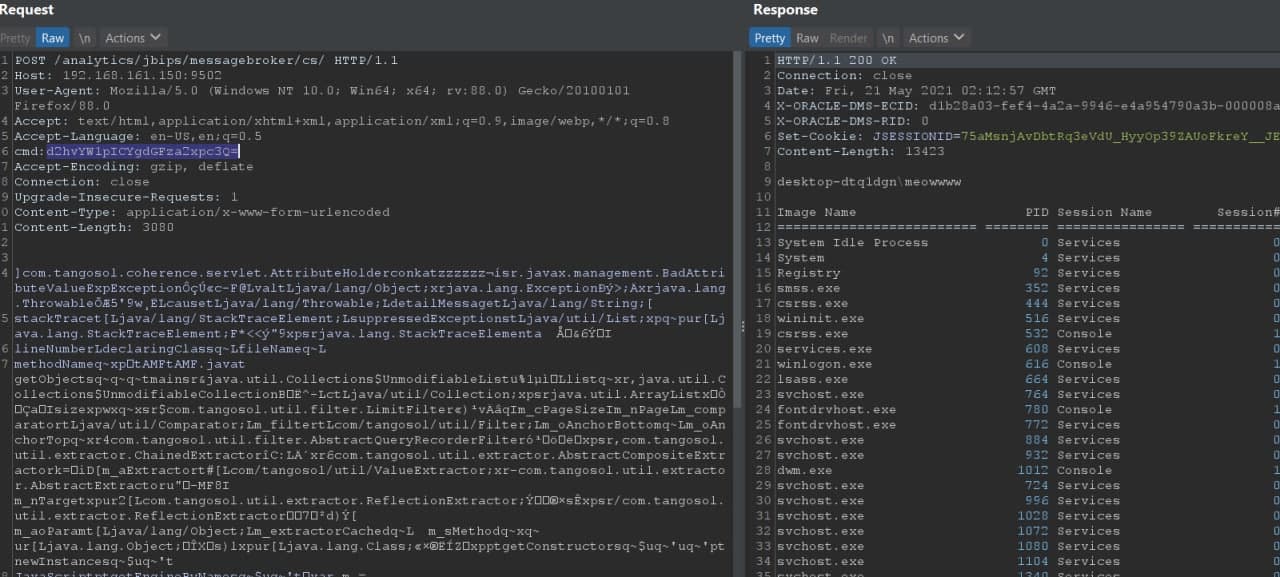 tuo4n8/cve-2020-2950
Proof-of-concept exploit for CVE-2020-2950, demonstrating AMF deserialization to Java deserialization in Oracle Business Intelligence, with debug…
 redfox-security/hacking-electron-apps-cve-2020-35717-
Exploit for CVE-2020-35717 targeting Electron applications, demonstrating a specific vulnerability and providing a proof-of-concept for security…
 typeconfused/cve-2025-14174-analysis
Analysis and PoC for CVE-2025-14174 - ANGLE Metal OOB write (iOS Safari, macOS Chrome)
 halcy0nic/cve-2023-38434
Proof of Concept for CVE-2023-38434
 thinkycx/activemq-rce-cve-2023-46604
activemq-rce-cve-2023-46604
 shack2/javaserializetools
Java反序列化漏洞利用工具V1.0 Java反序列化相关漏洞的检查工具,采用JDK 1.8+NetBeans8.2开发,软件运行必须安装JDK 1.8或者以上版本。 支持:weblogic xml反序列化漏洞…