

p0tools
 googleprojectzero/p0tools
Collection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
binary-analysiscurated-resourceseducation+5
856
googleprojectzero/p0toolsCollection of Google Project Zero vulnerability research documents and small standalone security tools, including exploitation and…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 idamcp/idamcp
MCP server integrating IDA Pro with AI agents, featuring a stateless gateway for multi-session management, a relational SQL query engine for binary…
 icicle-emu/icicle-python
Python bindings for the Icicle emulator, enabling grey-box firmware fuzzing, binary emulation, and reverse-engineering workflows across x64 and ARM64…
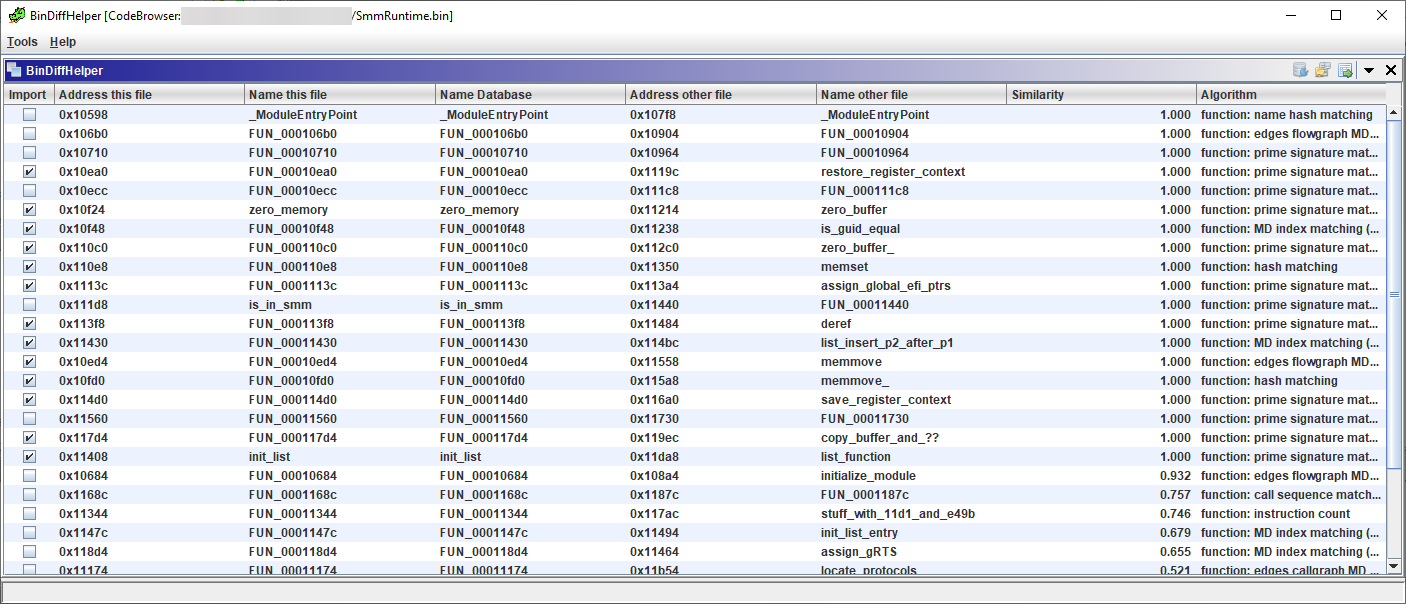 ubfx/bindiffhelper
Ghidra Extension to integrate BinDiff for function matching
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
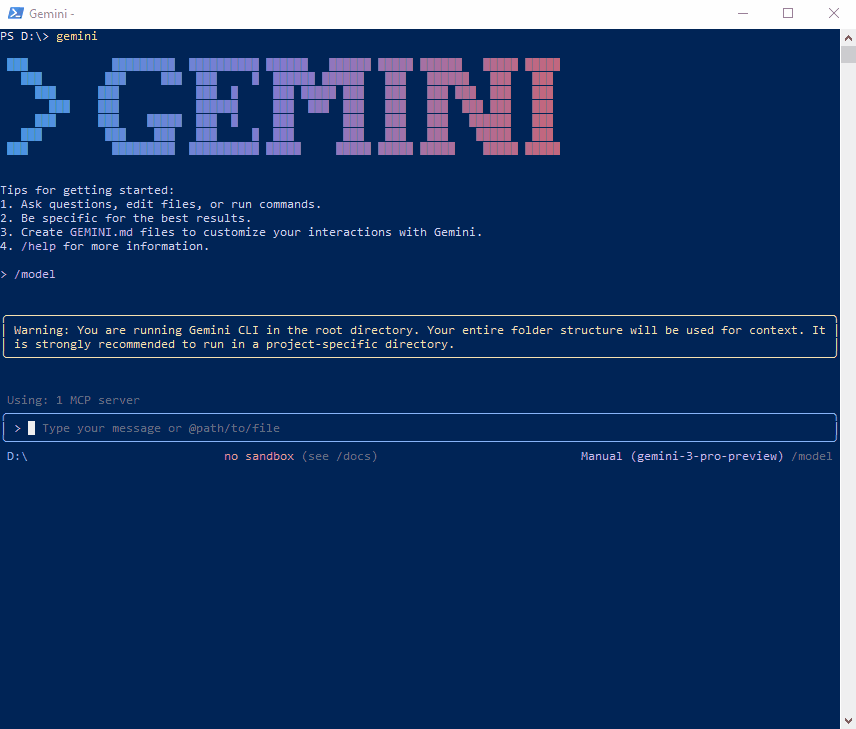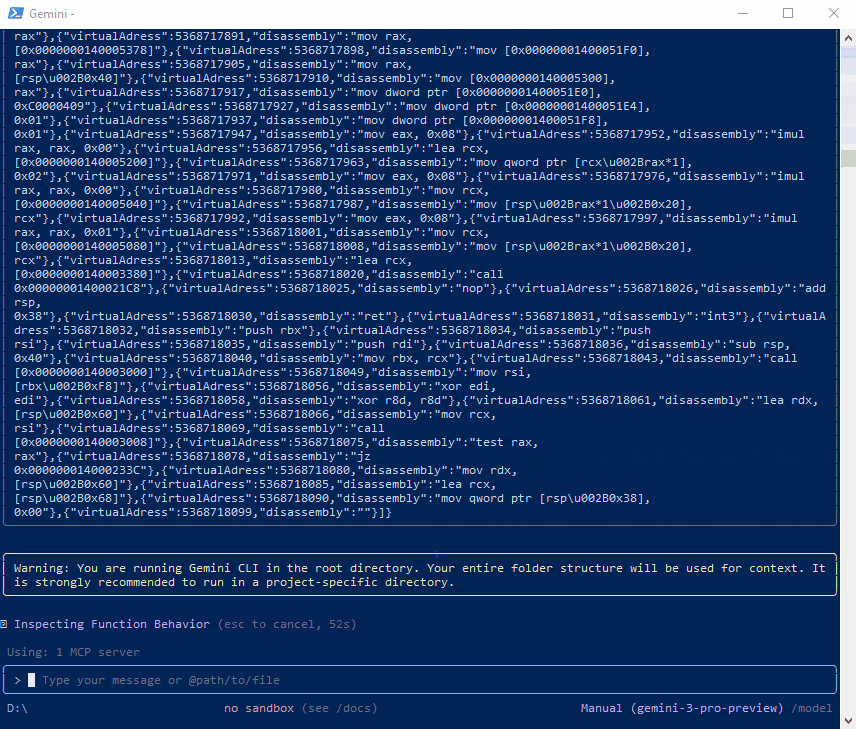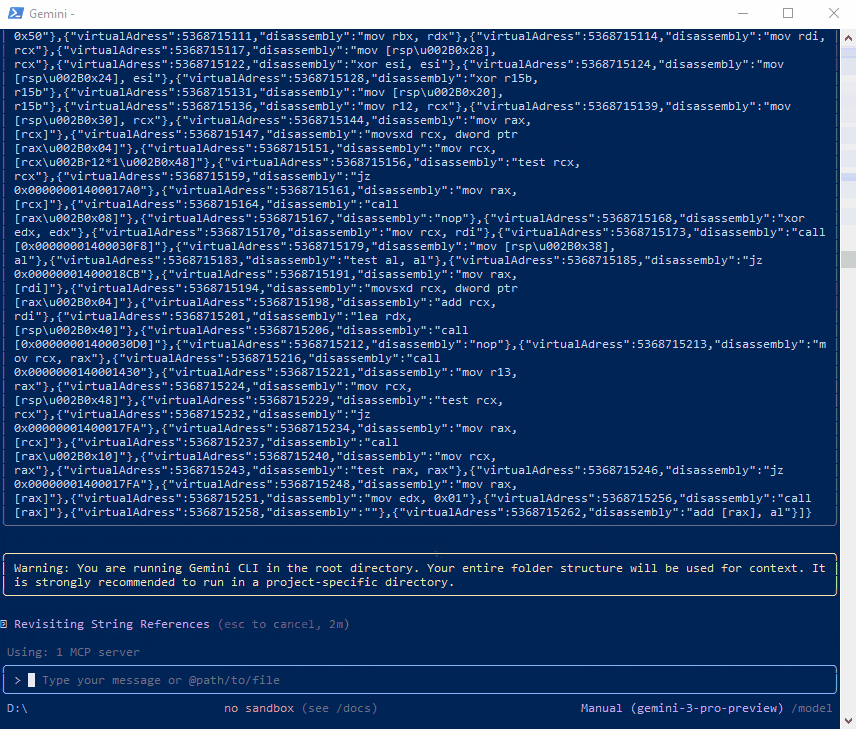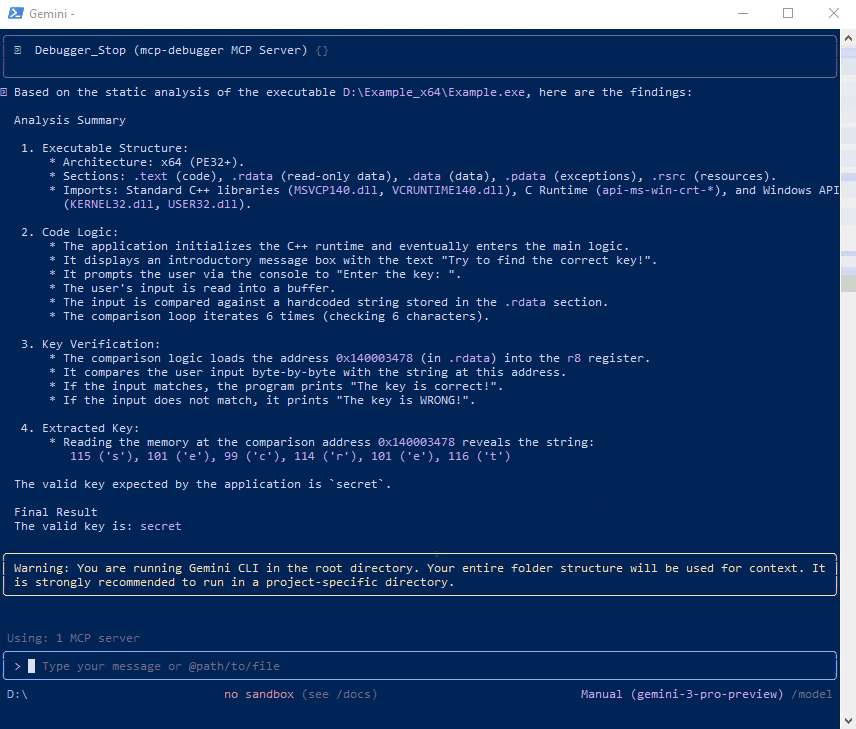 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
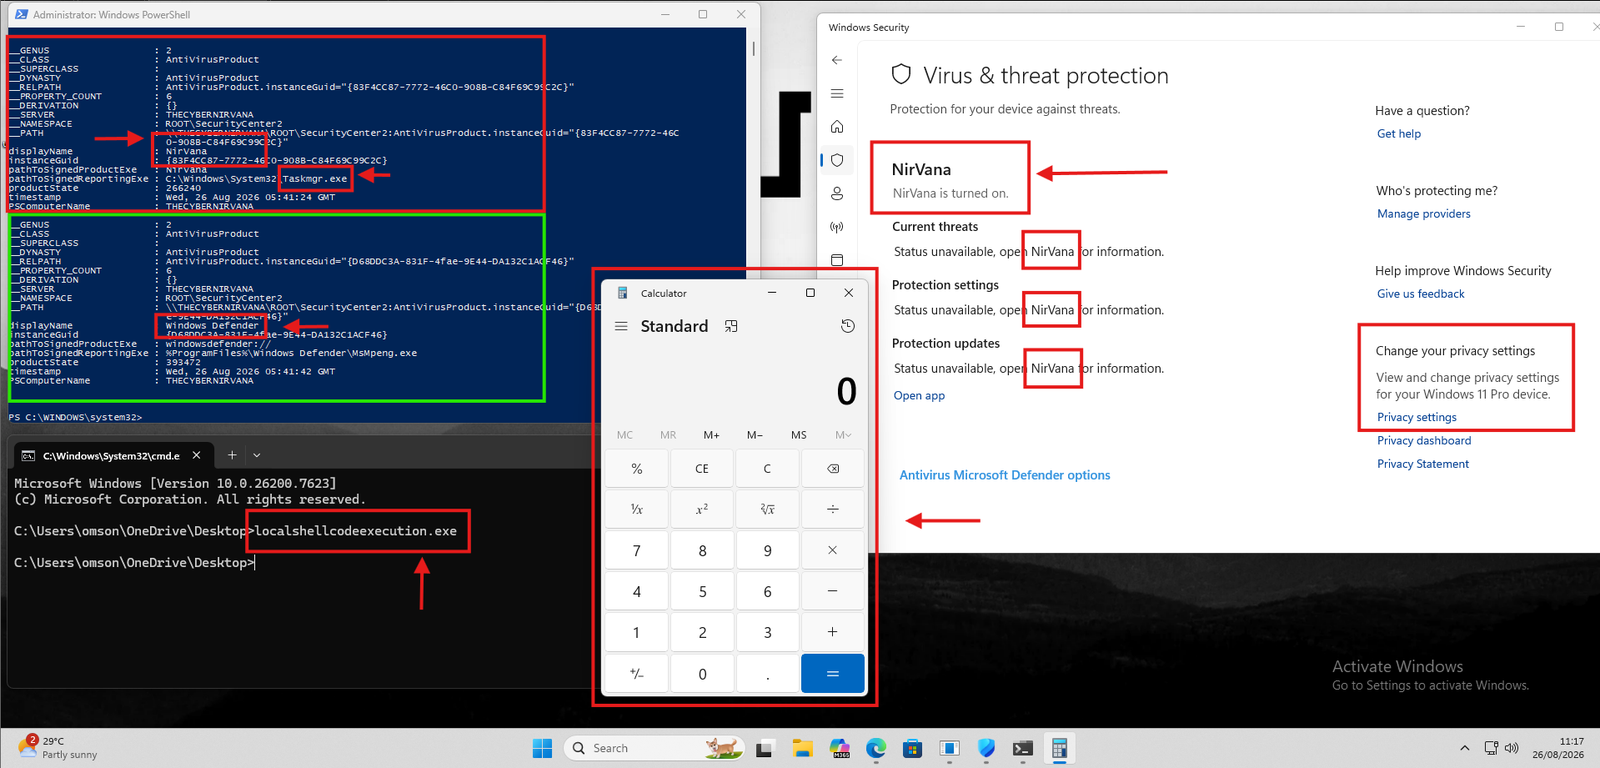 nirvanaon/own-defender
Research project reverse-engineering Windows Security Center COM interfaces to trace AV registration through ATL, vtable, WSCAPI, and RPC, with…
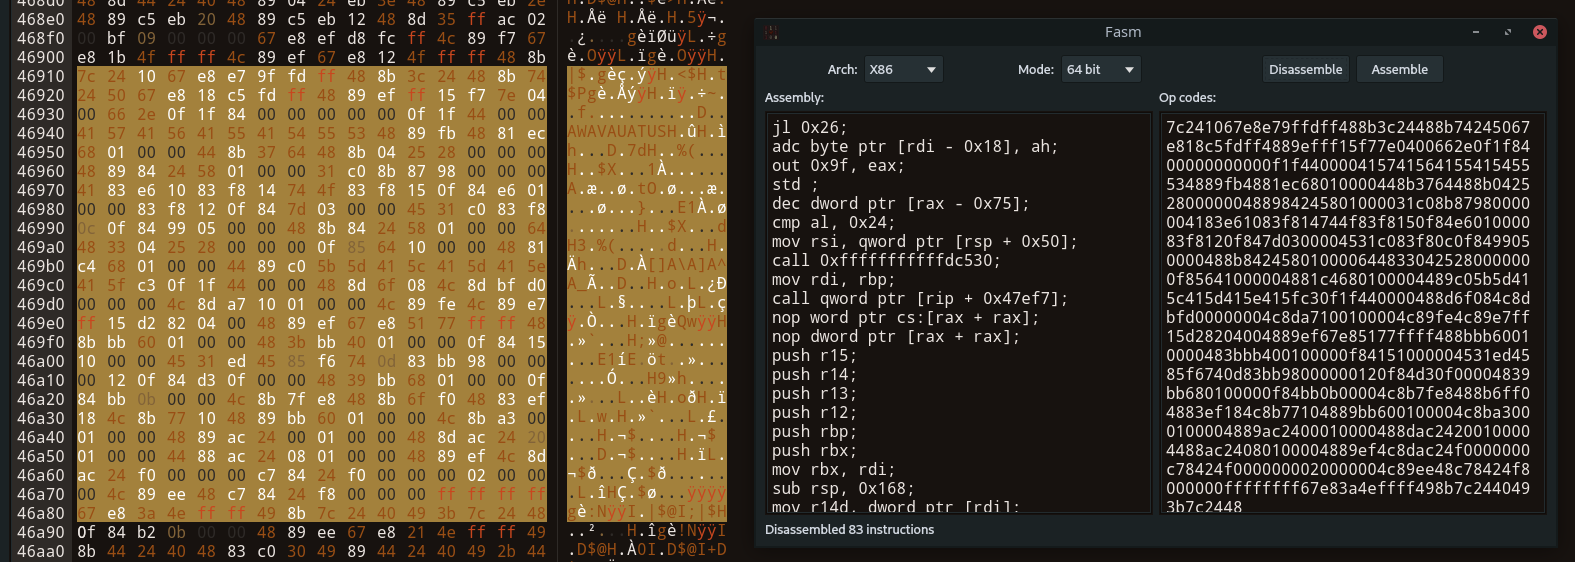 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
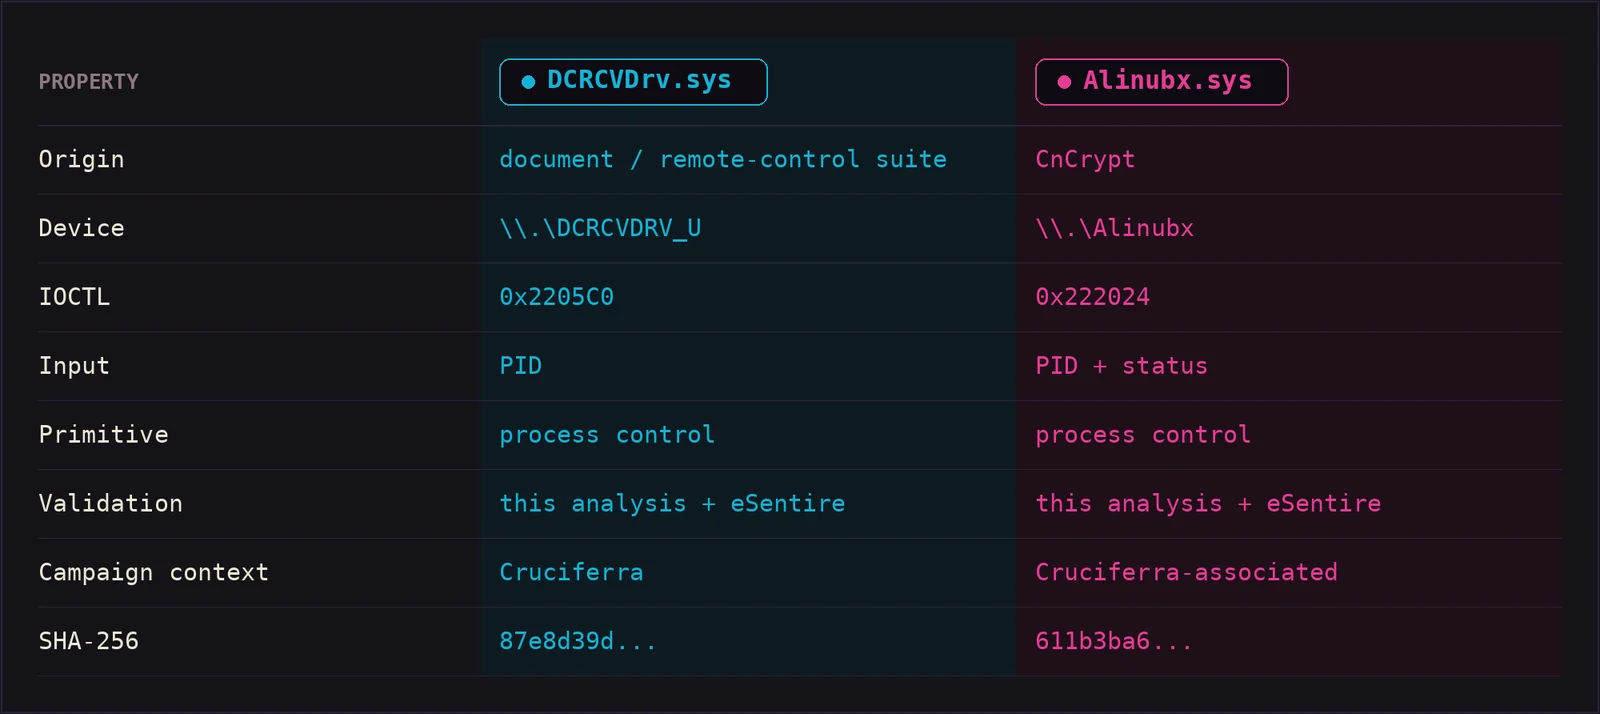 deathshotxd/0xcr0sscrush
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
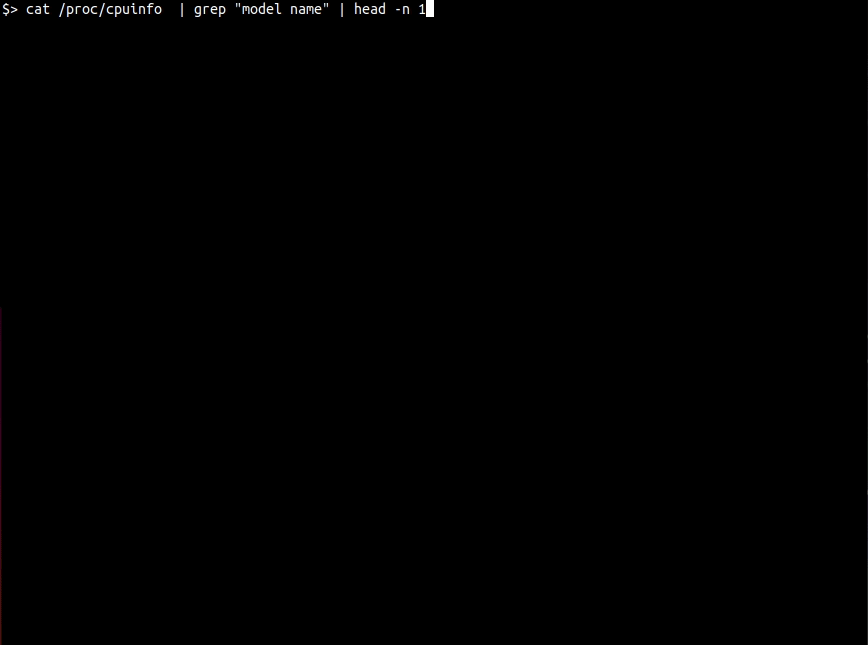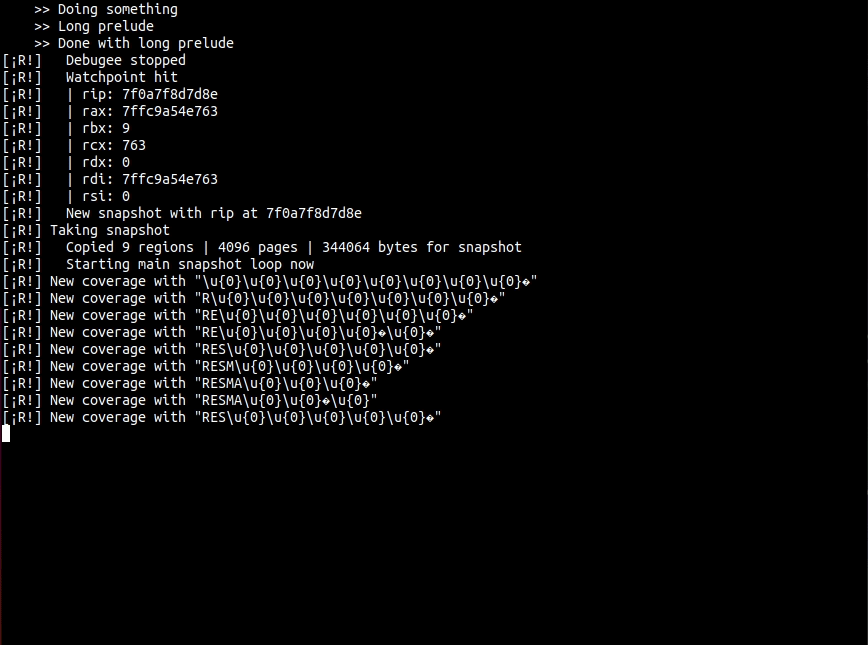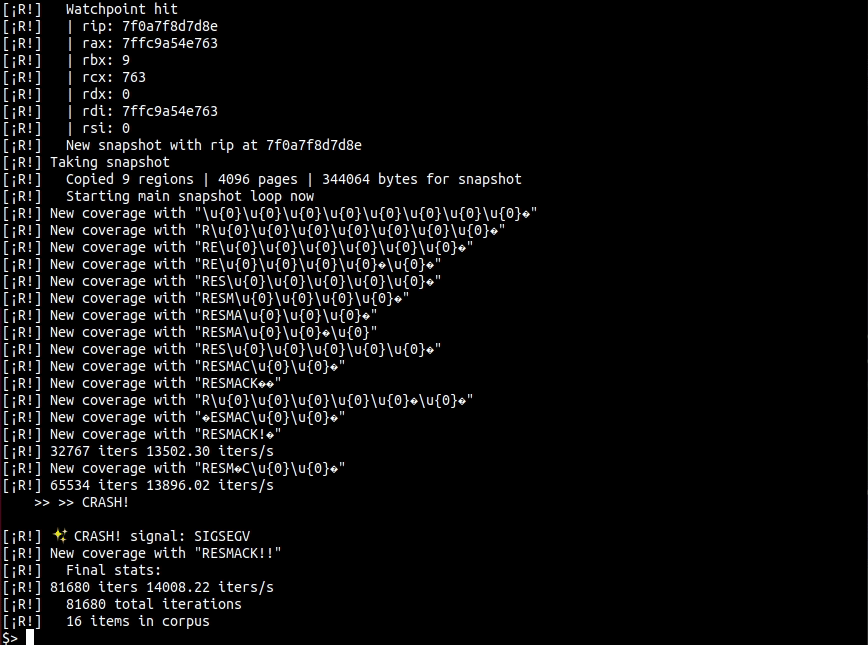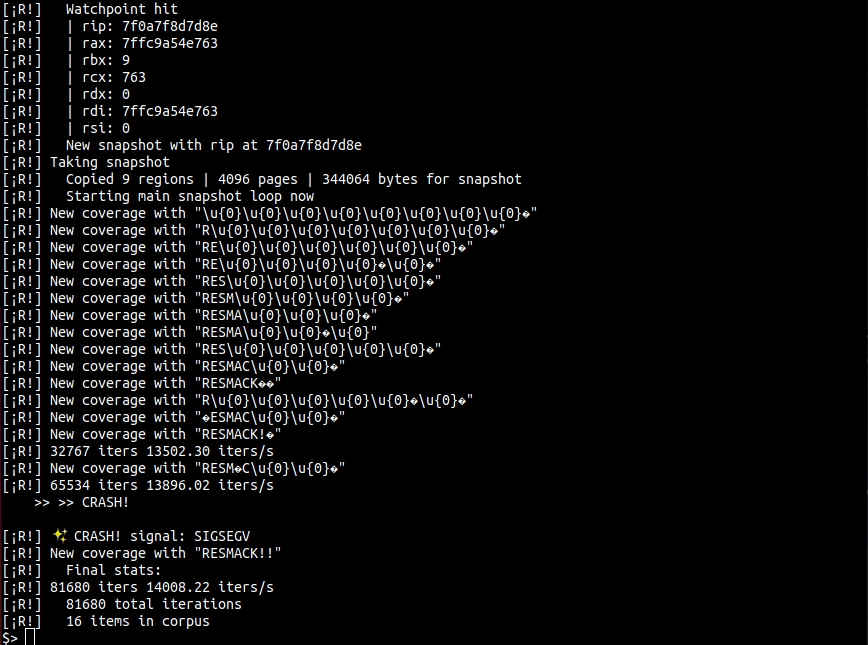
 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
 pxb1988/dex2jar
Tools to work with android .dex and java .class files
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 0xxa/google-poc
This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…