
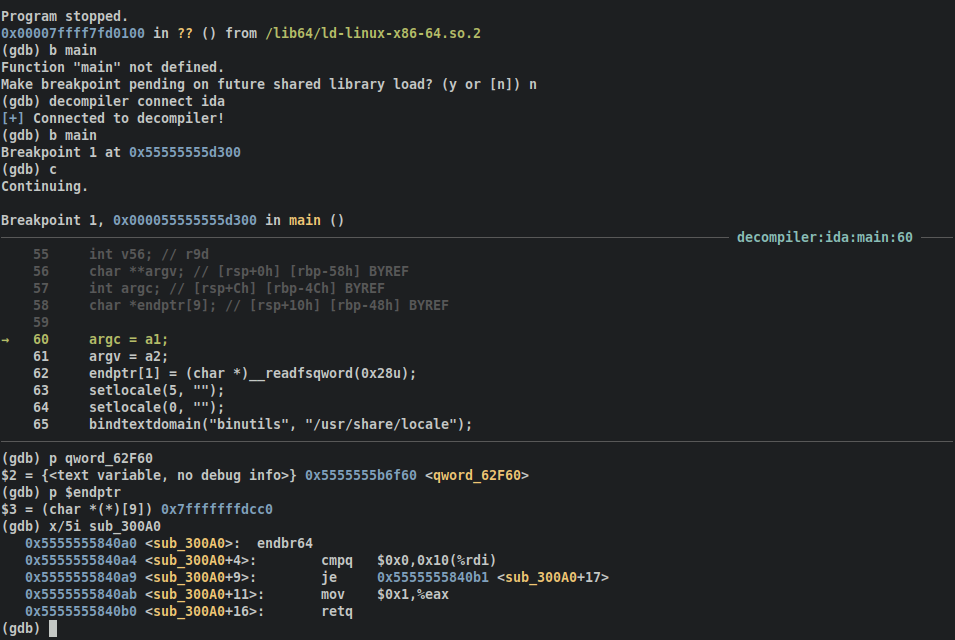
decomp2dbg
 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
binary-analysisbinary-exploitationdebuggers+3
82810 days ago
mahaloz/decomp2dbgA plugin to introduce interactive symbols into your debugger from your decompiler
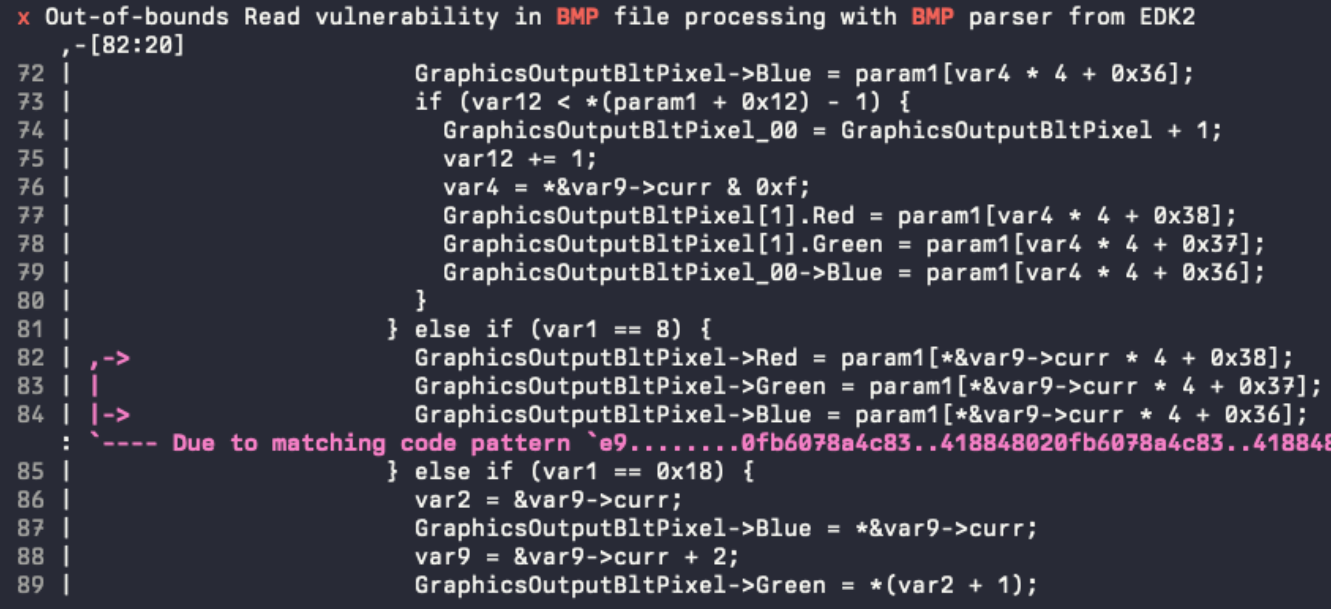 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
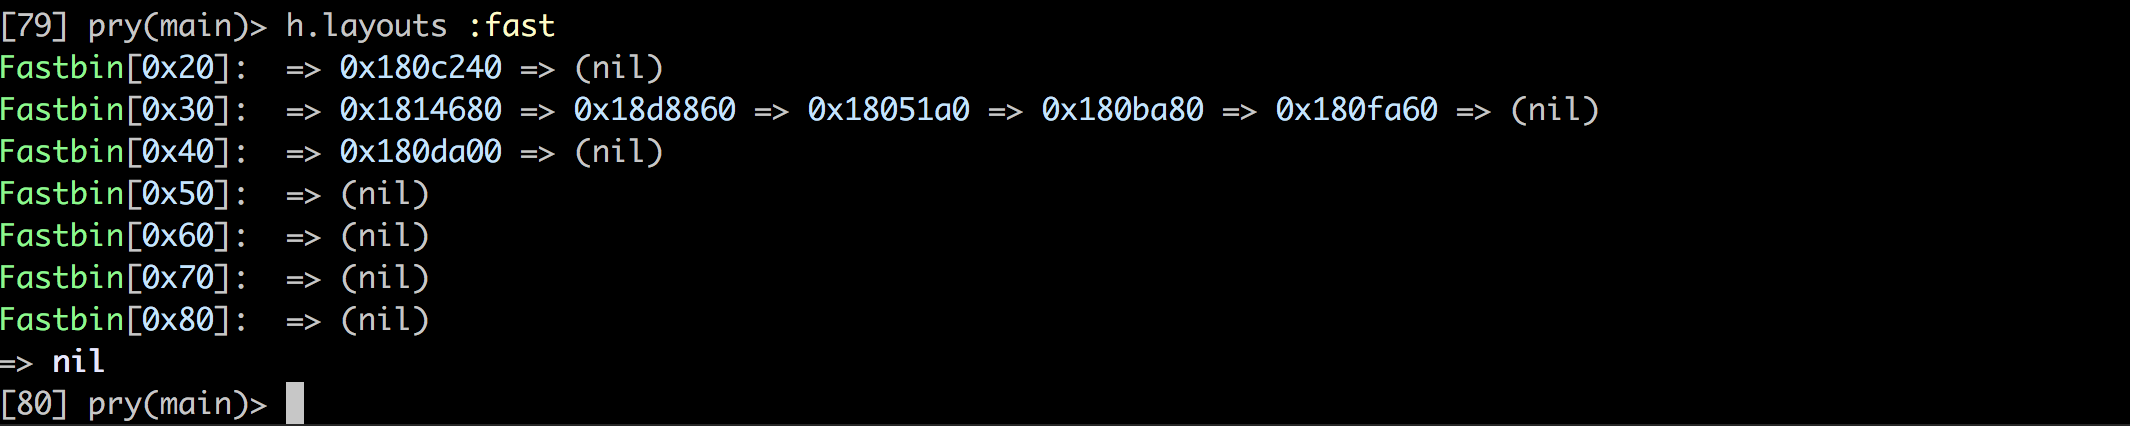 david942j/heapinfo
An interactive memory info for pwning / exploiting
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
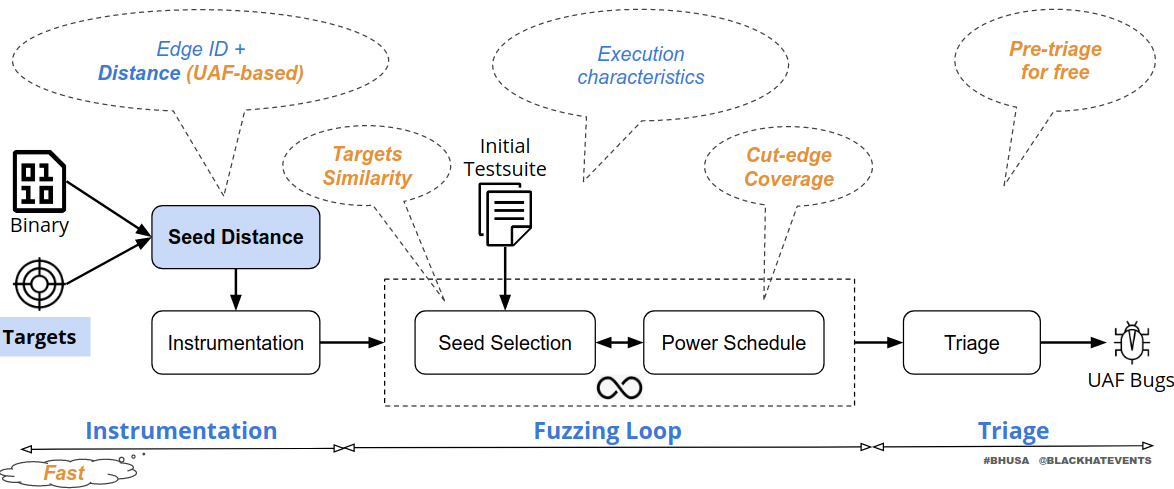 strongcourage/uafuzz
Binary-level directed fuzzer specialized in detecting Use-After-Free vulnerabilities via ordering-aware input metrics and static analysis, enabling…
 rocky/python-decompile3
Python decompiler for 3.7-3.8 Stripped down from uncompyle6 so we can refactor and start to fix up some long-standing problems
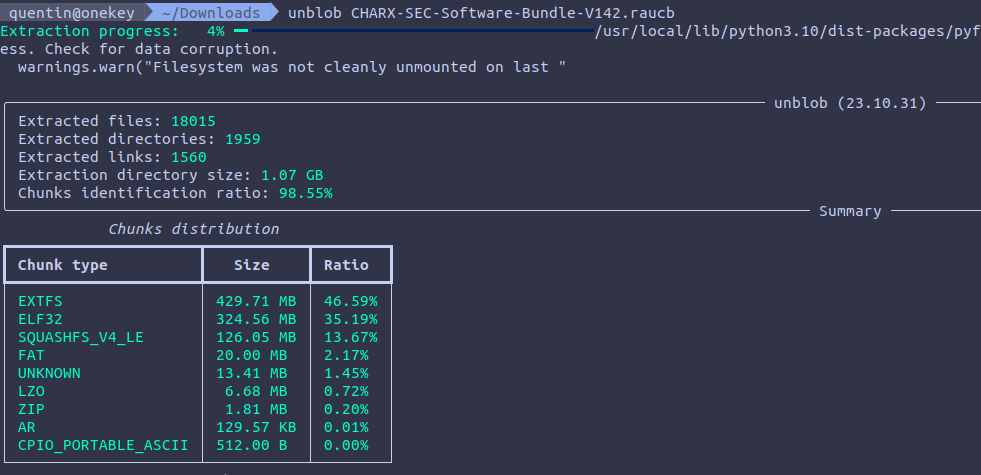 onekey-sec/firmware-workshop
In this workshop session, we will extract firmware from an EV charger, dig into the firmware, and eventually emulate it so we can interact with the…
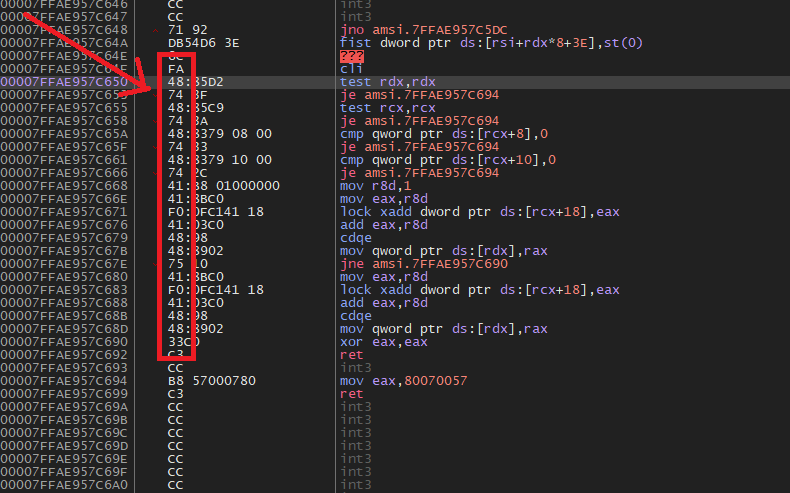 zeromemoryex/amsi-killer
Lifetime AMSI bypass
 ypl6/heaplens
CMPT733 Cybersecurity Lab II Project: GDB plugin for heap exploits inspired by CVE-2021-3156
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 httpvoid/cve-reverse
Curated list of CVEs that have been reverse-engineered and analyzed, serving as a resource for vulnerability research, exploitation understanding,…
 nccgroup/asafw
Set of scripts to deal with Cisco ASA firmware [pack/unpack etc.]
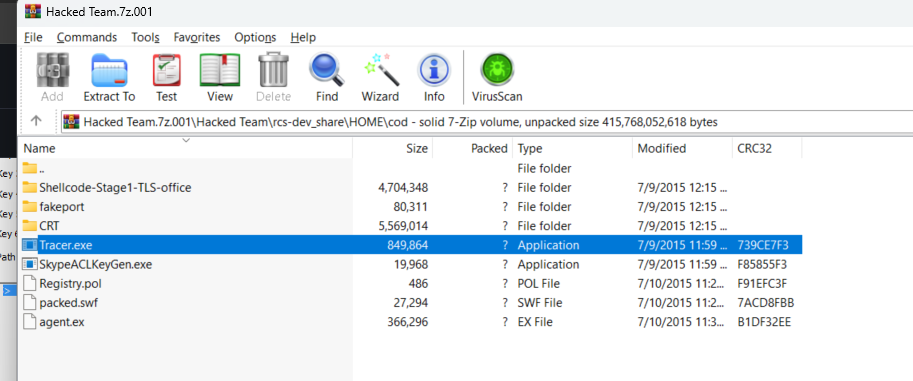 spiralbl0ck/skypeaclkeygen.exe-analysis-for-hacking-team
SkypeACLKeyGen.exe analysis for hacking team
 synacktiv/mojarragadget
Proof-of-concept exploit for a Java gadget chain in the Mojarra library, demonstrating deserialization vulnerability exploitation for versions 2.3…
 cdacesec/cve-2023-33802
Proof-of-concept for CVE-2023-33802, a denial-of-service vulnerability in SumatraPDF 3.4.6 32-bit, triggered by opening two large text files, causing…
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 lucadibello/tmux-fuzzing
Enhanced fuzzing for tmux using OSS-Fuzz. Includes custom `cmd-fuzzer` and `argument-fuzzer` harnesses for improved code coverage and a PoC for…