
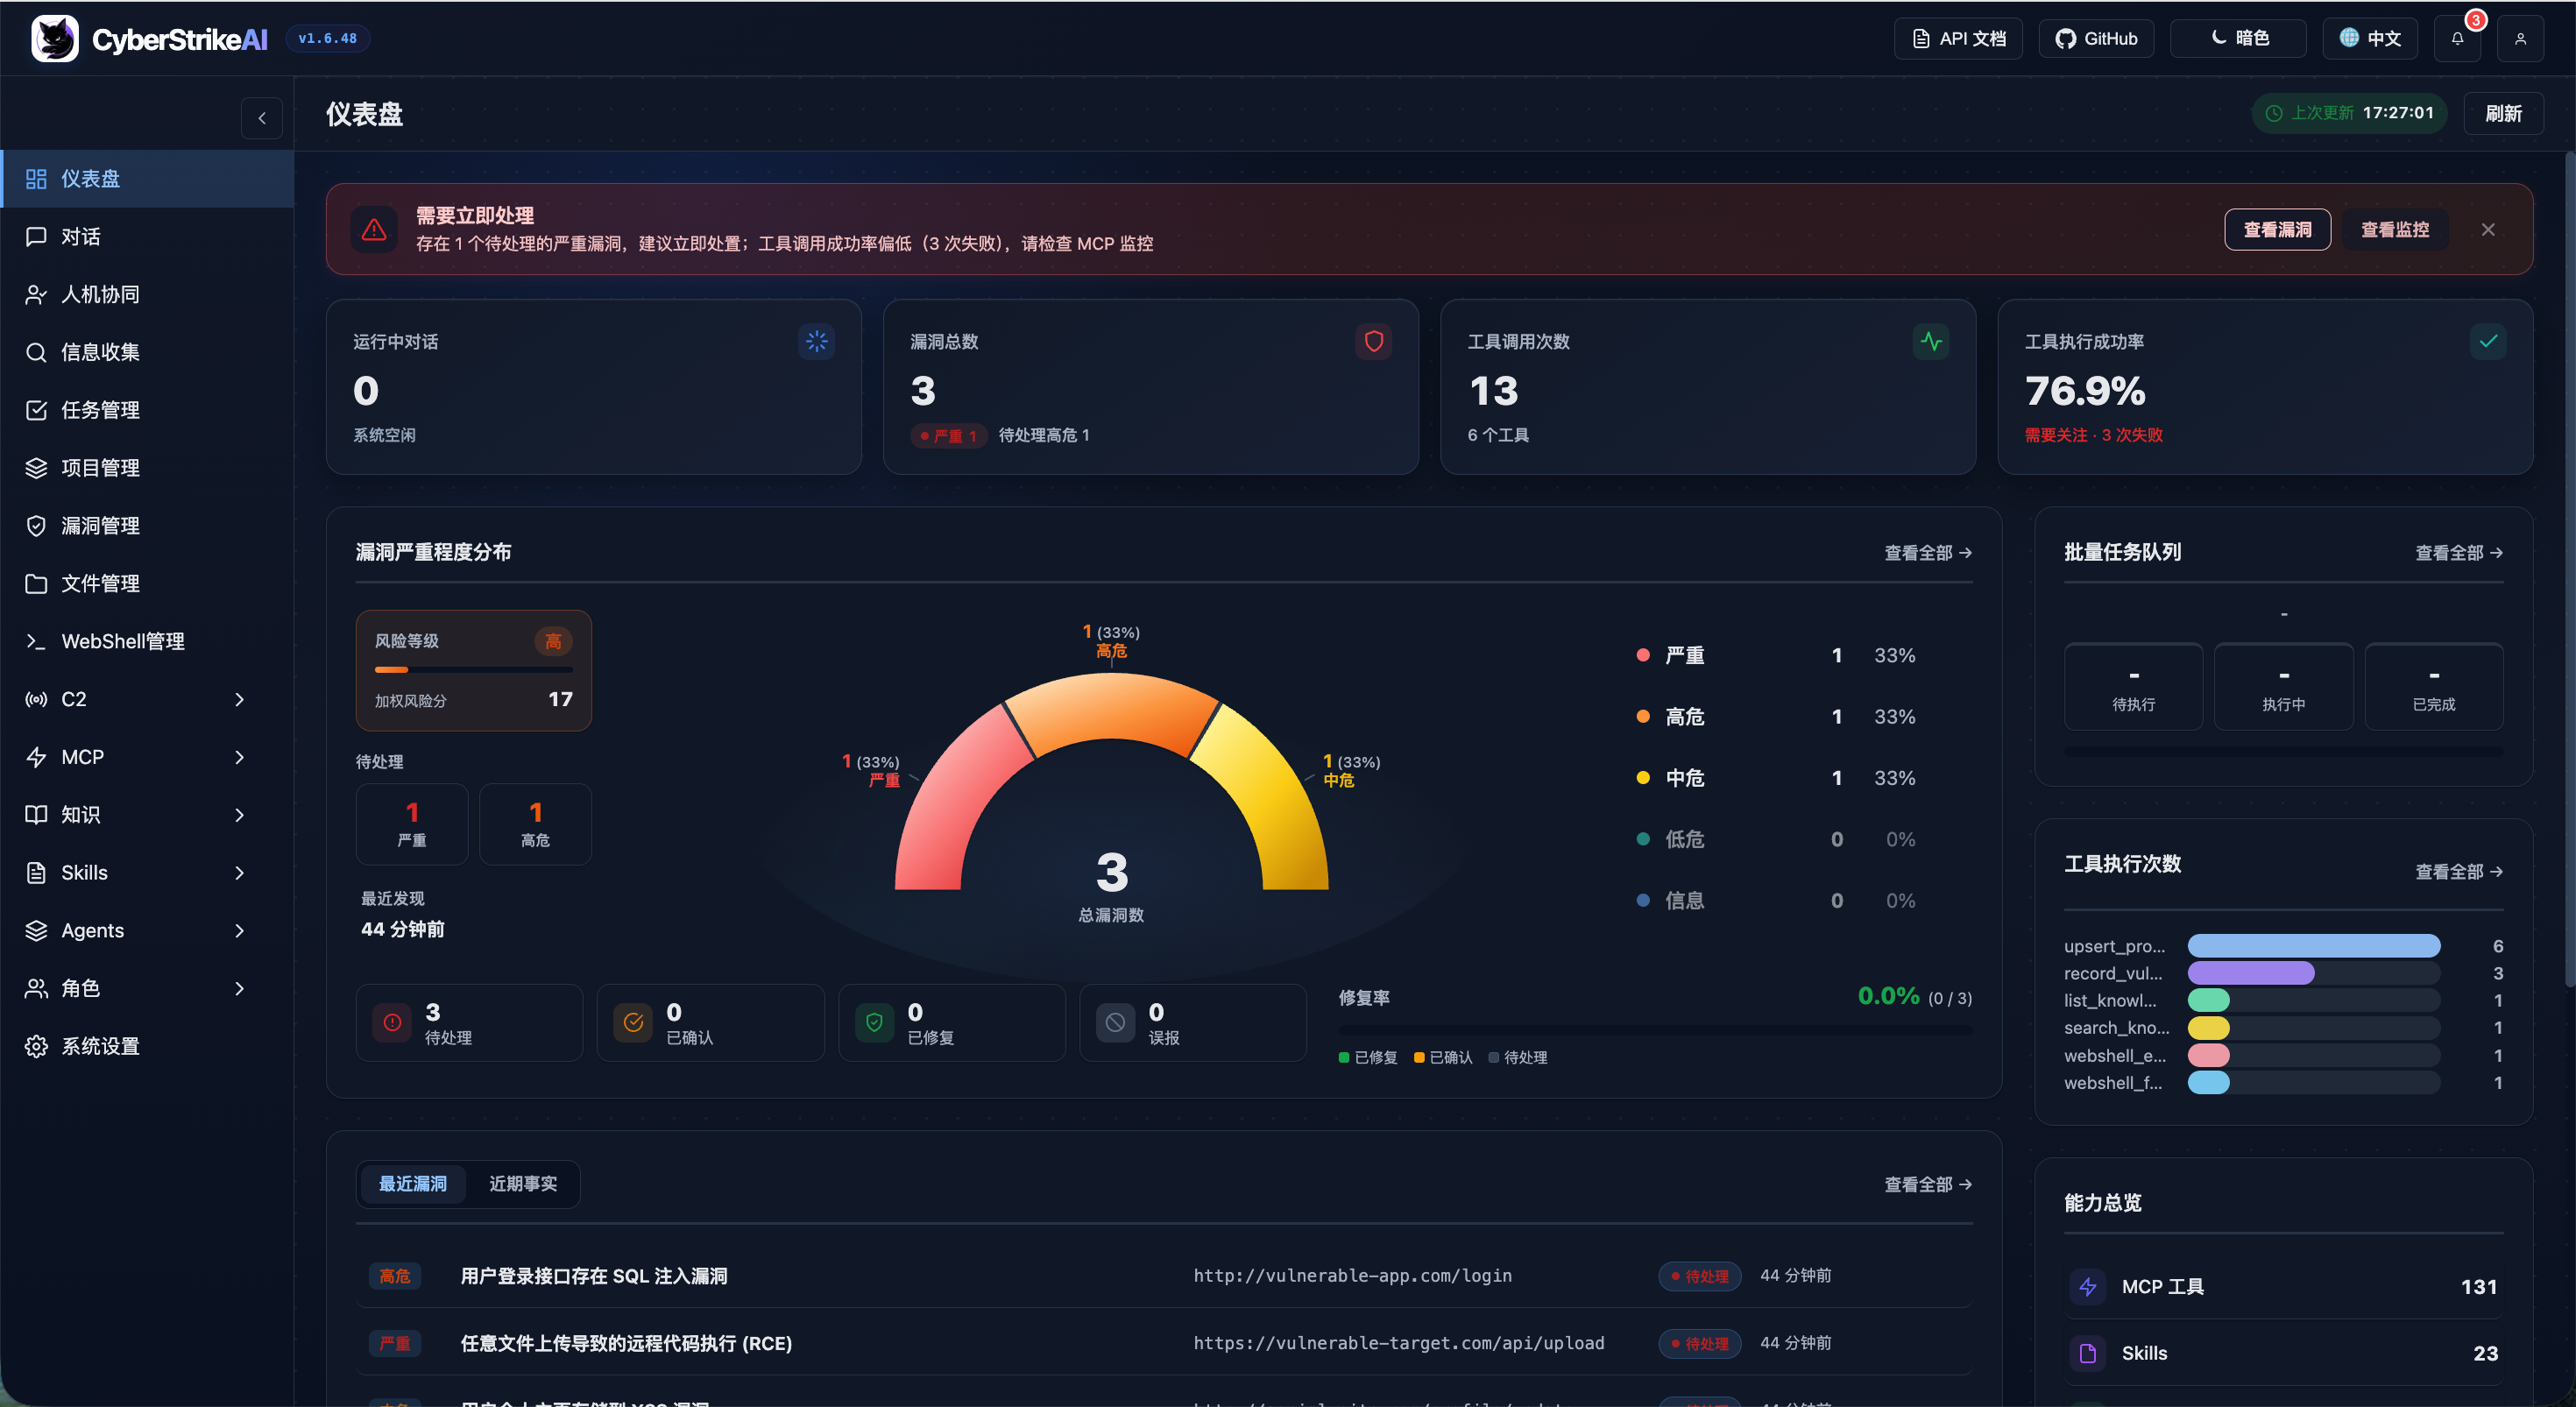
CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
7.0k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 upx/upx
UPX - the Ultimate Packer for eXecutables
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 whatswrongandwhy/ptrace
Linux ptrace-based process tracing and debugging utility for inspecting system calls, memory, and program execution flow.
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…

 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
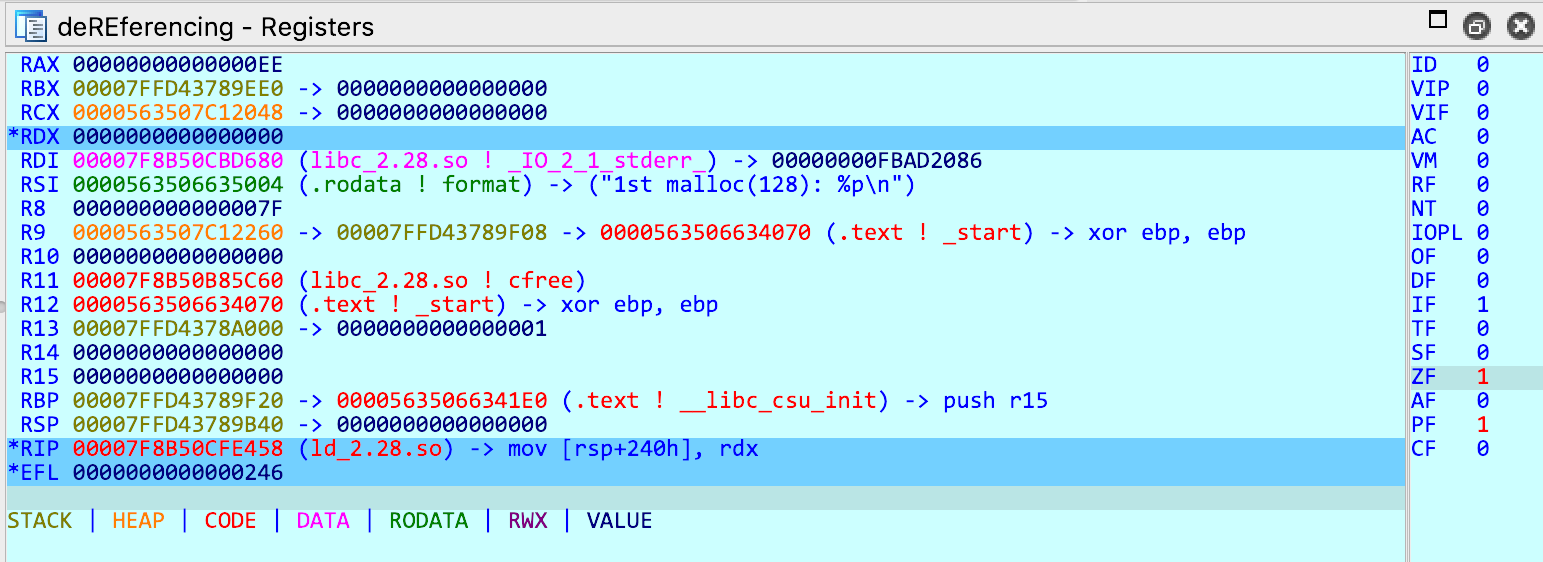 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
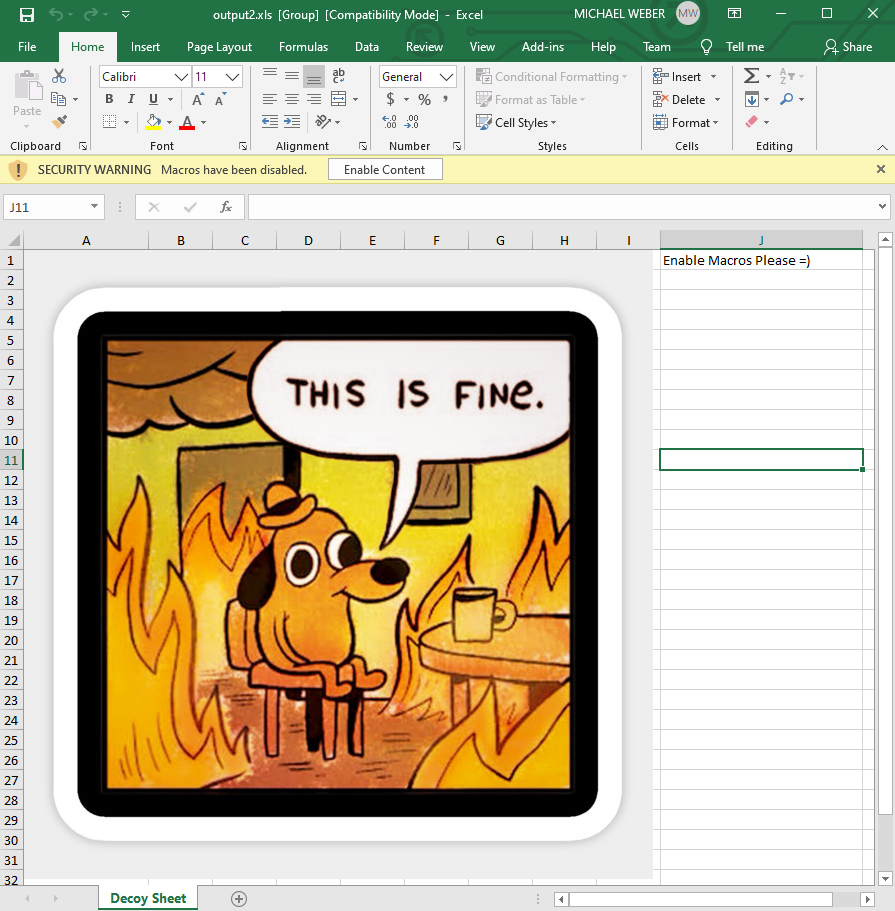 michaelweber/macrome
Excel Macro Document Reader/Writer for Red Teamers & Analysts
 0xax/linux-insides
A book-in-progress about the Linux kernel and its insides.
 m0n1x90/elfxtract
Automated ELF binary analysis tool for CTF/PWN challenges. Extracts security mitigations, ROP gadgets, PLT/GOT tables, and decompiles ASM to C using…
 ggfuchsi-oss/spectrida-reverse_engineering_stack
Parallel IDA Pro binary analysis with AI-powered function naming, Neo4j knowledge graph, and phantomrt emulation/hooking/fuzzing engine for automated…
 paolomonti42/salt
SALT - SLUB ALlocator Tracer for the Linux kernel
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…