Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
60 results
nuitka-static-unpacker preview

nuitka-static-unpacker

GitHubdimareverse/nuitka-static-unpacker

Static-first research tool for unpacking Nuitka-compiled binaries: extracts constants, modules, recovers .pyc files, and generates analysis reports.

binary-analysisdata-recoveryforensics+3
136

2 months ago
IPA preview

IPA

GitHubseekbytes/ipa

GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…

binary-analysisdefensive-toolsdigital-forensics+6
8832 years ago
kernagent preview

kernagent

GitHubkarib0u/kernagent

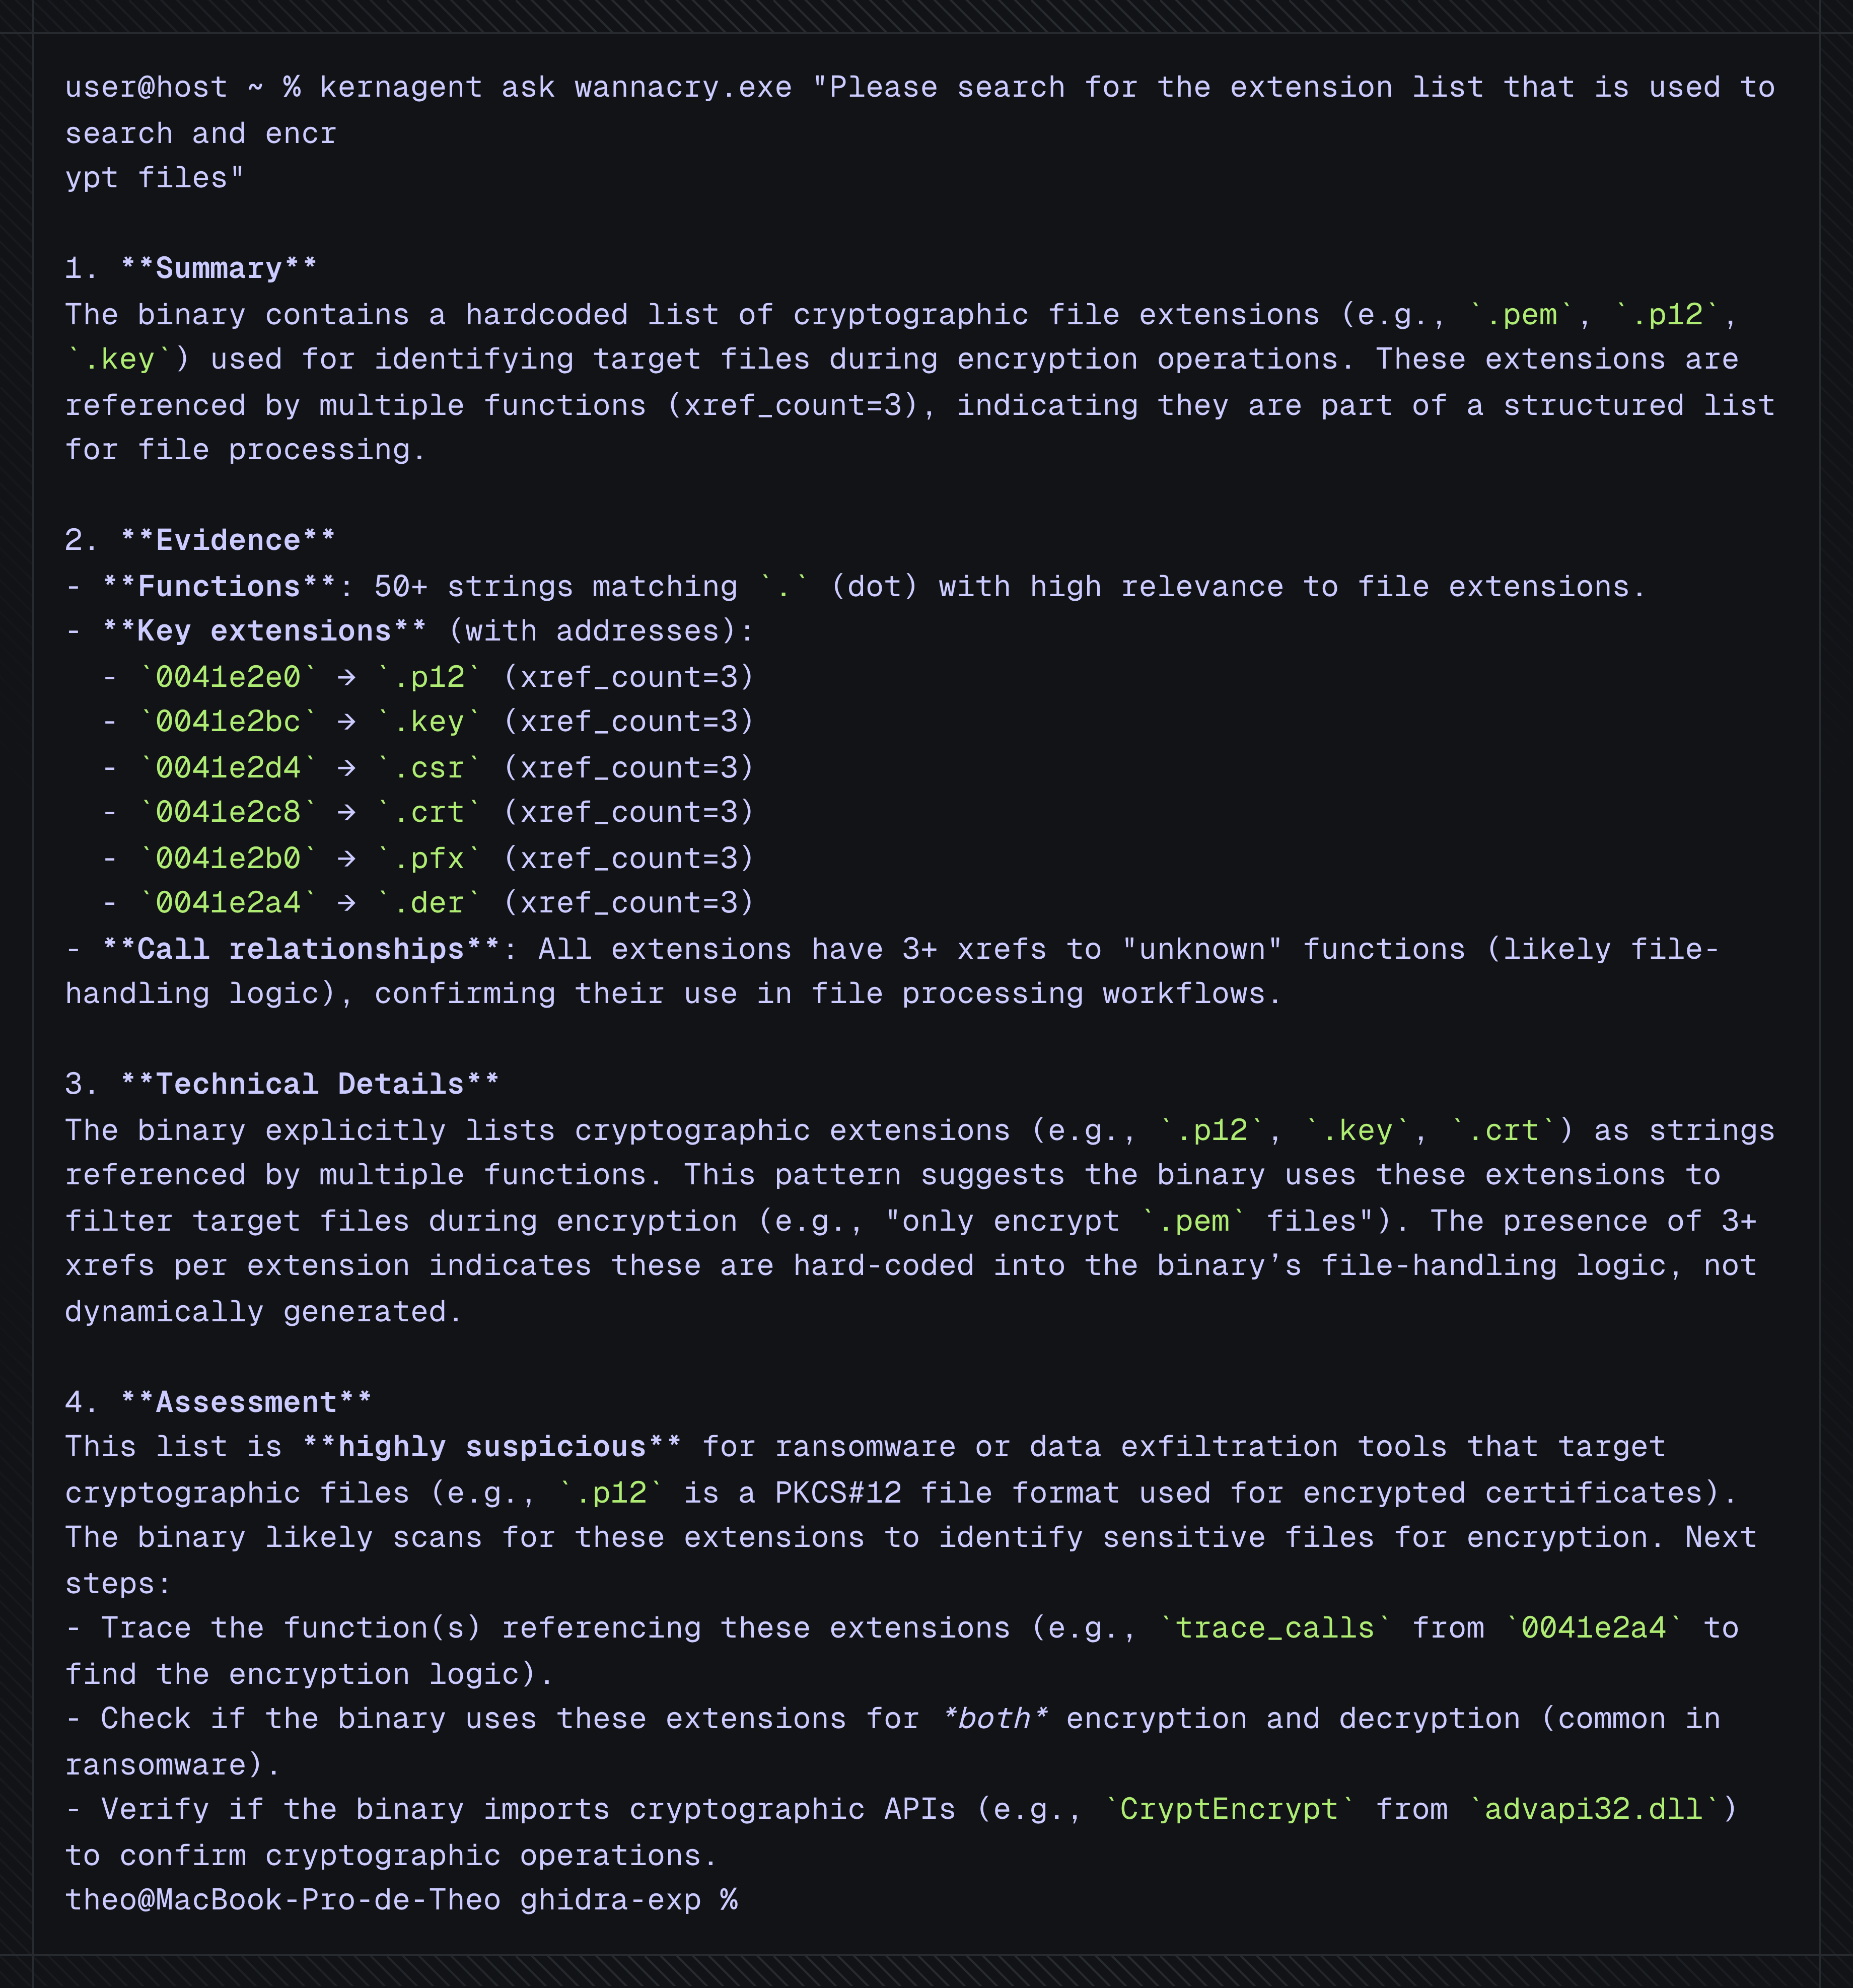
Headless AI agent for deterministic reverse engineering.

ai-assisted-reversingbinary-analysisforensics+4
10311 months ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).

binary-analysisforensicsmalware-analysis+2
3.9k4 months ago
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

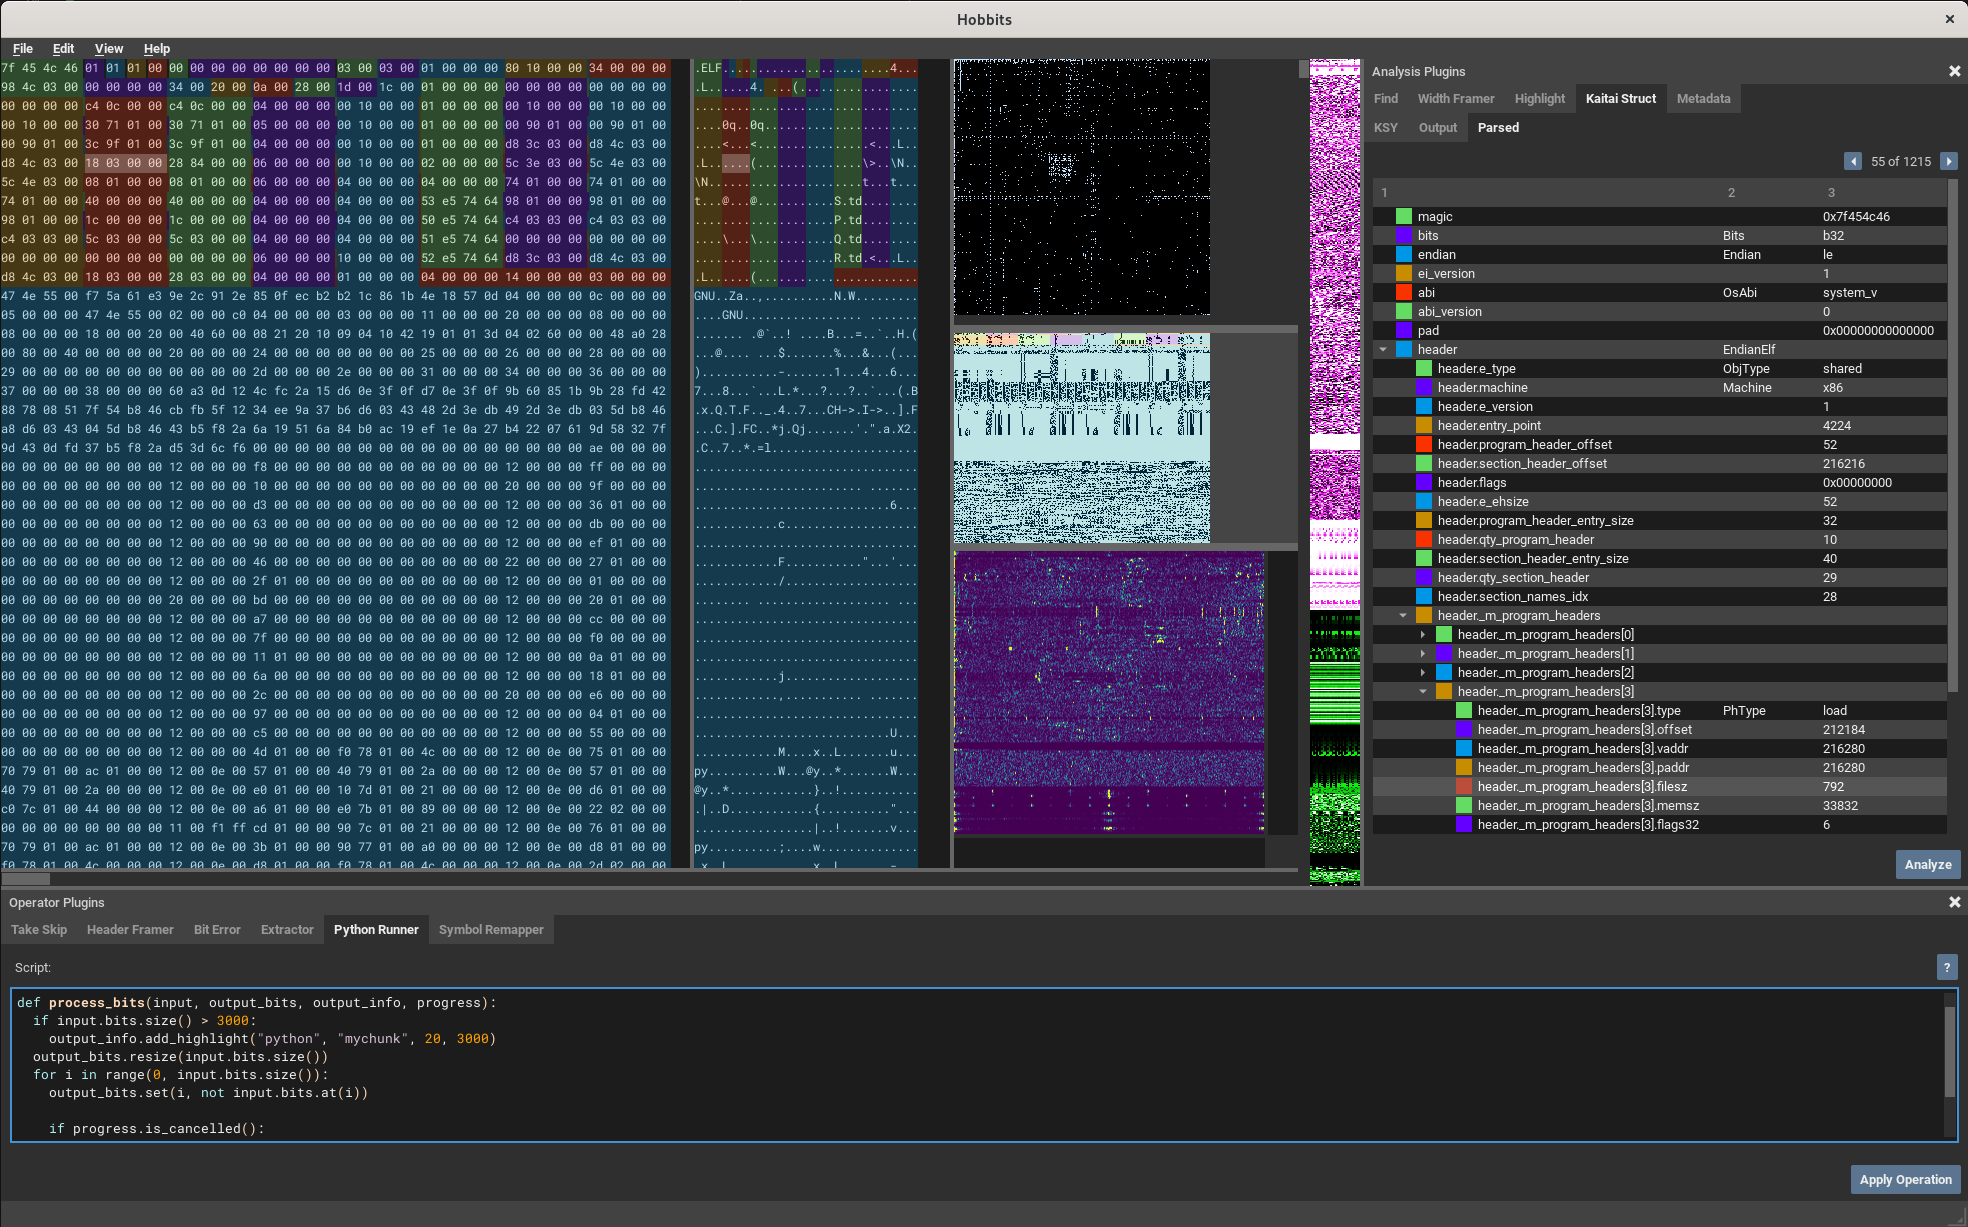
A multi-platform GUI for bit-based analysis, processing, and visualization

binary-analysisdata-recoveryforensics+1
7551 year ago
hacksguard preview

hacksguard

GitHubrhacknarok/hacksguard

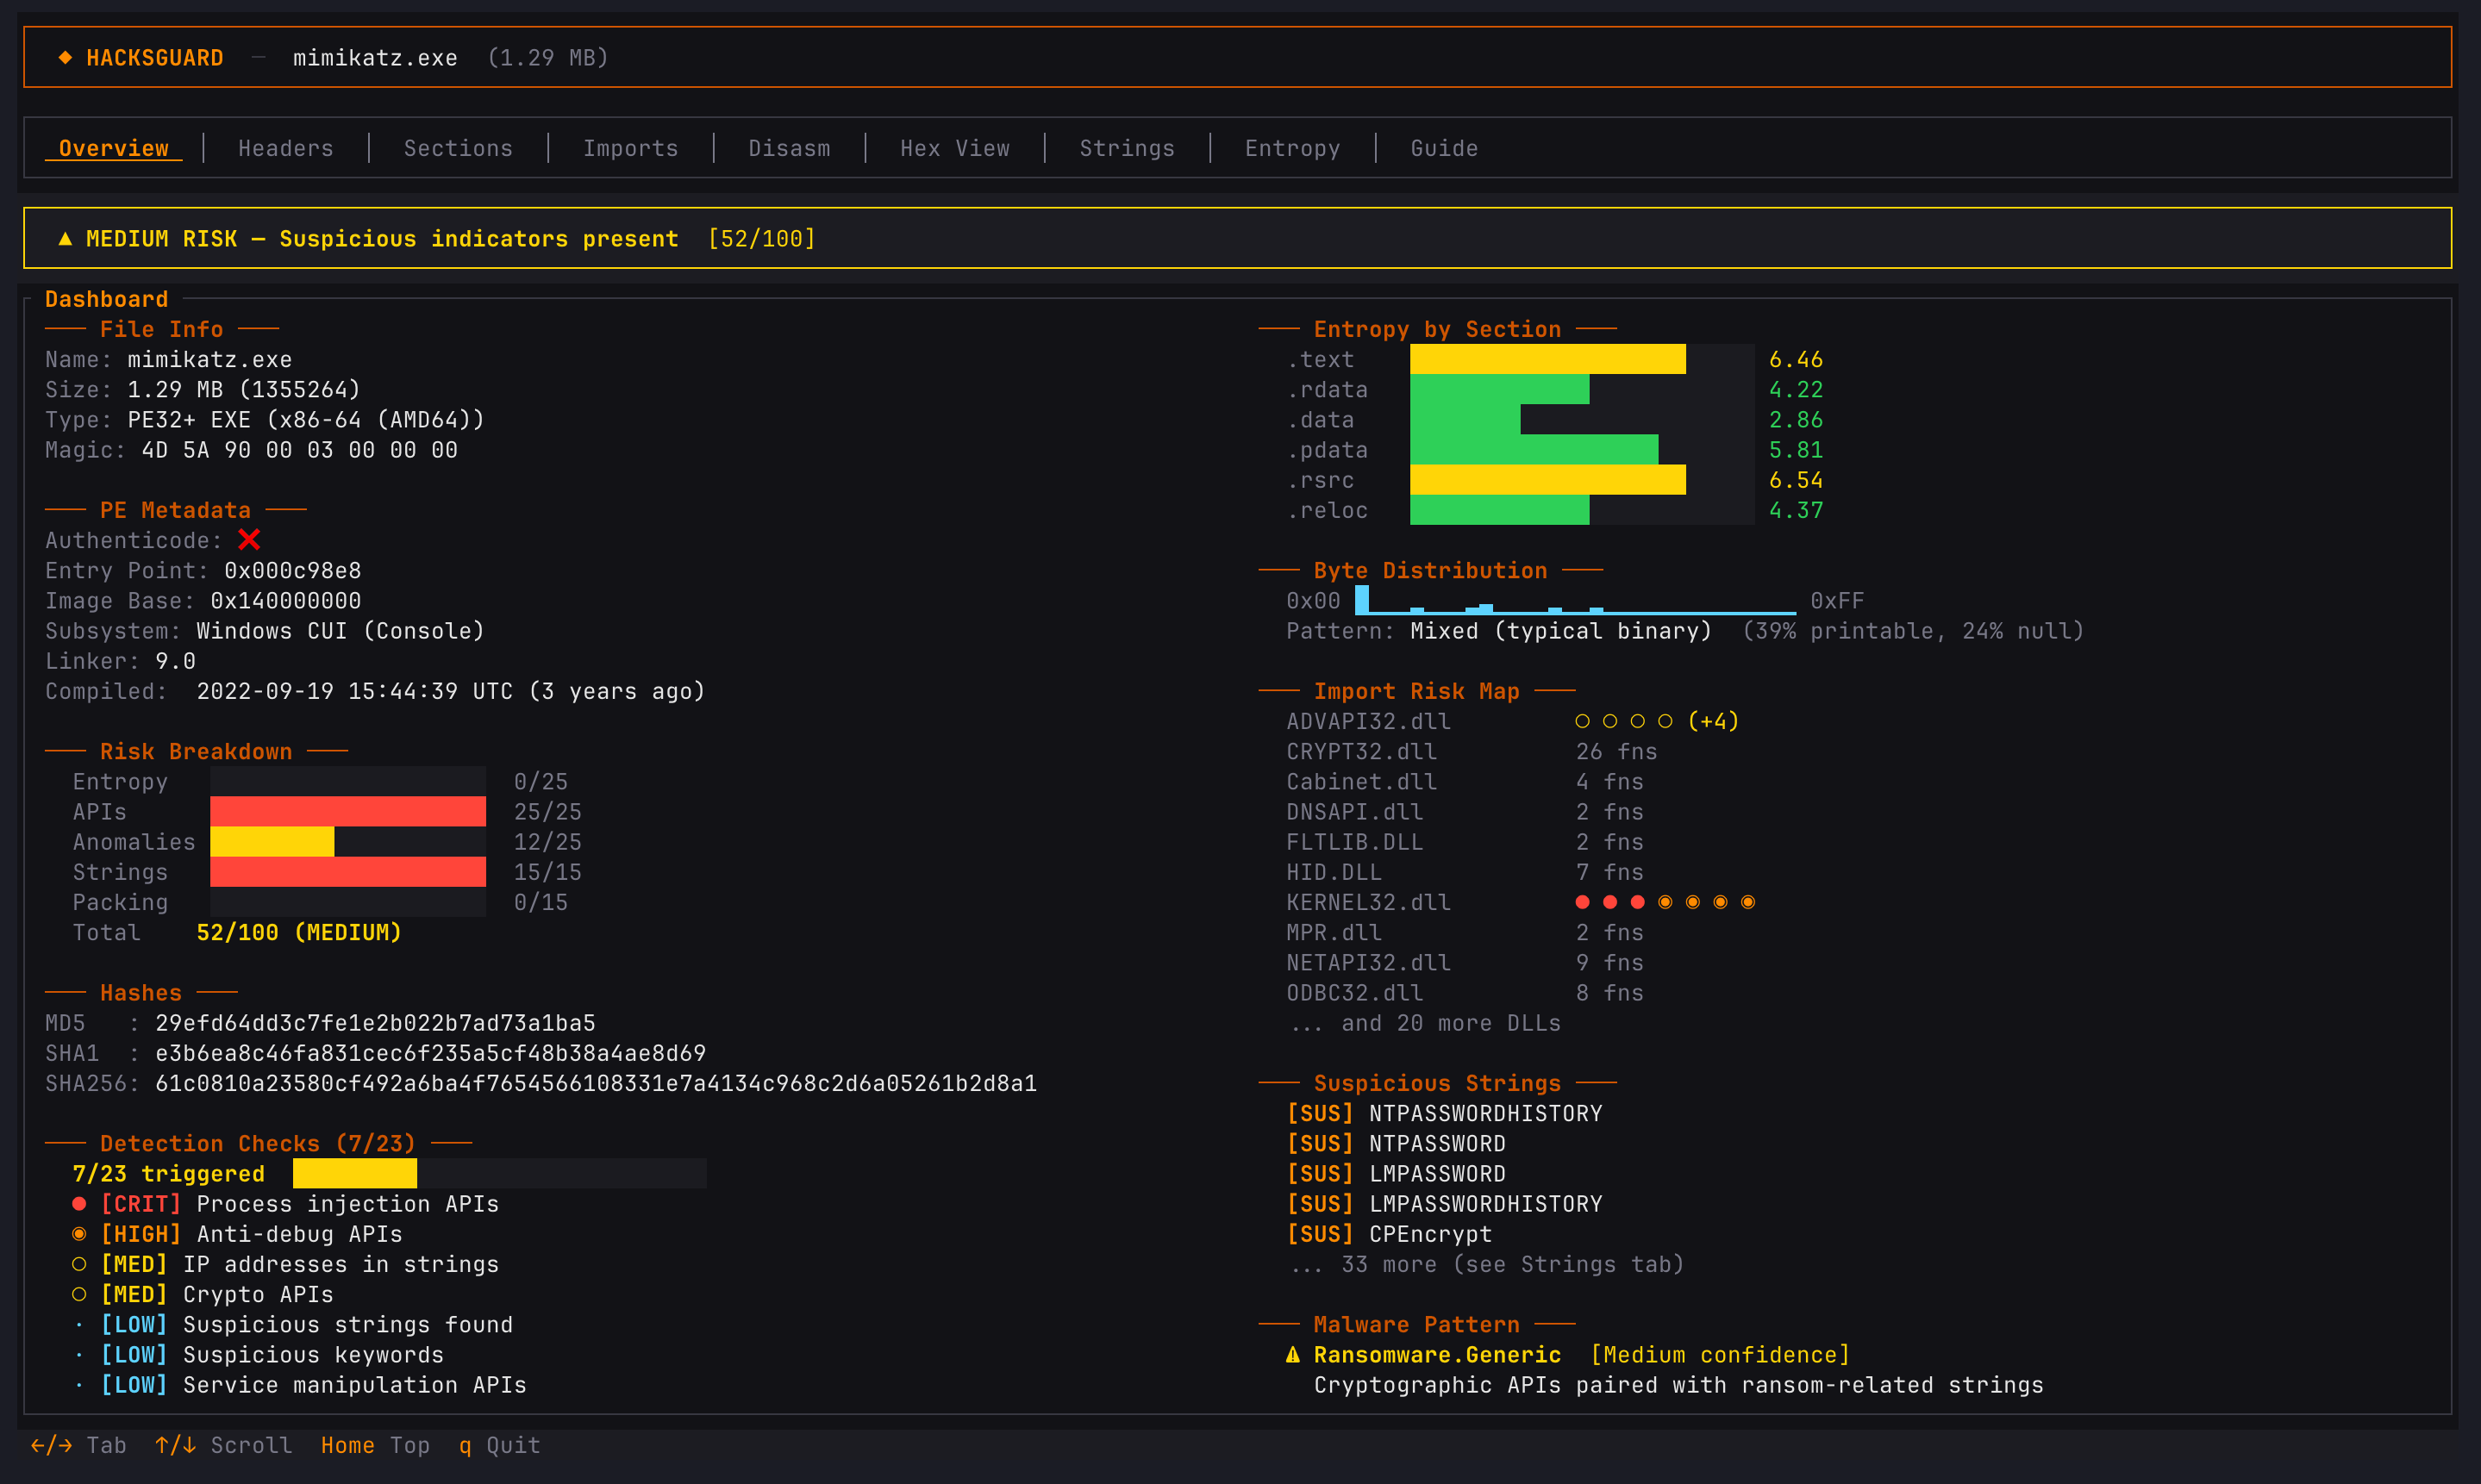
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.

binary-analysisforensicsmalware-analysis+2
2151 month ago
NoMoreXOR preview

NoMoreXOR

GitHubhiddenillusion/nomorexor

Tool to help guess a files 256 byte XOR key by using frequency analysis

binary-analysiscryptographyforensics+3
908 years ago
pefile preview

pefile

GitHuberocarrera/pefile

pefile is a Python module to read and work with PE (Portable Executable) files

binary-analysisforensicsmalware-analysis+3
2.1k10 days ago
machscope preview

machscope

GitHubm10ust/machscope

macOS IPC, launchd, Mach-O, and trust relationship explorer — zero-dependency terminal-native forensic tool

binary-analysisdigital-forensicsforensics+7
12 months ago
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…

binary-analysisforensicsincident-response+1
1702 years ago
pe-signgen preview

pe-signgen

GitHubforentfraps/pe-signgen

Universal signature generation for any system function from all Windows Builds using Winbindex

binary-analysisforensicsmalware-analysis+3
1810 months ago
dissect.cobaltstrike preview

dissect.cobaltstrike

GitHubfox-it/dissect.cobaltstrike

Python library for dissecting and parsing Cobalt Strike related data such as Beacon payloads and Malleable C2 Profiles

binary-analysiscommand-and-controldigital-forensics+4
2126 days ago
iocx preview

iocx

GitHubiocx-dev/iocx

An extensible, deterministic static‑analysis engine that extracts high‑signal IOCs from PE binaries and text, built for SOC automation and modern…

binary-analysisdevsecopsforensics+6
281 month ago
cve-2021-33909 preview

cve-2021-33909

GitHubbaerwolf/cve-2021-33909

This module fixes an issue in the kernels filesystem layer (CVE-2021-33909) by kprobe-replacing vulnerable functions during runtime

binary-analysisexploitationincident-response+1
65 years ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3922 months ago
entropystrip preview

entropystrip

GitHubdwexi/entropystrip

Algorithmic PE de-obfuscator, Shannon entropy radar, and incident triage engine

binary-analysisdefensive-toolsdigital-forensics+6
86 days ago
certgraveyard_yara preview

certgraveyard_yara

GitHubtjnel/certgraveyard_yara

Automated YARA rule generation from the Cert Central compromised certificate database.

binary-analysisdefensive-toolsforensics+2
154 days ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.

binary-analysisforensicshash-analysis+3
1915 years ago
Previous1234Next