

TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
192
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 google/bindiff
Quickly find differences and similarities in disassembled code
 helixo32/crimsonedr
Simulate the behavior of AV/EDR for malware development training.
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
 joxeankoret/diaphora
Diaphora, the most advanced Free and Open Source program diffing tool.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
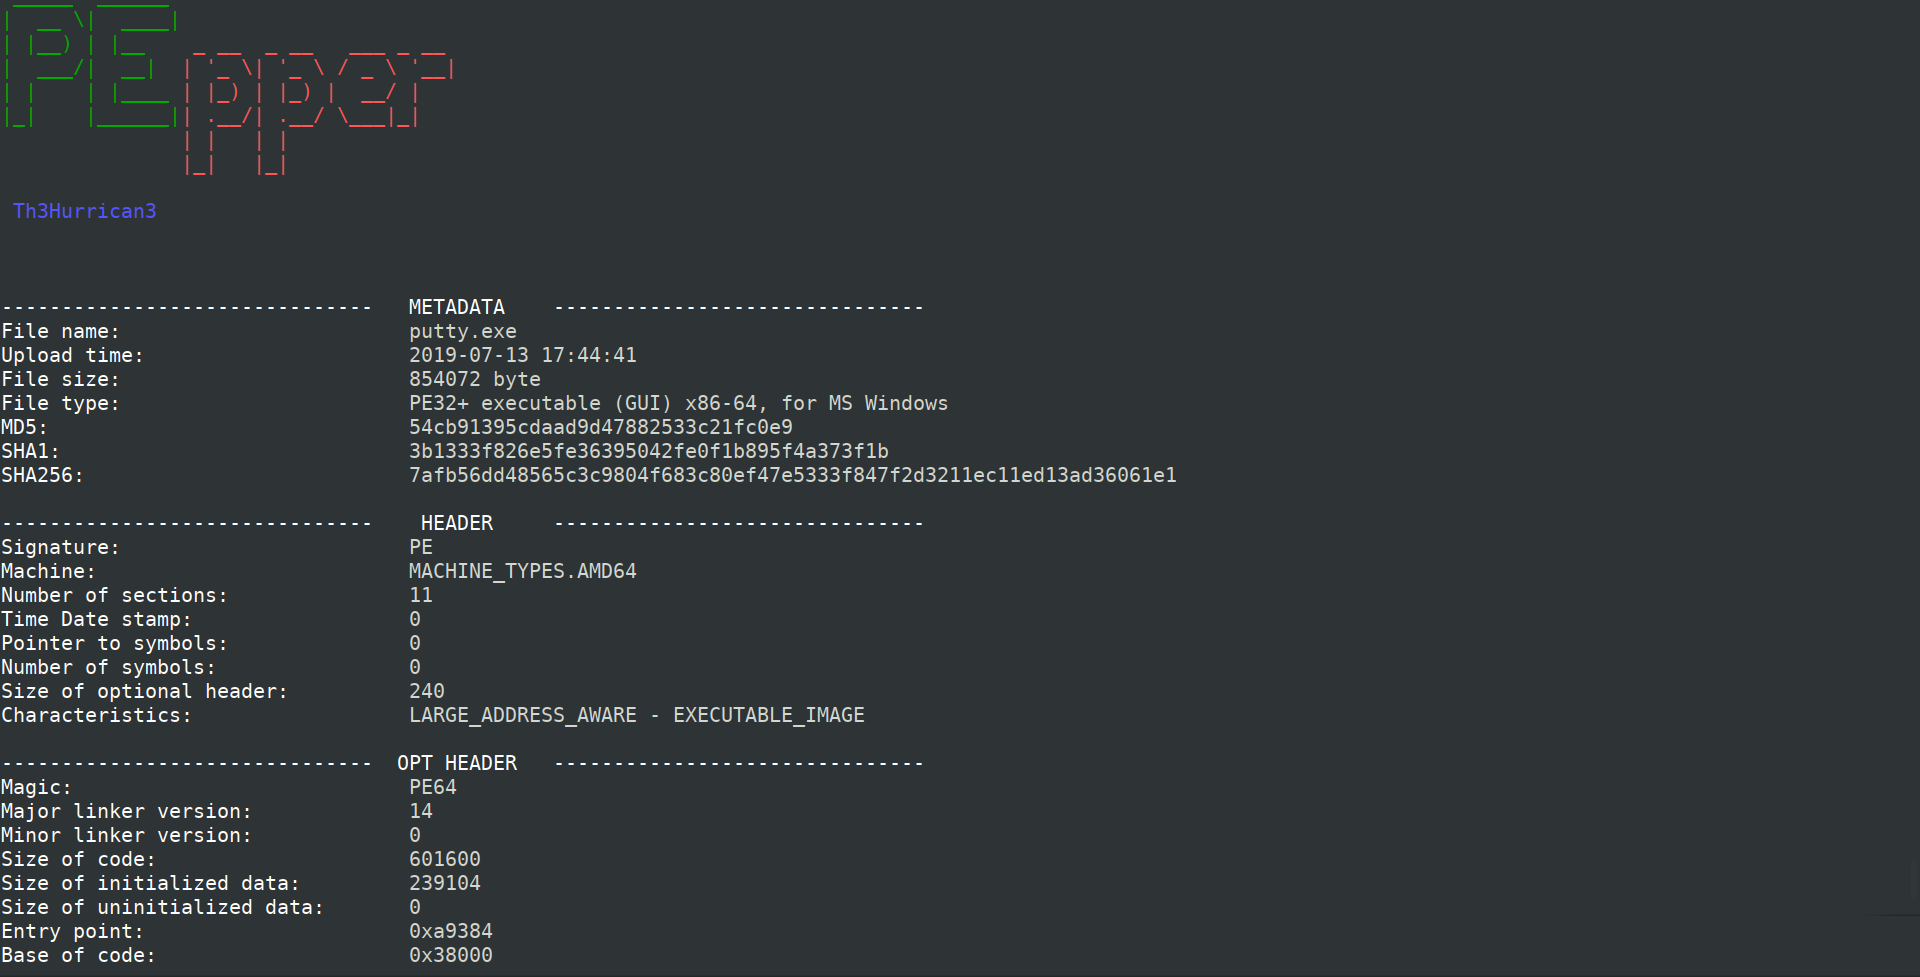 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable
 nirizr/rematch
REmatch, a complete binary diffing framework that is free and strives to be open source and community driven.
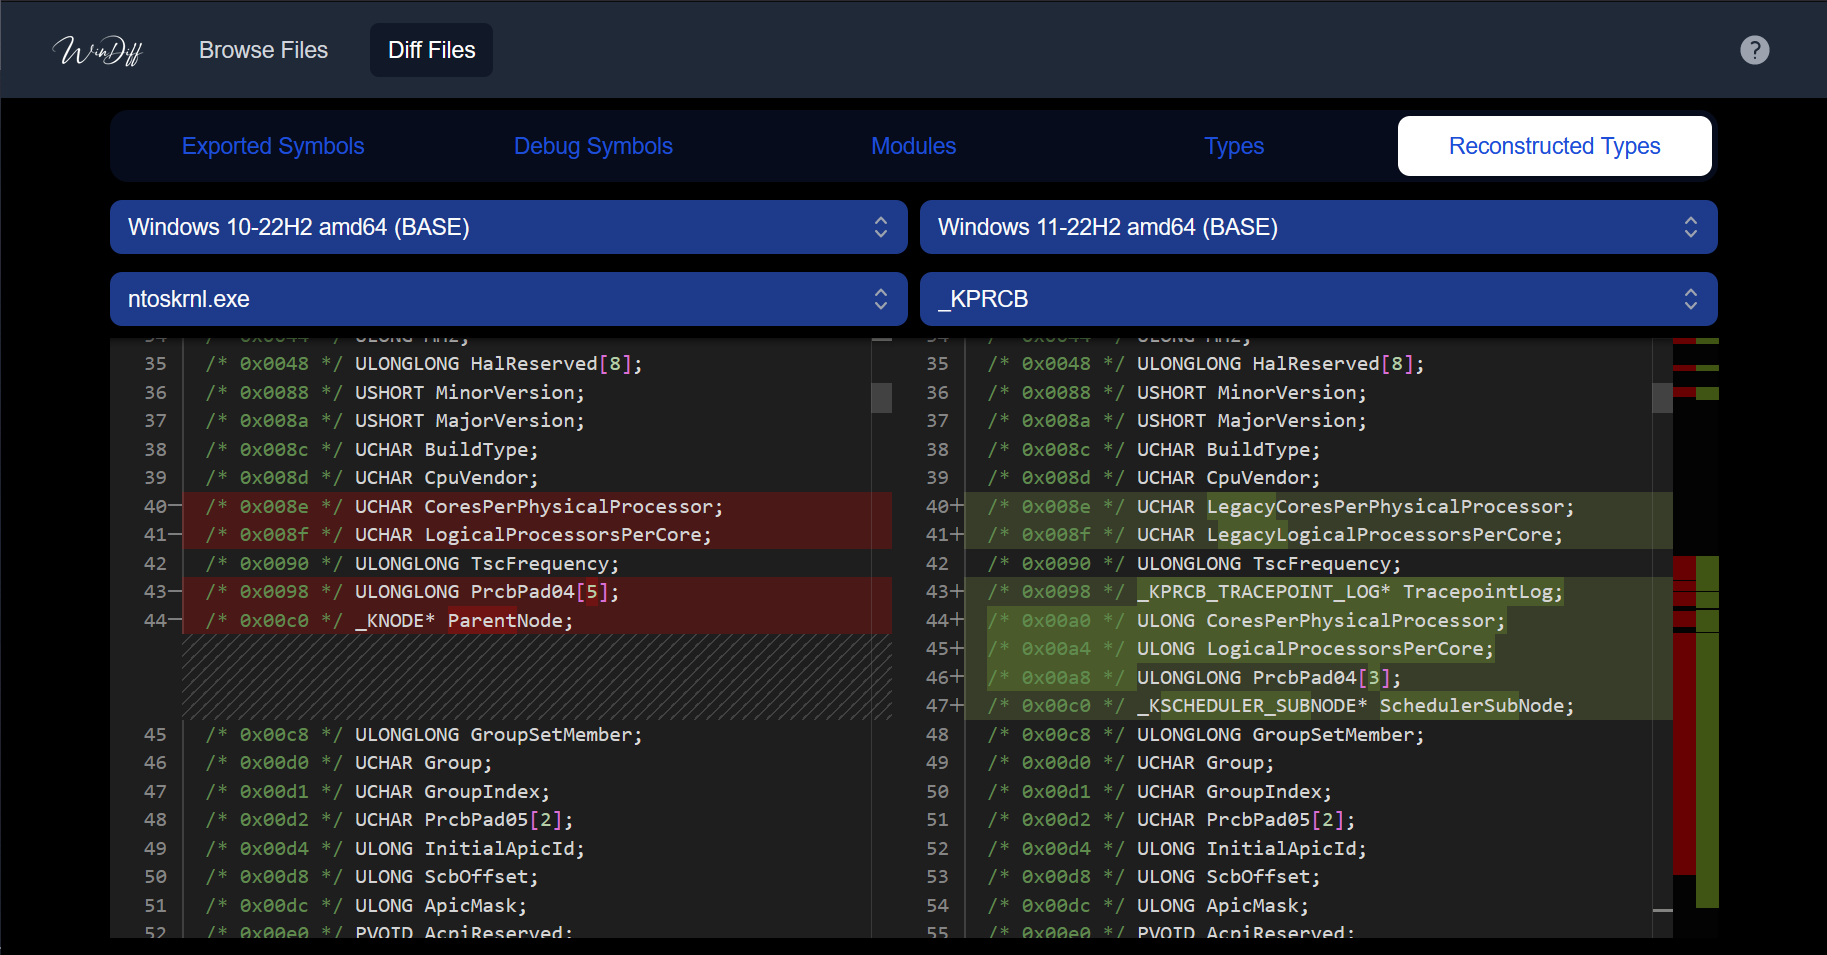 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
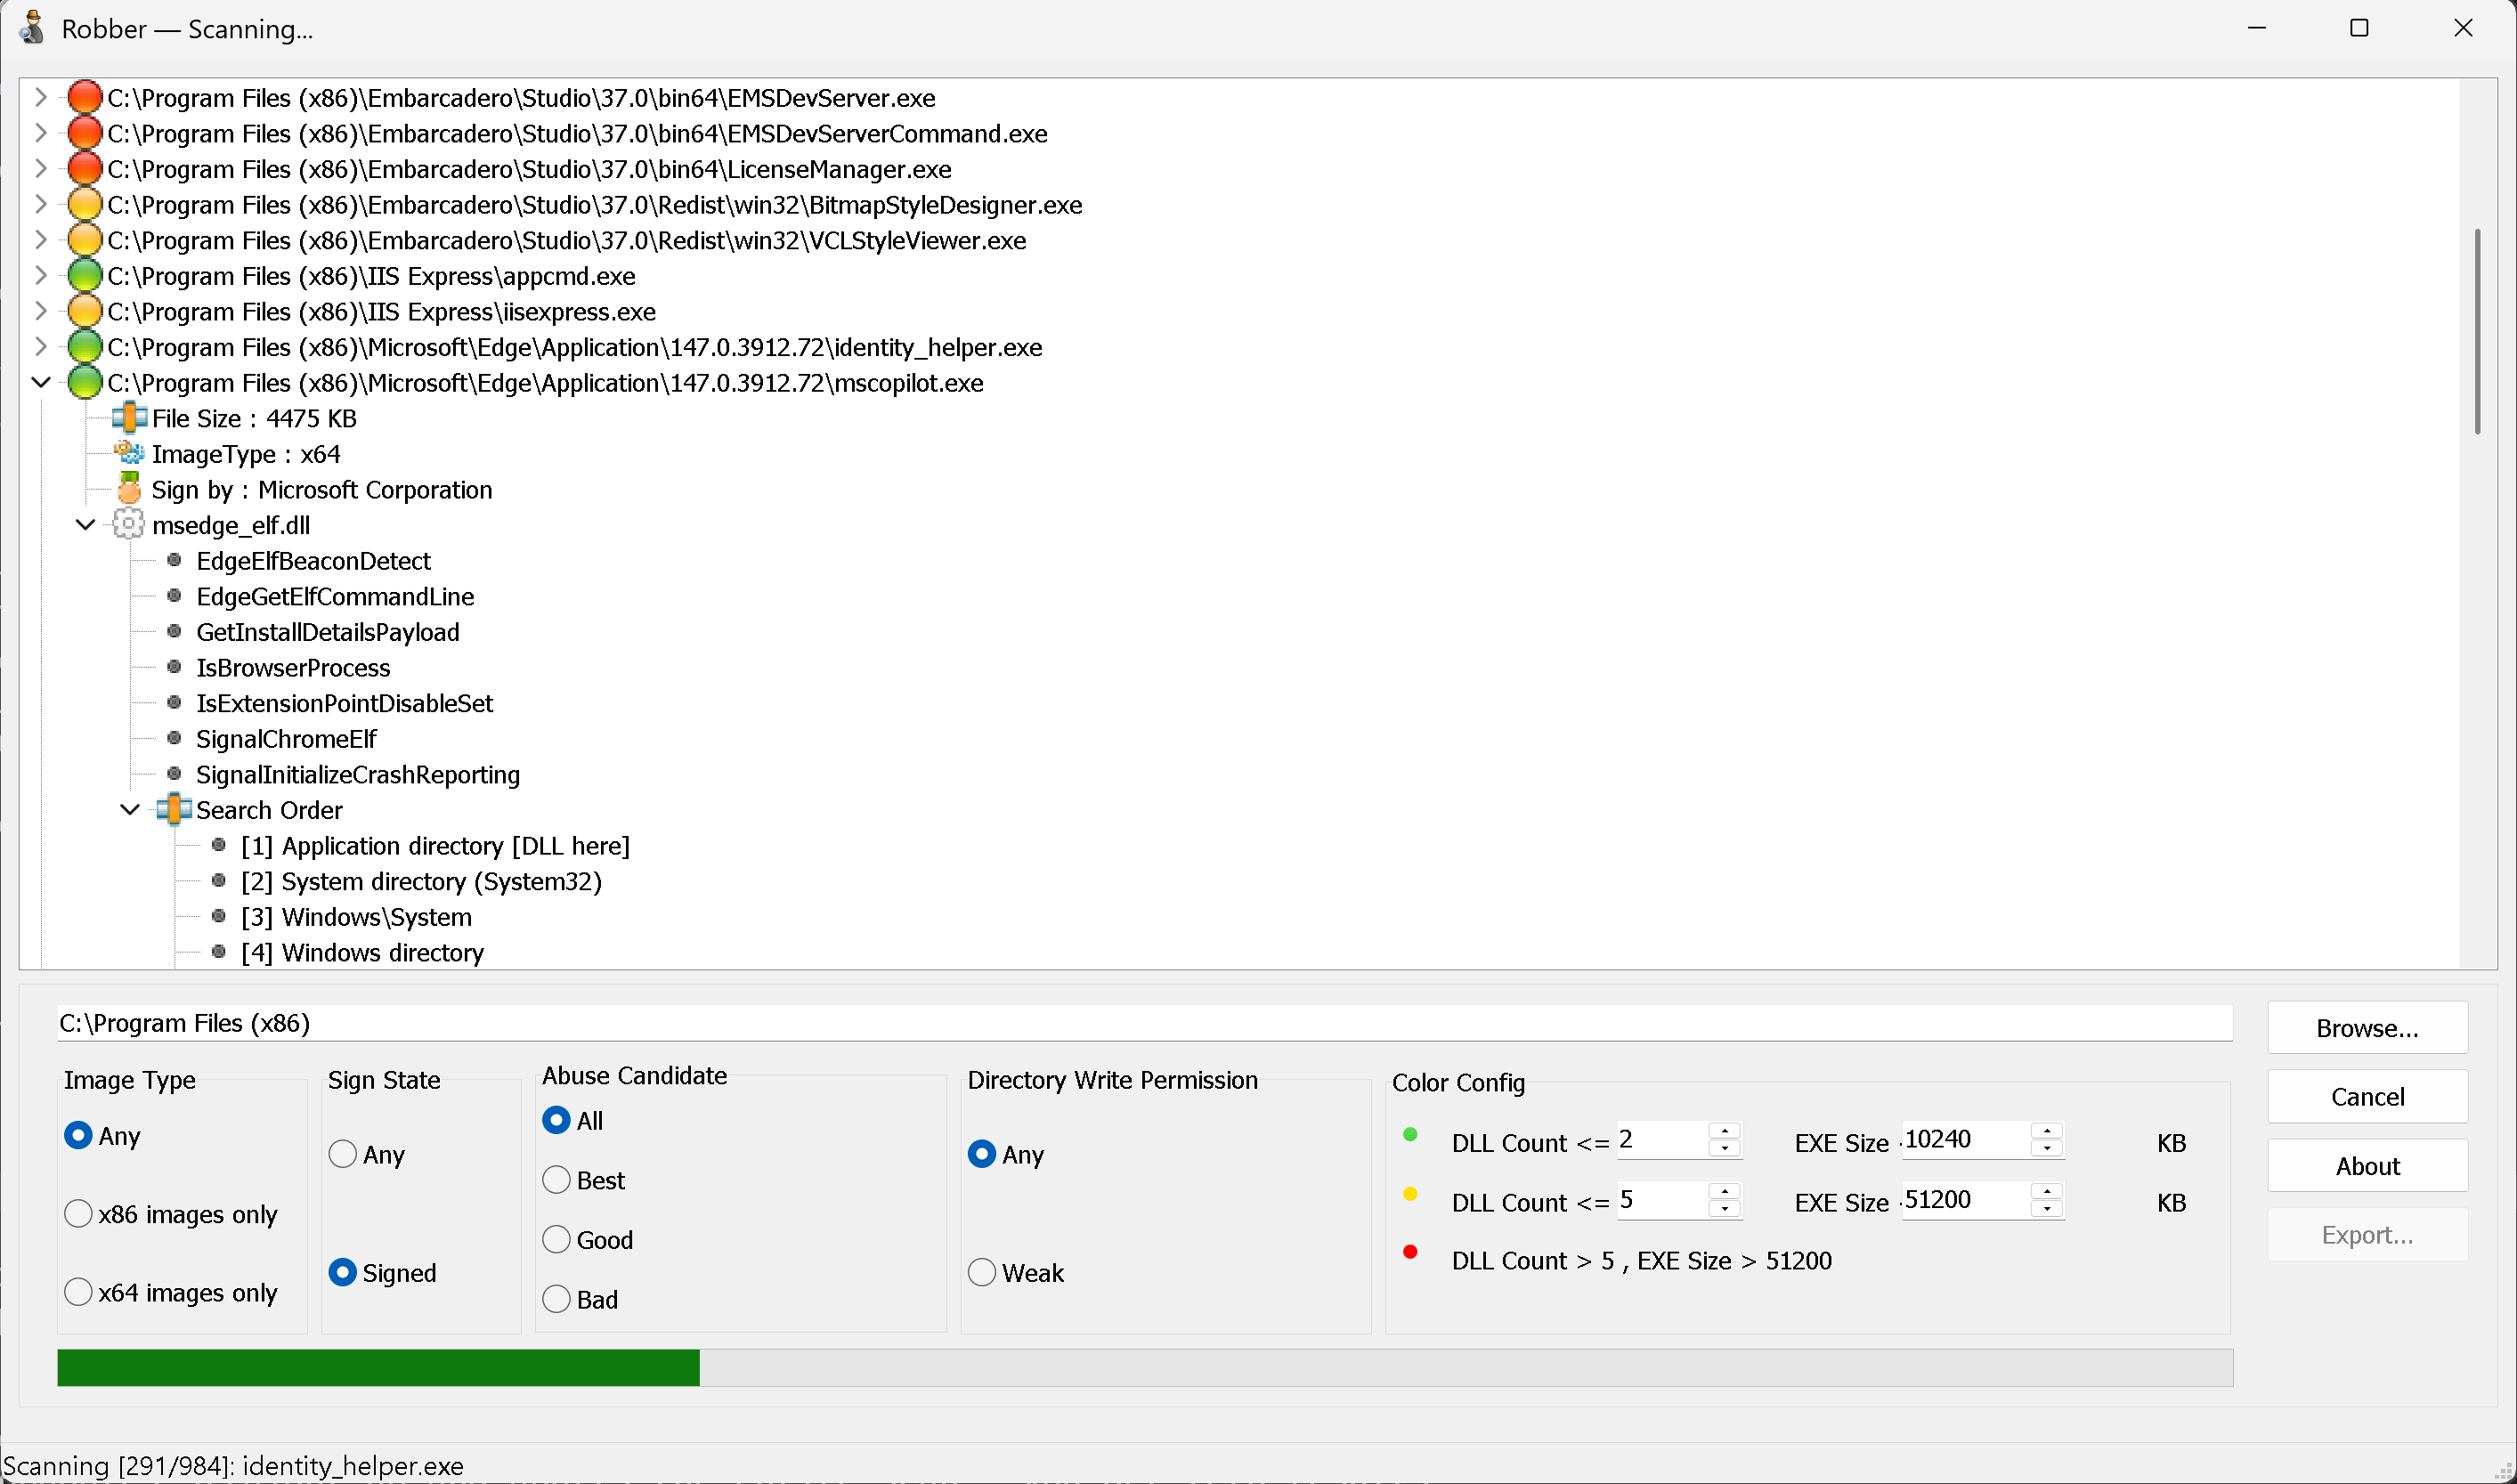 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
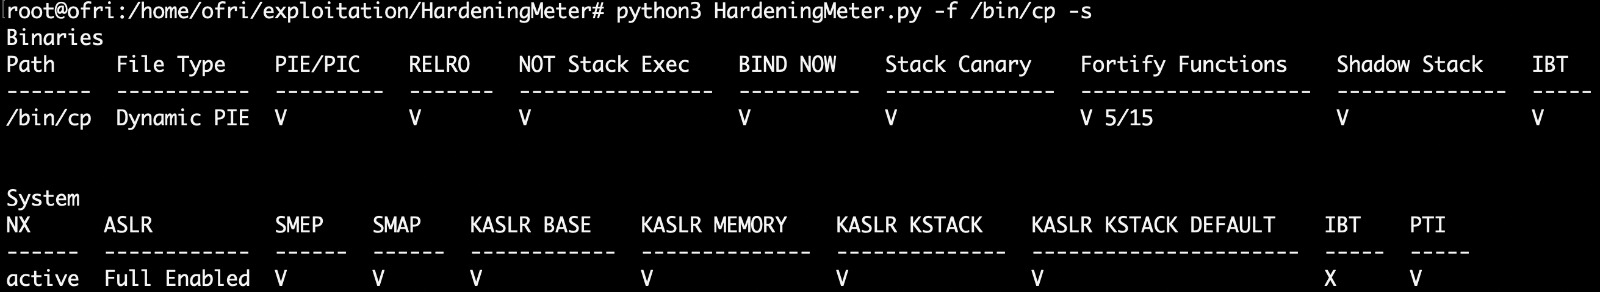 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.