

cortex
 pdb333/cortex
A Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
ai-assisted-reversingai-securitybinary-analysis+7
311 day ago
pdb333/cortexA Windows runtime analysis toolkit combining memory scanning, debugging, automation, and AI-friendly APIs.
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
 yaklang/javajive
Pure-Go Java Decompiler and Serialization Operator
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 mattiwatti/efiguard
Disable PatchGuard and Driver Signature Enforcement at boot time
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 hasherezade/pe-bear
Portable Executable reversing tool with a friendly GUI
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 sabecomoeh/cve-2013-3900
Proof-of-concept exploit for CVE-2013-3900, a WinVerifyTrust signature validation vulnerability enabling arbitrary code execution via crafted…
 ionescu007/simplevisor
Minimal Intel VT-x hypervisor for Windows and UEFI that virtualizes a live host for introspection, supporting dynamic hyperjacking, unhyperjacking,…
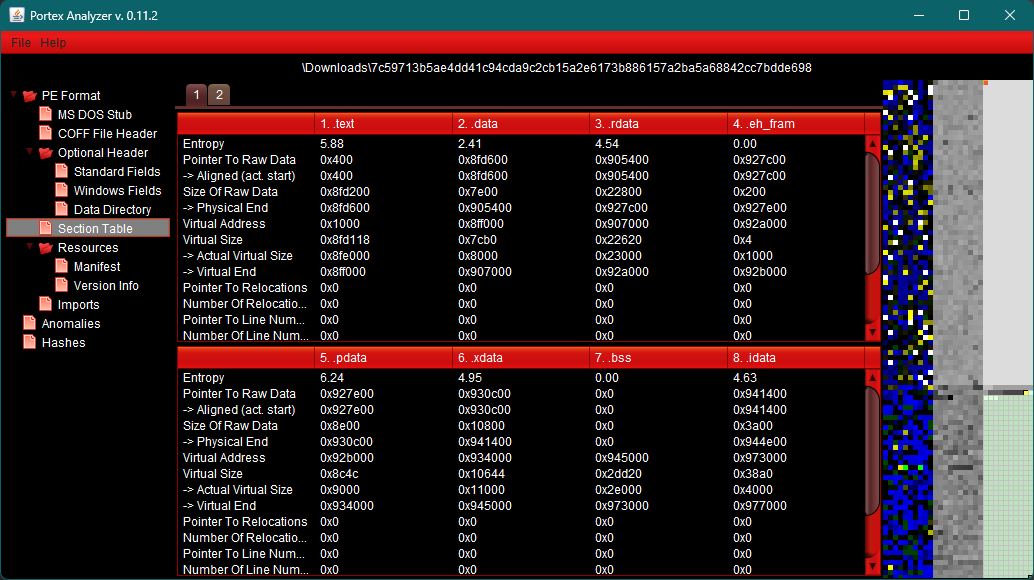 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
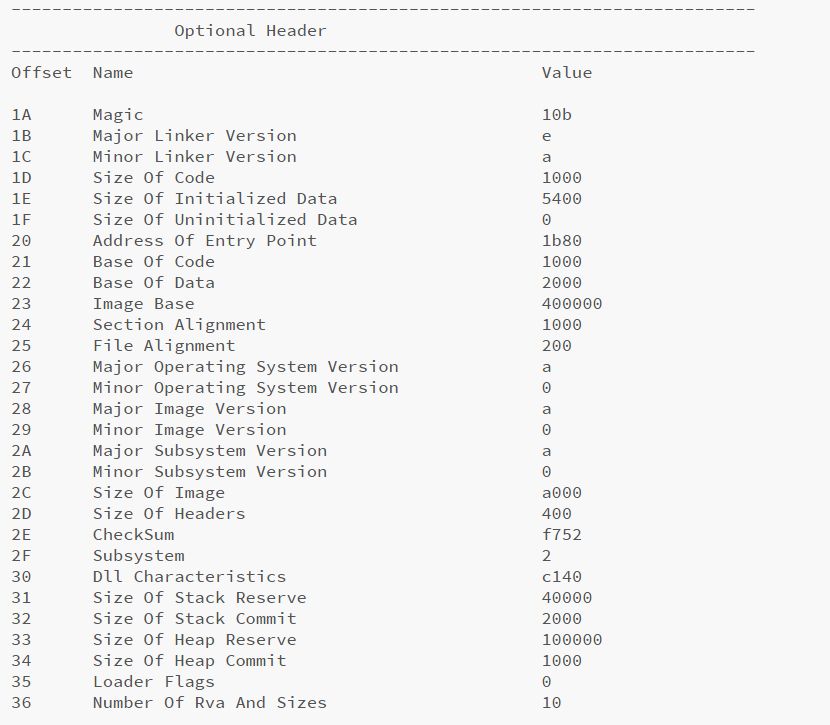 blacknbunny/peanalyzer
Advanced Portable Executable File Analyzer And Disassembler 32 & 64 Bit
 p0dalirius/pdbdownload
An utility to download PDB files associated with a Portable Executable (PE).
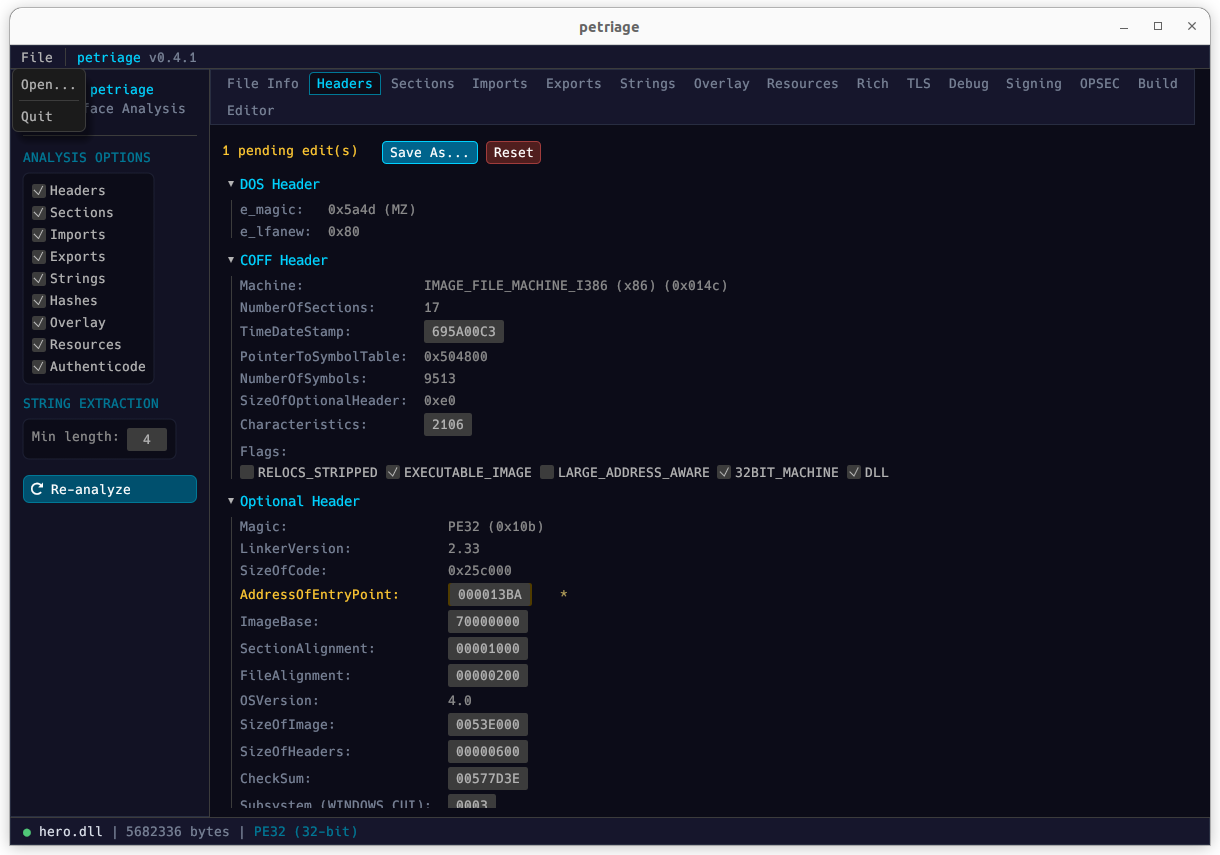 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.
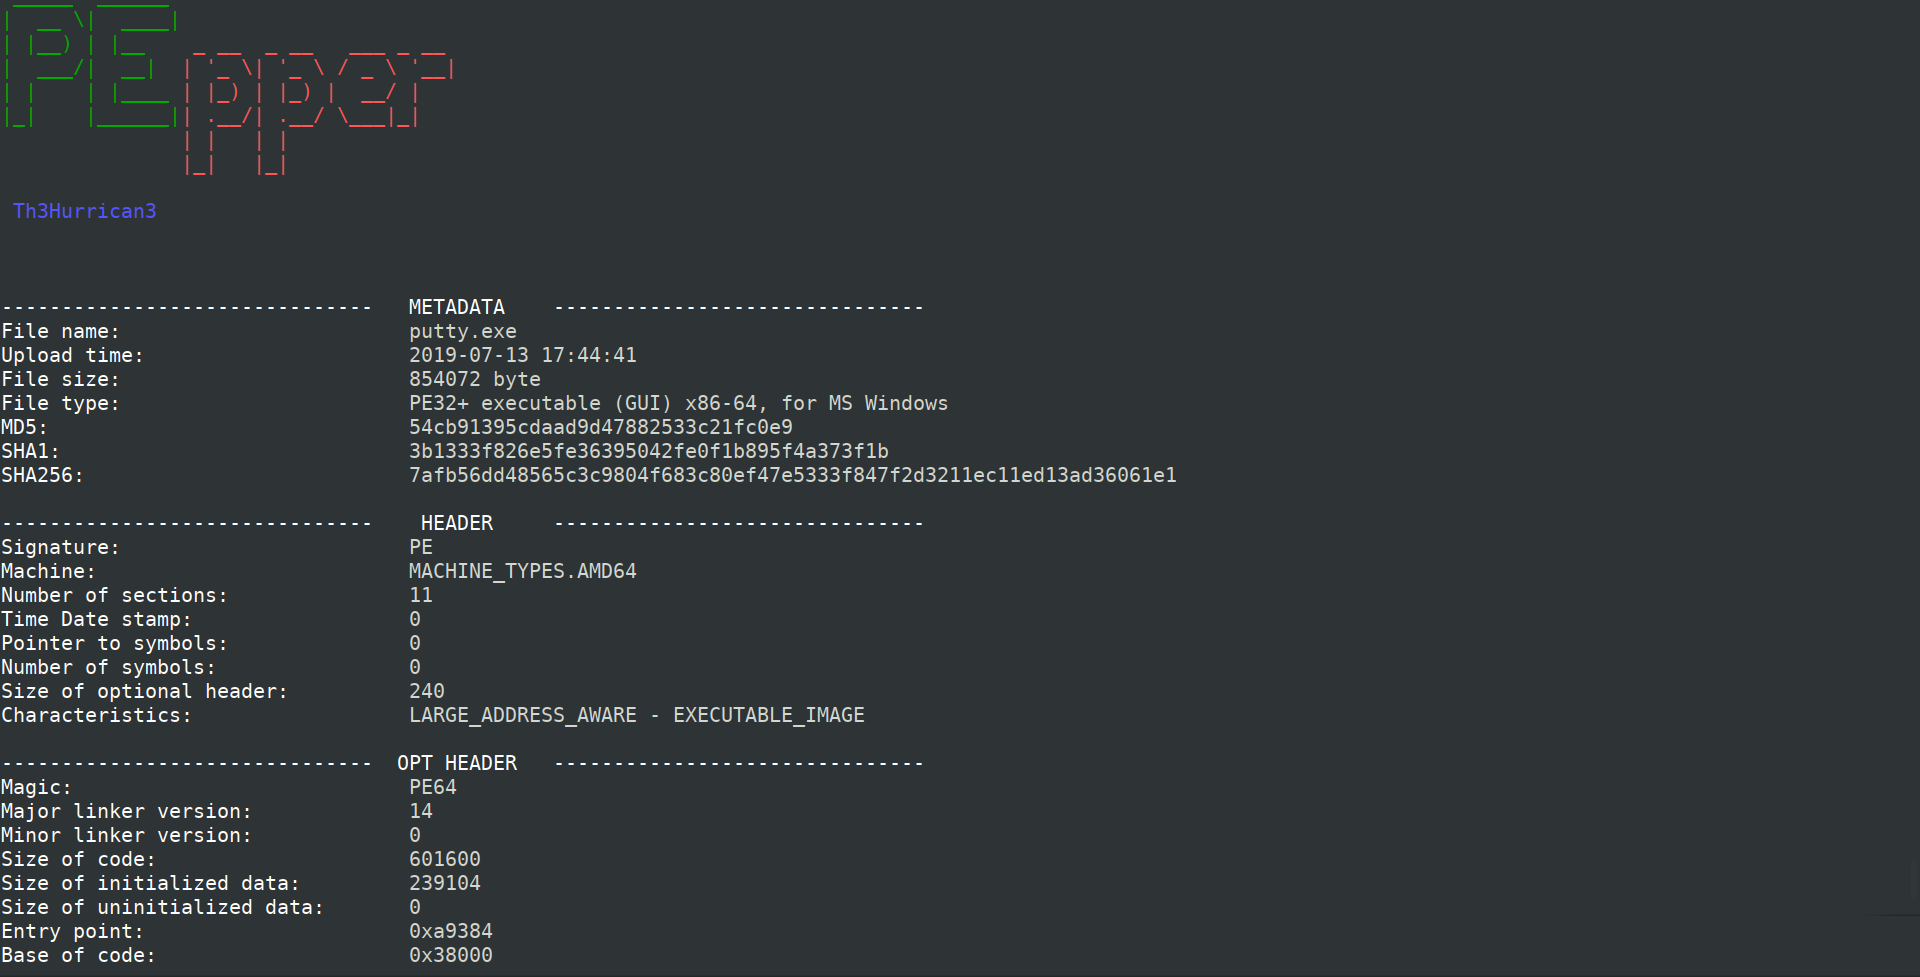 0x0be/pepper
An open source script to perform malware static analysis on Portable Executable