

rdx
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
android-securitybinary-analysiscode-analysis+6
ch0pin/rdxA native APK and DEX decompiler written in Rust
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 qilingframework/qiling
A True Instrumentable Binary Emulation Framework
 mrphrazer/msynth
Code deobfuscation framework to simplify Mixed Boolean-Arithmetic (MBA) expressions
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 jackofmosttrades/gadgetinspector
A byte code analyzer for finding deserialization gadget chains in Java applications
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
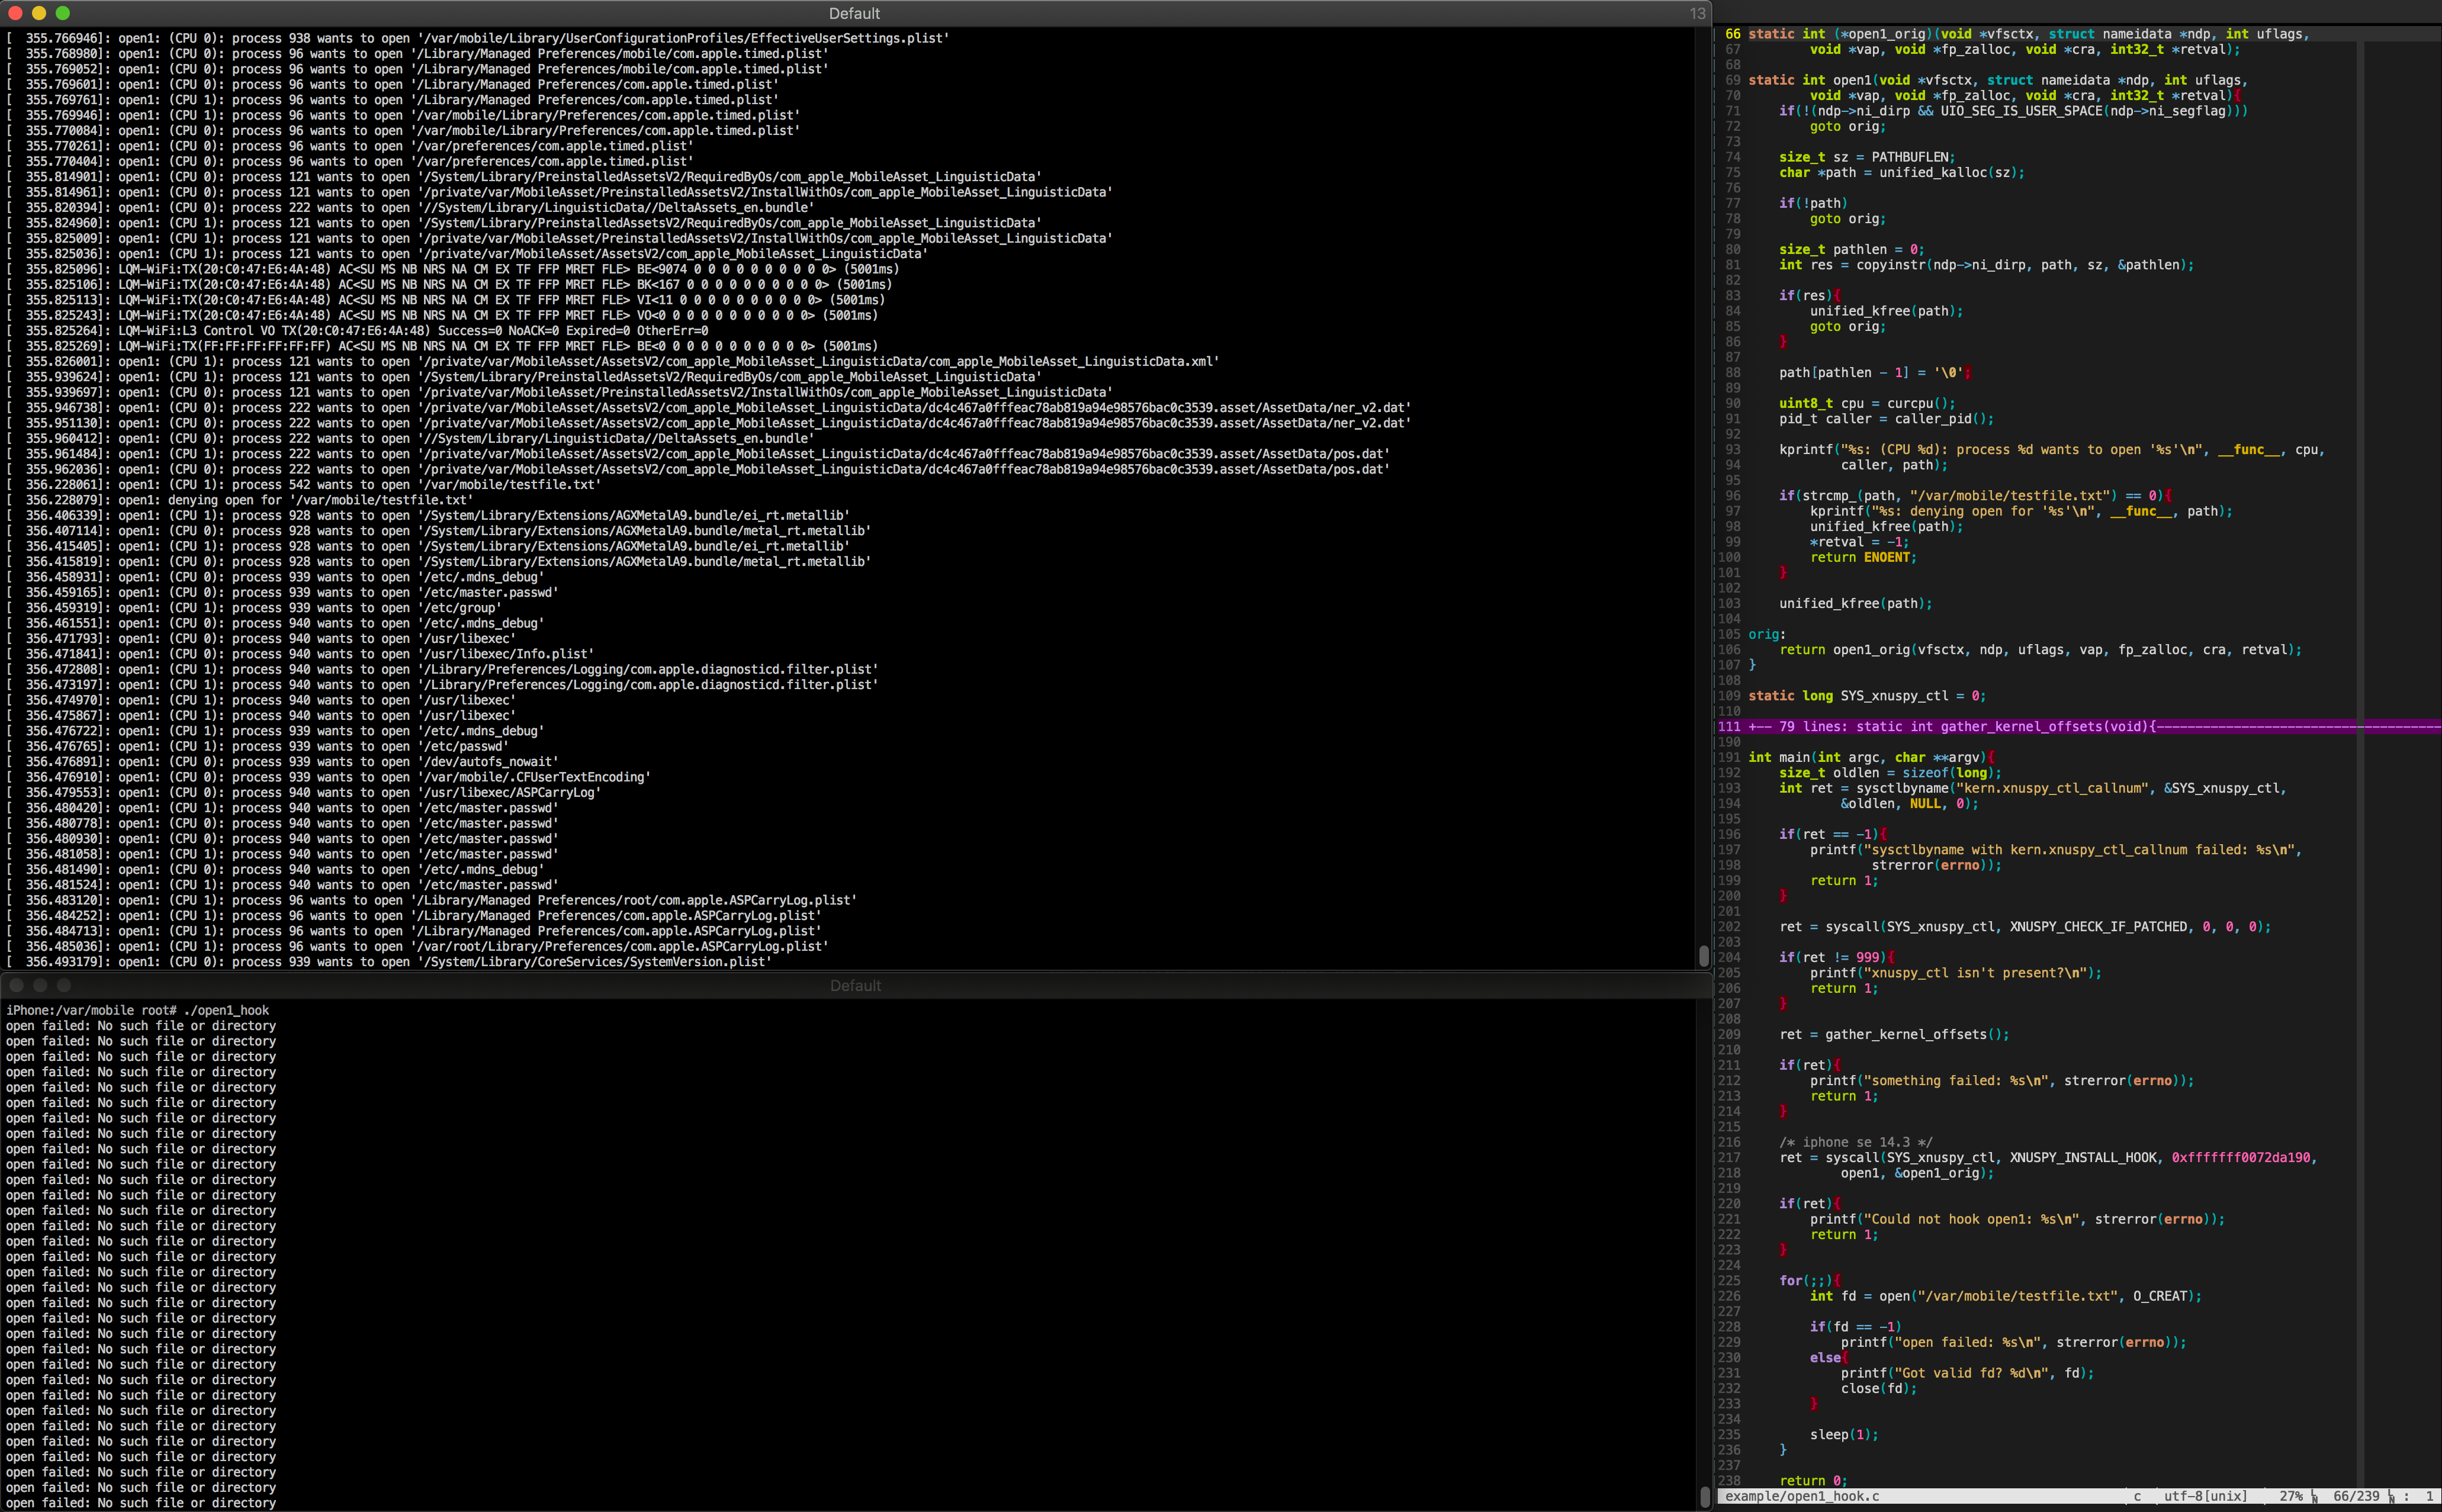 jsherman212/xnuspy
an iOS kernel function hooking framework for checkra1n'able devices
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 immunityinc/libptrace
An event driven multi-core process debugging, tracing, and manipulation framework.
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 angr/angr
A powerful and user-friendly binary analysis platform!
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection