HPE-Aruba-AOS8-Vulnerabilities

ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…

ArubaOS 8.13.2.0 pre-auth attack surface research. XXE+SSRF, ICMP reflection, buffer over-read, hardcoded credentials — all submitted to HPE…

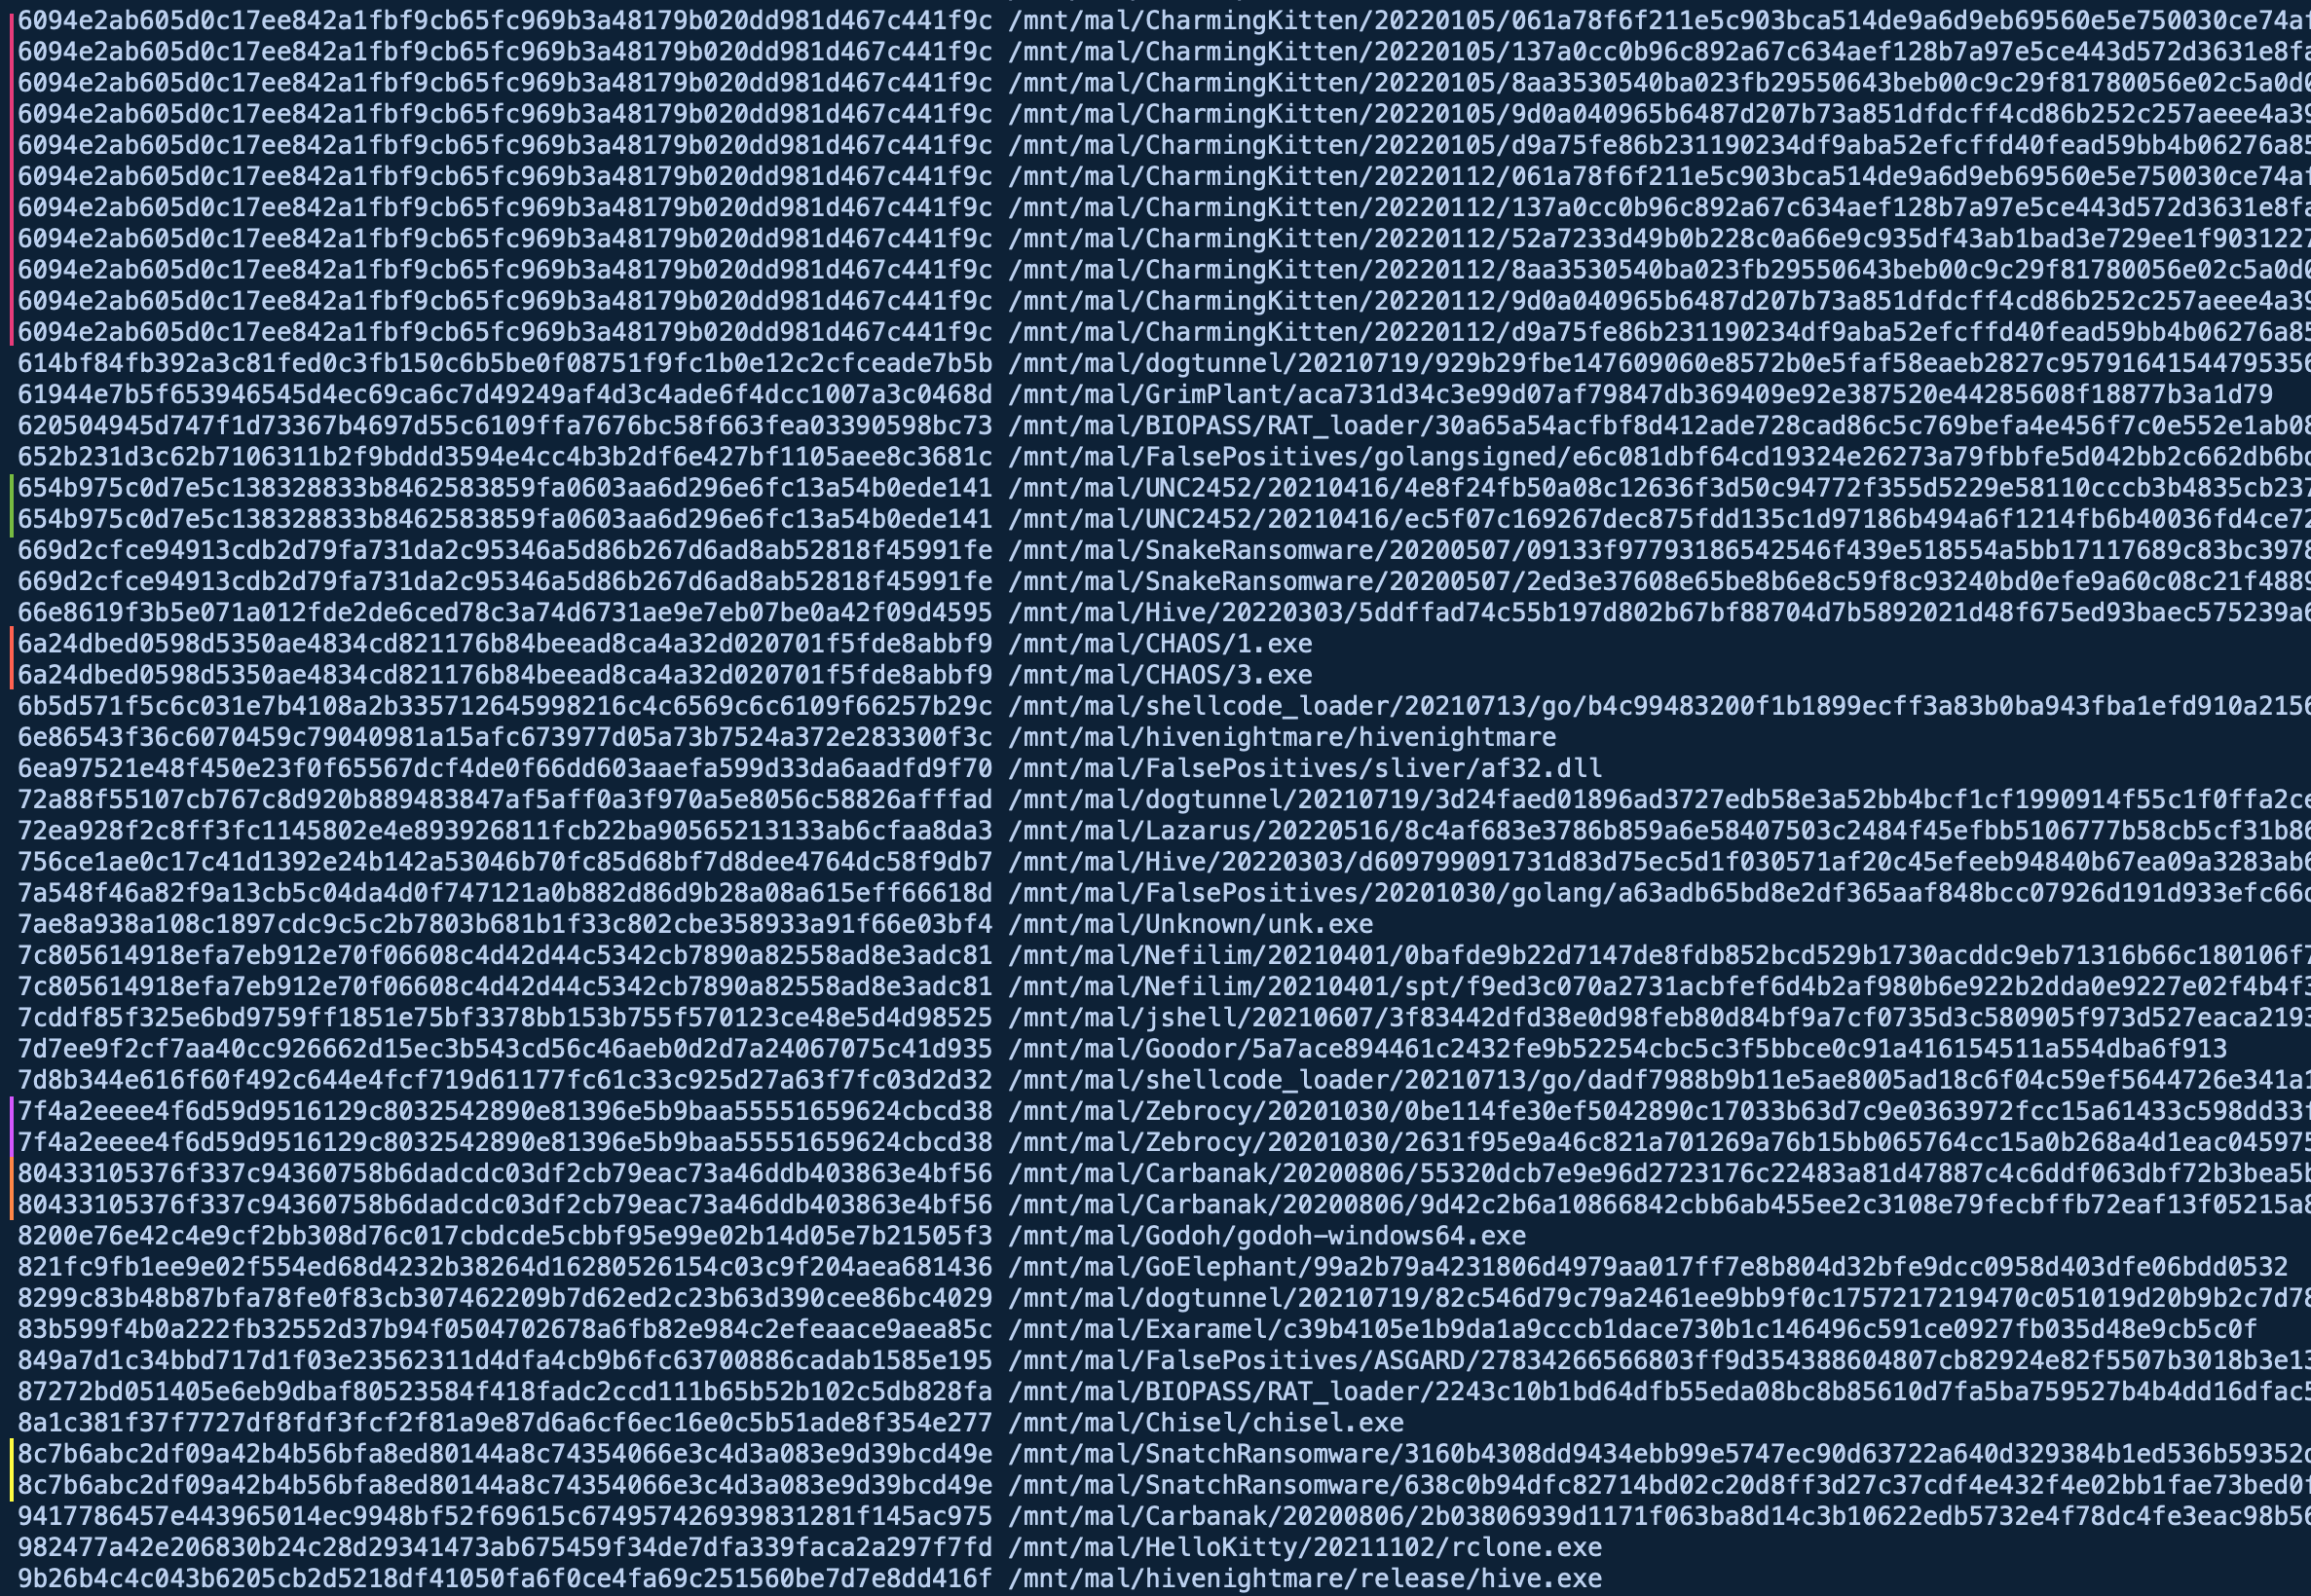
A small utility to deal with malware embedded hashes.

Cryptanalysis of a proprietary 1999 video DRM system. Recovers 61 encrypted wrestling videos from the WCW Internet Powerdisk CD-ROM through static…

Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.

Imphash-like calculation on Golang binaries

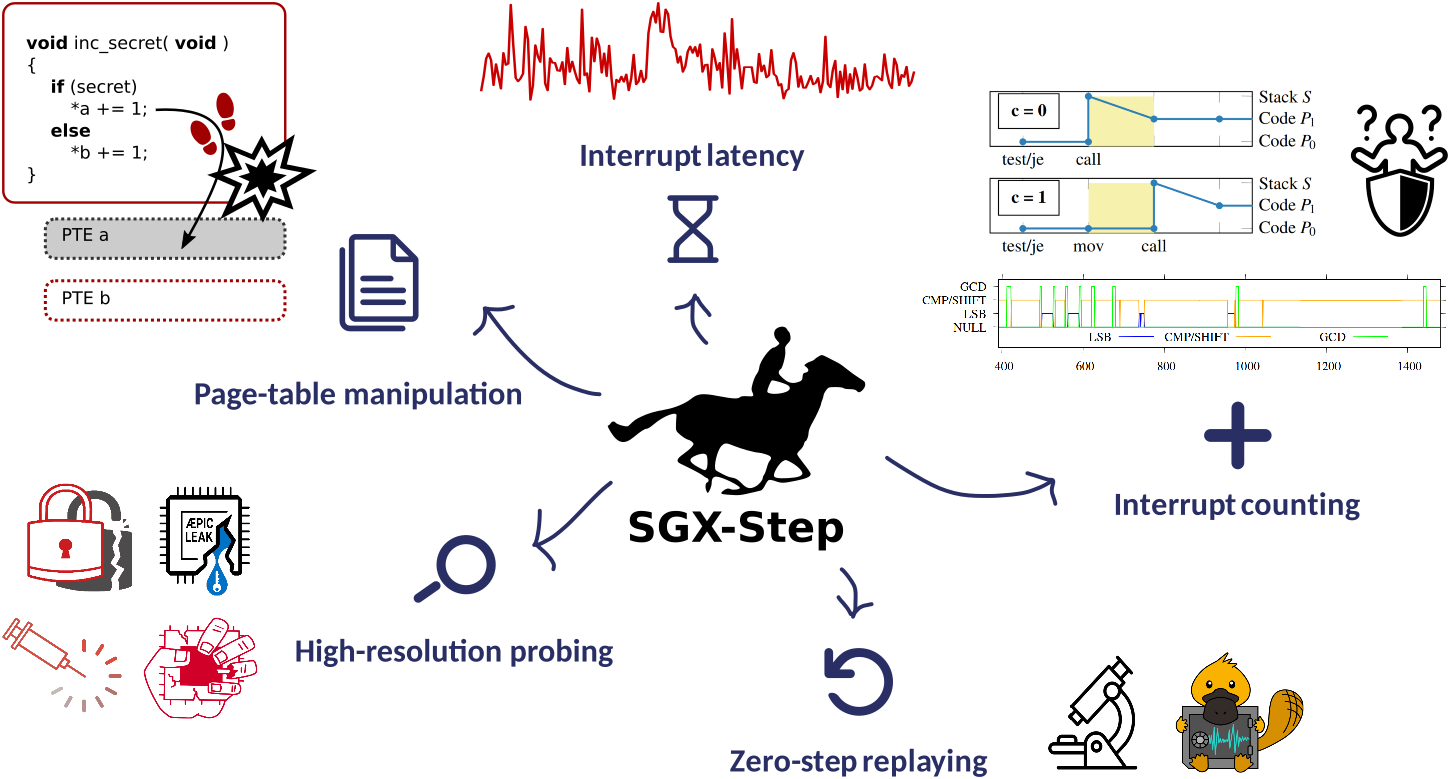
A practical attack framework for precise enclave execution control

Toolkit for implant attack of IoT devices

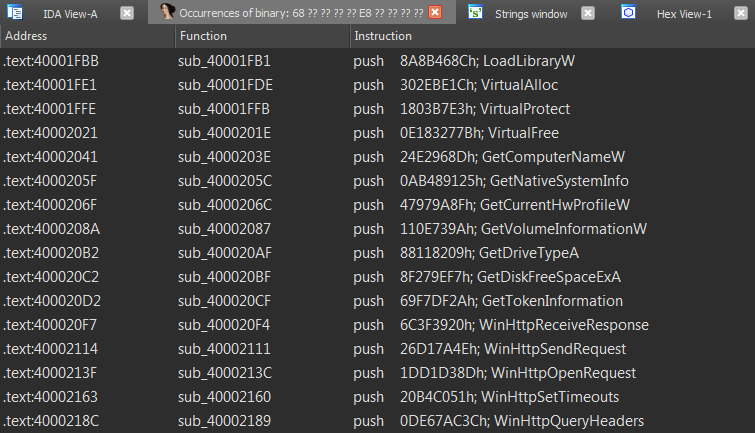
Assortment of hashing algorithms used in malware

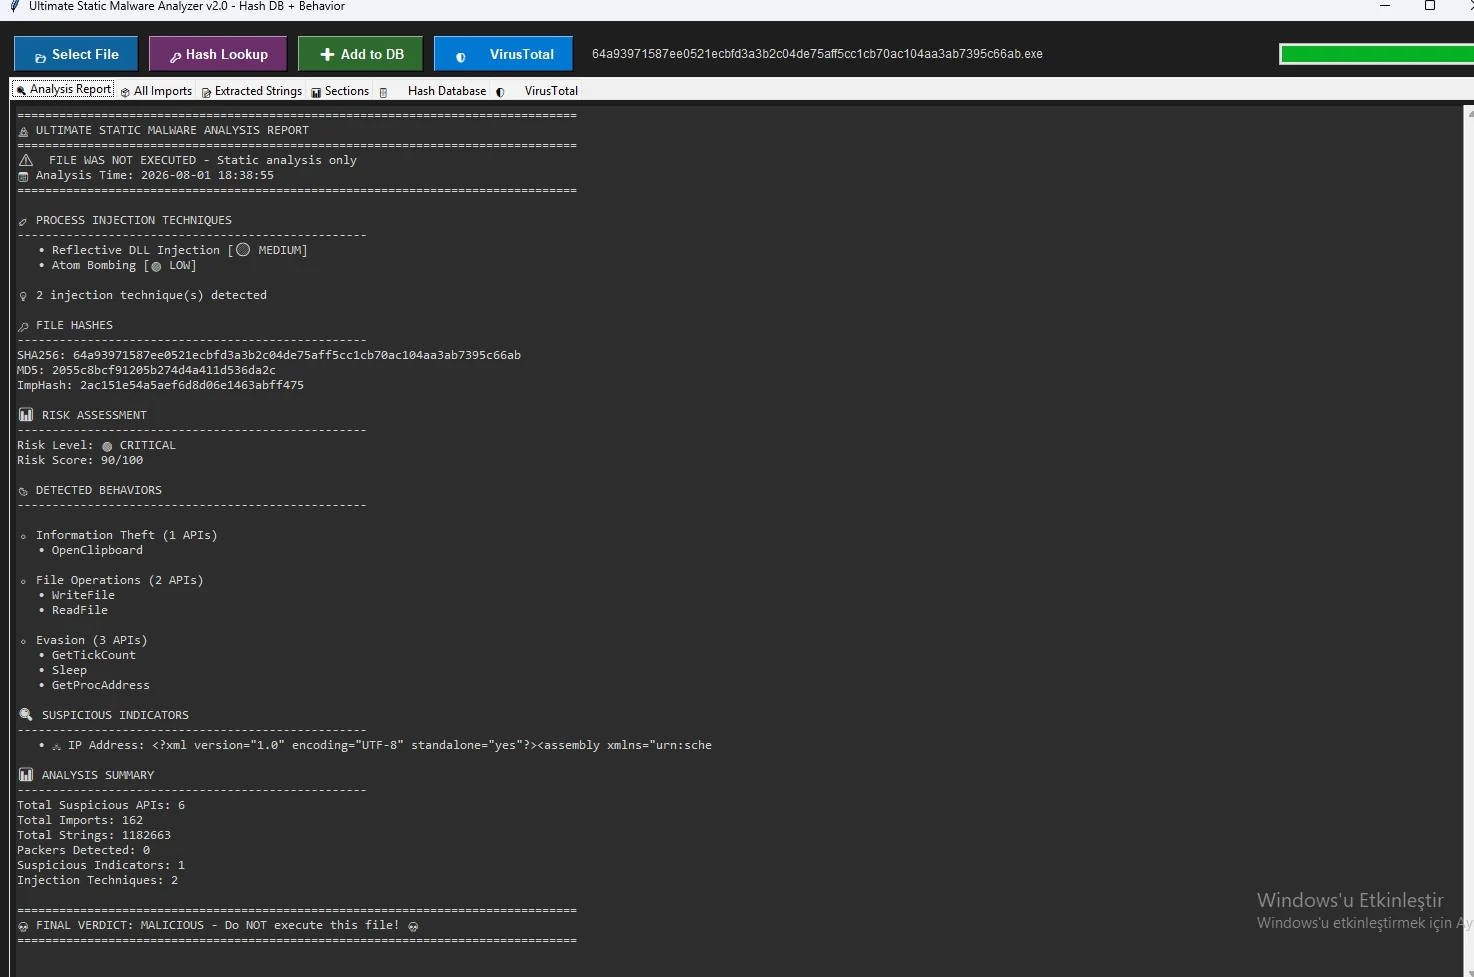
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Exploit script for CVE-2021-27211

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness


Automatically find and execute fault injection attacks

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

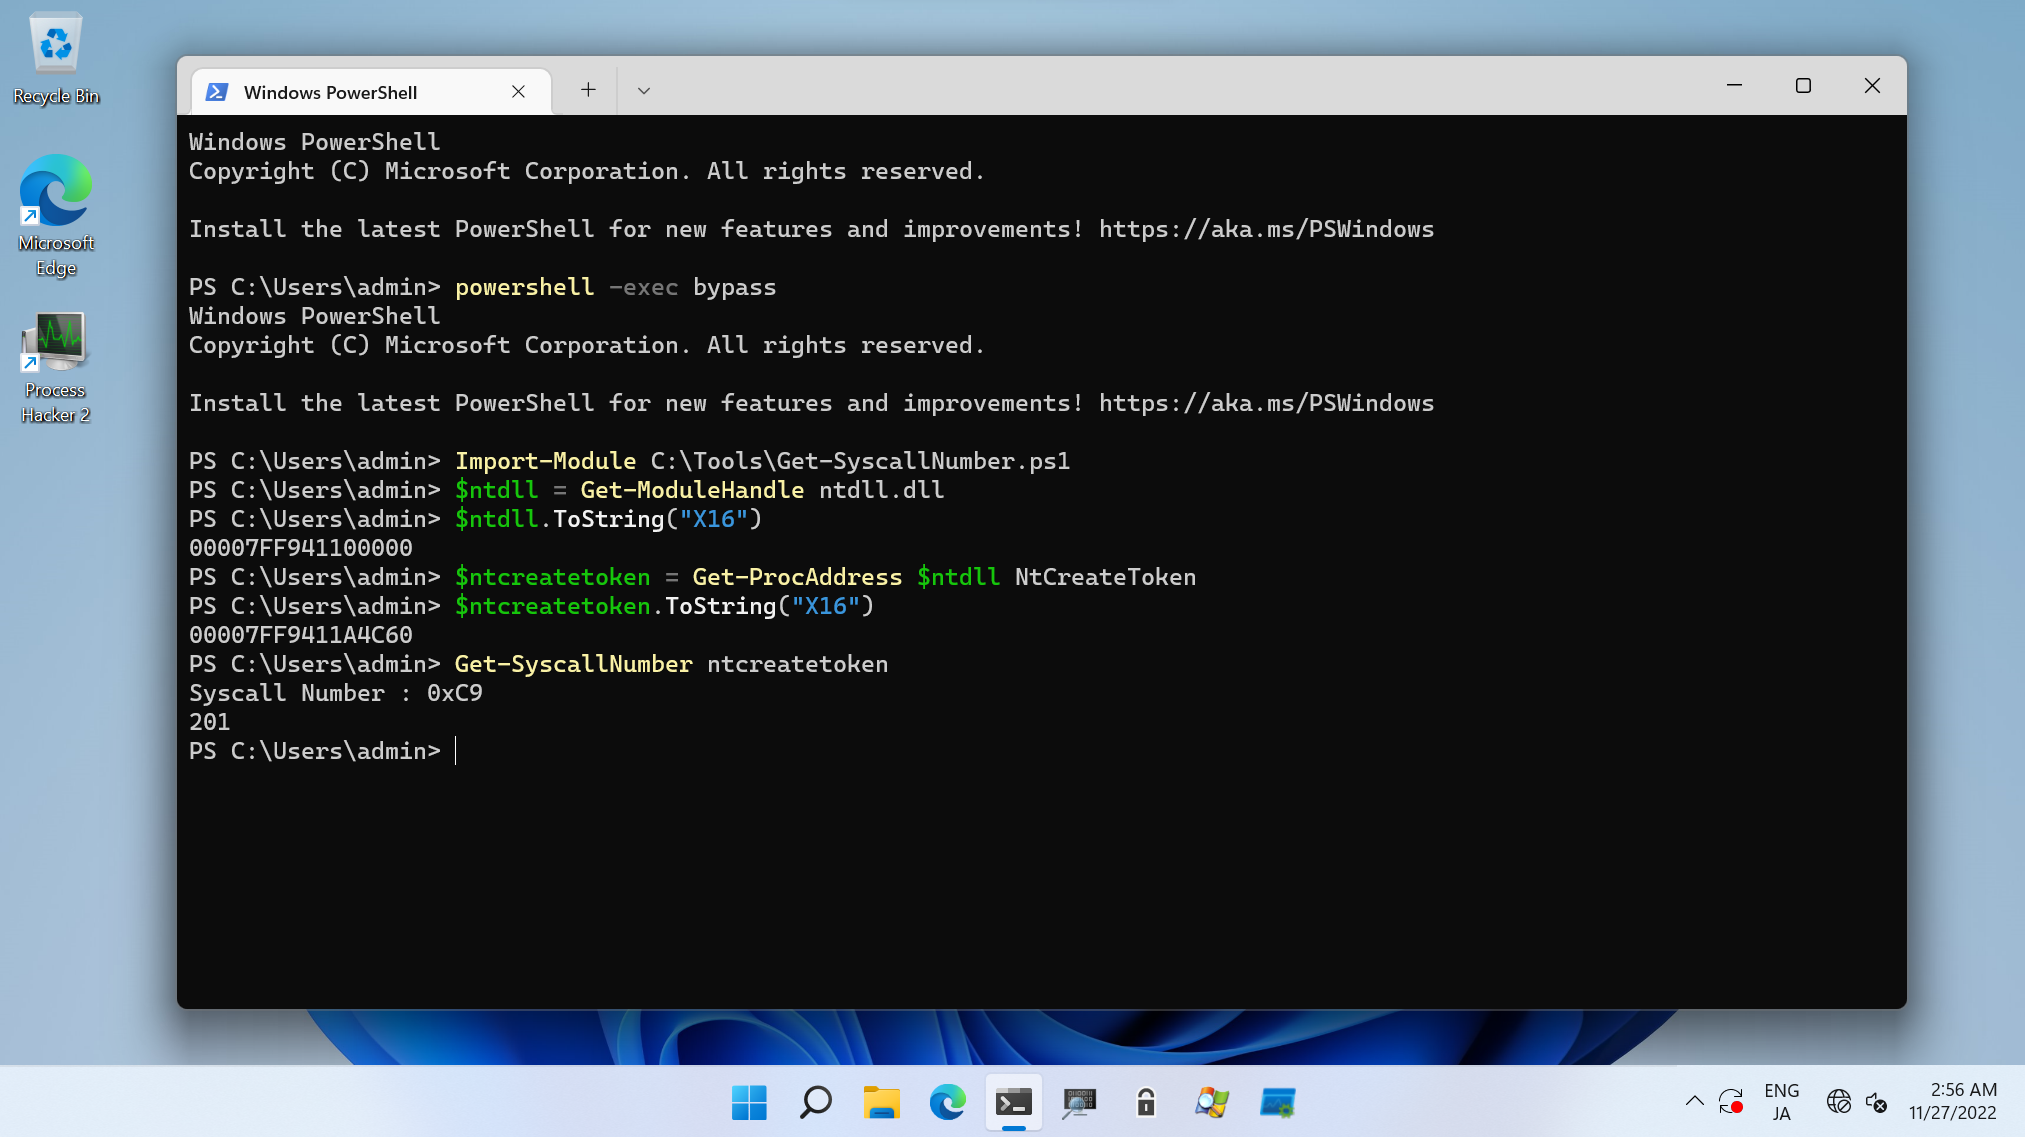
Tools and PoCs for Windows syscall investigation.