
CVE-2025-32432
Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…
authentication-authorizationexploitationinformation-gathering+3
Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Proof-of-concept exploit for CVE-2024-47533, an unauthenticated authentication bypass in Cobbler's XMLRPC API leading to remote code execution via…

Multiple exploits for Monitorr

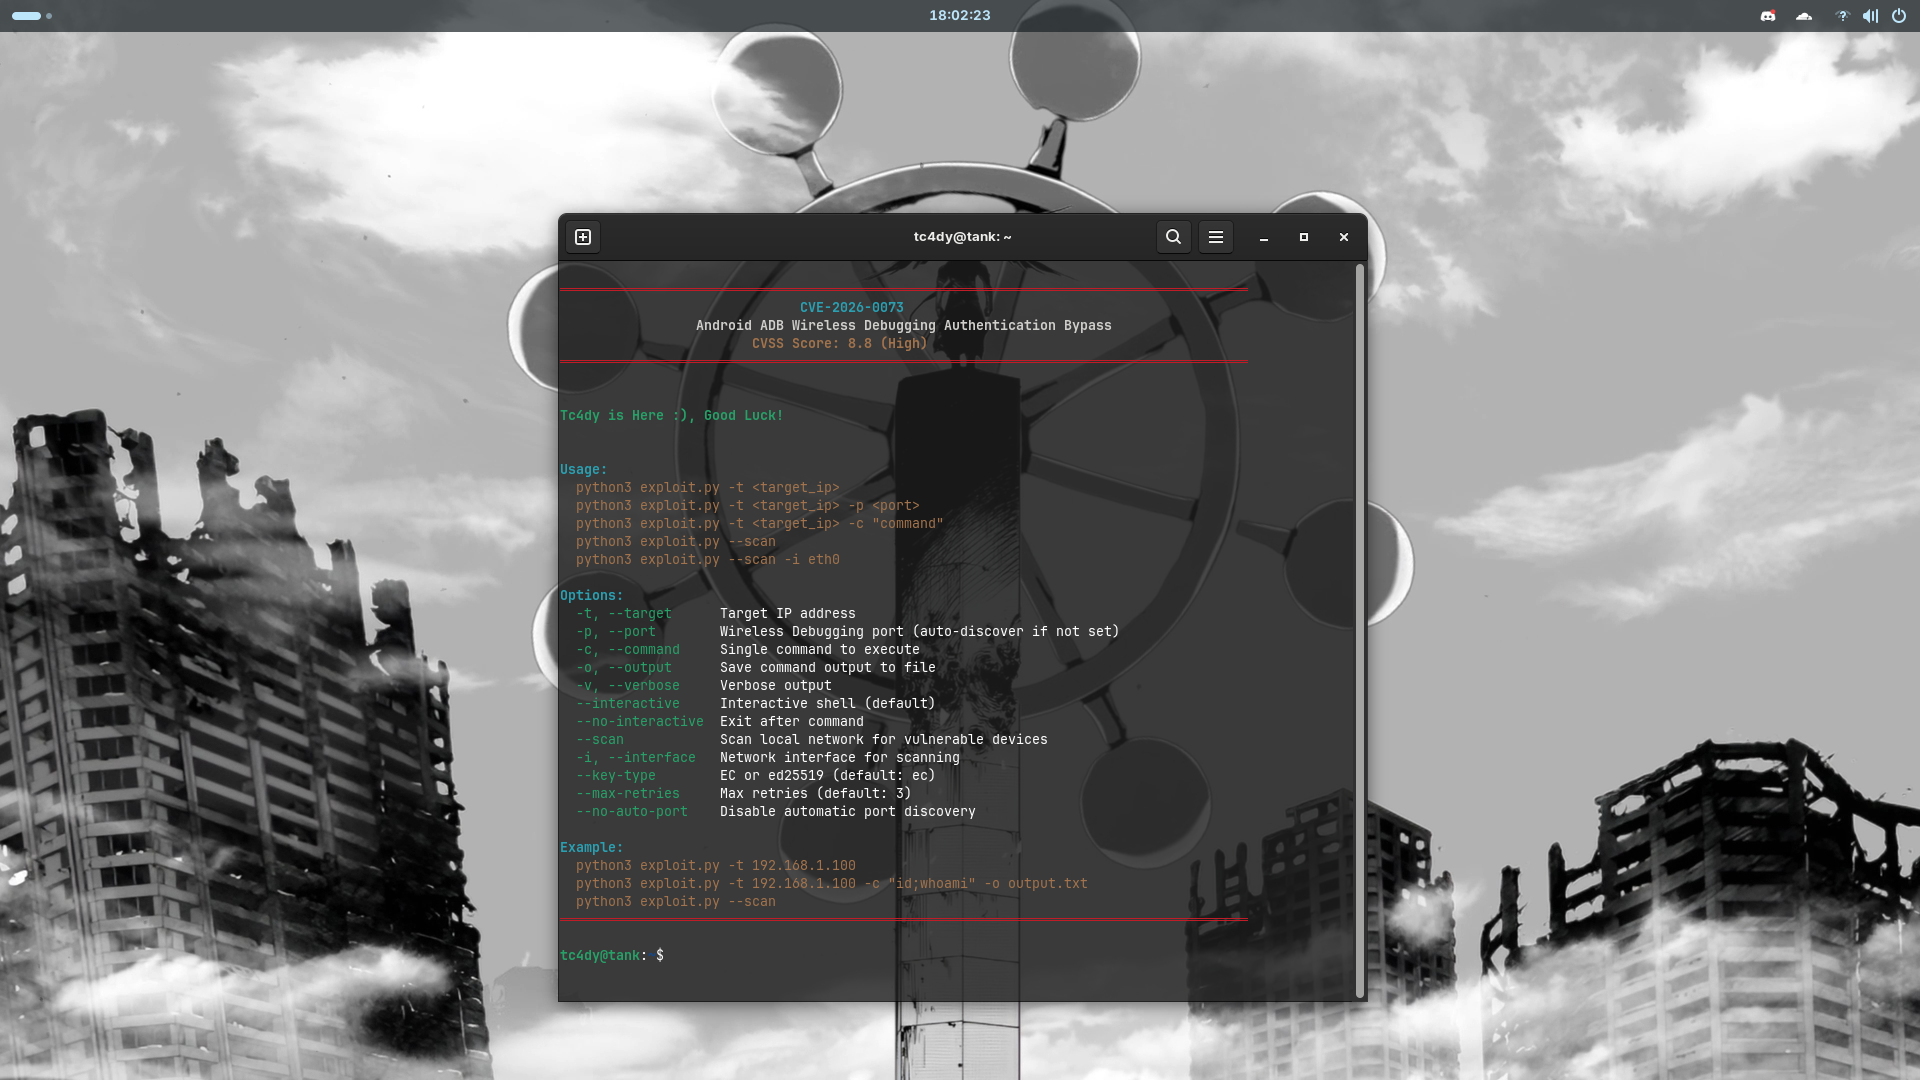
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…