connectwise-screenconnect_auth-bypass-add-user-poc

Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…

Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…

ScriptCase Pre-Authenticated Remote Command Execution exploitation script (CVE-2025-47227, CVE-2025-47228).

Python script to exploit the OWASSRF + TabShell chain on vulnerable Microsoft Exchange servers, leveraging Kerberos authentication for command…

The Governed Agentic AI Operating System — Rust + Tauri 2.0 | 65 crates, 658 commands, 84 pages, 5,029 tests, 10/10 OWASP

A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

Unauthenticated Remote Code Execution through authentication bypass and command injection in Cacti < 1.2.23 and < 1.3.0

CVE-2018-10933 very simple POC

Exploit for Gogs RCE (CVE-2018-18925) leveraging session forgery and Git hook injection to achieve arbitrary command execution with root privileges.

Exploit for CVE-2023-27524 targeting Apache Superset auth bypass and RCE. Forges session cookies, enumerates databases/users, executes OS commands,…

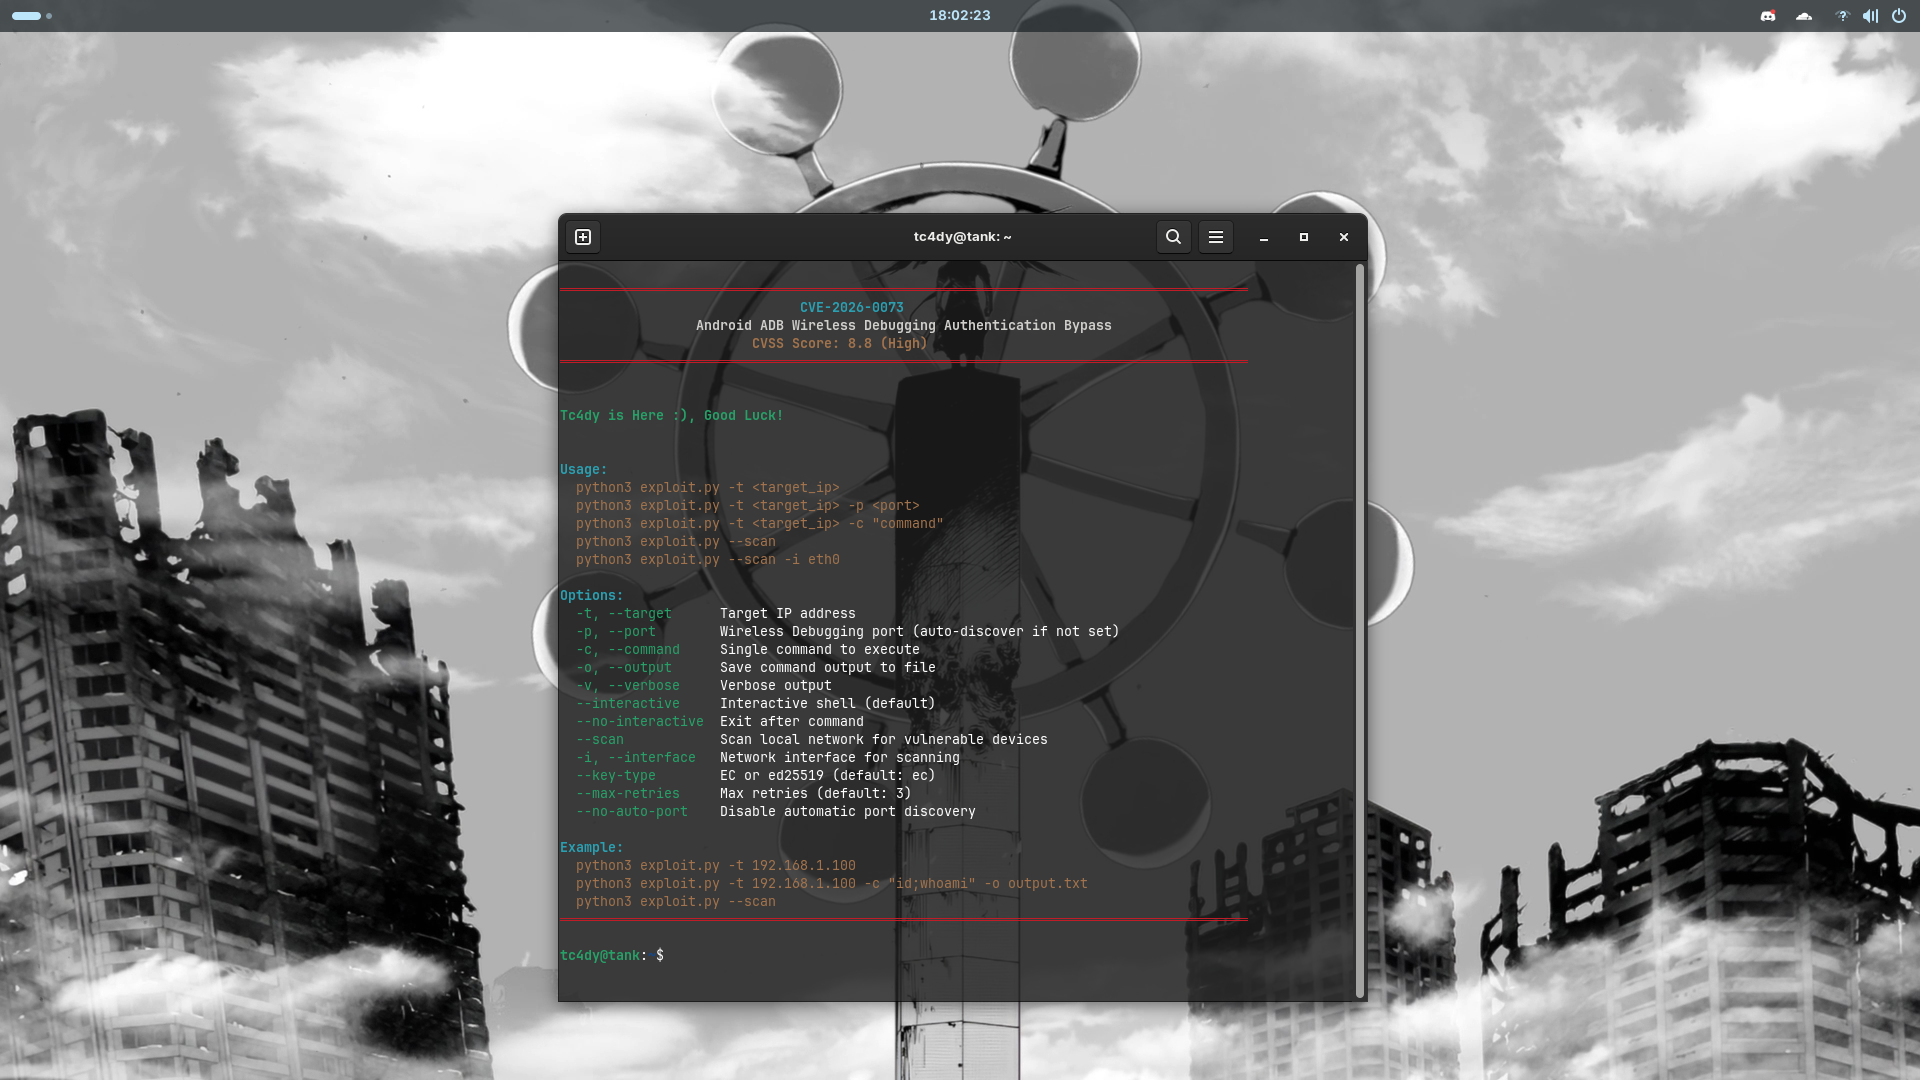
Zero-click authentication bypass exploit for Android ADB Wireless Debugging (CVE-2026-0073). Provides interactive shell, command execution, and…

Exploit for CVE-2024-0012 and CVE-2024-9474 targeting authentication bypass and authenticated command injection in Palo Alto PAN-OS management web…

Proof-of-concept exploit for CVE-2019-10915 targeting an authentication bypass in Siemens TIA Administrator, enabling remote command execution via…

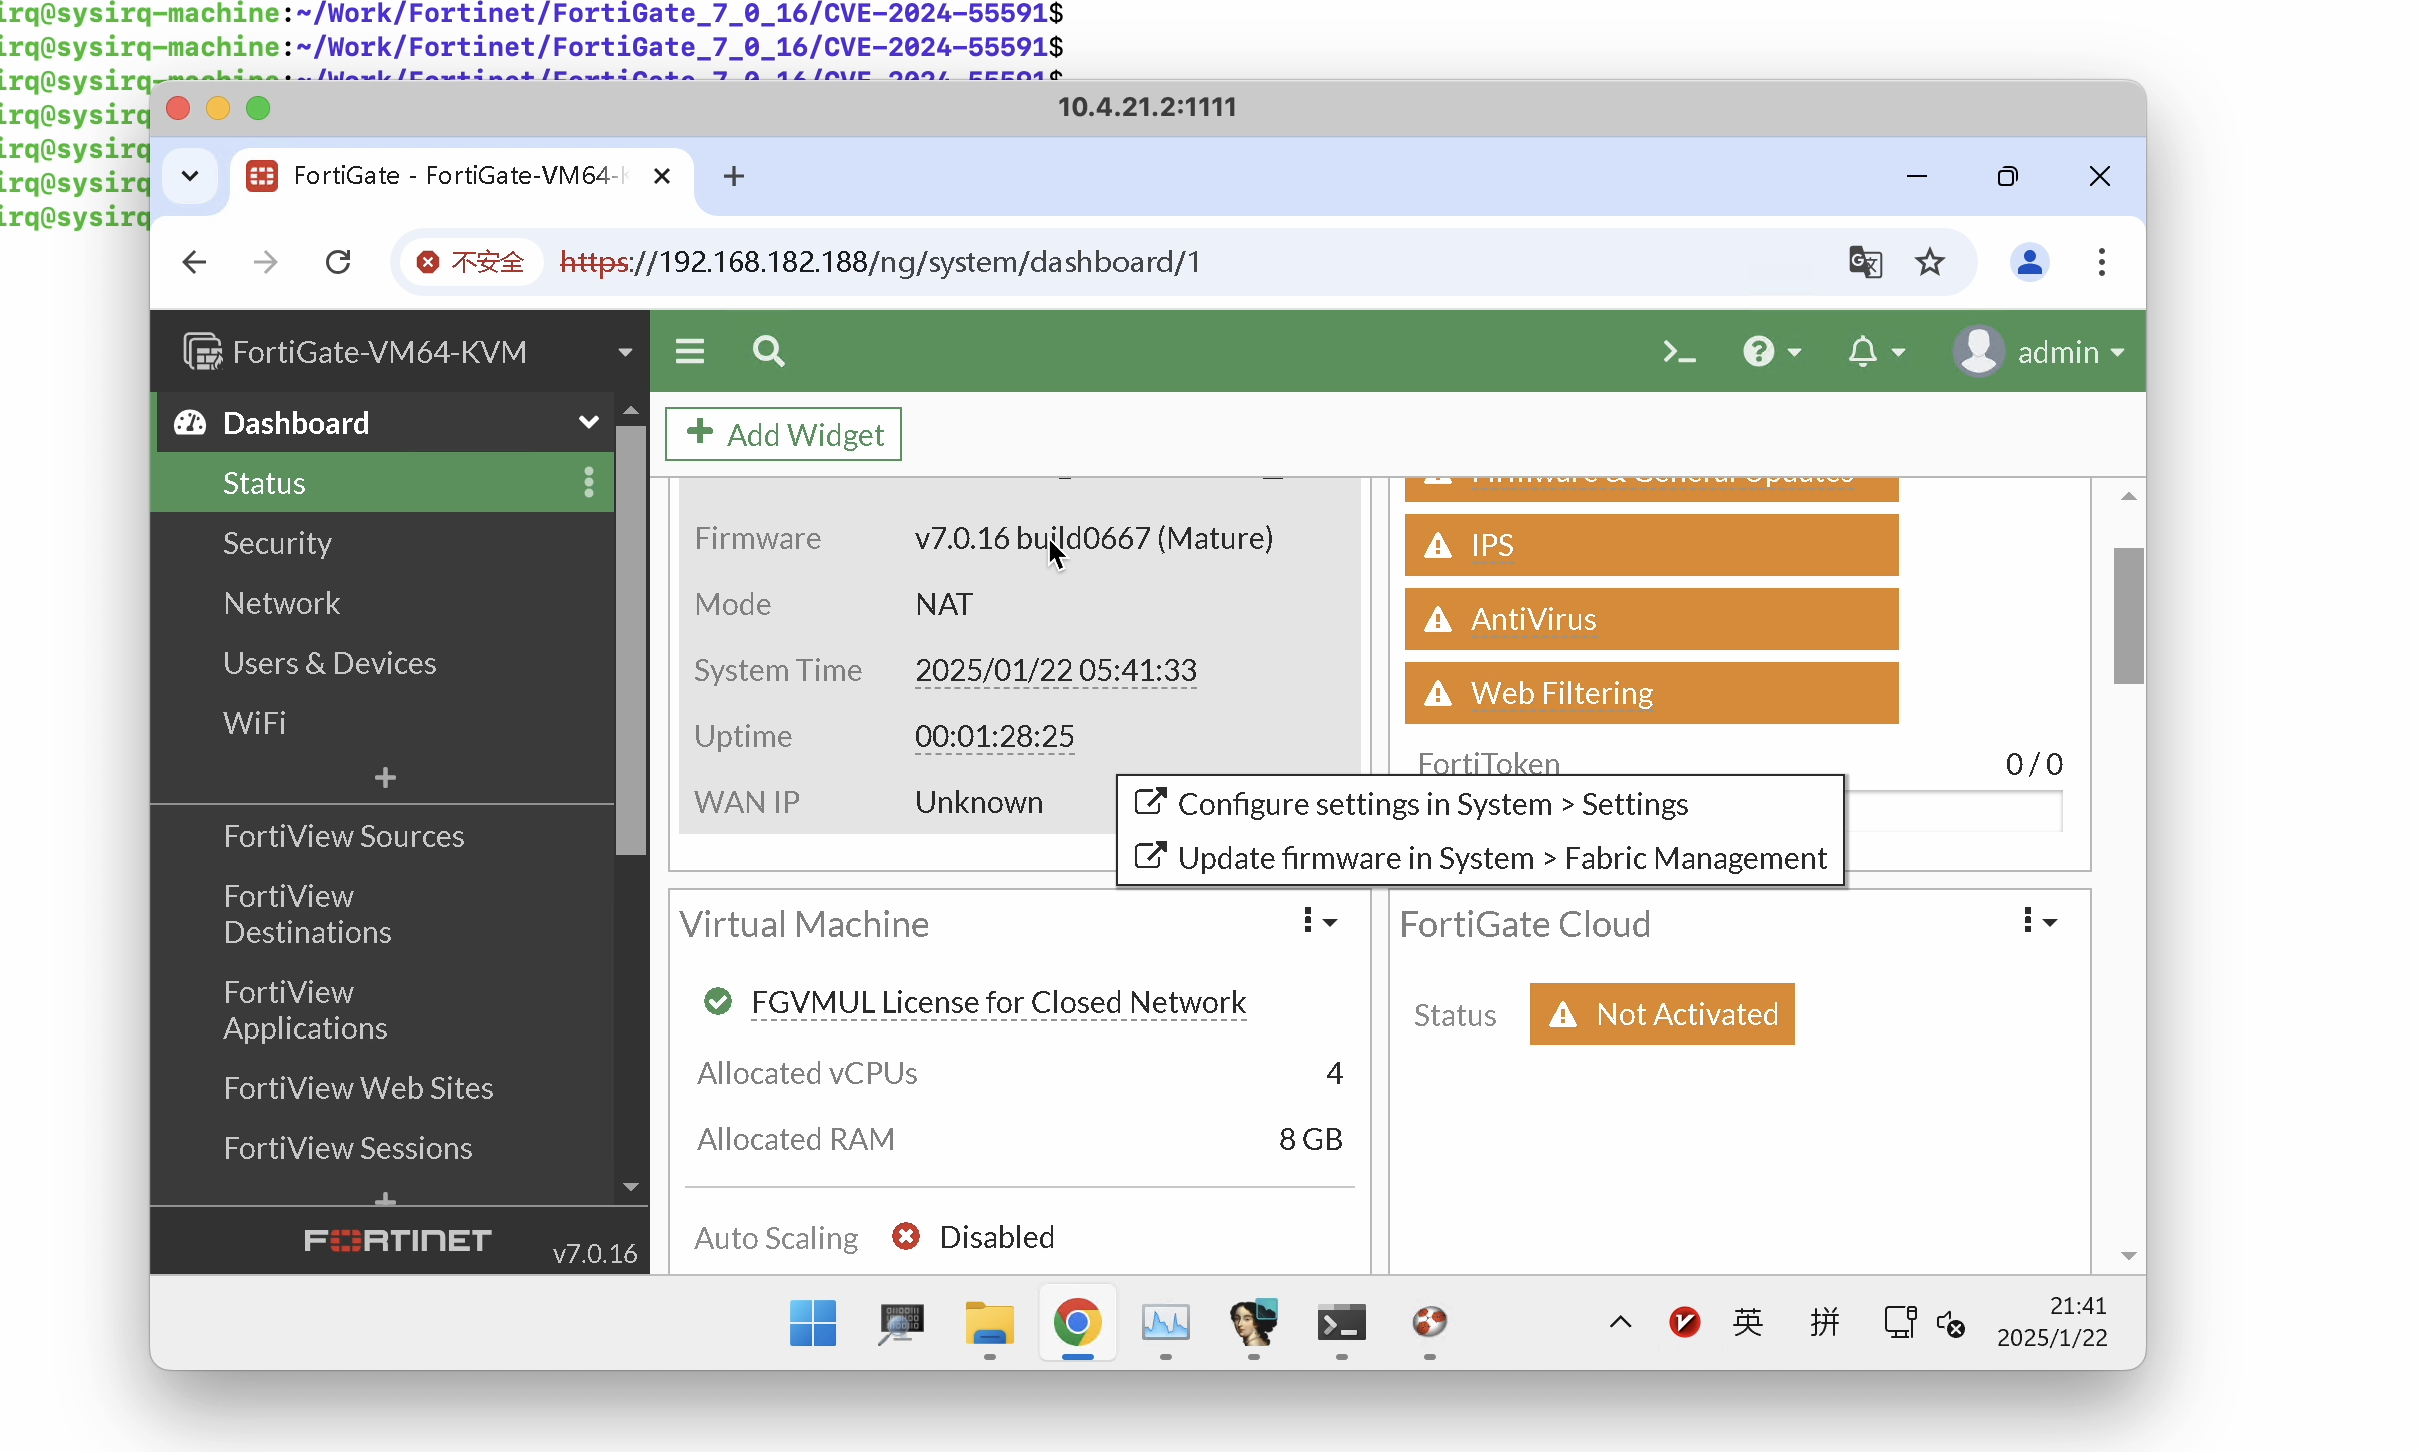
Python exploit for CVE-2024-55591, bypassing FortiOS authentication to execute remote commands on vulnerable FortiGate and FortiProxy devices.

Pre-auth RCE exploit for Craft CMS in Go. Grabs session/CSRF token, poisons PHP session, triggers deserialization for command execution or reverse…

Exploits CVE-2026-39987 pre-auth RCE in Marimo <0.23.0 by connecting to the unauthenticated /terminal/ws WebSocket. Supports arbitrary command…

Admin-only terminal bootstrap routes checked only for login state, which let a normal team member drive Coolify's realtime terminal backend and…

Proof-of-concept exploit for an authentication bypass in marimo's terminal WebSocket endpoint, enabling unauthenticated command execution in versions…