macOS-enterprise-privileges

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…

PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…

A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…

Modifed ver of the original exploit to save some times on password reseting for unprivileged user

WebUI for AAA

This publication is a collection of various common attack scenarios on Microsoft Entra ID (formerly known as Azure Active Directory) and how they can…

Certbot is EFF's tool to obtain certs from Let's Encrypt and (optionally) auto-enable HTTPS on your server. It can also act as a client for any…

CVE-2025-29927 Proof of Concept

Sell bookable services and appointments through WooCommerce -- closes CVE-2026-2931 by construction.

Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.

Lab + writeup for CVE-2026-28699: Gitea OAuth2 scope enforcement bypass via HTTP Basic auth

CVE-2026-23813 — AOS-CX pre-auth bypass via nginx regex. Detection script, bypass demo, config-disclosure PoC, and IDS rules.

Proof-of-concept exploit for CVE-2025-29927 that adds x-middleware-subrequest to bypass Next.js middleware authentication checks.

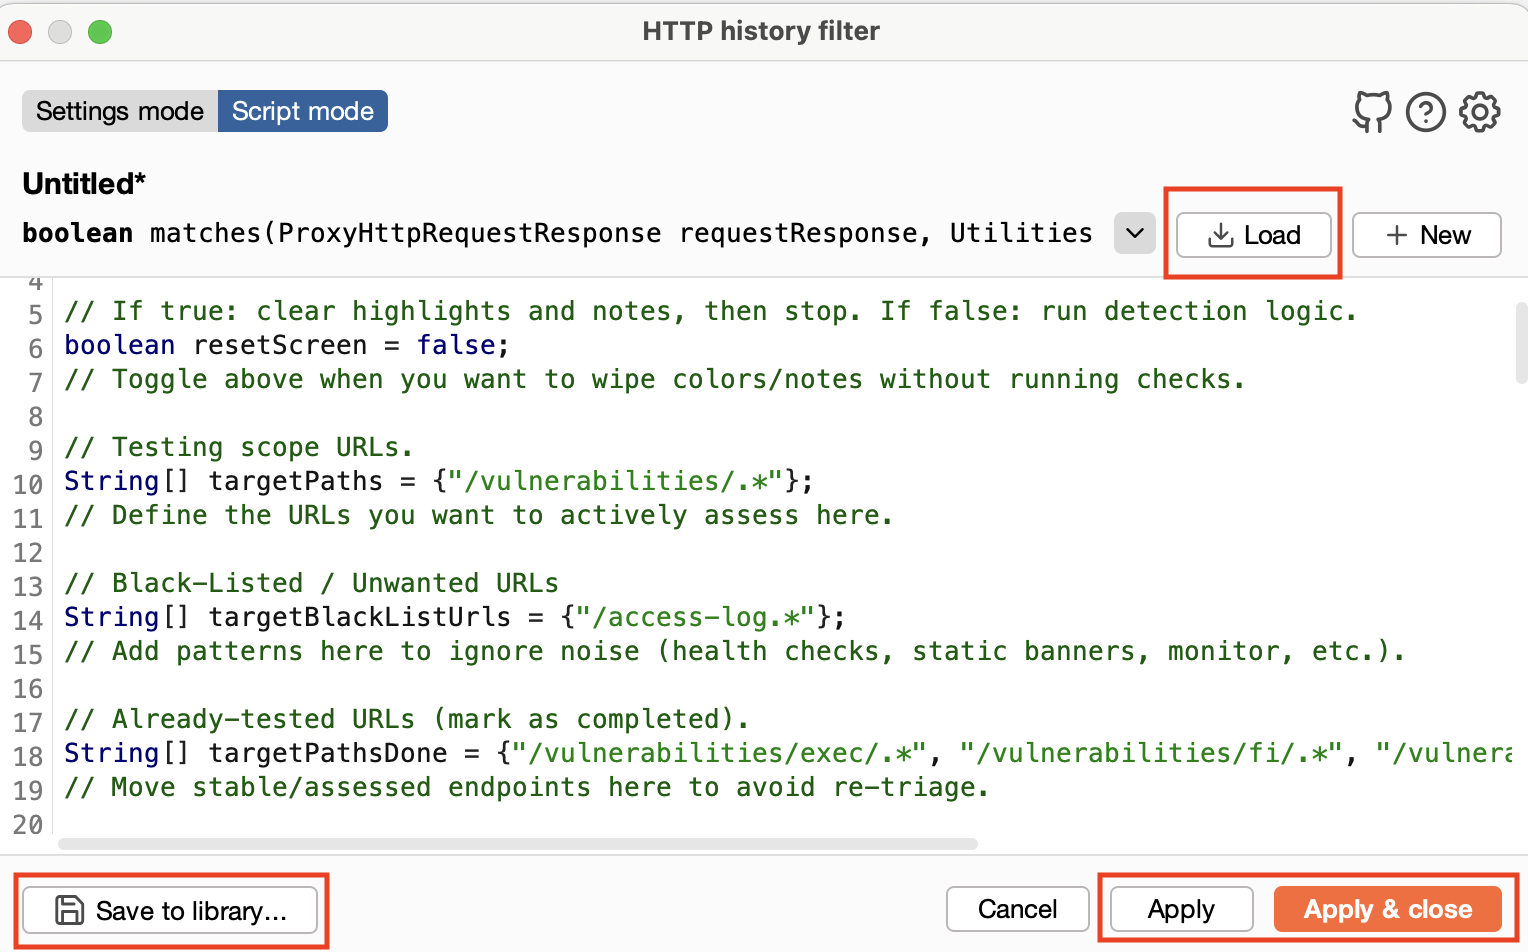
A Burp Suite extension for identifying injection flaws (LFI, RCE, SQLi), authentication/authorization issues, and HTTP 403 access violations. It…

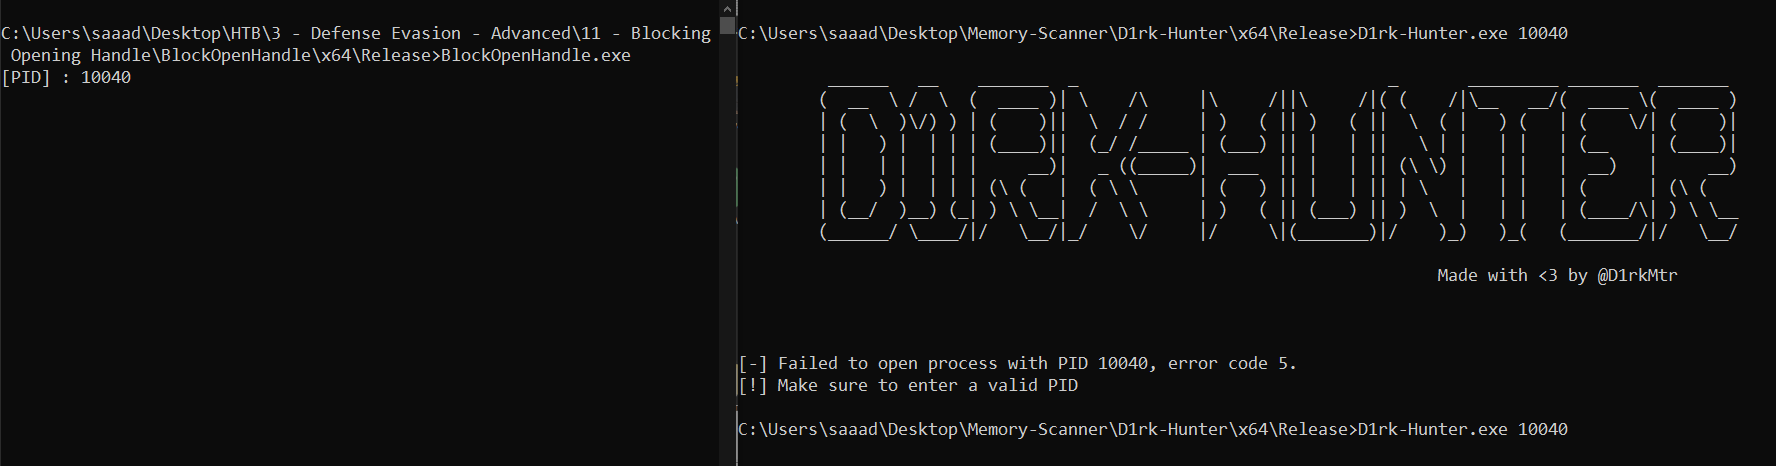
Block any Process to open HANDLE to your process , only SYTEM is allowed to open handle to your process ,with that you can avoid remote memory…

Cryptographically signed delegation receipts for AI agents. Define exactly what an AI can and can't do — signed, verifiable, tamper-proof.

PoC for CVE-2025-29927: Next.js Middleware Bypass Vulnerability. Demonstrates how x-middleware-subrequest can bypass authentication checks. Includes…

Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)