
CVEs
 rhinosecuritylabs/cves
Proof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
authentication-authorizationexploitationpenetration-testing+3
906
rhinosecuritylabs/cvesProof-of-Concept exploits for CVEs found by the team at Rhino Security Labs
 az0x7/vulnerability-checklist
Curated collection of web and API vulnerability checklists covering XSS, SQLi, CSRF, IDOR, authentication bypass, file upload, and bug bounty testing…
 trivulzianus/tarantubench
The full repo of all the labs available as part of the benchmark
 thomaspatzke/burp-sessionauthtool
Burp plugin which supports in finding privilege escalation vulnerabilities
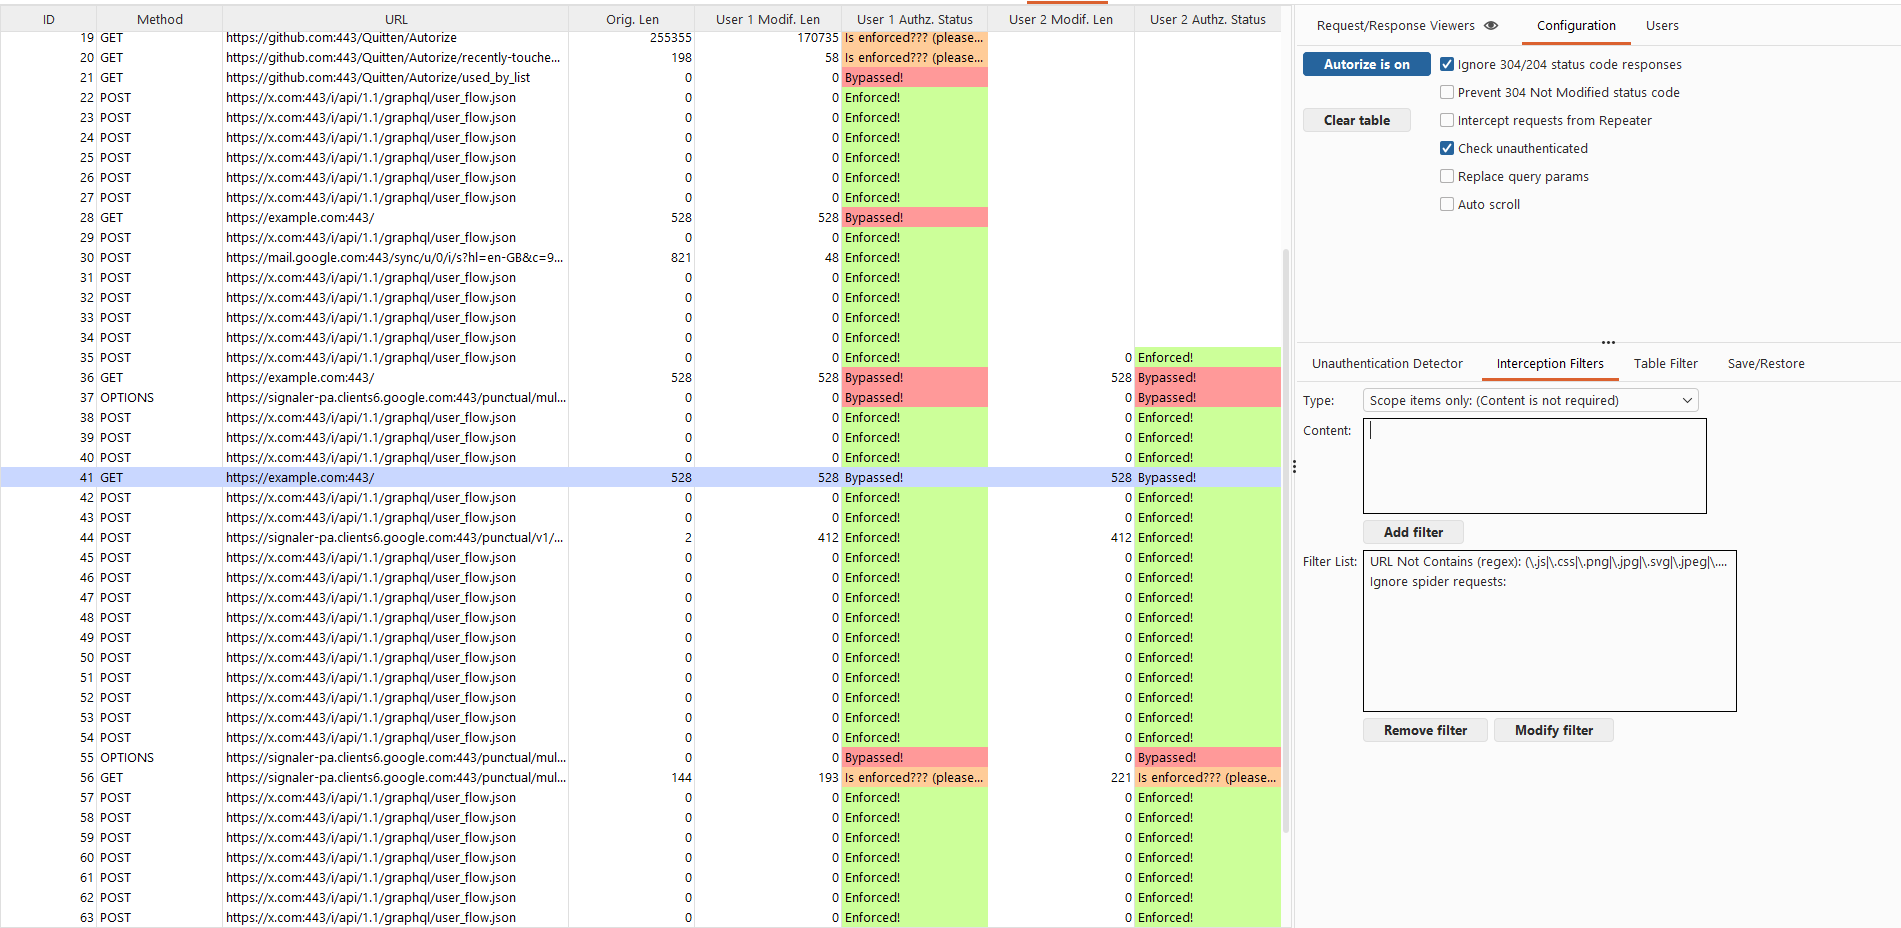 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
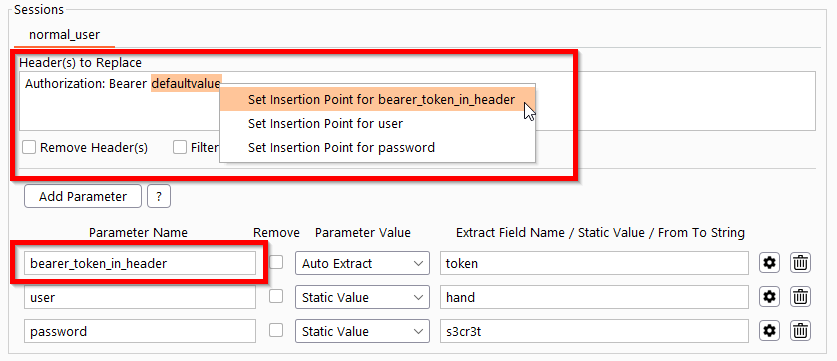 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
 immersive-labs-sec/cve-2025-31161
Proof of Concept for CVE-2025-31161 / CVE-2025-2825
 horizon3ai/secureconnect-auth-bypass
An exploit proof of concept for ConnectWise SecureConnect authentication bypass vulnerability.
 ayantaker/cve-2023-2986
Proof of Concept for vulnerability CVE-2023-2986 in 'Abandoned Cart Lite for WooCommerce' Plugin in WordPress
 himash/cve-2018-19410-poc
Proof of concept for the vulnerability CVE-2018-19410
 orangejuicehu/cve-2024-41958-poc
This is a small proof of concept for CVE-2024-41958
 aj2108/cve-2026-8347
CVE-2026-8347 is an Insecure Direct Object Reference (IDOR) combined with a wrong authorization level vulnerability in Concrete CMS versions 9.5.0…
 sourceincite/cve-2021-24085
Proof-of-concept exploit for CVE-2021-24085: CSRF-based elevation of privilege in Microsoft Exchange Server via msExchEcpCanary token forgery,…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 nastar-id/cve-2026-18315-poc
Proof-of-concept for CVE-2026-18315 (TrueBooker WordPress Plugin): Unauthenticated Authorization Bypass Through User-Controlled Key to Account…
 hunt-benito/siyuan-mcp-admin-takeover-cve-2026-66012-missing-authorization
Unauthenticated administrator takeover exploit for CVE-2026-66012 using MCP missing authorization to exfiltrate credentials and achieve remote code…
 zer0dayf/cve-2026-15013
Exploit for CVE-2026-15013: unauthenticated SAML auth bypass via algorithm confusion. Forges SAML responses to gain admin access and deploy…
 masa42/cve-2024-38821-poc
Proof-of-concept exploit for CVE-2024-38821, demonstrating authentication bypass in Spring Framework via path traversal to access restricted…