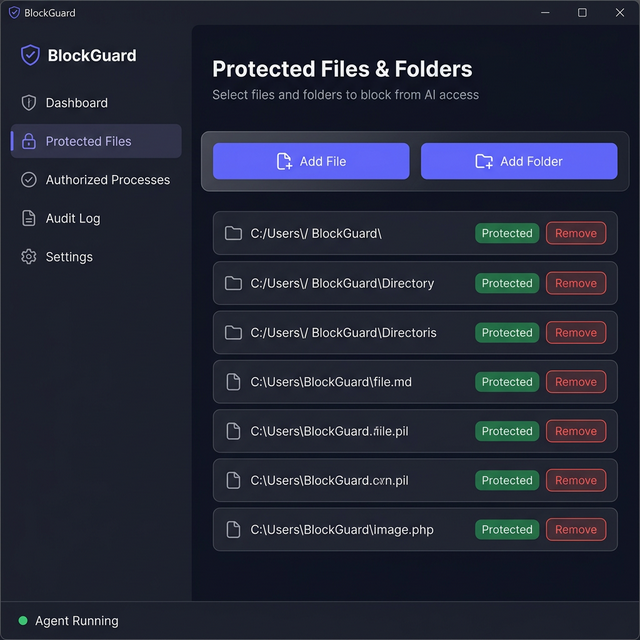
BlockGuard
 m2l33k/blockguard
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
authentication-authorizationconfiguration-auditingdata-exfiltration+4
m2l33k/blockguardBlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 opsifiz/cve-2018-10933
CVE-2018-10933 - LibSSH - Authentication Bypass
 satheesh575555/openssl_1.0.1g_after
Open-source toolkit implementing SSL/TLS protocols and a full-strength cryptography library with encryption, decryption, certificate management, and…
 uthrasri/g2.5_openssl
General-purpose cryptography library and SSL/TLS toolkit providing encryption, decryption, X.509 certificate management, and secure communication…
 trinadh465/openssl-1_0_1g_cve-2015-1792
OpenSSL toolkit implementing SSL/TLS protocols and a general-purpose cryptography library with ciphers, digests, public key algorithms, and X.509…
 pazhanivel07/openssl_1_0_1g_cve-2015-1788
General-purpose cryptography library implementing SSL/TLS protocols, symmetric/ asymmetric ciphers, message digests, and X.509 certificate handling…
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…
 trinadh465/openssl-1_0_1g_cve-2015-1791
OpenSSL 1.0.1g source code with CVE-2015-1791 patch, providing SSL/TLS and cryptographic library for secure communications.
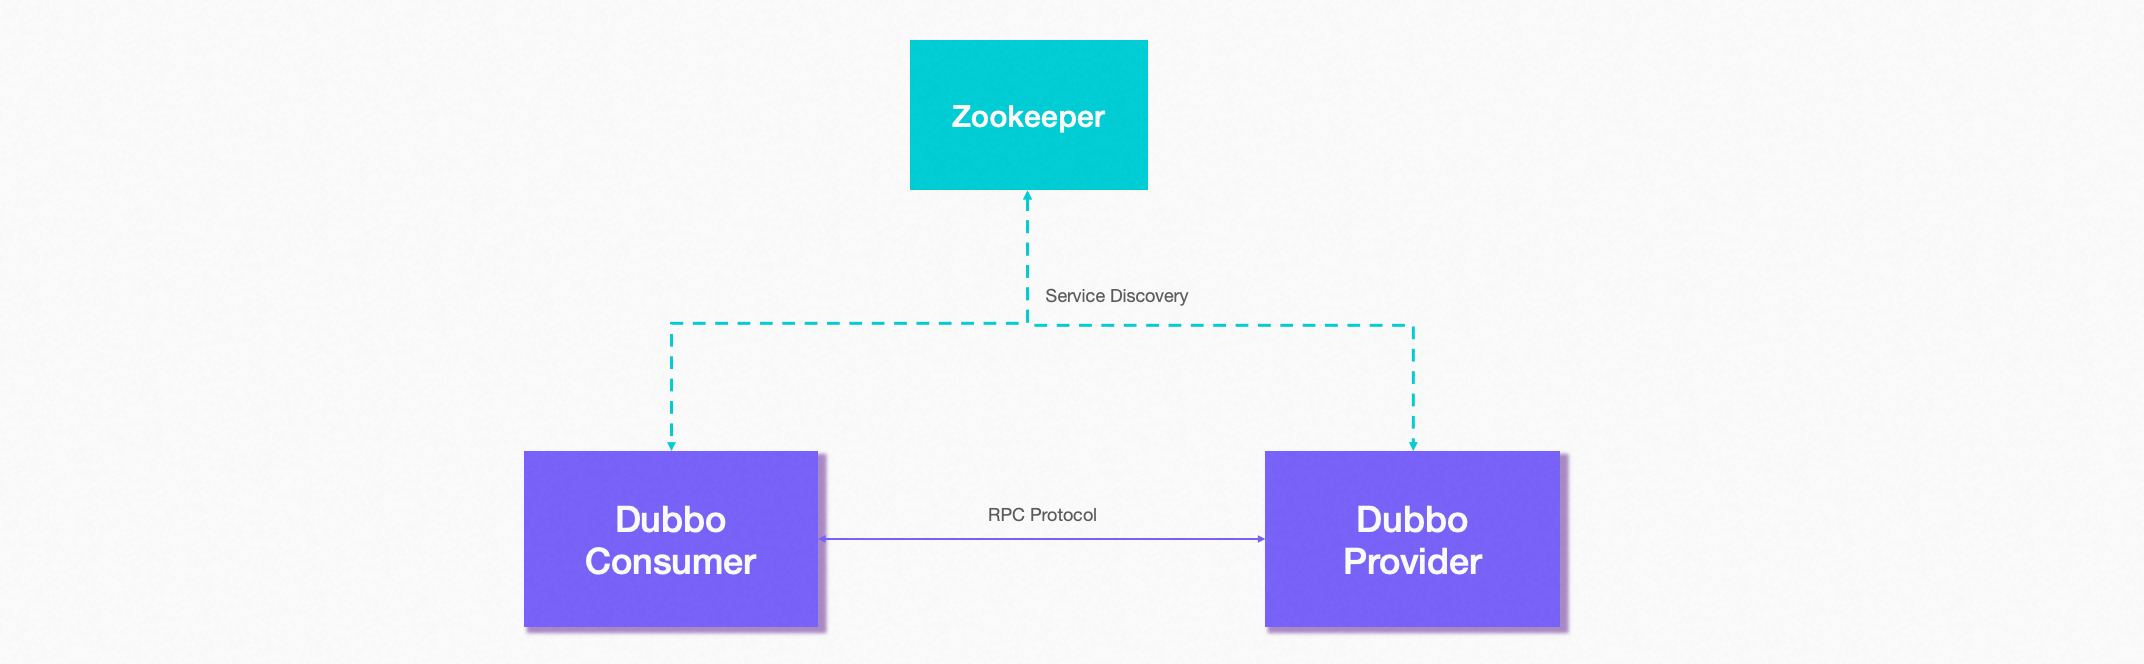 shoucheng3/apache__incubator-dubbo_cve-2021-30181_2-6-8
High-performance Java RPC and microservices framework with service discovery, traffic management, observability, and built-in security for building…
 satheesh575555/openssl_1_1_1_g
Robust toolkit implementing TLS/SSL protocols and a full-strength cryptographic library for encryption, decryption, certificate creation, and secure…
 bongbongco/cve-2012-6066
FreeSSHD Remote Authentication Bypass Vulnerability (freeSSHd 2.1.3)
 shoucheng3/asf__nifi_cve-2023-36542_1-22-0
Automated data flow platform for processing and distributing data with built-in provenance tracking, secure configuration, and scalable pipeline…
 shoucheng3/apache__nifi_cve-2022-33140_1-16-22
Automated data flow processing and distribution system with secure configuration, provenance tracking, and extensible plugin architecture for…
 notitssixtyn3in/cve-2025-4162030
Security advisory detailing a critical authentication vulnerability (CVE-2025-4162030) in Copilot, involving user ID switching that could lead to…