
CVE-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…

While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…

A security-patched fork of the legacy ClickFunnels Classic WordPress plugin. Fixes critical Stored XSS vulnerabilities (CVE-2022-4782) while…

A critical vulnerability in the Intelbras NVD 9032 R Ftd IP CFTV device allows an attacker to bypass the multi-factor authentication during password…

Proof-of-concept exploit for CVE-2025-29927, demonstrating authentication bypass in Next.js middleware via the x-middleware-subrequest header, with…

The goal of Axiom is to provide a completely anonymous, decentralized, and censorship-resistant social media platform. To make this possible, the…

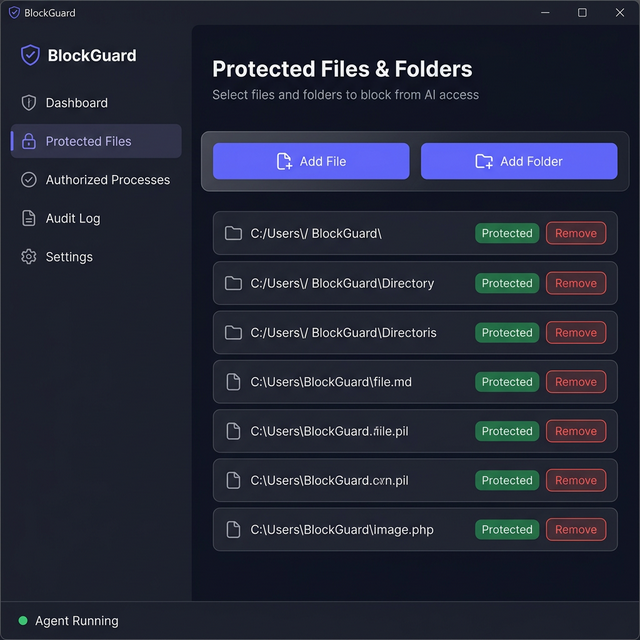
BlockGuard is a Windows Data Loss Prevention (DLP) agent that intercepts and controls file access at the process level. It ensures that only…

PoC of the CVE-2026-29000

Exploit for CVE-2018-0114: re-signs JWT tokens by embedding an attacker-controlled public key in the JWS header, bypassing authentication in…

Password Strength Evaluator is a tool to evaluate the strength of passwords and provide recommendations to improve their security.

Proof-of-concept exploit for CVE-2017-8295, demonstrating unauthorized password reset in WordPress 4.7.4 by intercepting the reset link without prior…

Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…

Demonstrates CVE-2022-31692 Spring Security authorization bypass with a minimal Java exploit, enabling security researchers to test and understand…

A POC for the all new CVE-2023-27524 which allows for authentication bypass and gaining access to the admin dashboard.

Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…

CVE-2025-29927 ~ a poc of the next.js middleware authentication bypass

SQL injection exploit for ABO.CMS 5.8 that bypasses authentication via the tb_login parameter, granting unauthenticated admin panel access. Includes…

PoC for the type confusion vulnerability in Mac's CMS that results in authentication bypass and administrator account takeover.