CVE-2025-9209
 nxploited/cve-2025-9209
RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
authentication-authorizationexploitationinformation-gathering+5
nxploited/cve-2025-9209RestroPress – Online Food Ordering System 3.0.0 - 3.1.9.2 - Unauthenticated Information Exposure to Authentication Bypass via Forged JWT
 dersecure/cve-2024-33676
Technical disclosure of CVE-2024-33676: weak authentication on Enel X JuiceBox EV chargers enabling PII extraction, settings manipulation, and OS…
 blueisbeautiful/cve-2025-54309
CrushFTP AS2 Authentication Bypass
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 randomrobbiebf/wordpress-bf
Brute Force Wordpress Blogs.
 randomrobbiebf/import-users-from-csv-with-meta
Import Users From CSV with Meta 1.15 - Unauthorised Authenticated Users Export
 tam-k592/cve-2024-52316
CVE-2024-52316 - Apache Tomcat Authentication Bypass Vulnerability
 s1lkys/cve-2020-29669
Macally WIFISD2
 geraldoalcantara/cve-2023-49547
Customer Support System 1.0 - SQL Injection Login Bypass
 randomrobbiebf/cve-2024-50477
Stacks Mobile App Builder <= 5.2.3 - Authentication Bypass via Account Takeover
 0xb0y426/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 authentication bypass in PaperCut MF/NG, allowing unauthenticated interaction with vulnerable print…
 c411e/cve-2023-47564
CVE-2023-47564
 theway-hue/cve-2017-5689-checker
Automated checker-exploit for CVE-2017-5689, scanning Intel AMT panels for authentication bypass and reporting vulnerable IPs.
 b0marek/cve-2023-4800
Repository for CVE-2023-4800 vulnerability.
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
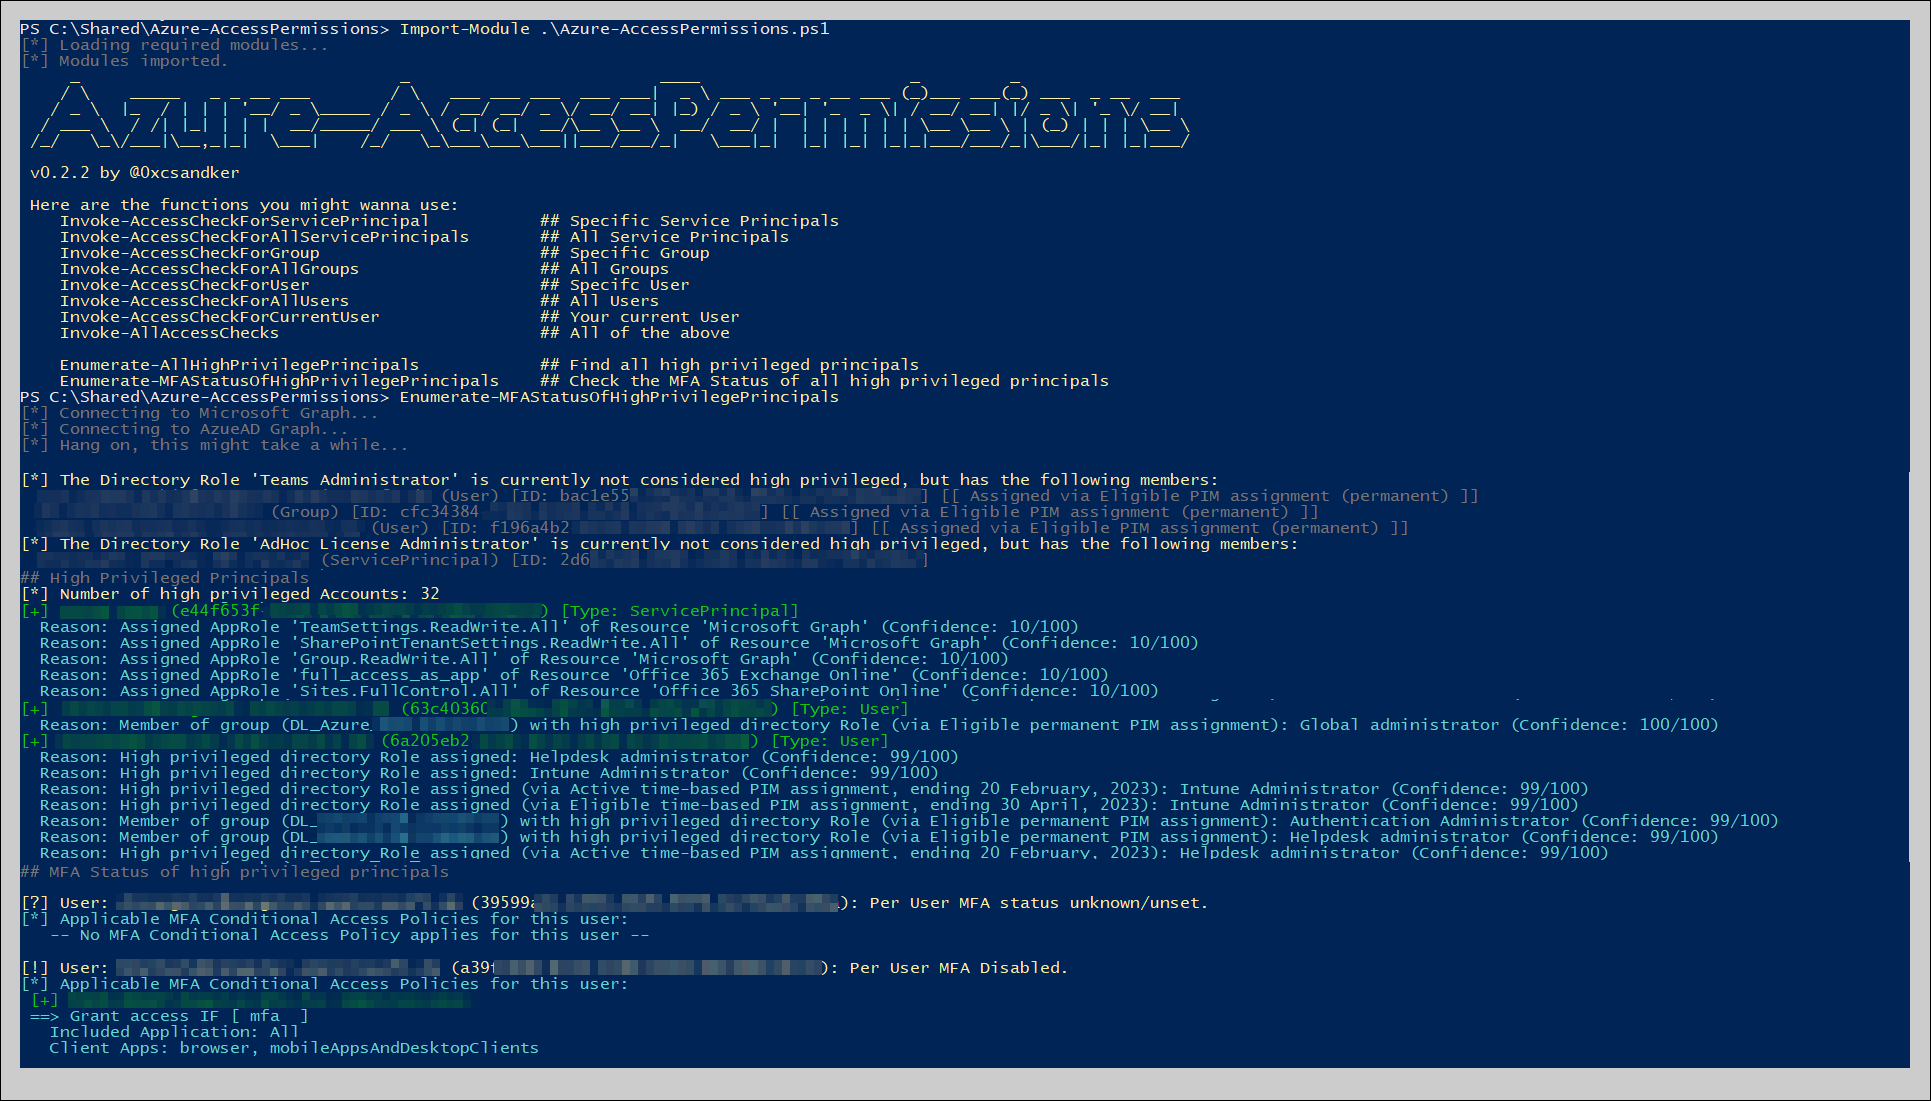 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…