
CVE-2024-55211
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
authentication-authorizationdns-analysisexploitation+3
2
micaelmaciel/cve-2024-55211Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 0xrixet/craftcms-poc-cve-2026-31266
Security research on Craft CMS authentication mechanism
 randomrobbiebf/cve-2024-9821
Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass
 rubbxalc/cve-2025-29927
Functional exploit for CVE-2025-29927, a critical Next.js middleware authorization bypass. Sends crafted HTTP requests with the…
 simoesctt/sctt-2026-33-0004-forticloud-sso-identity-singularity
While Fortinet's January 27, 2026 mitigation for **CVE-2026-24858** focuses on blocking specific accounts like `[email protected]`, it fails to…
 lequoca/fortinet-fortiweb-cve-2025-64446-58034
Security research on Fortinet FortiWeb vulnerabilities (CVE-2025-64446, CVE-2025-58034)
 aliyabuz25/cve-2025-49173
Security research — PoC for local root privilege escalation on macOS Mavericks 10.9.
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 royall-researchers/cve-2023-27350
Papercut Vulnerability, Affected Versions are PaperCut MF or NG version 8.0 or later (excluding patched versions) on all OS platforms.
 jayngng/cve-2021-22911
Modifed ver of the original exploit to save some times on password reseting for unprivileged user
 mrash/fwknop
Single Packet Authorization > Port Knocking
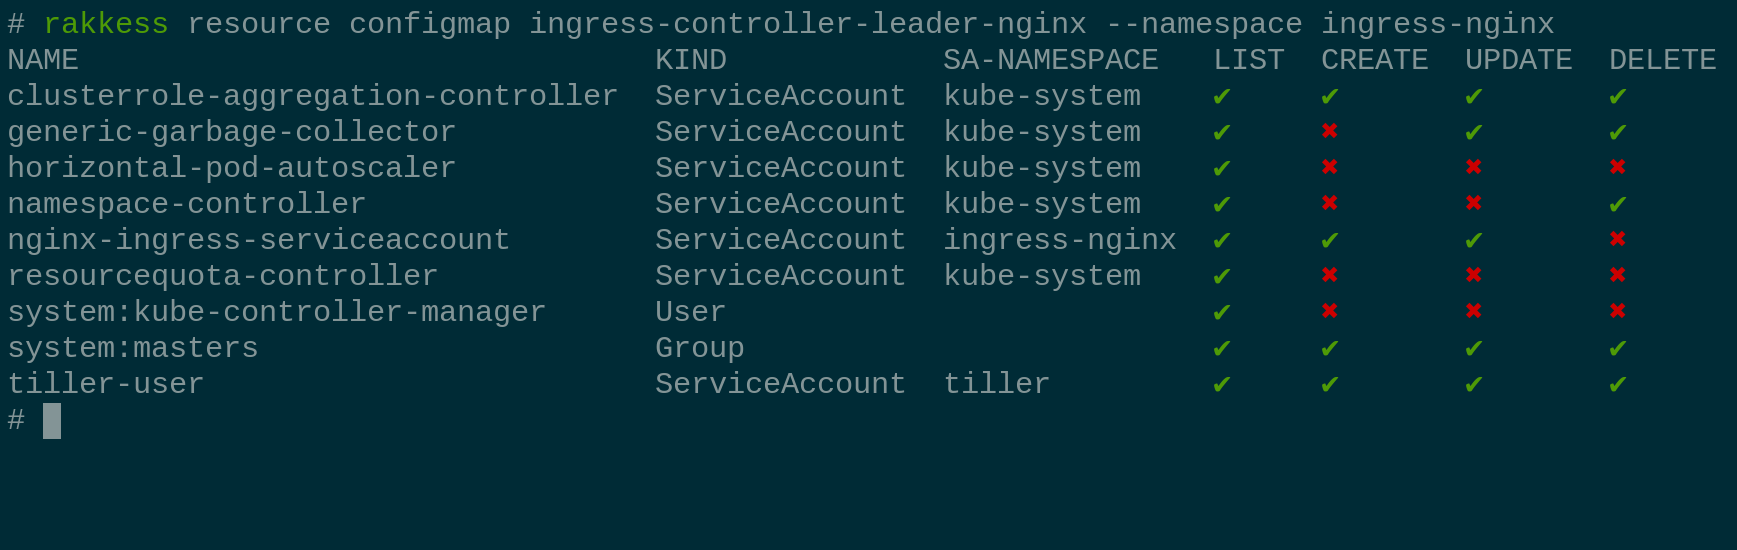 corneliusweig/rakkess
Review Access - kubectl plugin to show an access matrix for k8s server resources
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 agberohq/keeper
Simple Secure Keeper for Secrets
 l0ading-x/cve-2022-23131
cve-2022-23131
 qarait/ephemera
Zero-Trust SSH CA
 nxploited/cve-2025-3102
Wordpress SureTriggers <= 1.0.78 - Authorization Bypass due to Missing Empty Value Check to Unauthenticated Administrative User Creation
 ignis-sec/cve-2019-10008
ManageEngine Service Desk Plus 10.0 Privilaged account Hijacking