
CVE-2025-54309
 blueisbeautiful/cve-2025-54309
CrushFTP AS2 Authentication Bypass
authentication-authorizationexploitationinformation-gathering+3
blueisbeautiful/cve-2025-54309CrushFTP AS2 Authentication Bypass
 aksalsalimi/cve-2026-26418
Documentation of CVE-2026-26418, a missing authentication and authorization vulnerability in TCS Cognix Recon Client v3.0 Web API, including affected…
 0xdtc/crushftp-auth-bypass-cve-2025-31161
Exploit for CrushFTP CVE-2025-31161 auth bypass: detects vulnerable targets, enumerates users, and creates unauthorized admin accounts through…
 randomrobbiebf/wordpress-bf
Brute Force Wordpress Blogs.
 randomrobbiebf/import-users-from-csv-with-meta
Import Users From CSV with Meta 1.15 - Unauthorised Authenticated Users Export
 tam-k592/cve-2024-52316
CVE-2024-52316 - Apache Tomcat Authentication Bypass Vulnerability
 s1lkys/cve-2020-29669
Macally WIFISD2
 geraldoalcantara/cve-2023-49547
Customer Support System 1.0 - SQL Injection Login Bypass
 randomrobbiebf/cve-2024-50477
Stacks Mobile App Builder <= 5.2.3 - Authentication Bypass via Account Takeover
 0xb0y426/cve-2023-27350-poc
Proof-of-concept exploit for CVE-2023-27350 authentication bypass in PaperCut MF/NG, allowing unauthenticated interaction with vulnerable print…
 c411e/cve-2023-47564
CVE-2023-47564
 b0marek/cve-2023-4800
Repository for CVE-2023-4800 vulnerability.
 theway-hue/cve-2017-5689-checker
Automated checker-exploit for CVE-2017-5689, scanning Intel AMT panels for authentication bypass and reporting vulnerable IPs.
 haidang-infosec/phantom-grid
An eBPF-powered Active Defense system that turns your Linux server into a deceptive honeypot. Features transparent traffic redirection, OS…
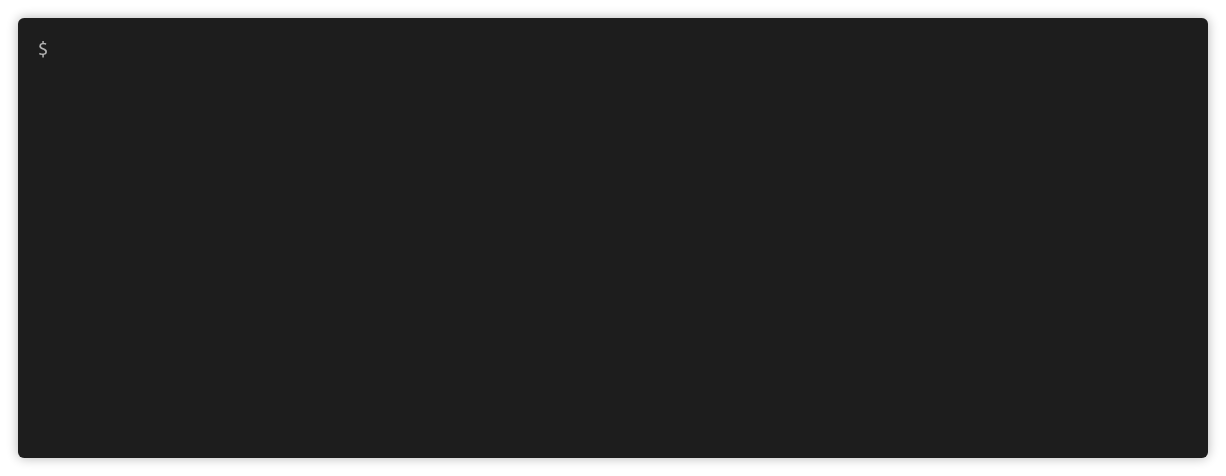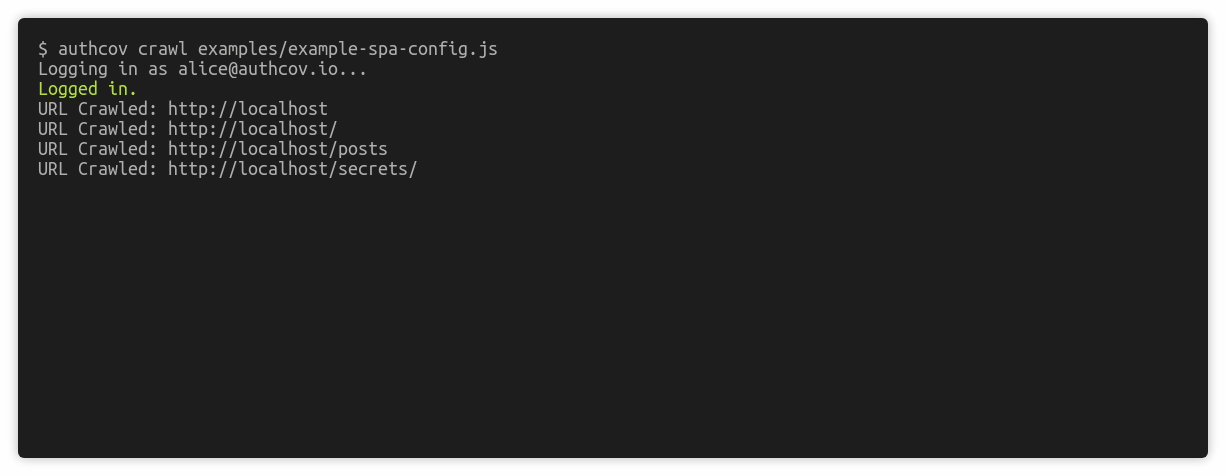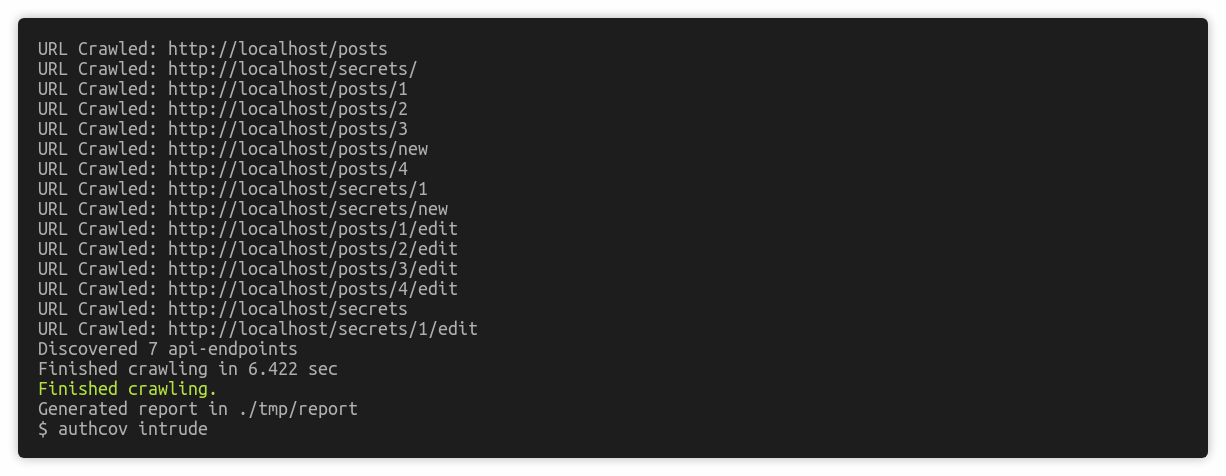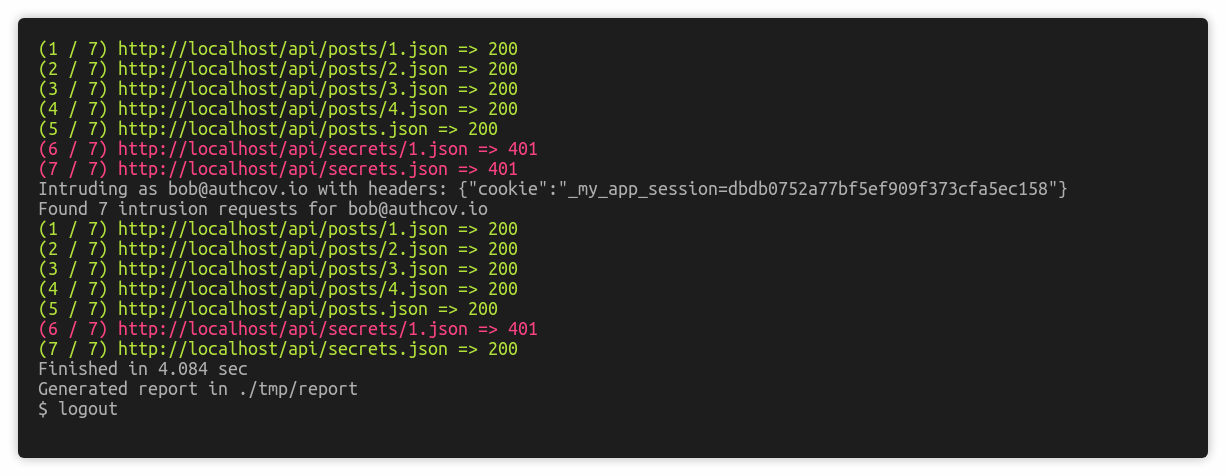 authcov/authcov
Web app authorisation coverage scanning
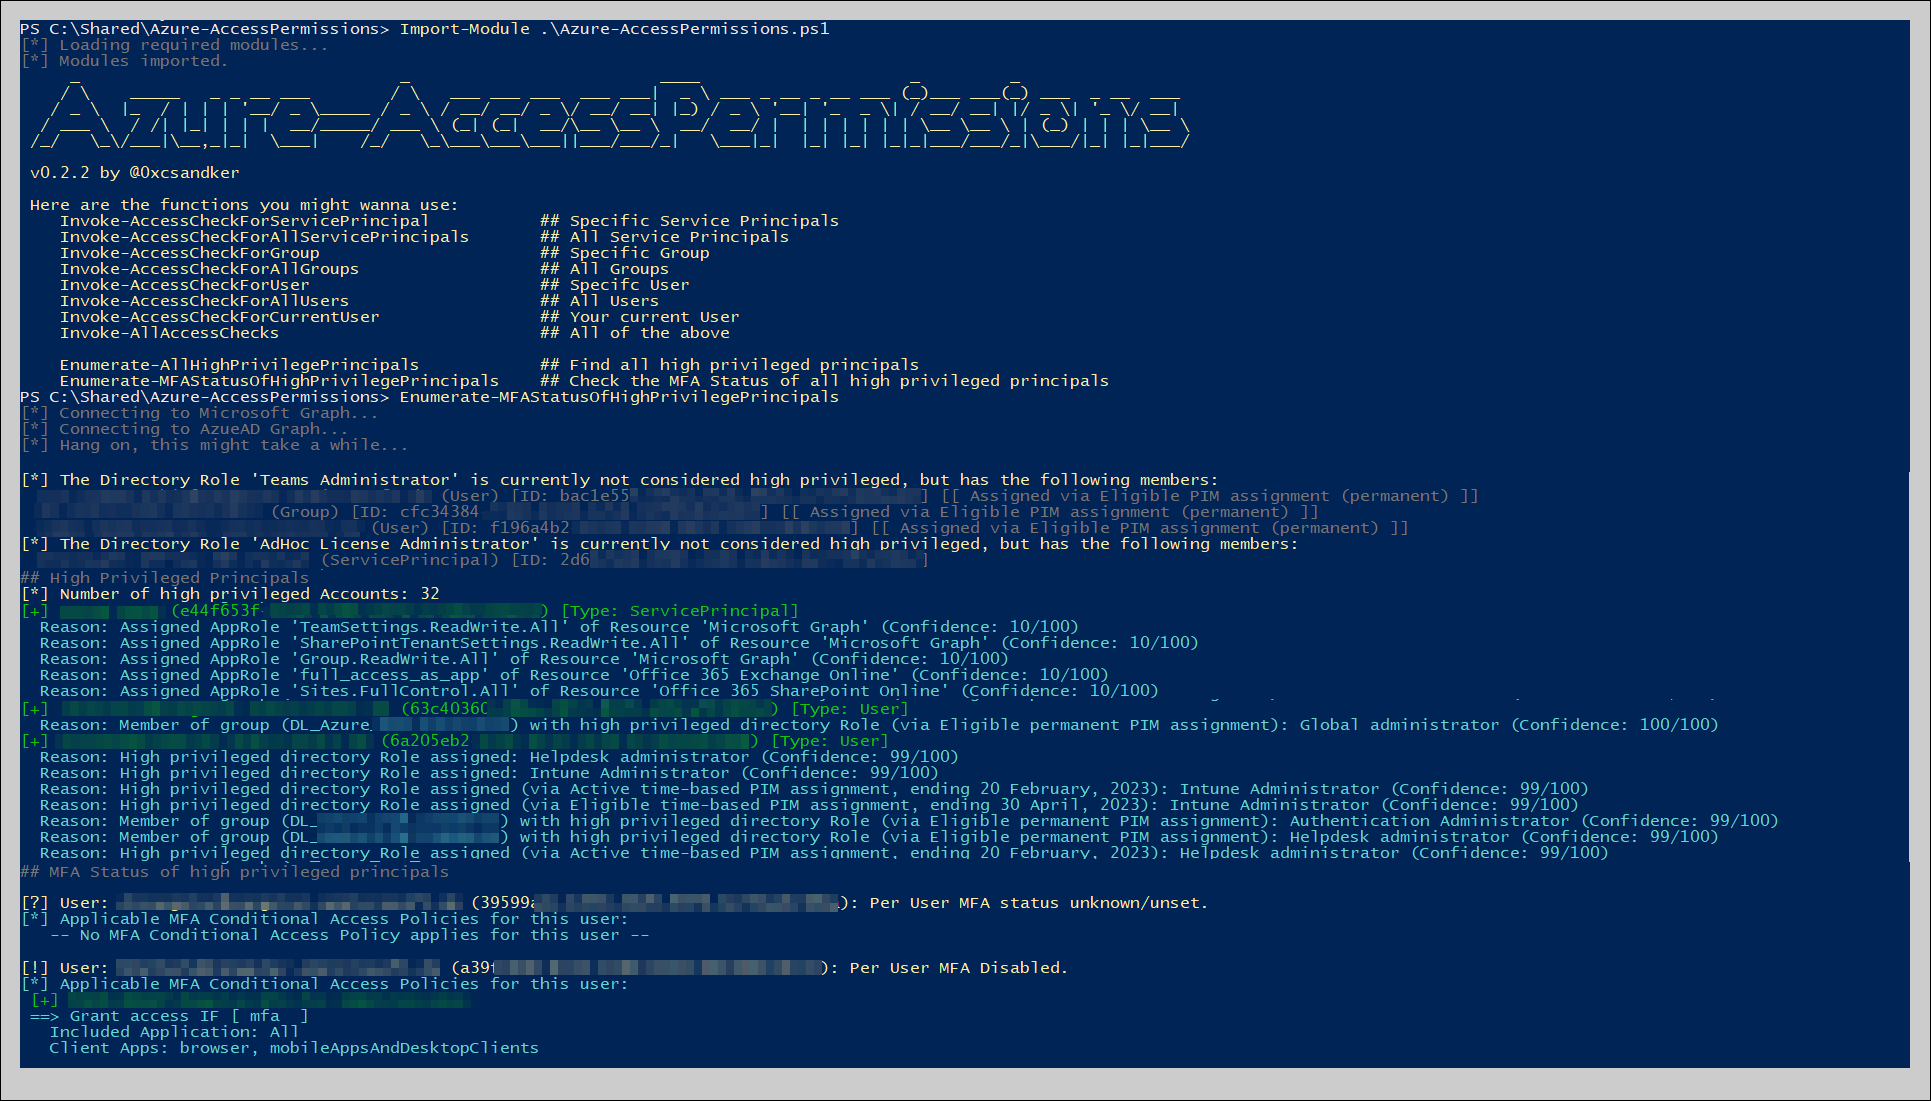 csandker/azure-accesspermissions
PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…
 mandiant/adfsdump
Dumps AD FS signing keys, token certificates, and relying-party configuration, enabling forged federated authentication tokens for red-team…
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection