ff4j__ff4j_CVE-2022-44262_1-8-13

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

Feature toggle framework for Java enabling runtime feature activation, role-based access, AOP-driven toggling, monitoring, audit trails, and a web…

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

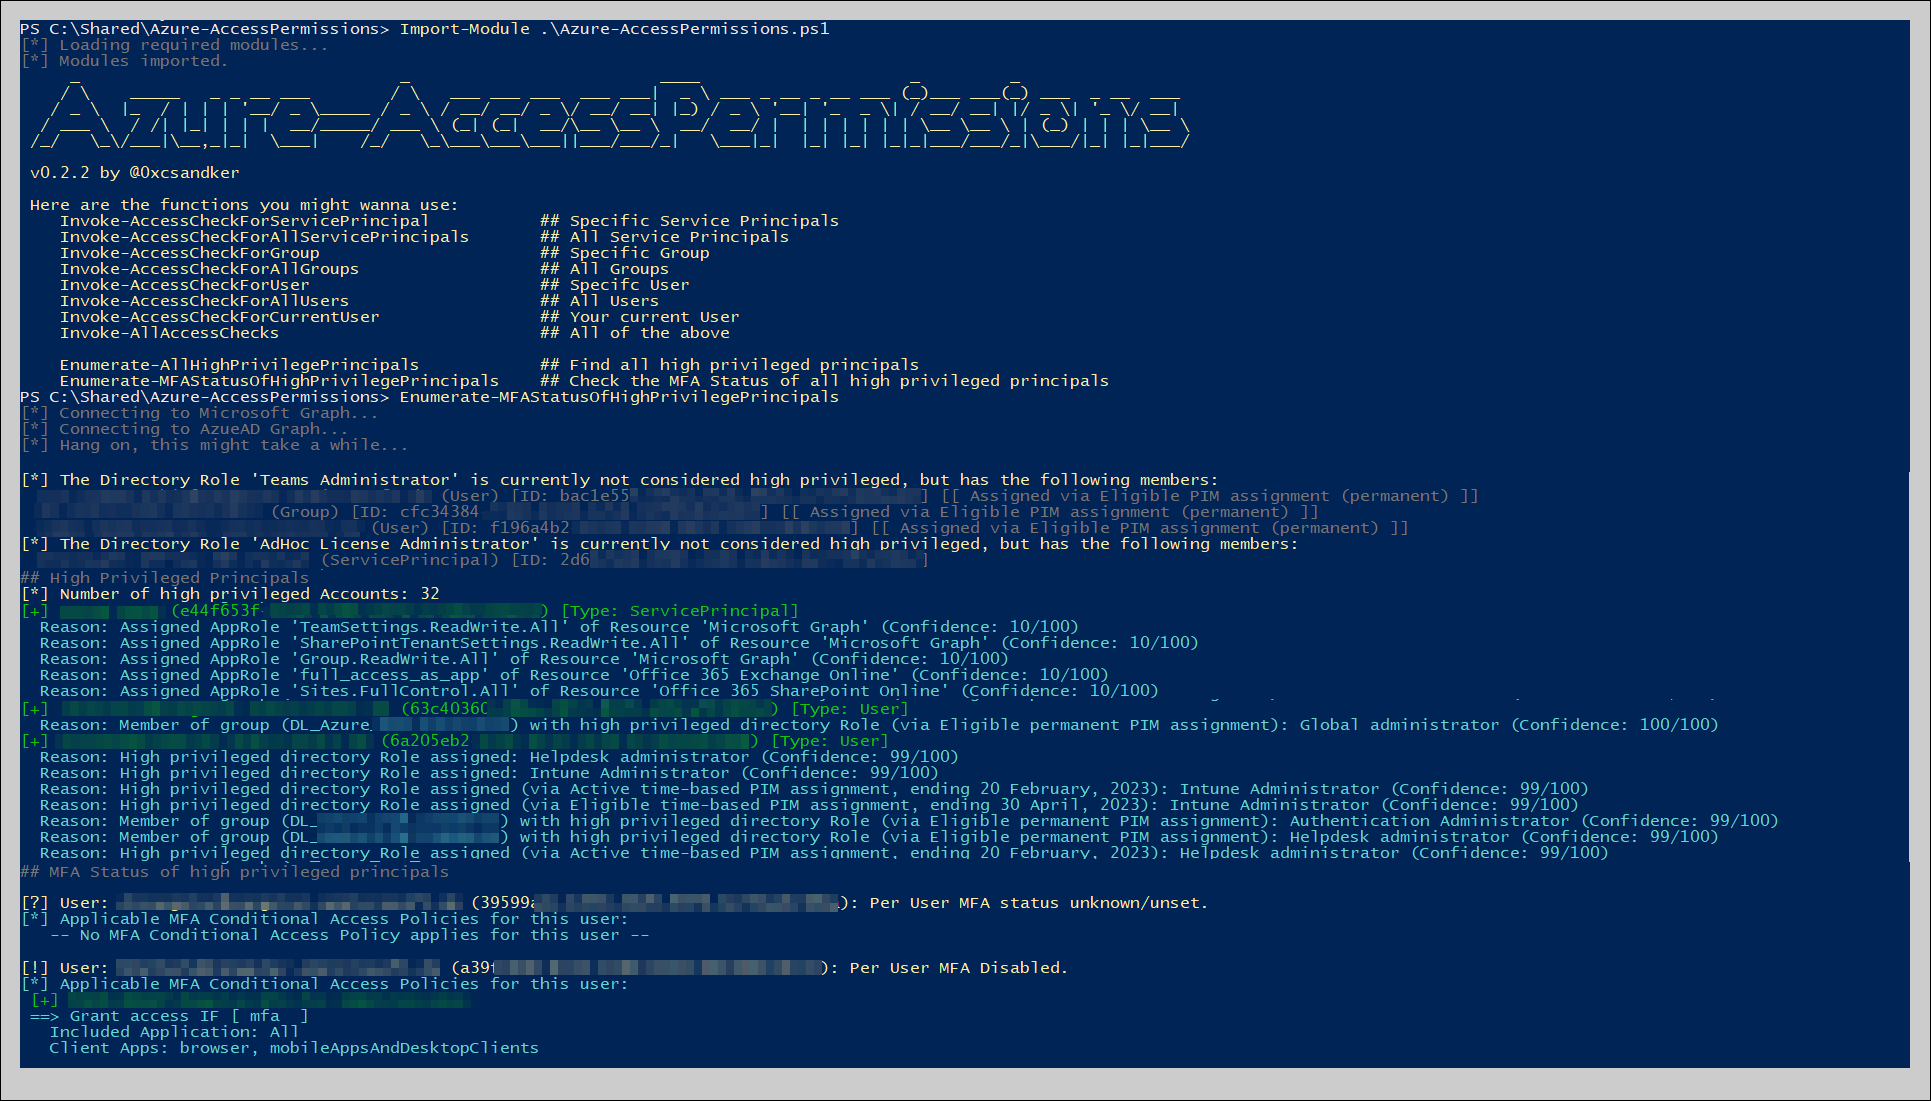
Audit program for AzureAD

Enumerate the permissions associated with AWS credential set

Synapse: Matrix homeserver written in Python/Twisted.

Identity services for traditional infrastructure, applications and containers.

LLM-backed AI agent security — inbound injection detection + outbound privacy protection

Workaround guide for CVE-2022-41923 privilege management vulnerability in Grails Spring Security Core plugin, providing patched filter definitions…

PowerShell script to enumerate Azure Active Directory access permissions, including role assignments, service principals, and privileged access…

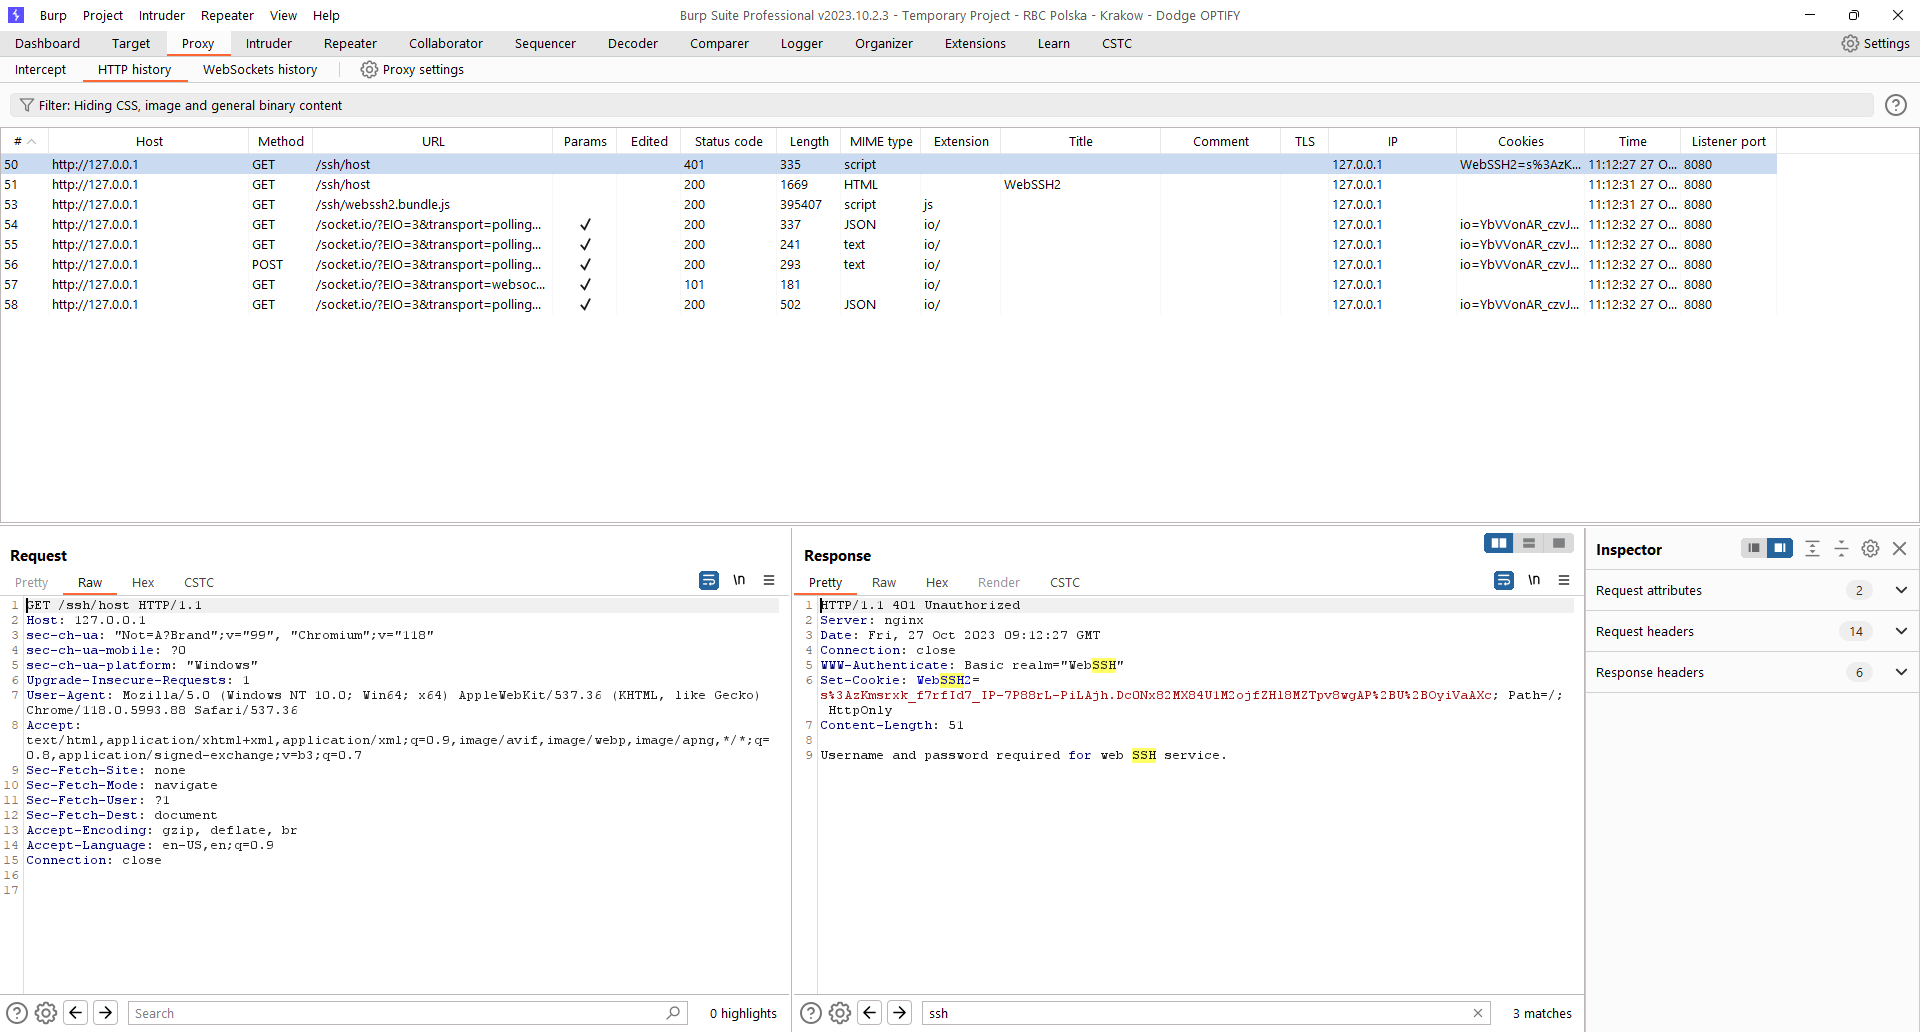
Repository contains description for CVE-2023-35794 discovered by Dodge Industrial Team for Dodge OPTIFY platfrom.

Burp plugin which supports in finding privilege escalation vulnerabilities

Session-scoped TOTP rate limiting permits repeated verification attempts

Non-destructive Go verifier that checks whether a Camaleon CMS instance applies the authorization fix for CVE-2026-102261 in the media crop endpoint.

Python exploit for CVE-2026-16764, a privilege escalation in OWASP DefectDojo where an is_staff REST API bypass lets a low-privileged user gain…

Ruby library implementing the SAML Service Provider side of SSO, handling authn requests, response validation, XML signature checks, and IdP metadata…

Advisory for CVE-2026-18783: missing server-side authentication on TREX MES /api/GetDataJSON3 allows unauthenticated data queries and arbitrary SQL…

Sanitized report and local proof-of-concept script demonstrating the MediaWiki action=emailuser API EmailUserAuthorizeSend hook bypass…

Sanitized report and local proof-of-concept script for CVE-2026-102975, a MediaWiki RevisionDelete API authorization bypass allowing suppression…