
CVE-2026-45156-POC
 cybertechajju/cve-2026-45156-poc
This repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
authentication-authorizationexploitationpenetration-testing+3
2
cybertechajju/cve-2026-45156-pocThis repository contains the Proof of Concept (PoC) exploit script for CVE-2026-45156
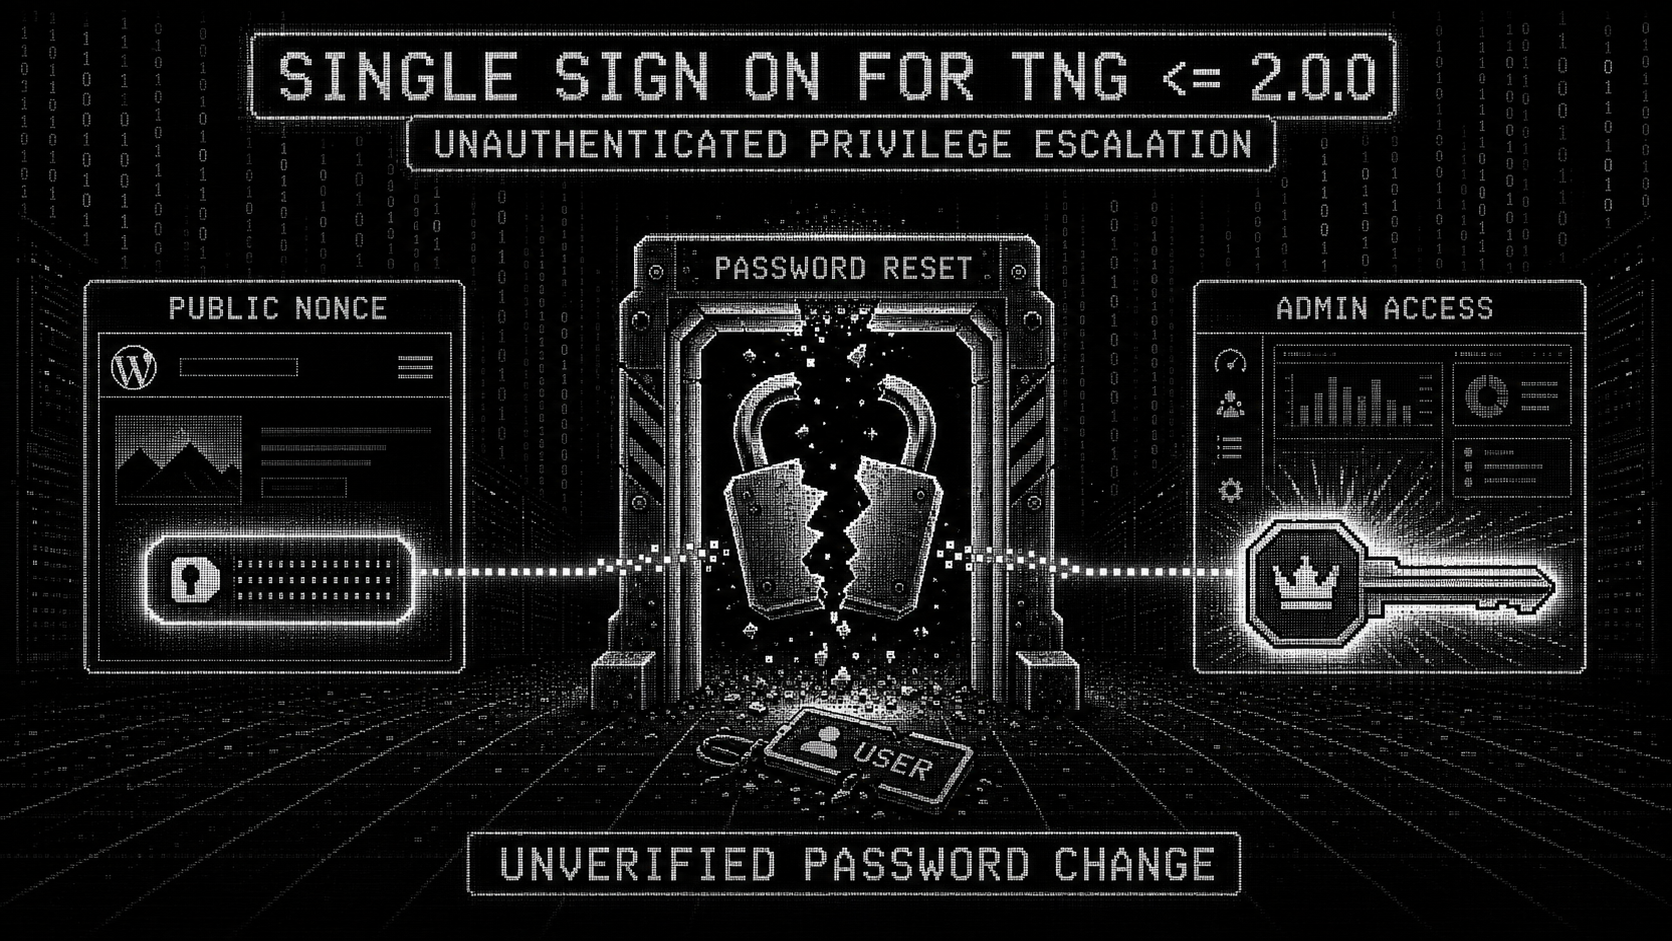 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 digicred-oss/caos-os
Customer Assurance Operating System. Answer the security questionnaires your customers send you, once.
 micaelmaciel/cve-2024-55211
Cookie-based authentication vulnerability on Tk-Rt-Wr135G
 rubikcuv5/cve-2018-10933
libSSH-Authentication-Bypass
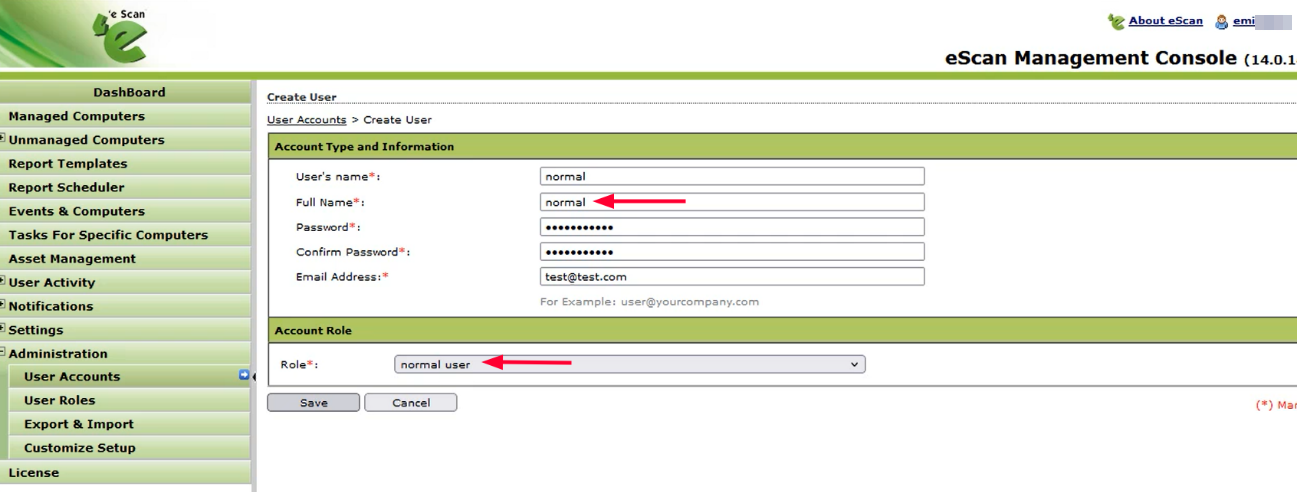 sahiloj/cve-2023-33730
eScan Management Console version 14.0.1400.2281 contains privilege escalation via `GetUserCurrentPwd` function lets attackers retrieve any user's…
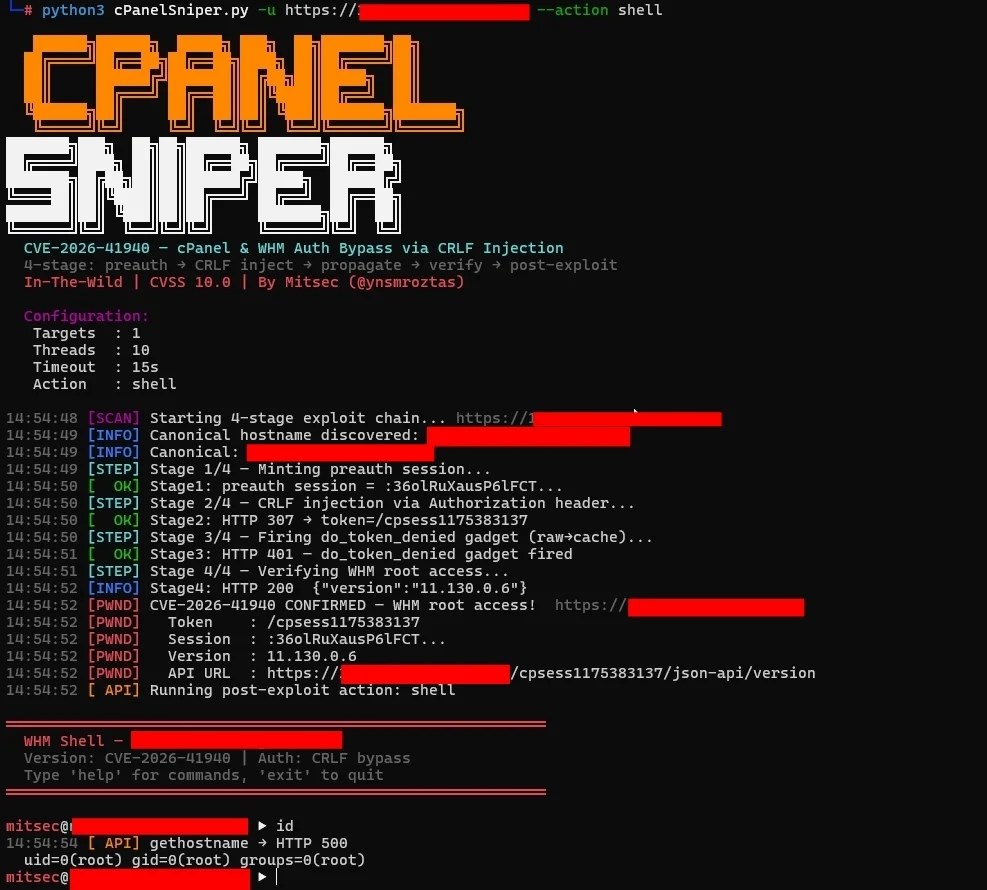 zwanski2019/cpanelsniper
CVE-2026-41940 — cPanel & WHM Authentication Bypass via Session-File CRLF Injection
 ha5ant/silverpeas-authbypass-cve-2024-36042
Python PoC for CVE-2024-36042 authentication bypass in Silverpeas < 6.3.5. Features version detection, multi-threaded user enumeration, message…
 nxploited/cve-2025-49901
WordPress Simple Link Directory Plugin < 14.8.1 is vulnerable to a high priority Broken Authentication
 ex-cal1bur/cve-2026-44595
# CVE-2026-44595 YAMCS Unauthorized User Enumeration via IAM API
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
 xthalach/cve-2024-11318
This repository details an IDOR vulnerability in AbsysNet 2.3.1, which allows a remote attacker to brute-force session IDs via the /cgi-bin/ocap/…
 trqt/cve-2024-48322
Exploit for CVE-2024-48322 targeting RunCodes instances. Retrieves user passwords via email inbox after authentication bypass, requiring only any…
 randomrobbiebf/cve-2024-9821
Bot for Telegram on WooCommerce <= 1.2.4 - Authenticated (Subscriber+) Telegram Bot Token Disclosure to Authentication Bypass
 randomrobbiebf/cve-2024-9106
Wechat Social login <= 1.3.0 - Authentication Bypass
 jenderal92/owa-valid-login-checker
Owa Valid Login Checker
 fevar54/blackash-cve-2025-20343
Technical documentation and proof-of-concept for CVE-2025-20343, a high-severity denial-of-service vulnerability in Cisco ISE allowing…
 mrpayloadc/cve-2025-0316-exploit
Automated auth bypass exploit for CVE-2025-0316 targeting WordPress WP Directorybox Manager. Features user enumeration, proxy support,…