

Kangaroo
 monkeysec-sys/kangaroo
Authentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
authentication-authorizationeducationexploitation+3
2
monkeysec-sys/kangarooAuthentication bypass exploit for CVE-2026-32746 targeting legacy Telnet servers, with defensive guidance and Go-based implementation for authorized…
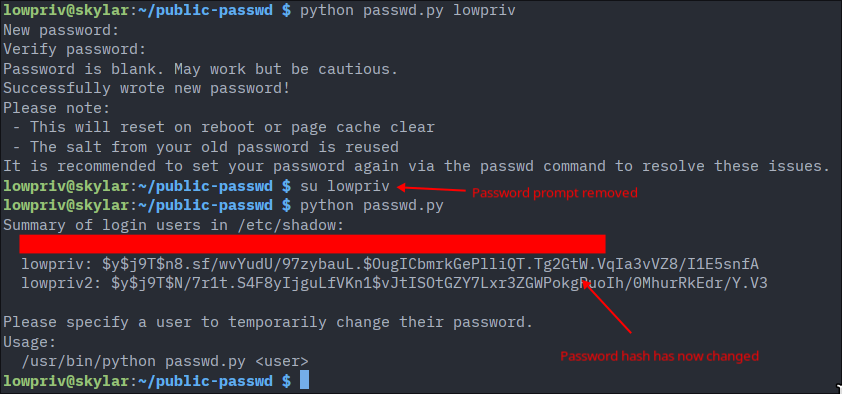 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 a17-ba/cve-2026-51119
Technical analysis and advisory for CVE-2026-51119, a privilege escalation in Invixium IXM WEB allowing authenticated low-privilege users to create…
 ilhomjonr/cve-2026-71518
Advisory and PoC for an unauthenticated authorization bypass in Typemill media downloads, using path-equivalent URL variants to access…
 bogdanrotariu/cve-2026-29204-whmcs-clientarea-addonid
Provides community notes and an optional temporary hook to guard against CVE-2026-29204, a WHMCS client area addonId ownership vulnerability, with…
 tanarchytan/cve-2021-1675
Fix without disabling Print Spooler
 sap/macos-enterprise-privileges
This application gives Mac users in enterprise environments control over the administration of their machines by elevating their access level to…
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
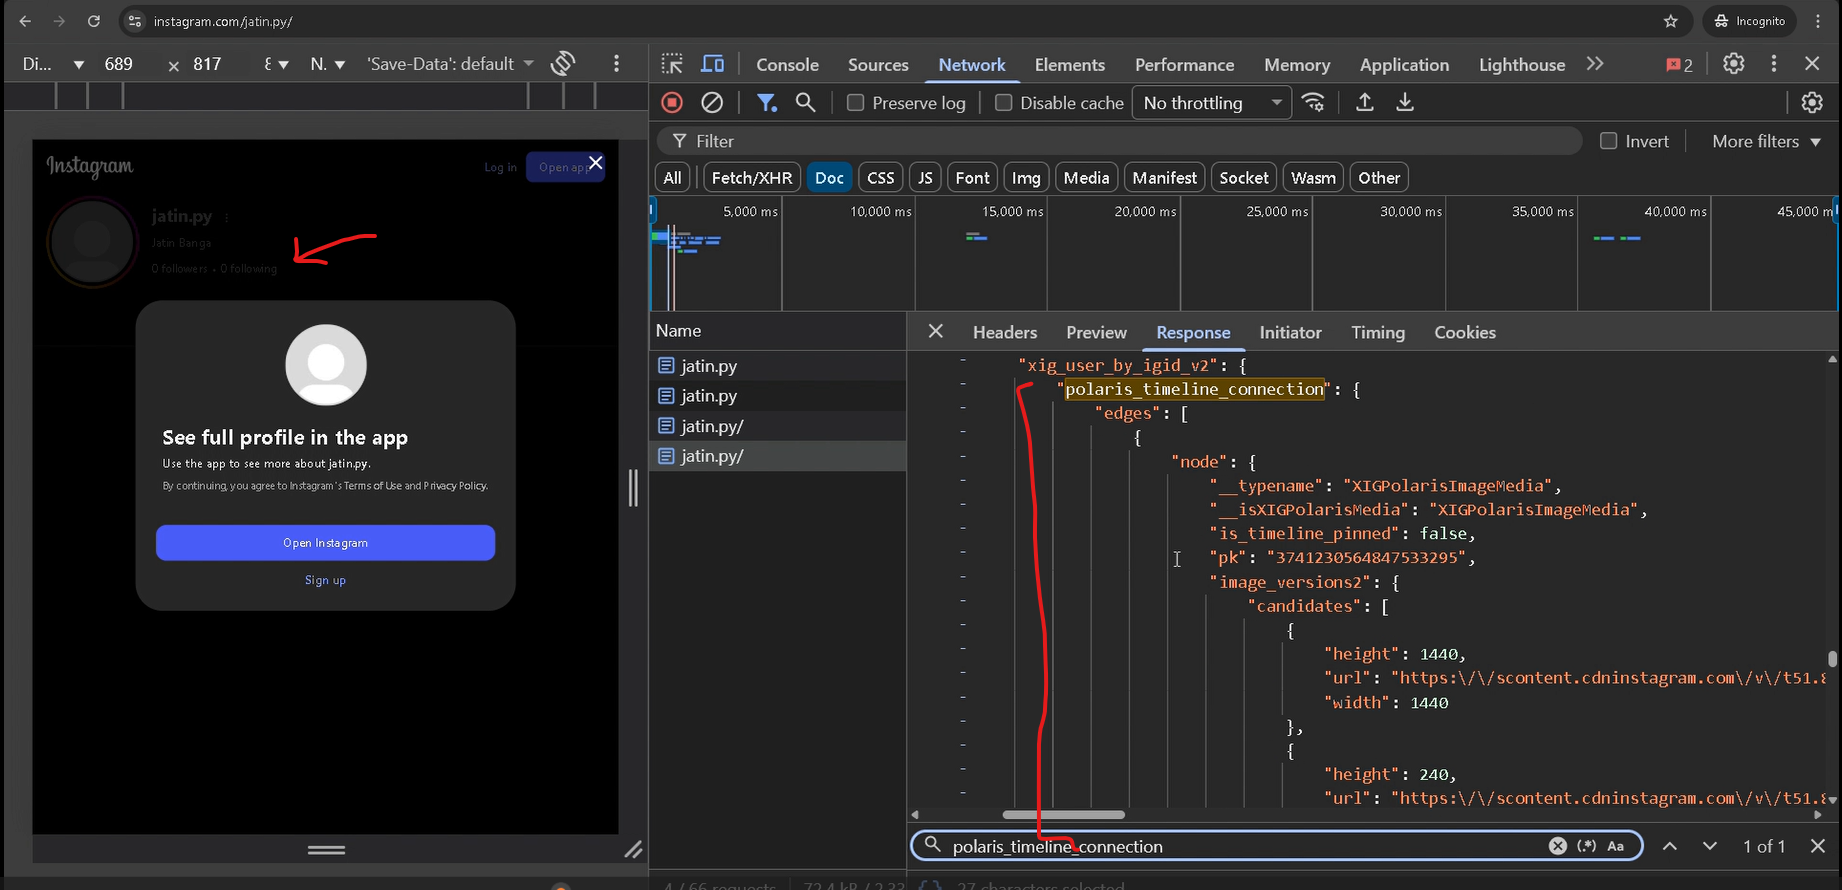 jatin-dot-py/instagram-private-bypass
This repository discloses a server-side authorization bypass in Instagram, which allowed unauthenticated access to private timelines; it seems likely…
 0xreadingsteiner/silent-call
Silent;Call — Pre-authentication remote root on Cisco CUCM 15.x (CVSS 10.0)
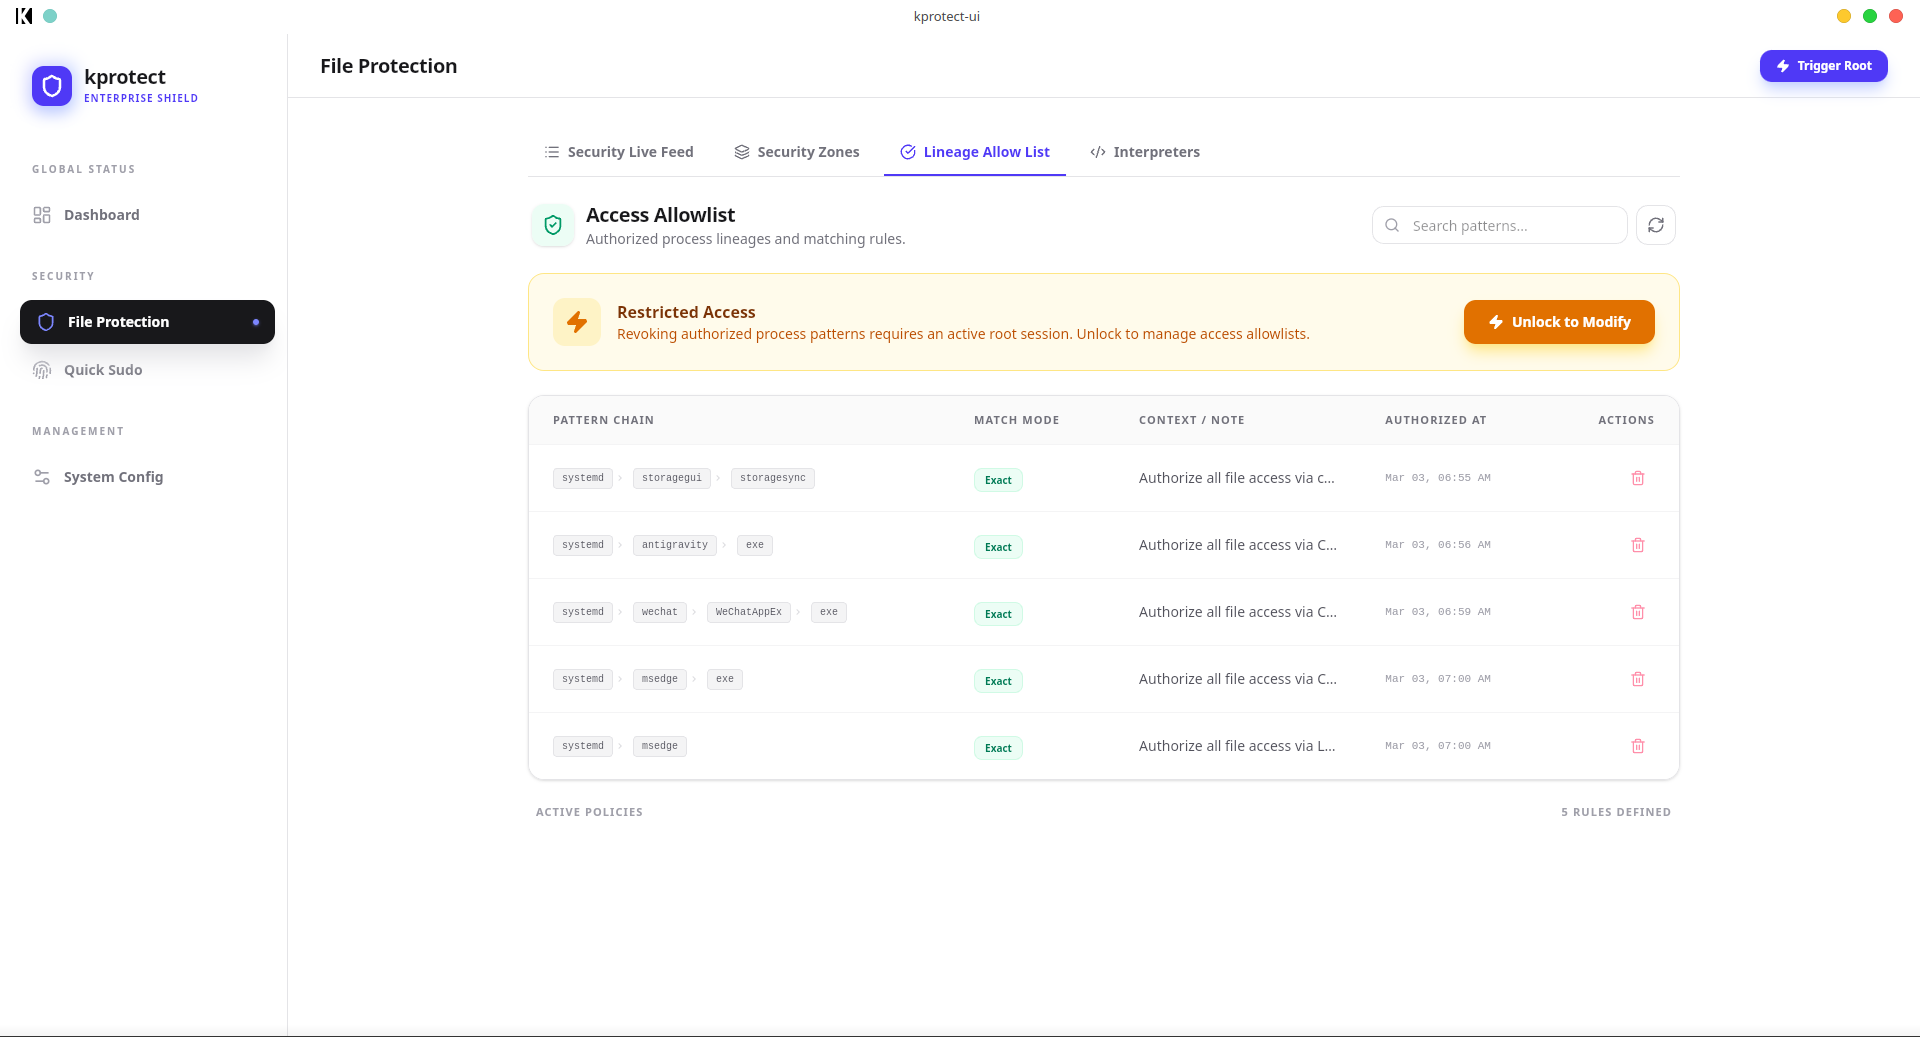 khoinp1012/kprotect
Kernel-level security engine using eBPF-LSM to enforce file access policies based on process lineage, protecting sensitive data from supply-chain…
 murrez/cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940, an authentication bypass chain in WHM/cPanel. Multi-threaded scanner that changes root password on…
 squeeze440/terrapod-poc
PoC — missing authorization on the platform-wide GPG trust-anchor store in Terrapod (GHSA-6qrc-597p-mrp9, CVE-2026-87006, CVSS 6.5).
 boreas37/cve-2026-41452-poc
CVE-2026-41452 — Krayin CRM unauth installer bypass (X-Requested-With) → admin takeover. Verified: overwrite + login on 2.2.4, blocked on 2.2.5
 george0papasotiriou/cve-2026-23004-automotive-uds-authentication-bypass-via-replay-attack
Proof-of-concept exploit demonstrating UDS authentication bypass via challenge-response replay on automotive ECUs, with Python CAN-UDS simulator.
 boreas37/cve-2026-44848-poc
PoC for CVE-2026-44848: Portainer missing authorization on Docker plugin endpoints -> host RCE (GHSA-rrmm-9v76-h3p4). Stdlib-only Python.
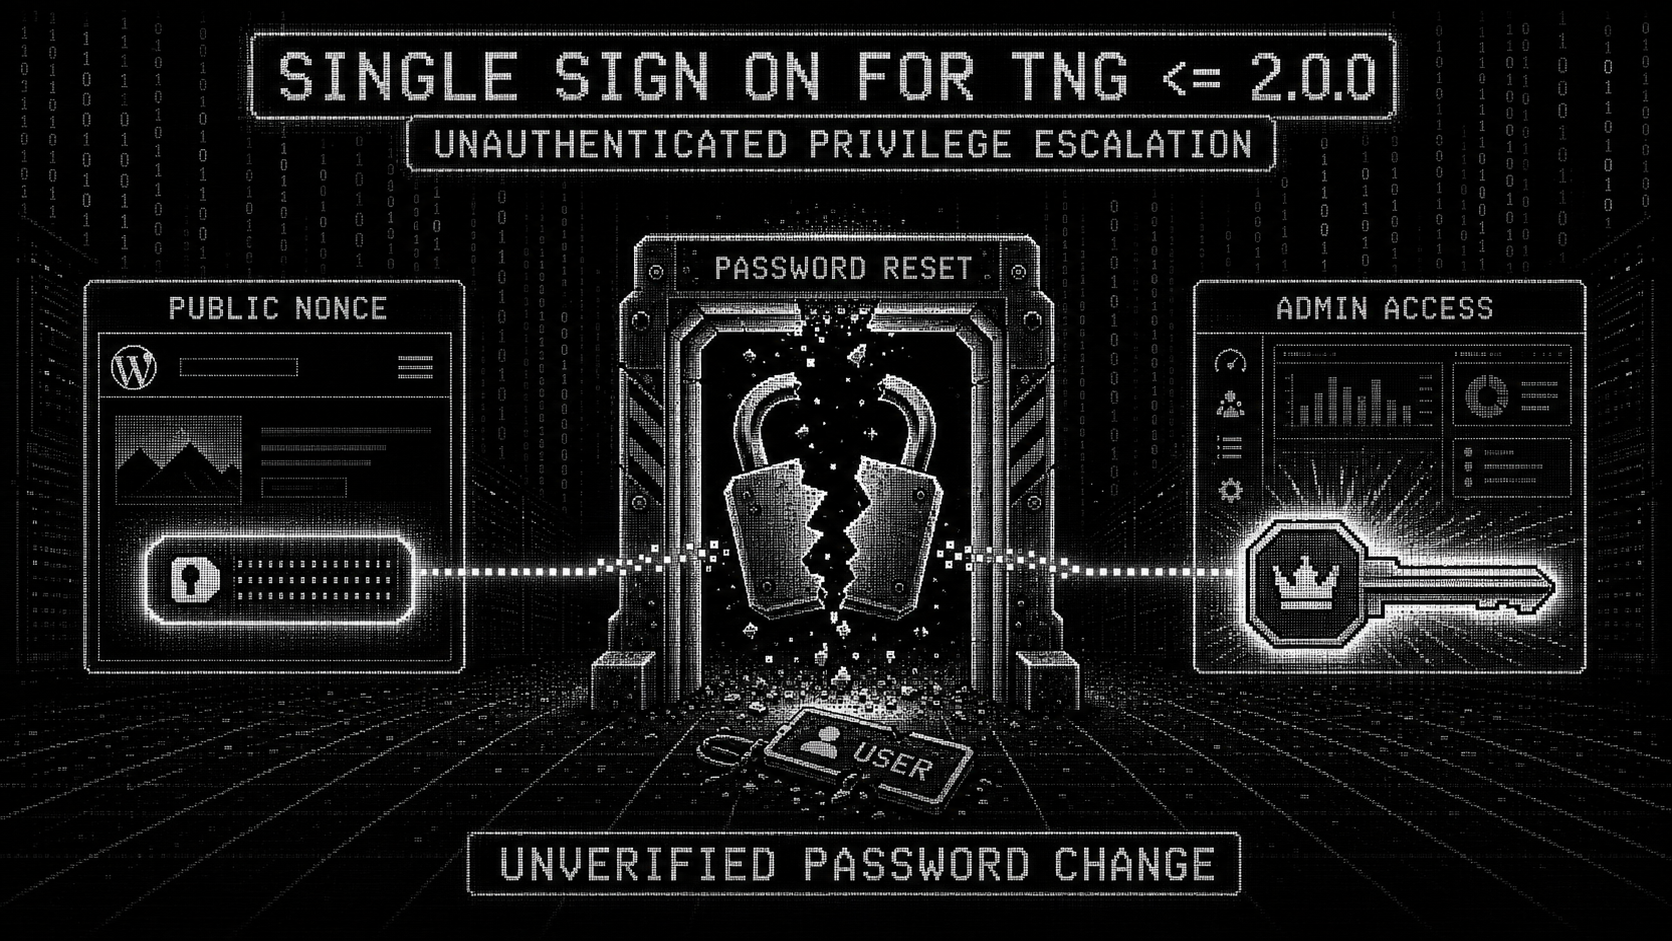 instructor-admin/cve-2026-15964-poc
PoC & checker for CVE-2026-15964 - unauthenticated password change in the WordPress plugin Single Sign On For TNG <= 2.0.0 (CVSS 9.8)
 kc57/jitbit_helpdesk_auth_bypass
Utility to derive the shared secret on a JitBit Helpdesk install which can be used for authentication bypass (CVE-2017-18486)