
aquaman
 tech4242/aquaman
🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
api-securityauthentication-authorizationcloud-security+7
36
tech4242/aquaman🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…
 tc4dy/cve-2026-29000-poc-exploit
CVE-2026-29000 – pac4j-jwt Authentication Bypass (CVSS 10.0). One-click admin forge via public key JWE wrapping. Leaks configs, users, secrets.…

 kavryxdev-group/enterprise-abac-gateway
Zero-trust reverse proxy and ABAC authorization gateway in Go with embedded OPA policy evaluation and distributed token revocation.
 adarsh14734/aegis-releases
Sandbox and MCP proxy that blocks AI coding agents from reading SSH keys, AWS credentials, and .env files, with deny-by-default policy and…
 dezso-dfield/cve-2023-27350
PaperCut NG/MG Authentication Bypass and Remote Code Execution (RCE) Exploit Tool. A standalone Bash implementation of the PaperCut exploit chain,…
 mrpayloadc/cve-2025-0316-exploit
Automated auth bypass exploit for CVE-2025-0316 targeting WordPress WP Directorybox Manager. Features user enumeration, proxy support,…
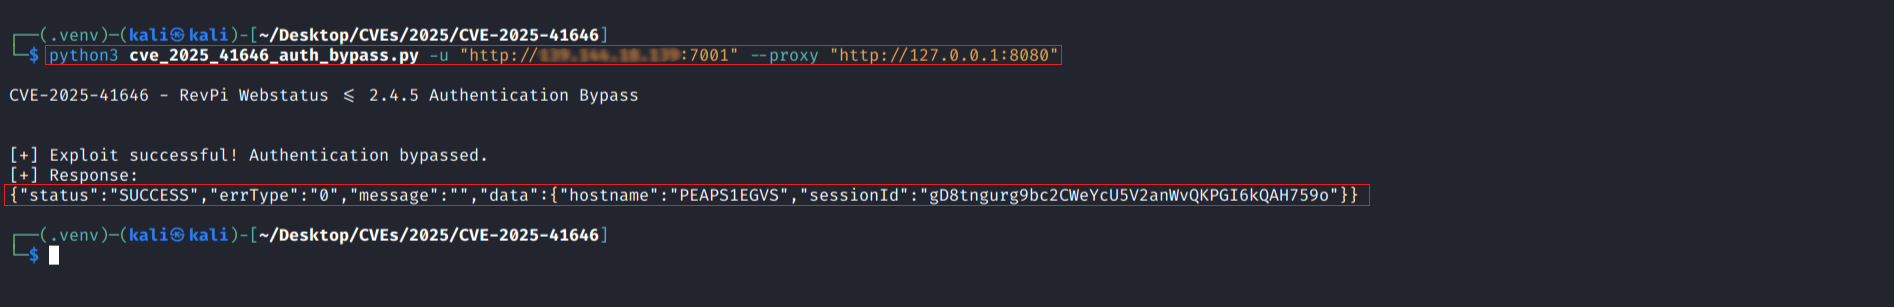 r0otk3r/cve-2025-41646
Python exploit script for CVE-2025-41646, an authentication bypass in RevPi Webstatus <= 2.4.5. Supports single/mass exploitation, proxy, silent…
 abdurahmon3236/cve-2024-38473
Proof-of-concept demonstrating an encoding flaw in Apache HTTP Server mod_proxy that can bypass authentication via crafted encoded URLs.
 covepseng/cve-2026-49352-poc
Exploitability PoC for CVE-2026-49352 (9router Hardcoded JWT Secret Authentication Bypass)
 goauthentik/authentik
Provides open-source SSO and identity provider functionality with SAML, OAuth2/OIDC, LDAP, and RADIUS support for centralized authentication,…