SecurityExplained
SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…

SecurityExplained is a new series after the previous learning challenge series #Learn365. The aim of #SecurityExplained series is to create…

A tool to extract the IdP cert from vCenter backups and log in as Administrator

PHP-RBAC is an authorization library for PHP. It provides developers with NIST Level 2 Standard Role Based Access Control and more, in the fastest…

A security-first reverse proxy built to guard the free web.

The next generation encrypted file sharing project

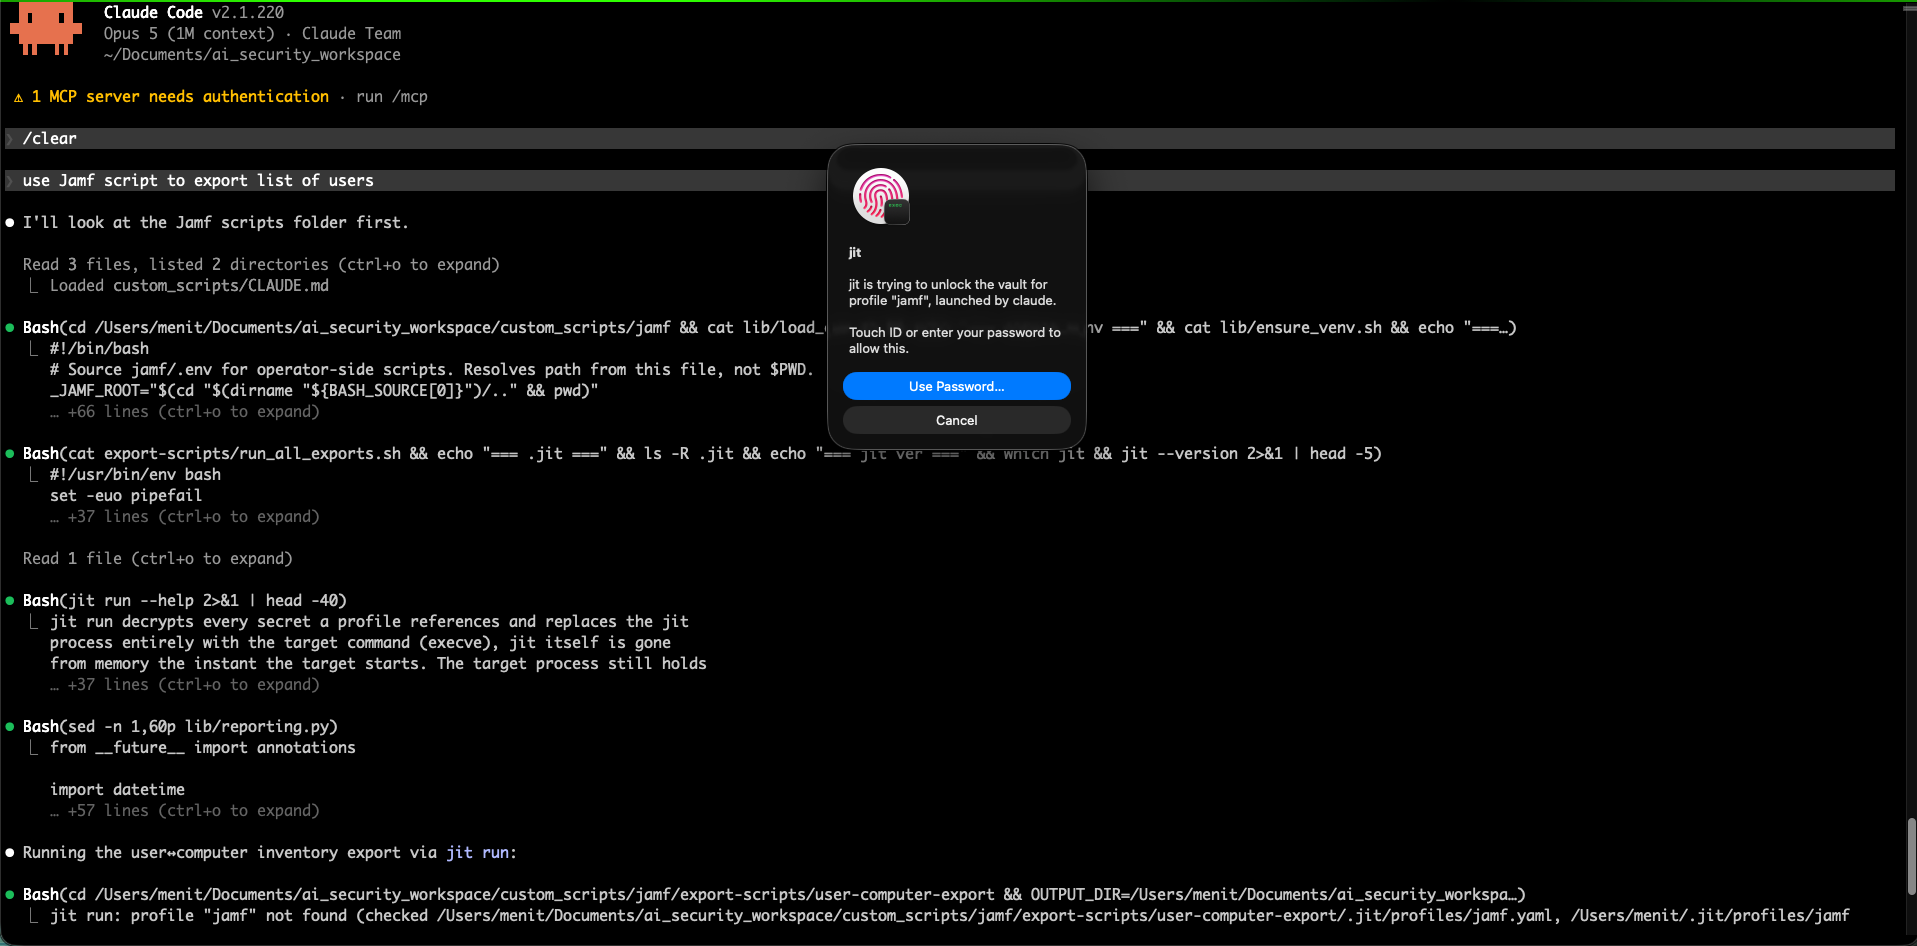
Find the plaintext secrets on your Mac and move them behind Touch ID, injected just in time without breaking the tools that read them. Free and…

A C# tool for requesting certificates from ADCS using DCOM over SMB. This tool allows you to remotely request X.509 certificates from CA server using…

Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!

.Net Assembly loader for the [CVE-2021-42287 - CVE-2021-42278] Scanner & Exploit noPac

The SSH Multiplex Backdoor Tool

🔱 The only independent credential proxy for AI agents: bring-your-own-vault isolation & least-privilege request policies. Your keys stay where you…

Exploit for the CVE-2024-5806

An authentication bypass vulnerability in the web component of Ivanti ICS 9.x, 22.x and Ivanti Policy Secure allows a remote attacker to access…

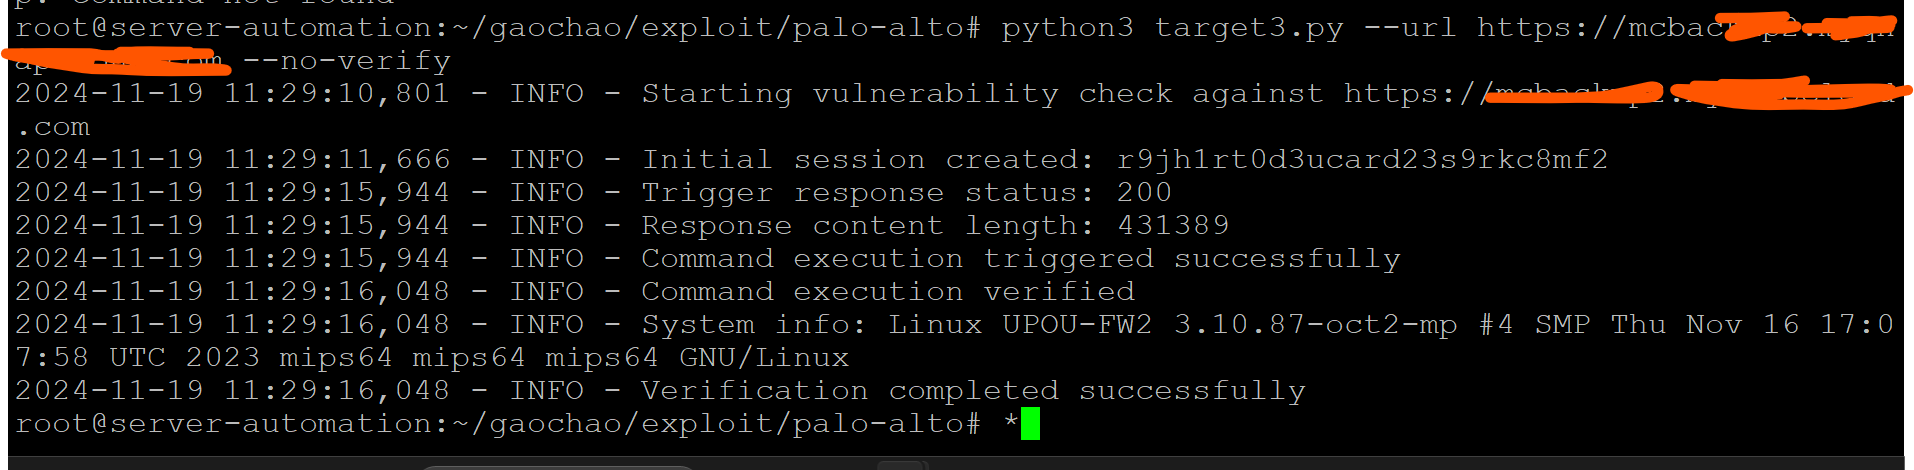
CVE-2024-0012 PAN-OS: Authentication Bypass in the Management Web Interface (PAN-SA-2024-0015) RCE POC

A proof-of-concept script to exploit CVE-2026-16232, an authentication bypass via the SmartConsole login process using an application token.

Reproduction environment for CVE-2025-29927, demonstrating Next.js middleware authorization bypass via the x-middleware-subrequest header. Includes…

CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…

Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…